
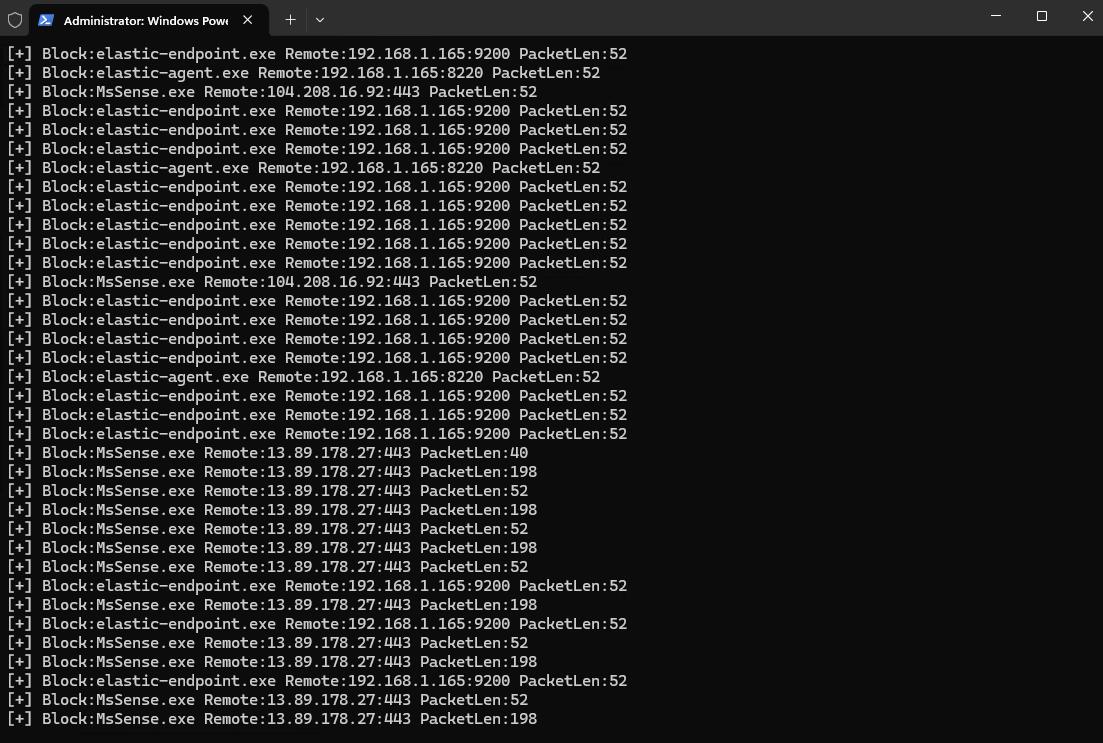
EDRPrison
 senzee1984/edrprison
Leverage a legitimate WFP callout driver to prevent EDR agents from sending telemetry
adversarial-attackids-ips-evasionnetwork-security+2
4772 years ago
senzee1984/edrprisonLeverage a legitimate WFP callout driver to prevent EDR agents from sending telemetry
 loosehose/dutchoven
Application-scoped Windows network brownouts in native C and BOF form
 crisprss/magicnetdefs
Similar to Petitpotam, the netdfs service is enabled in Windows Server and AD environments, and the abused RPC method allows privileged processes to…
 george0papasotiriou/cve-2026-22007-ntp-monlist-amplification-over-ipv6
Python PoC for CVE-2026-22007: NTP monlist amplification over IPv6, including a simulated vulnerable server and spoofed UDP reflection attack.
 yosangwon/arp-dns-spoof
Sample code for DNS spoofing with ARP poisoning.
 amberwolfcyber/nachovpn
A delicious, but malicious SSL-VPN server 🌮
 pasquini-dario/project_mantis
Project Mantis: Hacking Back the AI-Hacker; Prompt Injection as a Defense Against LLM-driven Cyberattacks
 xiaolichan/redcaddy
C2 redirector base on caddy
 rasta-mouse/crystal-kit
Evasion kit for Cobalt Strike
 helviojunior/hookchain
HookChain: A new perspective for Bypassing EDR Solutions
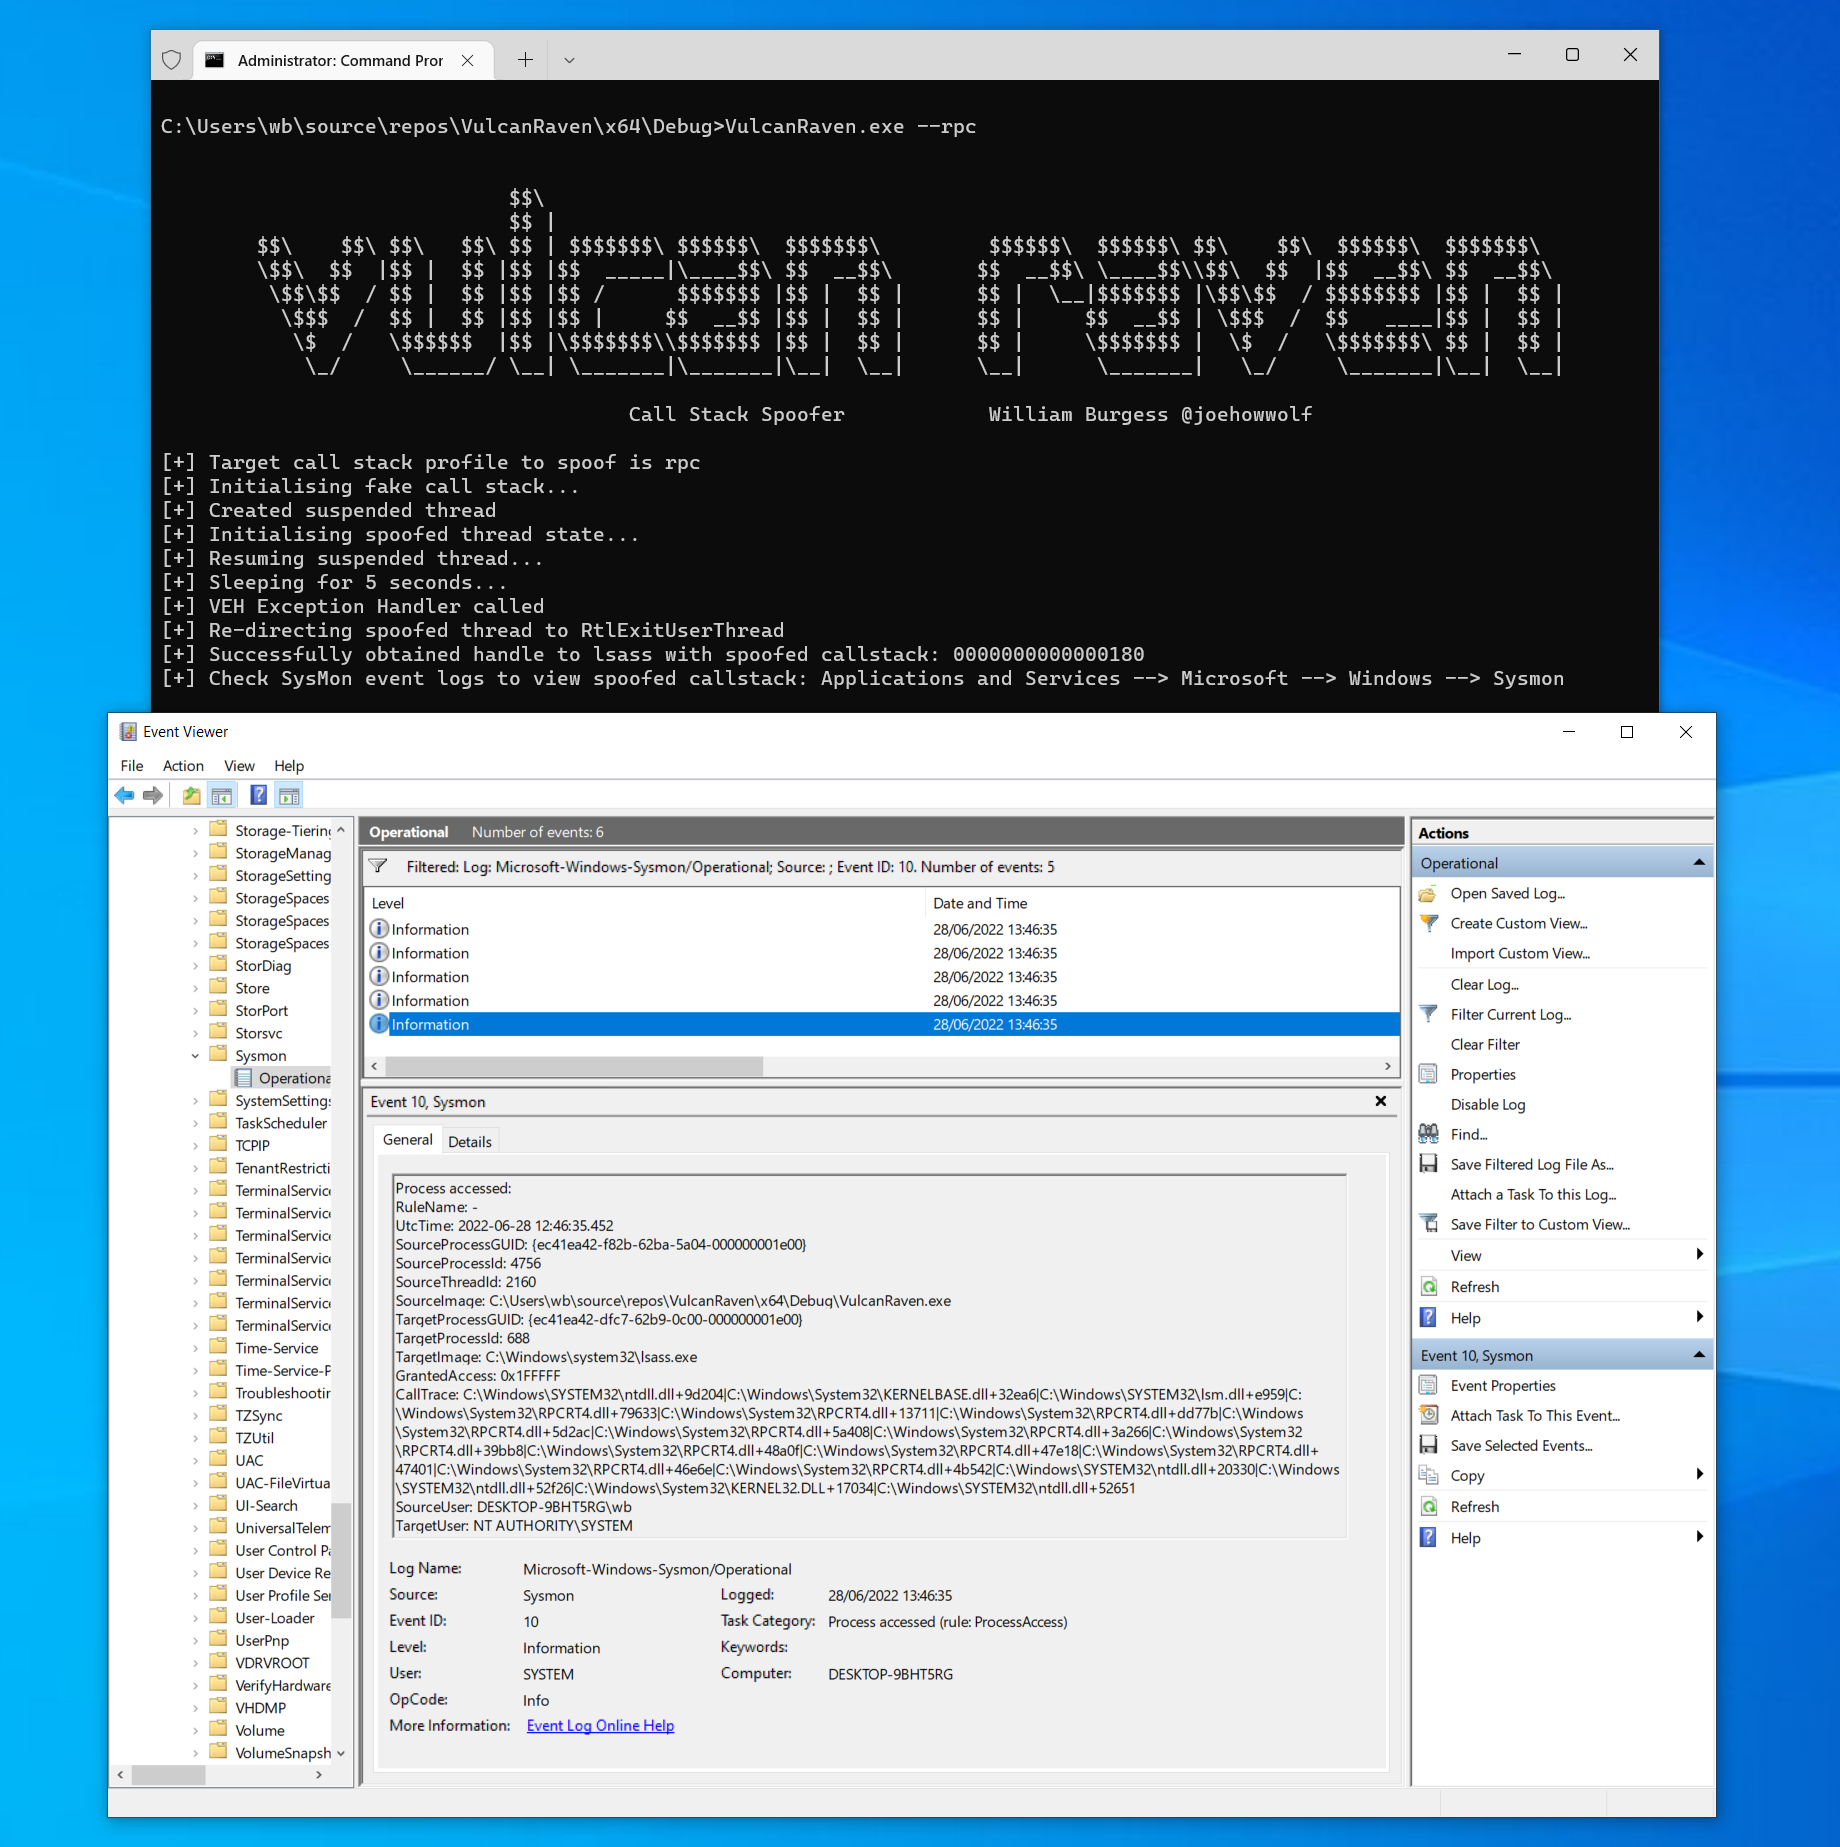 withsecurelabs/callstackspoofer
A PoC implementation for spoofing arbitrary call stacks when making sys calls (e.g. grabbing a handle via NtOpenProcess)
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
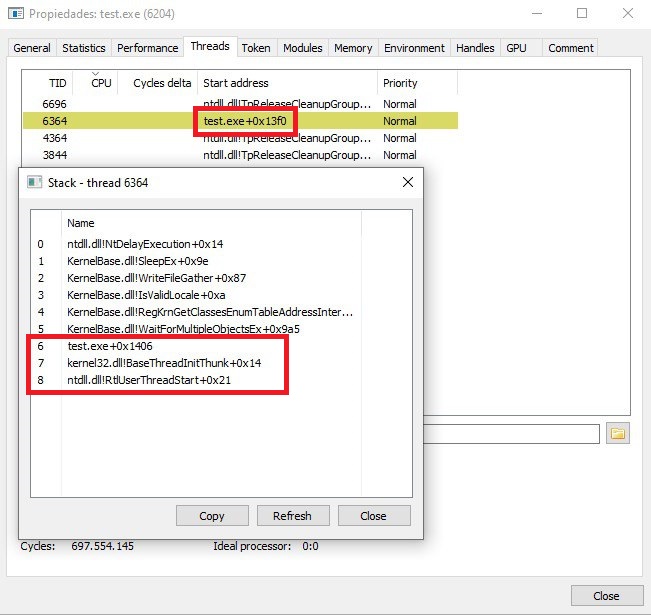 kudaes/unwinder
Call stack spoofing for Rust
 lloydlabs/ntqueueapcthreadex-ntdll-gadget-injection
This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 nul0x4c/etwsessionhijacking
A Poc on blocking Procmon from monitoring network events
 rasta-mouse/libtp
Crystal Palace library for proxying Nt API calls via the Threadpool
 whispergate/lldp
C2 profile for Mythic tunneling encrypted peer-to-peer agent traffic through IEEE 802.1AB LLDP Organizationally Specific TLVs for covert Layer 2…