
lldp
 whispergate/lldp
C2 profile for Mythic tunneling encrypted peer-to-peer agent traffic through IEEE 802.1AB LLDP Organizationally Specific TLVs for covert Layer 2…
adversarial-attackcommand-and-controlids-ips-evasion+1
23
whispergate/lldpC2 profile for Mythic tunneling encrypted peer-to-peer agent traffic through IEEE 802.1AB LLDP Organizationally Specific TLVs for covert Layer 2…
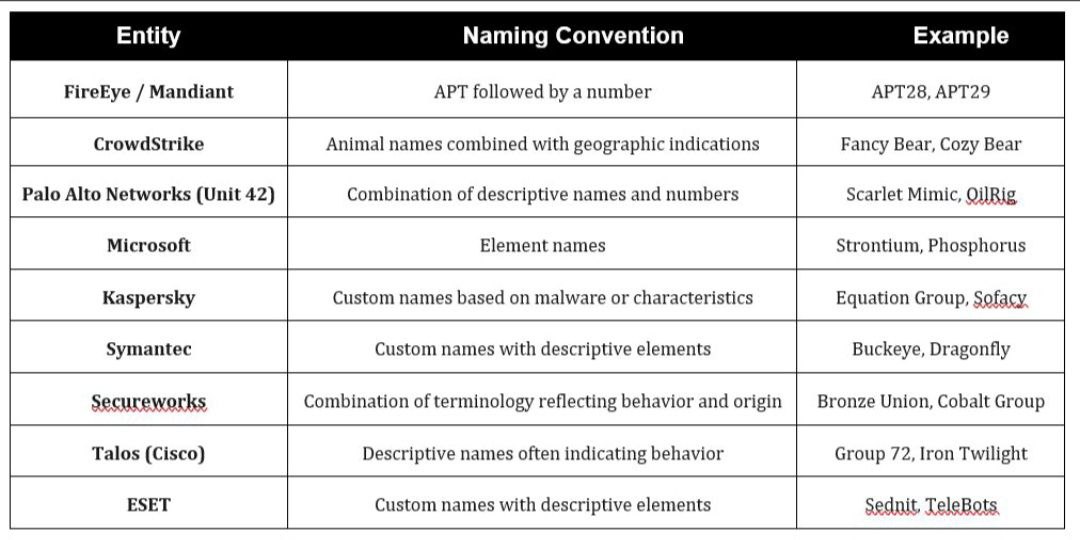 s3n4t0r-0x0/apts-adversary-simulation
This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…
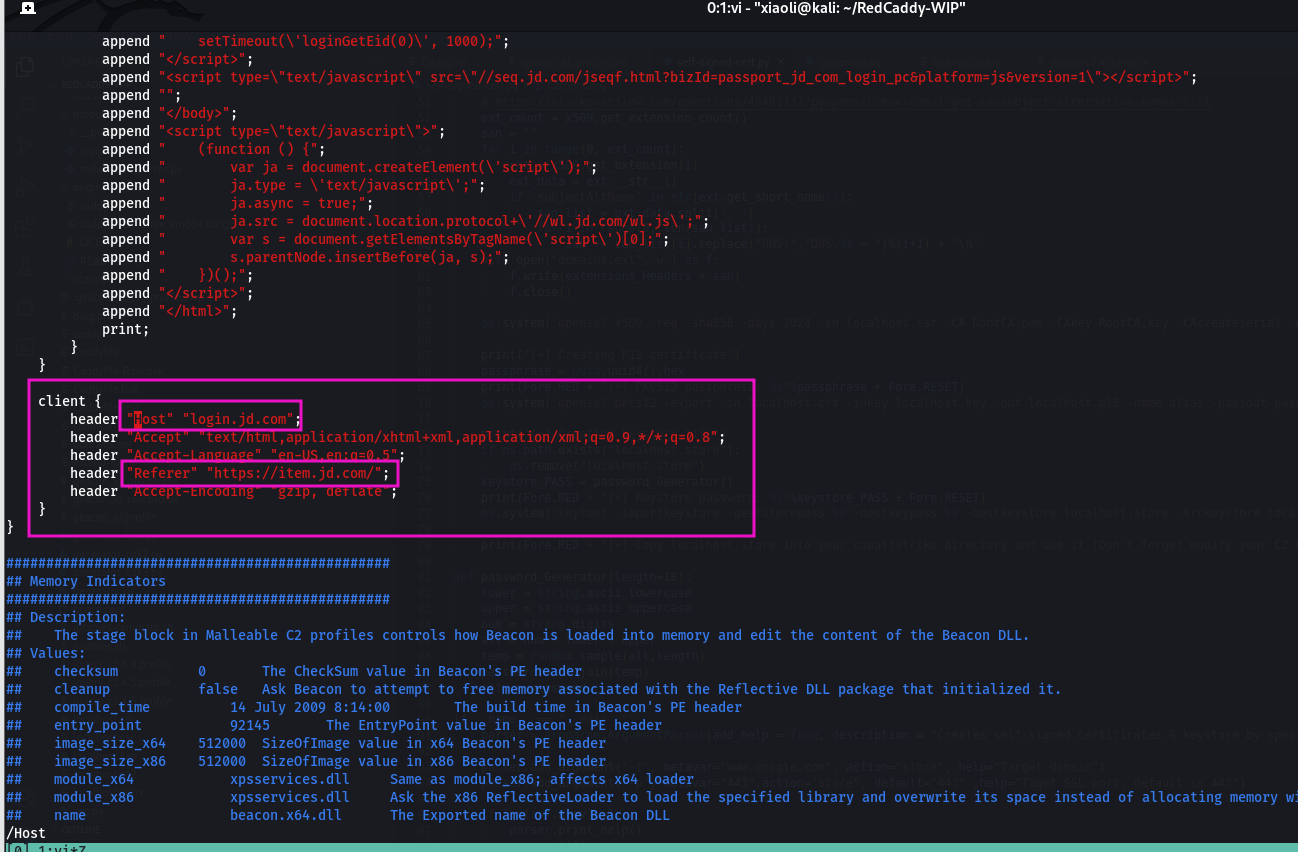 xiaolichan/redcaddy
C2 redirector base on caddy
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 bishopfox/sliver
Adversary Emulation Framework
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 matheuzsecurity/ringreaper
Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
 darkcodersc/sharpftpc2
A Streamlined FTP-Driven Command and Control Conduit for Interconnecting Remote Systems.
 apache/caldera
Automated Adversary Emulation Platform
 microsoft/pyrit
Open-source framework for red-teaming generative AI systems: automate attack prompts, score model responses, and audit behavior to identify security…
 guardicore/monkey
Infection Monkey - An open-source adversary emulation platform
 funnywolf/viper
Adversary simulation and Red teaming platform with AI
 rasta-mouse/crystal-kit
Evasion kit for Cobalt Strike
 0xb11a1/yetanotherobfuscator
C# obfuscator that bypass windows defender
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 zeromemoryex/amsi-killer
Lifetime AMSI bypass
 d00mfist/mystikal
macOS Initial Access Payload Generator
 mattifestation/antimalwareblight
Execute PowerShell code at the antimalware-light protection level.