Anti-Virus-Evading-Payloads

During the exploitation phase of a pen test or ethical hacking engagement, you will ultimately need to try to cause code to run on target system…

During the exploitation phase of a pen test or ethical hacking engagement, you will ultimately need to try to cause code to run on target system…

Proof-of-concept exploit for CVE-2026-22003 demonstrating Redis Lua sandbox escape via debug.sethook to execute arbitrary system commands.

Defense framework that mitigates malicious fine-tuning of LLMs using selective layer recovery and dynamic routing, with training, harmfulness…

Attack framework for breaking fine-tuning based prompt injection defenses (SecAlign, SecAlign++, StruQ) using architecture-aware adversarial attacks…

Reproduces CVE-2026-21019 by manipulating node clock to force early Kubernetes CronJob execution; includes vulnerable YAML manifest and Python…


Canary Hunter aims to be a quick PowerShell script to check for Common Canaries in various formats generated for free on canarytokens.org

Training-free language model modification: Remove censorship, suppress slop, reduce sycophancy, and more

This is the tool to dump the LSASS process on modern Windows 11

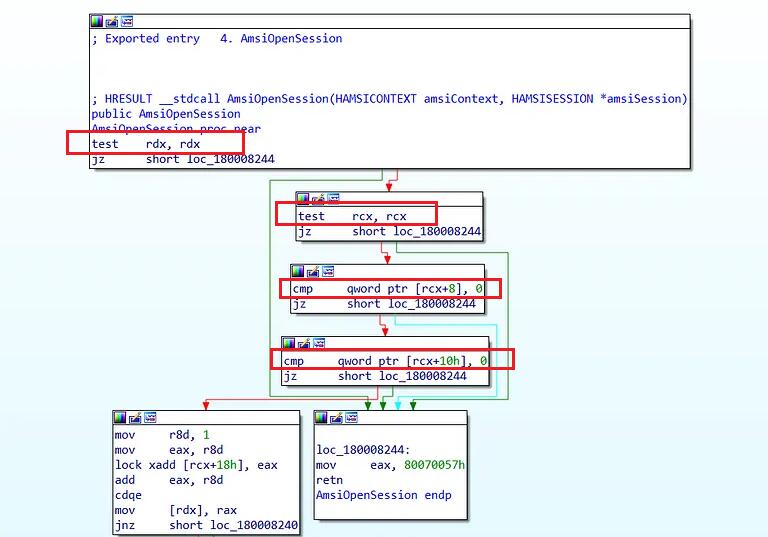
Amsi Bypass payload that works on Windwos 11

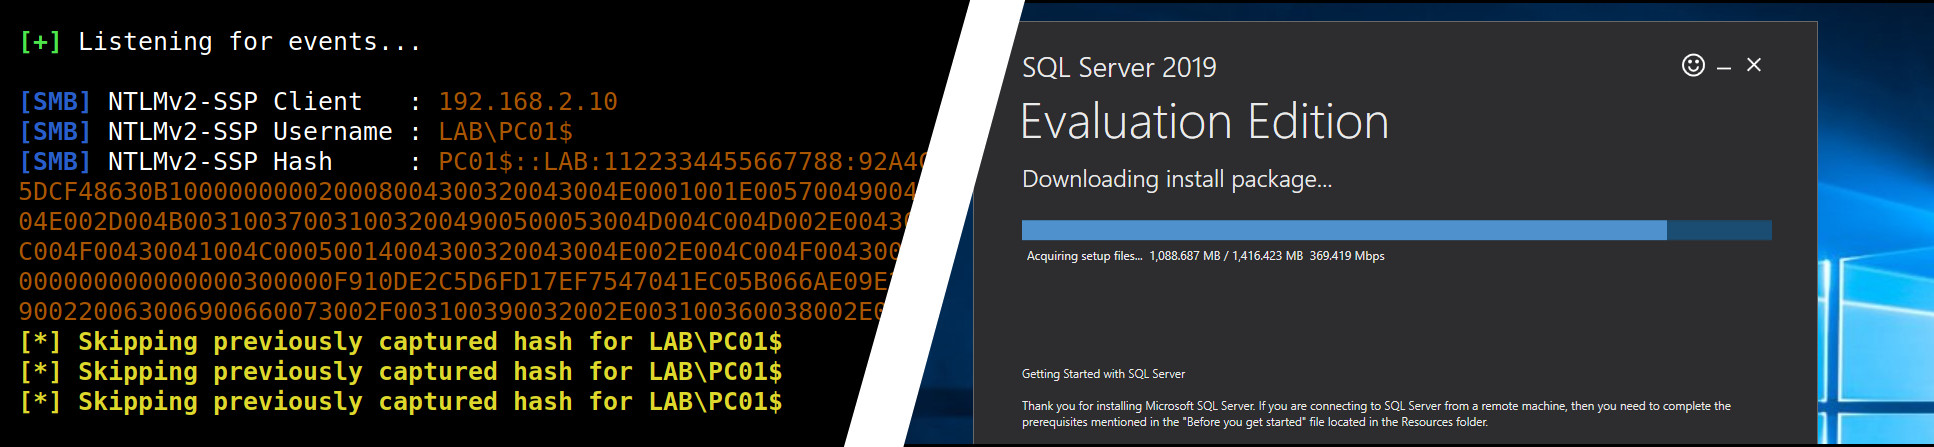
A technique to coerce a Windows SQL Server to authenticate on an arbitrary machine.

PoC script for HTTP/2 Rapid Reset (CVE-2023-44487) that sends crafted HTTP/2 streams to trigger denial-of-service conditions on vulnerable servers,…

Experiments for control-token chain-of-thought suppression and parser-leniency attacks on tool-using LLM agents

A simple PoC on the Remote Code Execution (RCE) Vulnerability of CraftCMS designated as CVE-2025-32432 written in Go

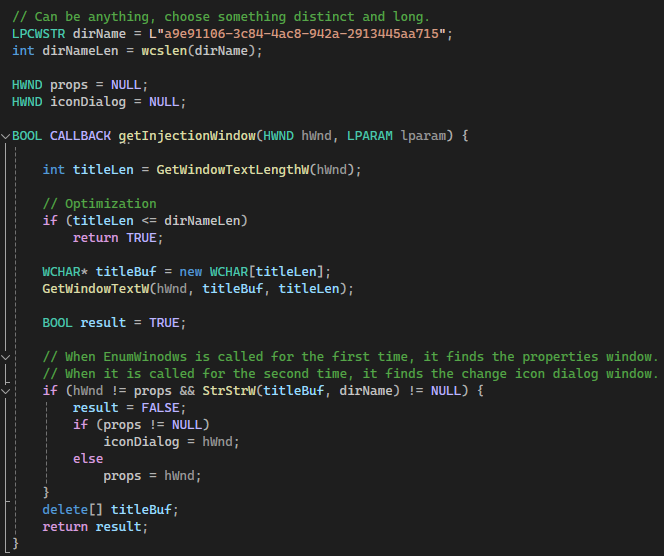
Inject DLLs into the explorer process using icons

Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC

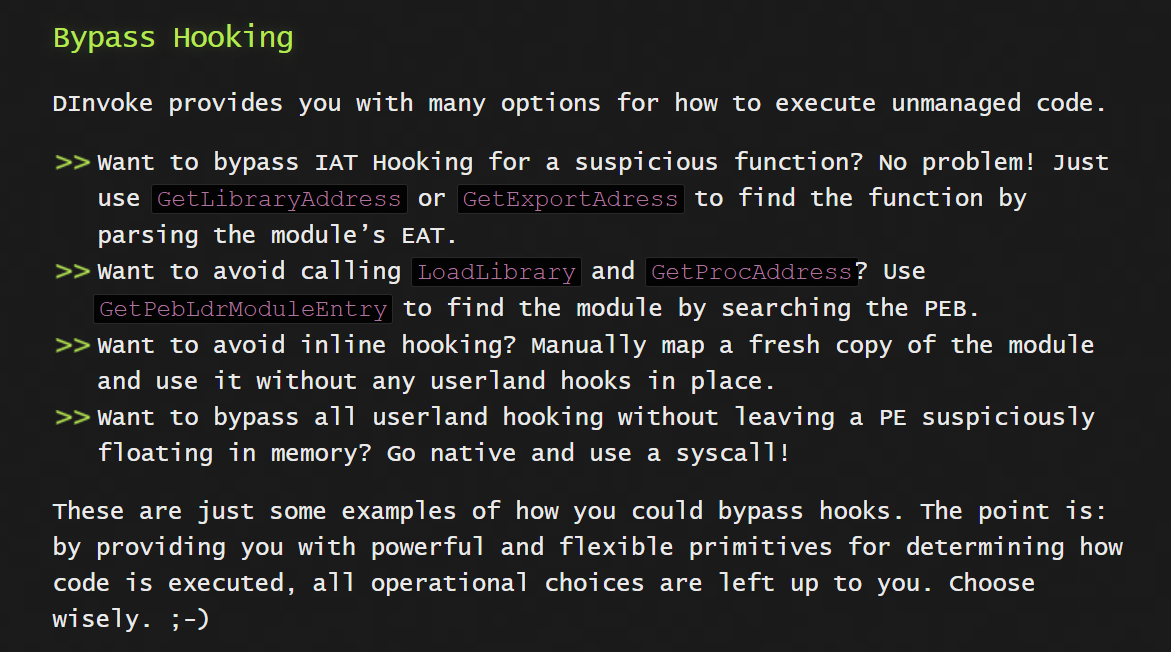
D/Invoke implementation in Nim