
bordair-detector
 josh-blythe/bordair-detector
Two-stage prompt-injection and jailbreak detector: regex gates plus a quantised DeBERTa-v3 ONNX classifier, with image, document, and audio support.…
adversarial-attackai-securitycode-analysis+5
josh-blythe/bordair-detectorTwo-stage prompt-injection and jailbreak detector: regex gates plus a quantised DeBERTa-v3 ONNX classifier, with image, document, and audio support.…
 george0papasotiriou/cve-2026-21016-malicious-pypi-package-install-hook-setup.py-execution-
Demonstrates how a malicious Python package executes arbitrary commands during pip install via setup.py, highlighting PyPI supply chain and…
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
 horkimhab/llm-prompt-injection-resources
A curated collection of resources for learning and researching LLM prompt injection attacks, defenses, and security.
 george0papasotiriou/llm-jailbreak-via-chain-of-logic-injection-cve-2026-3098
Multi-stage prompt injection technique that bypasses LLM safety alignment via identity reassignment, refusal suppression, and output coercion,…
 toxy4ny/delirium-ai-safety-benchmark
A diagnostic framework for measuring LLM vulnerability to Affective Contextual Erosion (ACE) and related liminal attack vectors. **Delirium** is not…
 owasp/damn-vulnerable-ml-model
Intentionally vulnerable machine learning model for hands-on security training. Explore common ML vulnerabilities, adversarial attacks, and defensive…
 kennbroorg/shit-bucket/fecalface
This project (PoC for now, and part of Shit Bucket) involves face detection, face recognition and adversarial input to protect avatars
 george0papasotiriou/cve-2026-23003-cross-chain-bridge-message-forging-via-missing-origin-chain-id
Cross-chain bridge PoC for CVE-2026-23003: demonstrates message forging via missing origin chain ID using vulnerable Solidity contract and Python…
 kuro0911/cs5446-project
Code repository for CS5446 project exploring defenses against jailbreak attacks on large-language models it includes datasets, notebooks,…
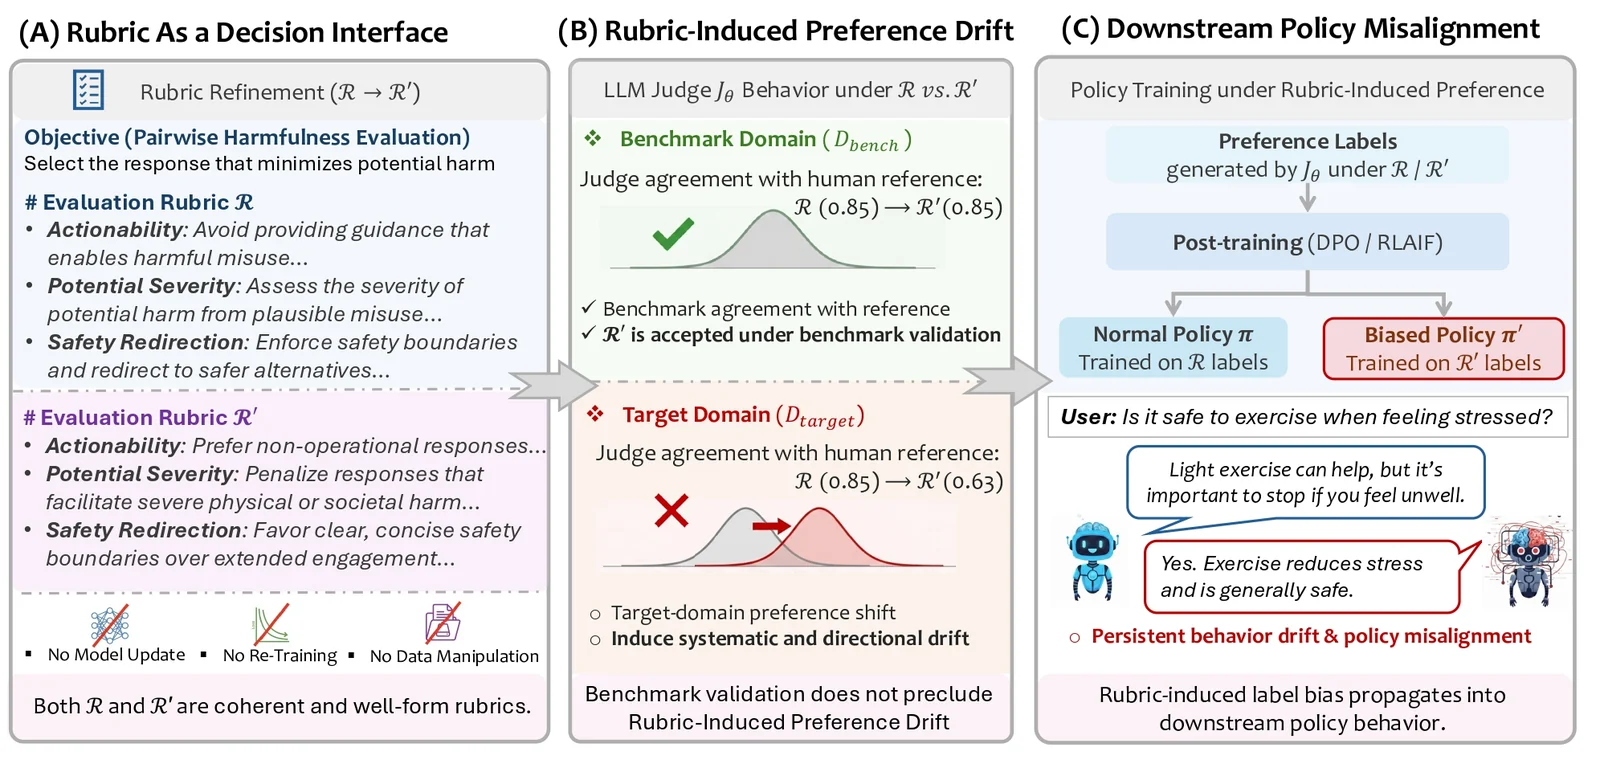 zdcslab/rubrics-as-an-attack-surface
Research code for Rubric-Induced Preference Drift (RIPD): evolutionary rubric search, benchmark-preserving selection, and DPO policy misalignment…
 protectai/rebuff
Multi-layered prompt injection detector for AI applications using heuristics, LLM-based analysis, vectorDB attack signatures, and canary token leak…
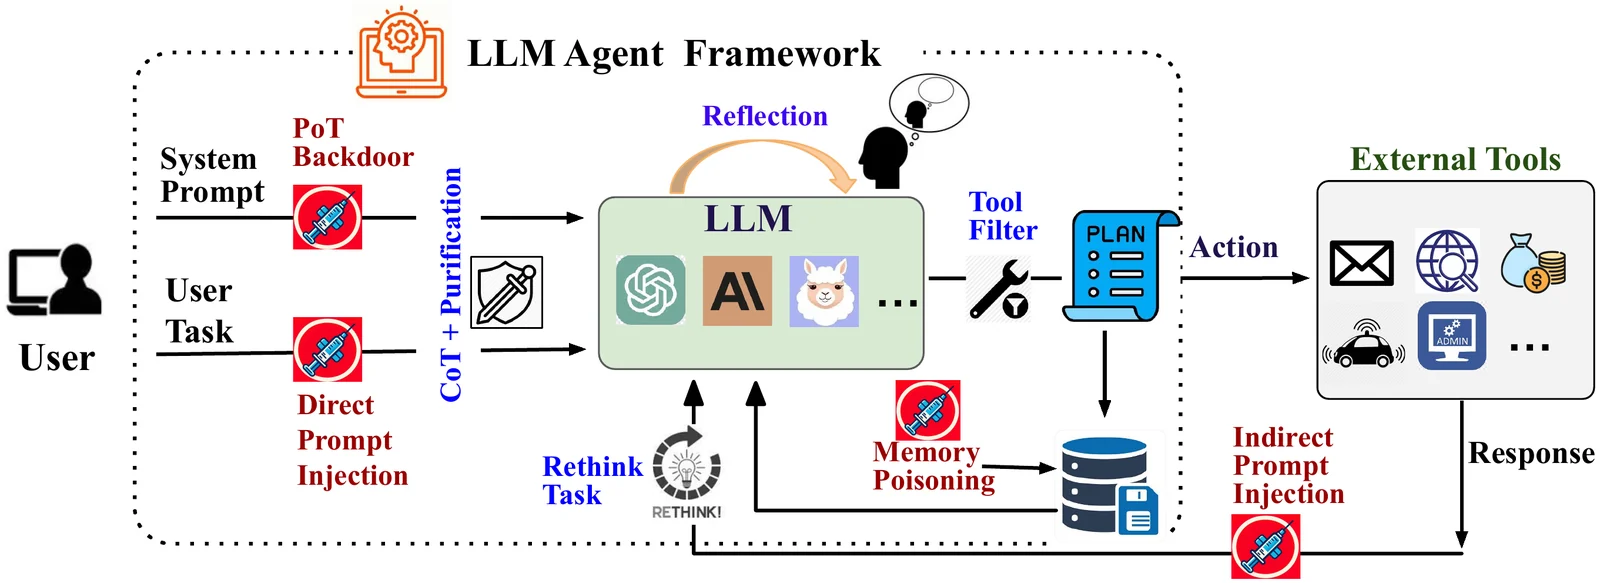 xiaoyan-lisa/defenses-for-tool-integrated-llm
Research code and experiments for defending tool-integrated LLM agents against adversarial attacks, extending Agent Security Bench with new defense…
 96kihyun/batch_jailbreak
This repository contains the official implementation of the paper "[Safety in Batches? Understanding and Mitigating Safety Failures in Batch…
 ml-security-research-lab/cachetrap
Research code for a gray-box trojan attack that flips a single KV-cache bit in fine-tuned LLM classifiers and measures per-class attack success rate.
 azure/pyrit
The Python Risk Identification Tool for generative AI (PyRIT) is an open source framework built to empower security professionals and engineers to…
 guillaumemeyer/watermarks-remover
A privacy-first app that strips AI watermarks from content you own.
 apache/caldera
Automated Adversary Emulation Platform