
better_opts_attacks
Attack framework for breaking fine-tuning based prompt injection defenses (SecAlign, SecAlign++, StruQ) using architecture-aware adversarial attacks…

Attack framework for breaking fine-tuning based prompt injection defenses (SecAlign, SecAlign++, StruQ) using architecture-aware adversarial attacks…

PoC for CVE-2026-71554 - h2 duplicate Host header request smuggling primitive (fixed in 4.4.1)

Open-source adversary emulation for AI agents and MCP servers.

Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…

A high-severity prompt injection flaw in Claude AI proves that even the smartest language models can be turned into weapons — all with a few lines of…

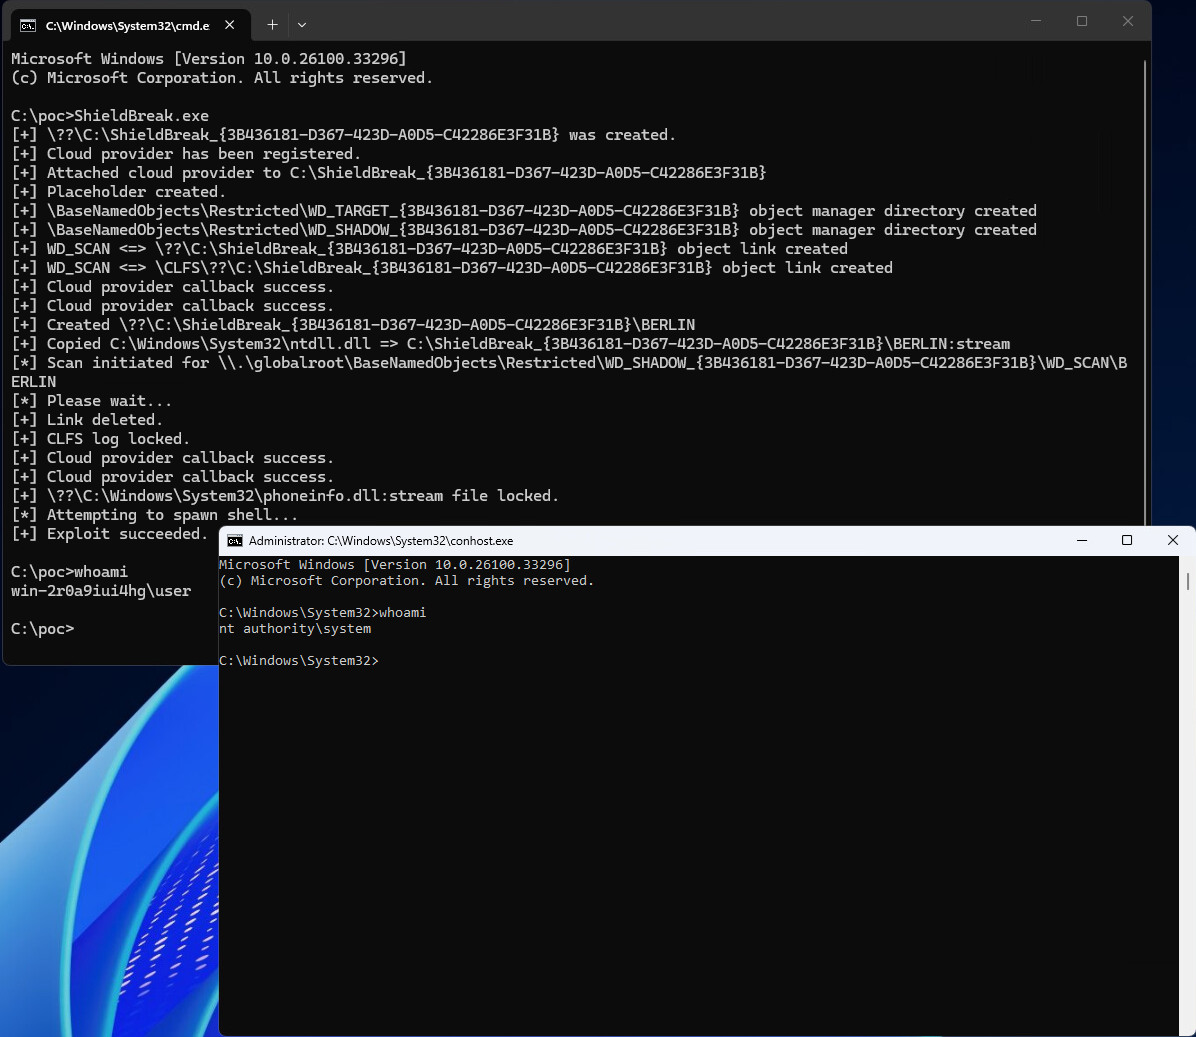
Windows Defender patch bypass PoC for CVE-2026-50656 (RoguePlanet), demonstrating exploitability on Windows 11 25H2 and Server 2025 despite…

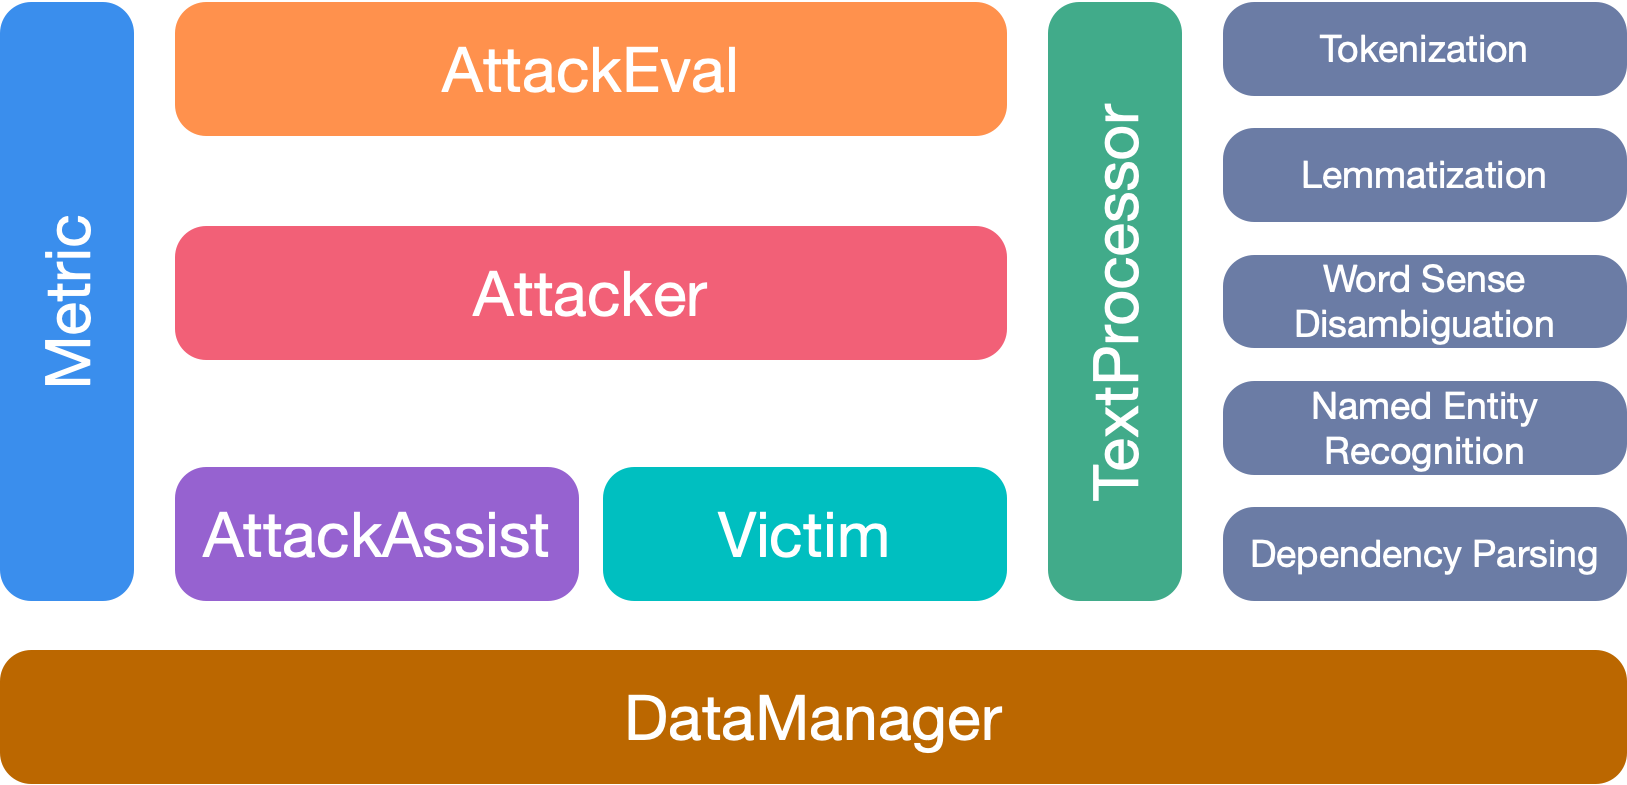
An Open-Source Package for Textual Adversarial Attack.

Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.

Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…

A POC to disable TamperProtection and other Defender / MDE components

Code repository for CS5446 project exploring defenses against jailbreak attacks on large-language models it includes datasets, notebooks,…

Research code for poisoning attacks on the PGM-index, demonstrating how to craft adversarial data to degrade learned index performance.

Source code about machine learning and security.

Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…

Reproduces CVE-2026-21019 by manipulating node clock to force early Kubernetes CronJob execution; includes vulnerable YAML manifest and Python…

Detect EDR's exceptions by inspecting processes' loaded modules

This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…

A prompt injection in a code‑review bot that executes AI‑generated fixes in a sandbox. The sandbox uses a blacklist to prevent dangerous commands,…