

OffensiveCpp
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.
adversarial-attackcurated-resourcesexploitation+6
7681 year ago
lsecqt/offensivecppThis repo contains C/C++ snippets that can be handy in specific offensive scenarios.
 helviojunior/hookchain
HookChain: A new perspective for Bypassing EDR Solutions
 vxcrypt0r/voidgate
A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
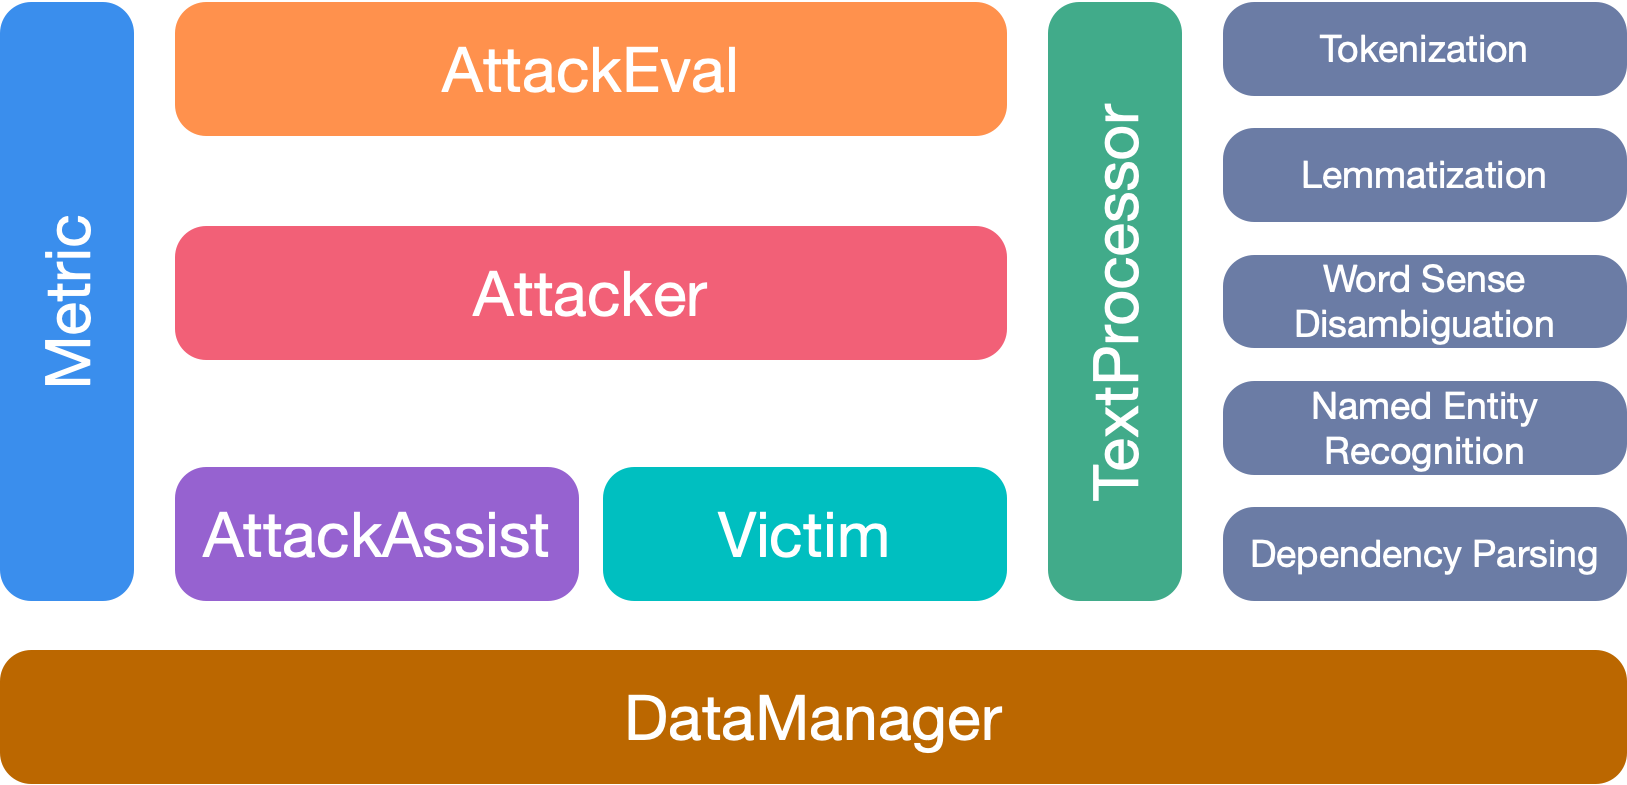 thunlp/openattack
An Open-Source Package for Textual Adversarial Attack.
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
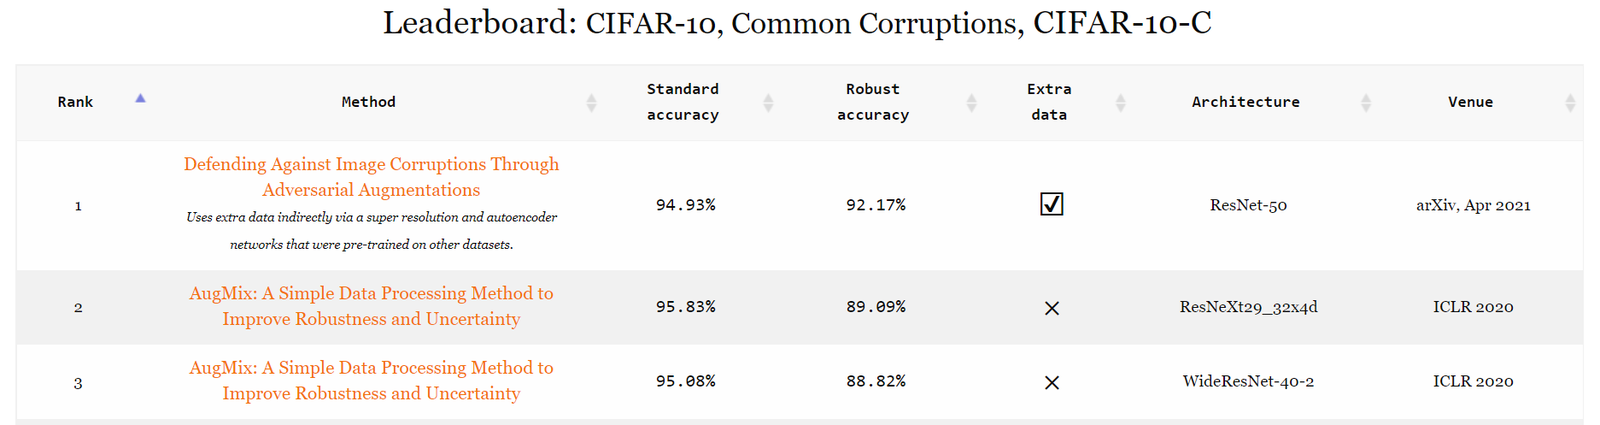 robustbench/robustbench
Standardized adversarial robustness benchmark with a public leaderboard and downloadable model zoo for evaluating ML models against Lp attacks and…
 davidcarliez/trustmebro
Bypass llm guardrails by confusing it with fabricated tool output.
 shiva108/ai-llm-red-team-handbook
AI / LLM Red Team Field Manual & Consultant’s Handbook
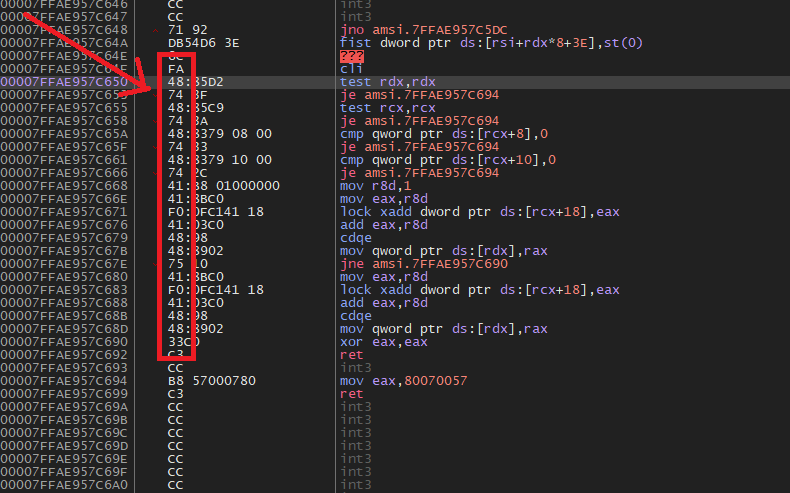 zeromemoryex/amsi-killer
Lifetime AMSI bypass
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
 0xsojalsec/uncensored-ai
Fully automatic censorship removal for language models
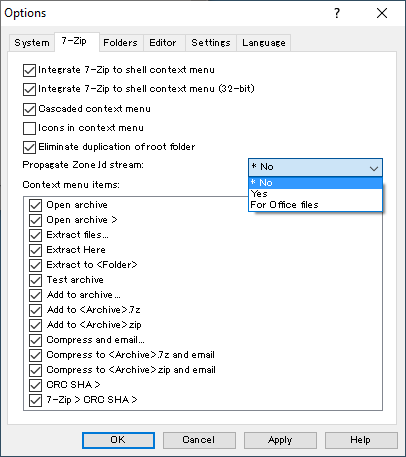 nmantani/archiver-motw-support-comparison
Compares Windows archiver support for Mark of the Web propagation, helping teams assess which tools preserve MOTW and mitigate macro-based malware…
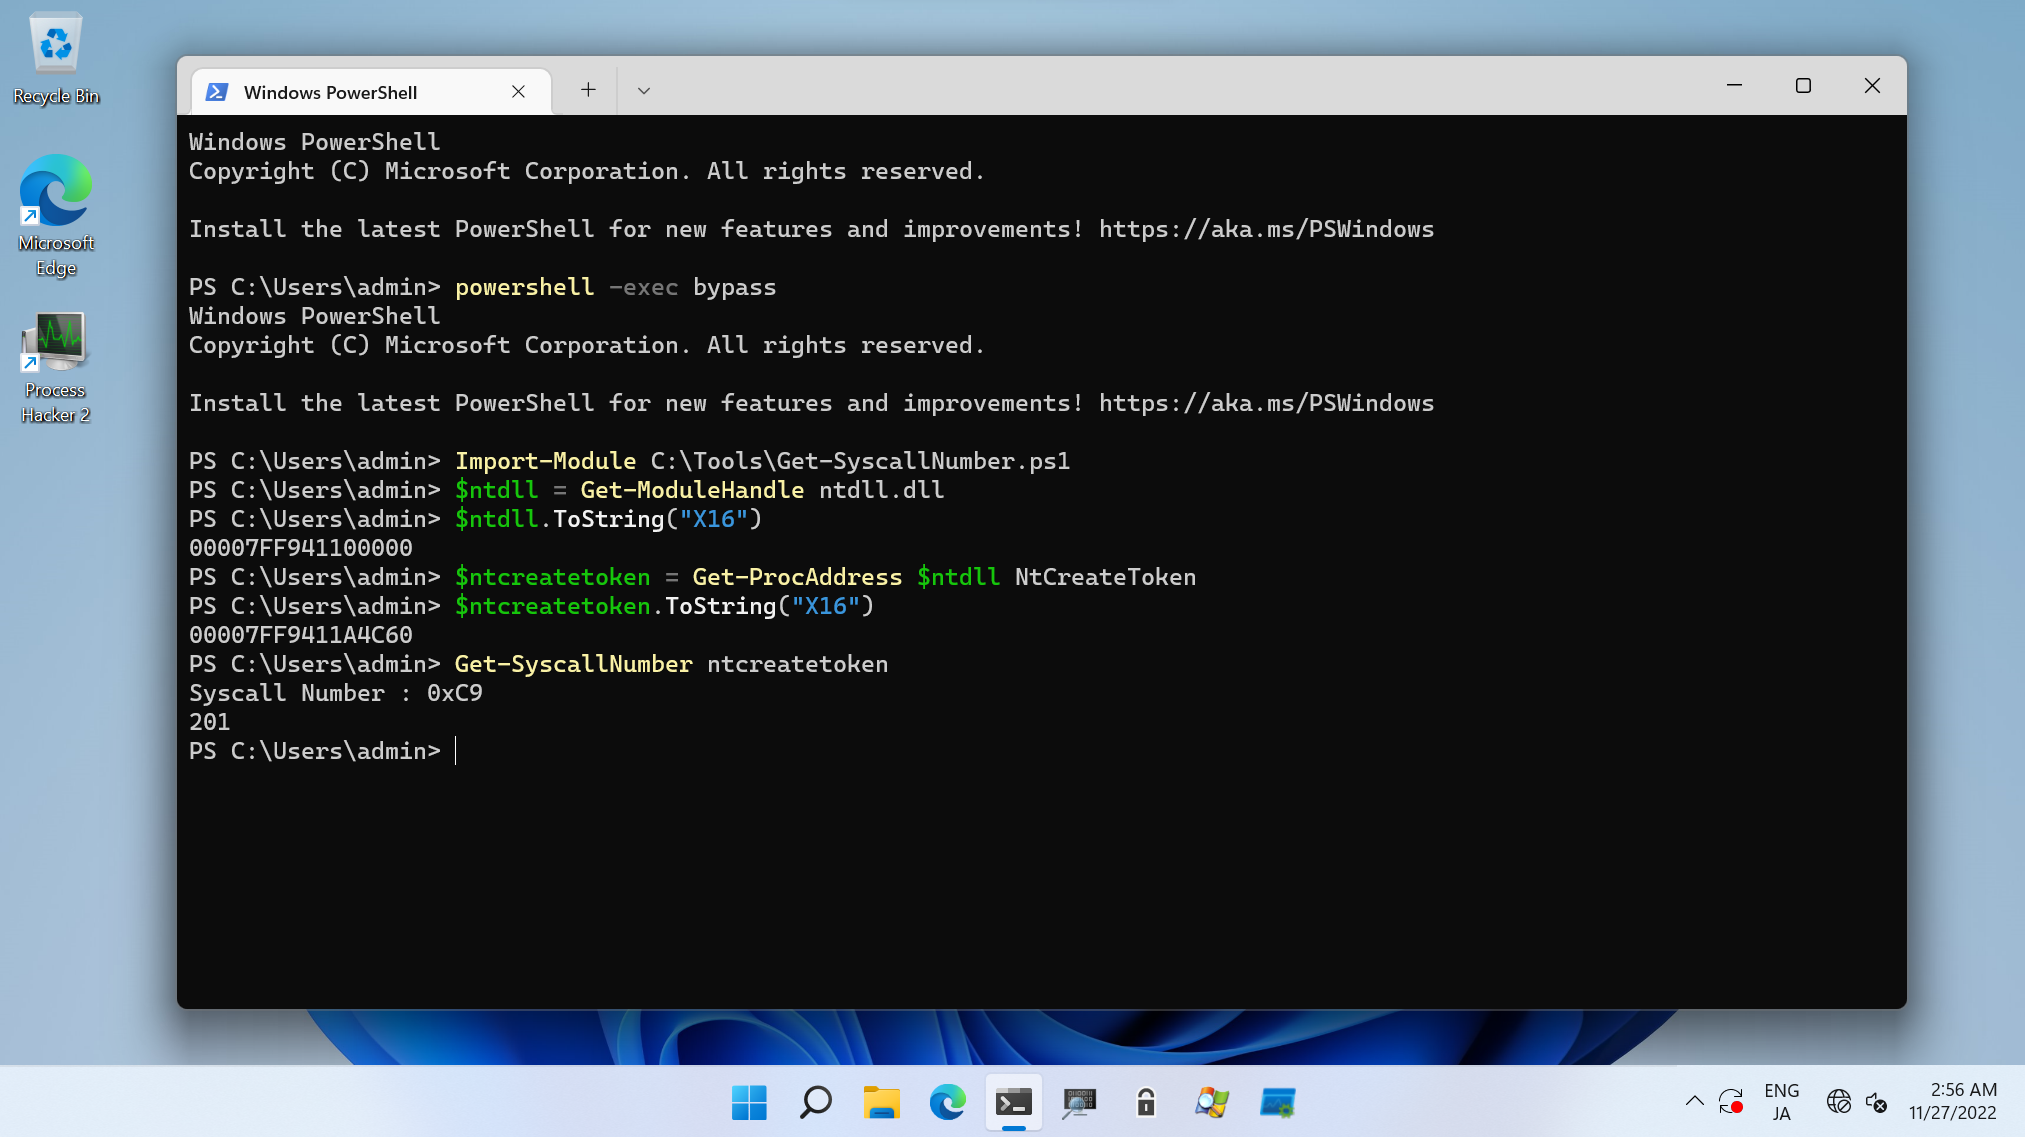 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
 vectra-ai-research/maad-af
MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
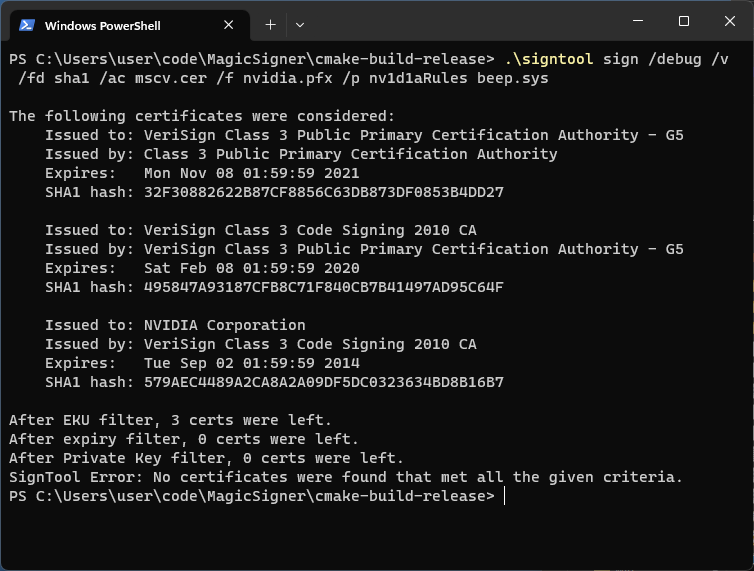 namazso/magicsigner
Signtool for expired certificates
 arosenmund/defcon33_silence_kill_edr
Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.