
CopyEscape-CVE-2026-17106
 masasron/copyescape-cve-2026-17106
PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp
adversarial-attackcontainer-escapecontainer-security+3
2
masasron/copyescape-cve-2026-17106PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp
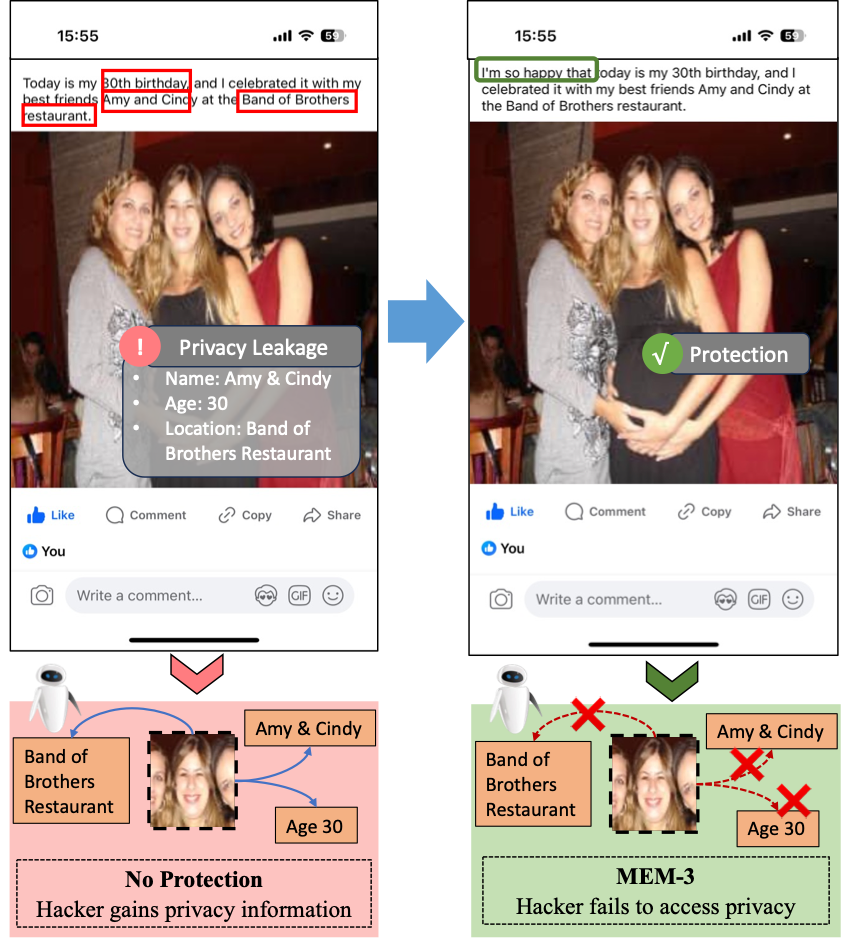 thinwayliu/multimodal-unlearnable-examples
The code for ACM MM2024 (Multimodal Unlearnable Examples: Protecting Data against Multimodal Contrastive Learning)
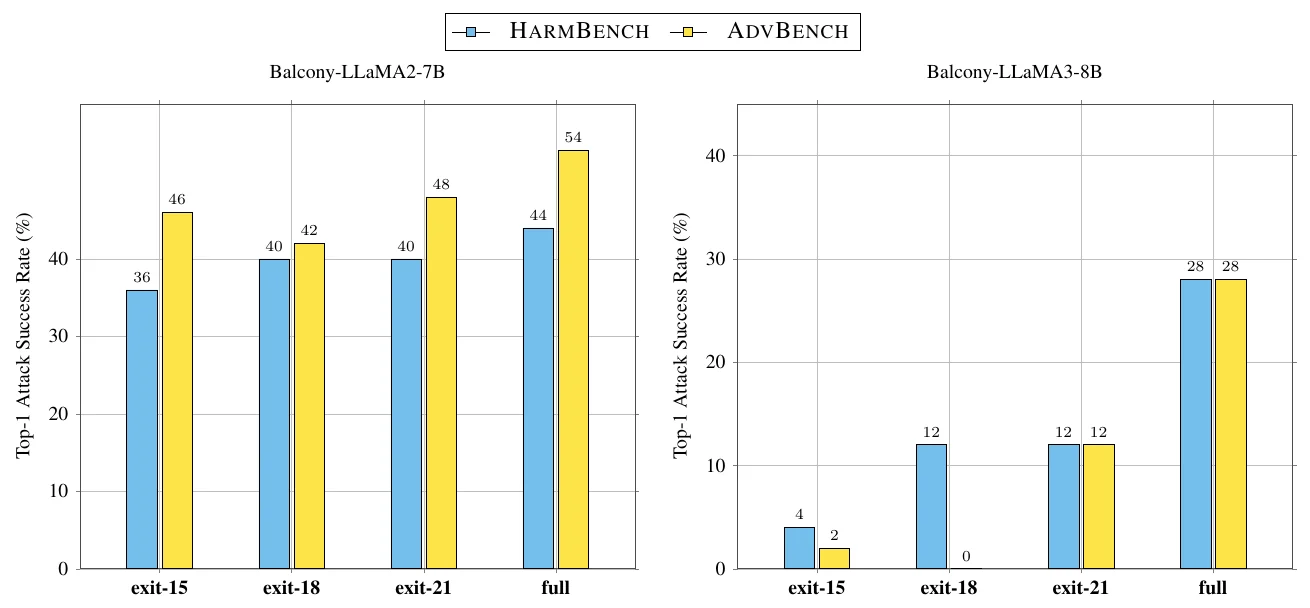 lassnajmuldeen/balcony-jailbreaking
Jailbreak vulnerability across early-exit depths LLMs. Published at NeurIPS 2026 in the FLMSec workshop
 nextronsystems/aptsimulator
A toolset to make a system look as if it was the victim of an APT attack
 netero1010/edrsilencer
A tool uses Windows Filtering Platform (WFP) to block Endpoint Detection and Response (EDR) agents from reporting security events to the server.
 saadahla/filelesspeloader
Loading Remote AES Encrypted PE in memory , Decrypted it and run it
 rosesecurity/anti-virus-evading-payloads
During the exploitation phase of a pen test or ethical hacking engagement, you will ultimately need to try to cause code to run on target system…
 redteamoperations/redcloud-os
RedCloudOS is a Cloud Adversary Simulation Operating System for Red Teams to assess the Cloud Security of Leading Cloud Service Providers (CSPs)
 binderlabs/dircreate2system
Weaponizing to get NT SYSTEM for Privileged Directory Creation Bugs with Windows Error Reporting
 saadahla/unhookingpatch
Bypass EDR Hooks by patching NT API stub, and resolving SSNs and syscall instructions at runtime
 saadahla/ntdllreflection
Bypass Userland EDR hooks by Loading Reflective Ntdll in memory from a remote server based on Windows ReleaseID to avoid opening a handle to ntdll ,…
 kudaes/split
Apply a divide and conquer approach to bypass EDRs
 mr-un1k0d3r/amsi-etw-patch
Patch AMSI and ETW
 lloydlabs/ntqueueapcthreadex-ntdll-gadget-injection
This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…
 unkvolism/fuck-etw
Bypass the Event Trace Windows(ETW) and unhook ntdll.
 frank2/blenny
A payload delivery system which embeds payloads in an executable's icon file!
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 gmh5225/bedaisy-bypass
Kernel-mode hook that intercepts, decrypts, and nullifies BEDaisy-to-service report traffic to suppress anti-cheat detection on UEFI and non-UEFI…