
CopyEscape-CVE-2026-17106
 masasron/copyescape-cve-2026-17106
PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp
adversarial-attackcontainer-escapecontainer-security+3
22
masasron/copyescape-cve-2026-17106PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp
 hackspeak/cve-2026-64638
XSS2Shell (CVE-2026-64638) WordPress pre-auth XSS to RCE PoC mirror — WordSec, MIT; for authorized security testing
 george0papasotiriou/cve-2026-21010-voip-sip-digest-authentication-replay
Python PoC for CVE-2026-21010 that replays captured SIP digest Authorization headers to bypass nonce uniqueness/expiration and make unauthorized VoIP…
 george0papasotiriou/cve-2026-1337-ai-coding-assistant-prompt-injection-to-sandbox-escape
A prompt injection in a code‑review bot that executes AI‑generated fixes in a sandbox. The sandbox uses a blacklist to prevent dangerous commands,…
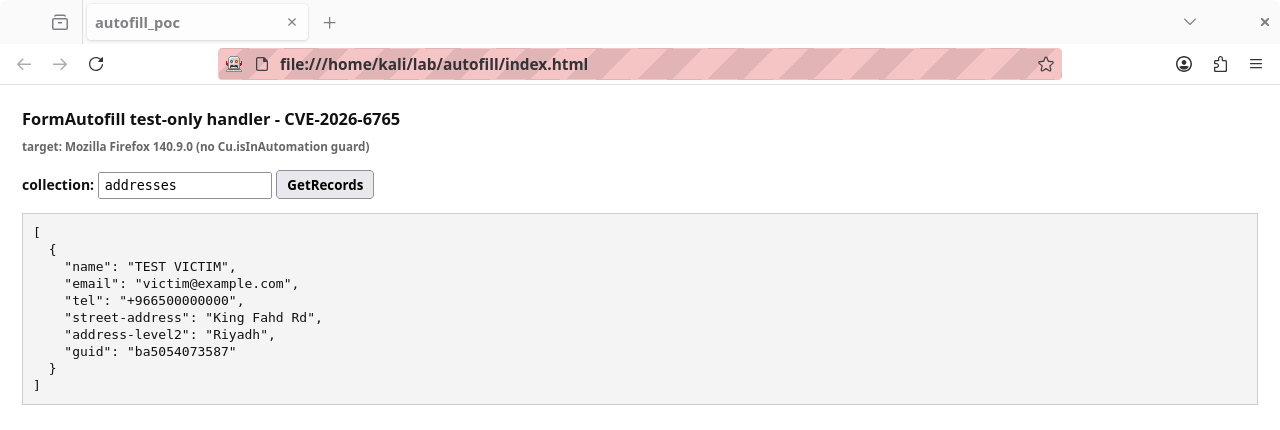 defineid/skeletonkey
CVE-2026-6765, Test only FormAutofill handlers exposed in Firefox
 george0papasotiriou/cve-2026-22007-ntp-monlist-amplification-over-ipv6
Python PoC for CVE-2026-22007: NTP monlist amplification over IPv6, including a simulated vulnerable server and spoofed UDP reflection attack.
 george0papasotiriou/cve-2026-6060-quic-handshake-amplification-via-address-validation-bypass
Educational Python PoC for a QUIC address-validation bypass that triggers handshake amplification, including vulnerable server simulation and attack…
 george0papasotiriou/cve-2026-22016-ipfs-cid-spoofing-via-multihash-length-extension
Python proof-of-concept demonstrating IPFS CID spoofing via multihash length extension, highlighting content-addressing verification flaws that can…
 george0papasotiriou/cve-2026-0101-ble-address-spoofing-via-weak-resolvable-private-address
Python PoC for CVE-2026-0101 demonstrating BLE address spoofing via replay of a captured Resolvable Private Address to impersonate a trusted…
 george0papasotiriou/cve-2026-23010-ccsds-telecommand-replay-without-sequence-number
PoC simulation of a critical CCSDS telecommand replay vulnerability in satellite command systems, demonstrating missing sequence-number validation…
 hunt-benito/the-sanitizer-is-the-weapon-cve-2026-68749-cve-2026-68750-quadratic-dos-in-elixir-html-sanitize-ex
PoC demonstrating quadratic DoS in Elixir html_sanitize_ex via crafted HTML; includes timing benchmarks, remote exploitation curl, and verification…
 george0papasotiriou/cve-2026-21016-malicious-pypi-package-install-hook-setup.py-execution-
Demonstrates how a malicious Python package executes arbitrary commands during pip install via setup.py, highlighting PyPI supply chain and…
 george0papasotiriou/cve-2026-22020-weak-seed-in-quantum-key-distribution-error-correction
Python PoC demonstrating CVE-2026-22020: exploitable weak seed in quantum key distribution privacy amplification, reducing final key entropy.
 mthamil107/db_audit_research
Self-Defeating Audits: reproducible lab showing a low-privilege PostgreSQL role reversibly blinding a trigger-based auditor + poisoning attribution…
 sonnelon/cve-2026-23744-poc
The poc of CVE-2026-23744
 george0papasotiriou/llm-jailbreak-via-chain-of-logic-injection-cve-2026-3098
Multi-stage prompt injection technique that bypasses LLM safety alignment via identity reassignment, refusal suppression, and output coercion,…
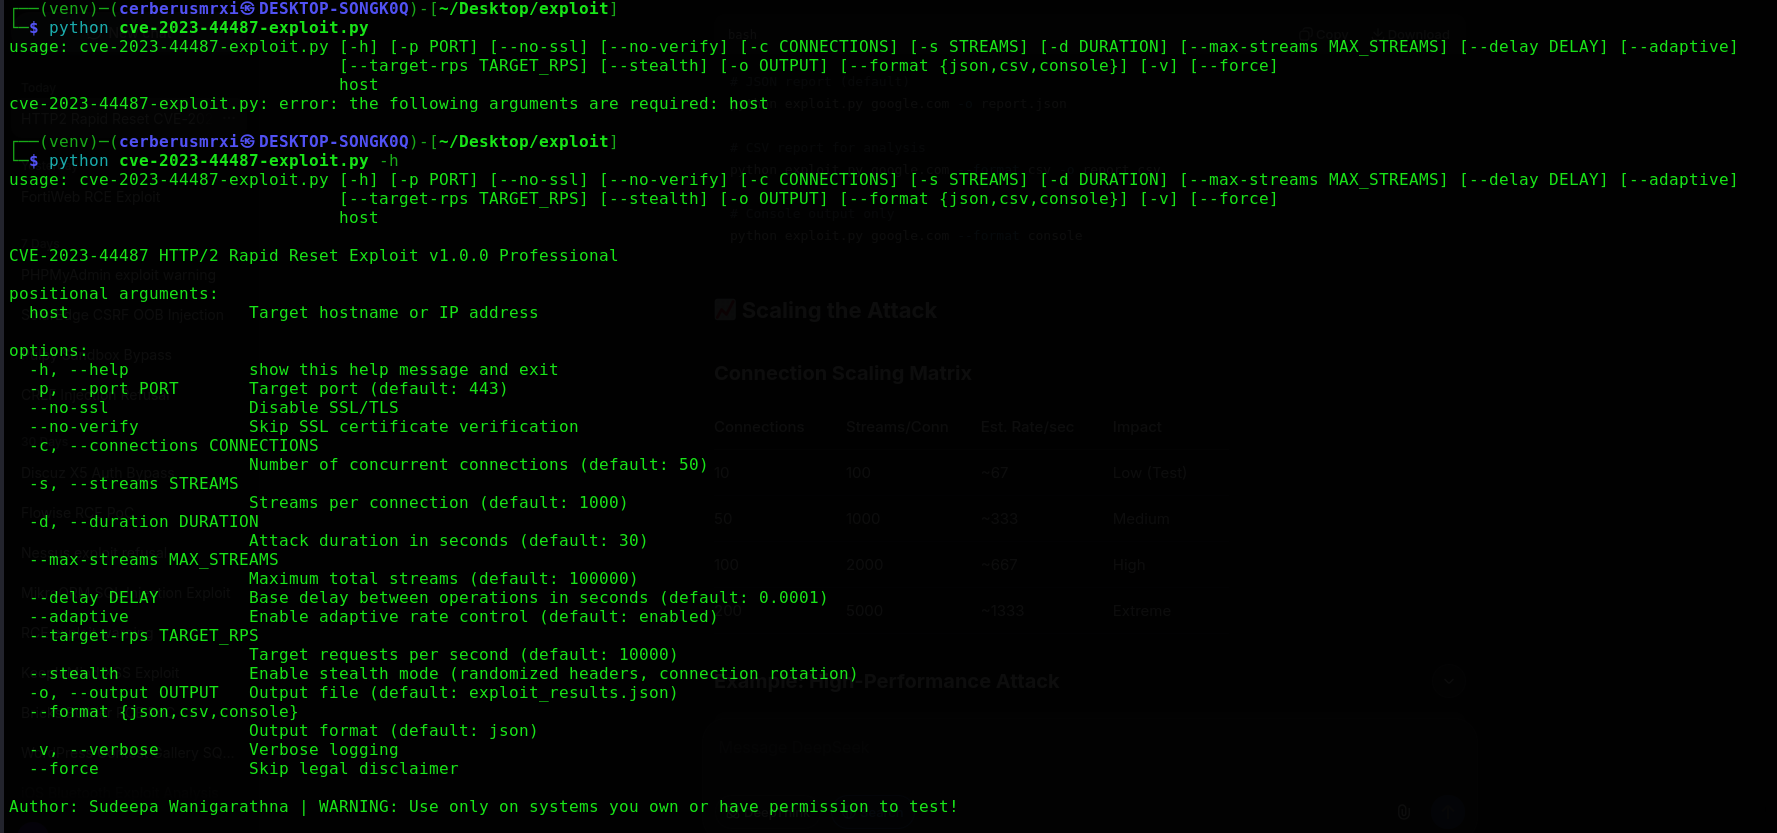 cerberusmrxi/cve-2023-44487-http2-dos-rapid-reset-exploit
Advanced CVE-2023-44487 HTTP/2 Rapid Reset vulnerability exploitation framework. Features multi-connection concurrent attacks, adaptive rate control,…
 sunandm/poc-h2-cve-2026-71554
PoC for CVE-2026-71554 - h2 duplicate Host header request smuggling primitive (fixed in 4.4.1)