

Terminator
 zeromemoryex/terminator
Reproducing Spyboy technique to terminate all EDR/XDR/AVs processes
adversarial-attackexploitationpost-exploitation+1
1.1k3 years ago
zeromemoryex/terminatorReproducing Spyboy technique to terminate all EDR/XDR/AVs processes
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
 winscripting/uac-bypass
PowerShell proof-of-concept that bypasses Windows User Account Control (UAC) to elevate privileges, intended for authorized penetration testing and…
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
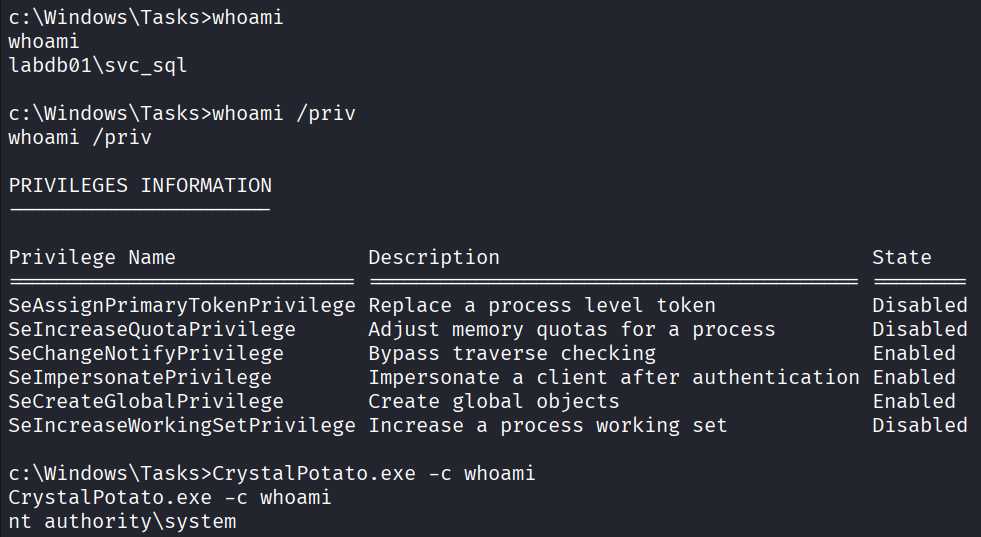 ricardojoserf/crystalpotato
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…
 deepinstinct/shimme
PoC for Windows privilege escalation and code injection using OfficeClickToRun RPC and undocumented shim manipulation to inject DLLs into SYSTEM…
 sleepthegod/windows
Windows And Ways To Break It
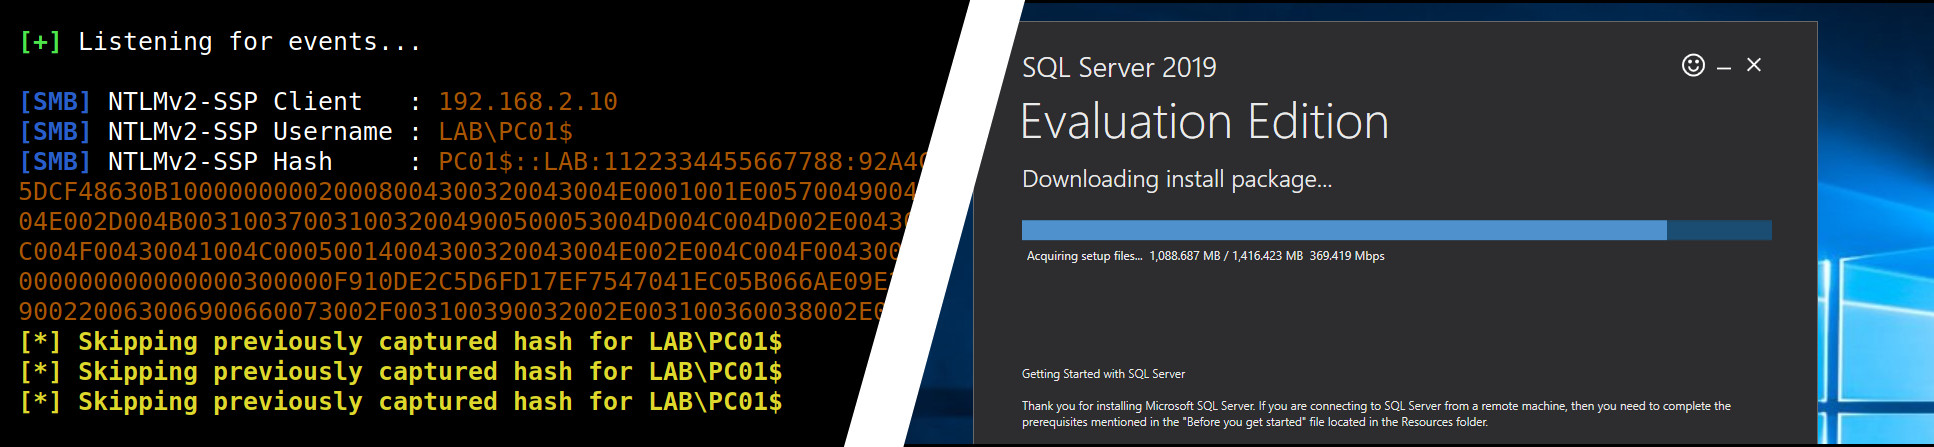 p0dalirius/mssql-analysis-coerce
A technique to coerce a Windows SQL Server to authenticate on an arbitrary machine.
 wh04m1001/diagtrackeop
Windows privilege-escalation exploit abusing SeImpersonate via DiagTrack RPC, using Secondary Logon to get an INTERACTIVE token and gain SYSTEM.
 imabee101/cve-2023-44487
PoC script for HTTP/2 Rapid Reset (CVE-2023-44487) that sends crafted HTTP/2 streams to trigger denial-of-service conditions on vulnerable servers,…
 zju-llm-safety/trace
Agentic jailbreak framework for LLM-based agents using scheme-based task decomposition, multi-turn disguising strategies, and adaptive self-evolution…
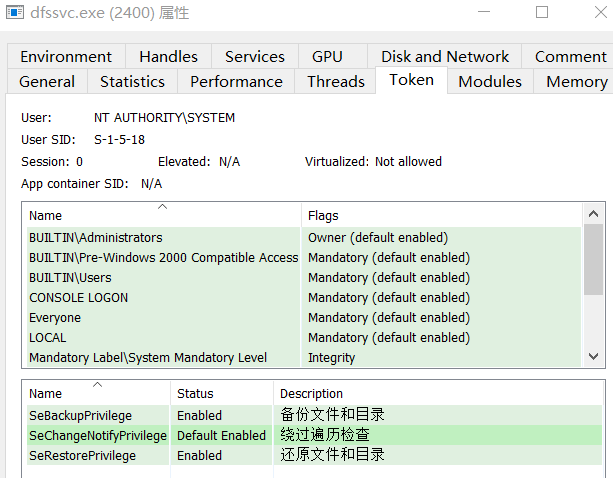 crisprss/magicnetdefs
Similar to Petitpotam, the netdfs service is enabled in Windows Server and AD environments, and the abused RPC method allows privileged processes to…
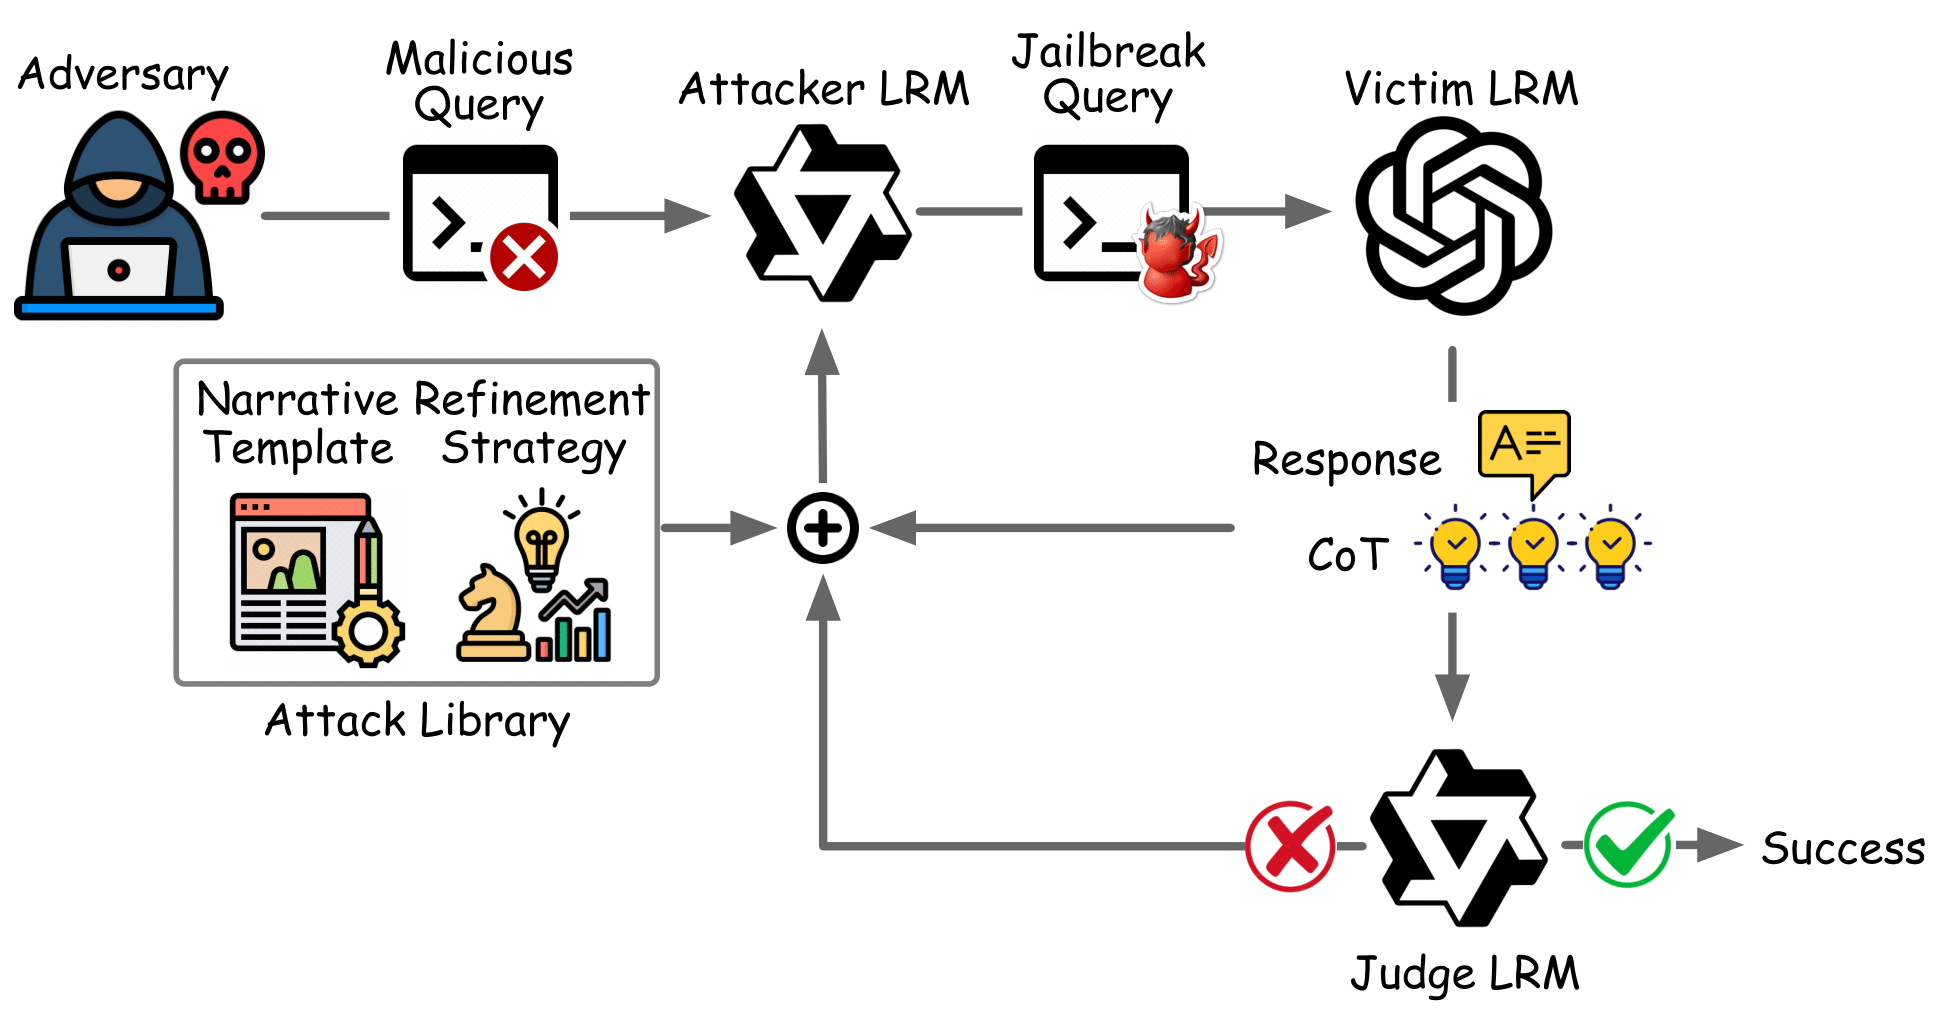 jackpurcell/autoran-public
Automated framework for hijacking safety reasoning in large reasoning models via simulated reasoning traces and iterative prompt refinement to…
 hackspeak/cve-2026-64638
XSS2Shell (CVE-2026-64638) WordPress pre-auth XSS to RCE PoC mirror — WordSec, MIT; for authorized security testing
 george0papasotiriou/cve-2026-22003-redis-lua-sandbox-escape-via-debug.sethook-
Proof-of-concept exploit for CVE-2026-22003 demonstrating Redis Lua sandbox escape via debug.sethook to execute arbitrary system commands.
 lxxexxbxx/cve-2026-44578
Proof-of-concept exploit for CVE-2026-44578 that reproduces the vulnerable condition, enabling security researchers to validate affected systems and…
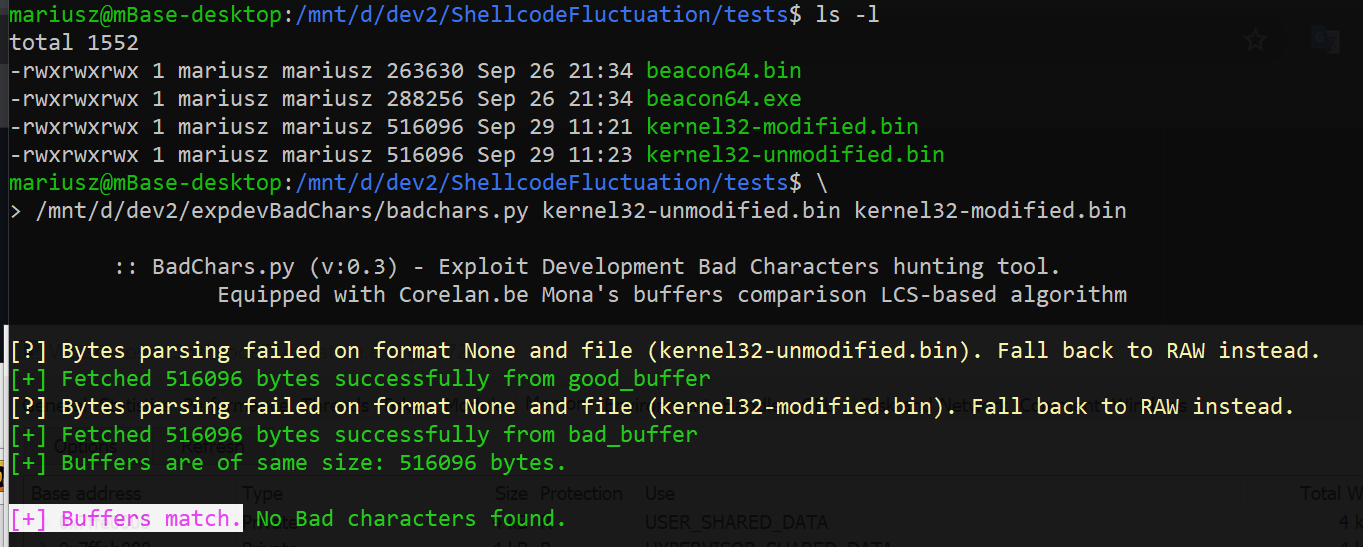 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents
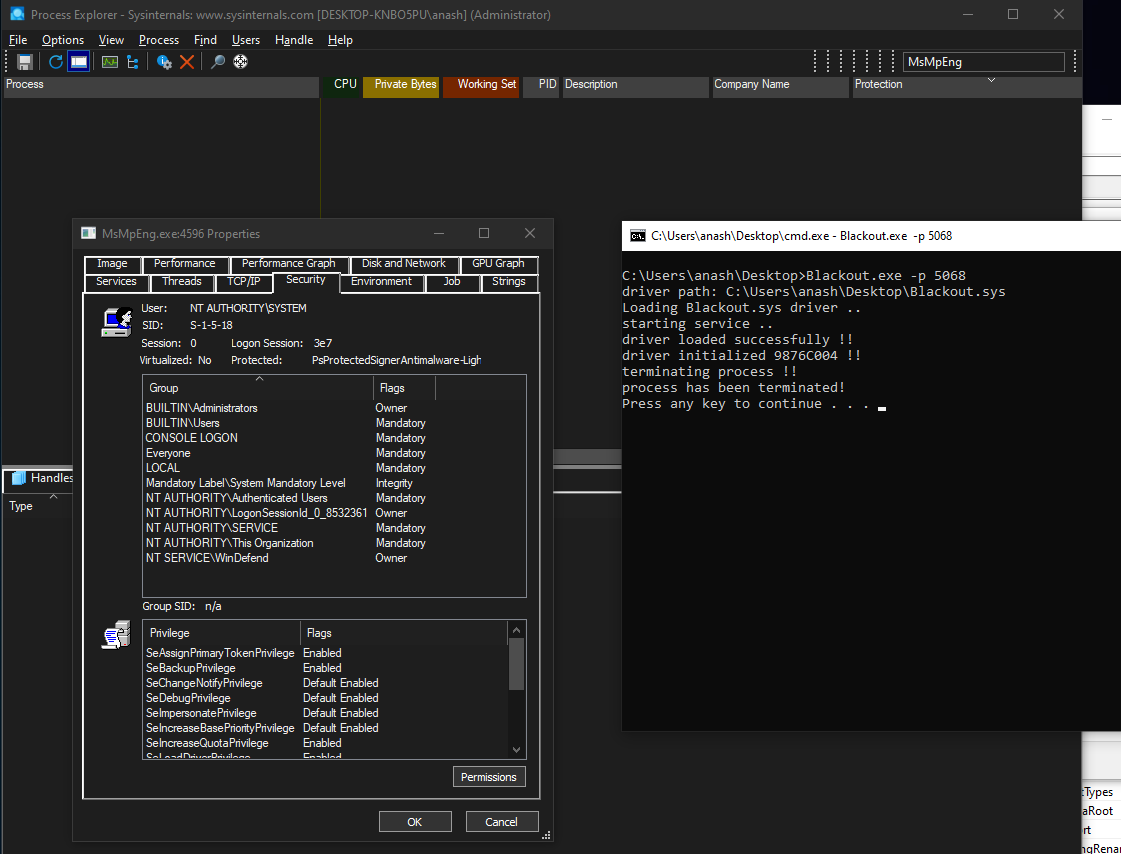 zeromemoryex/blackout
kill anti-malware protected processes ( BYOVD )