

kurasagi
 neomaster831/kurasagi
Windows 11 24H2-25H2 Runtime PatchGuard Bypass
adversarial-attackbinary-exploitationeducation+4
neomaster831/kurasagiWindows 11 24H2-25H2 Runtime PatchGuard Bypass
 vxcrypt0r/voidgate
A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
 saadahla/filelesspeloader
Loading Remote AES Encrypted PE in memory , Decrypted it and run it
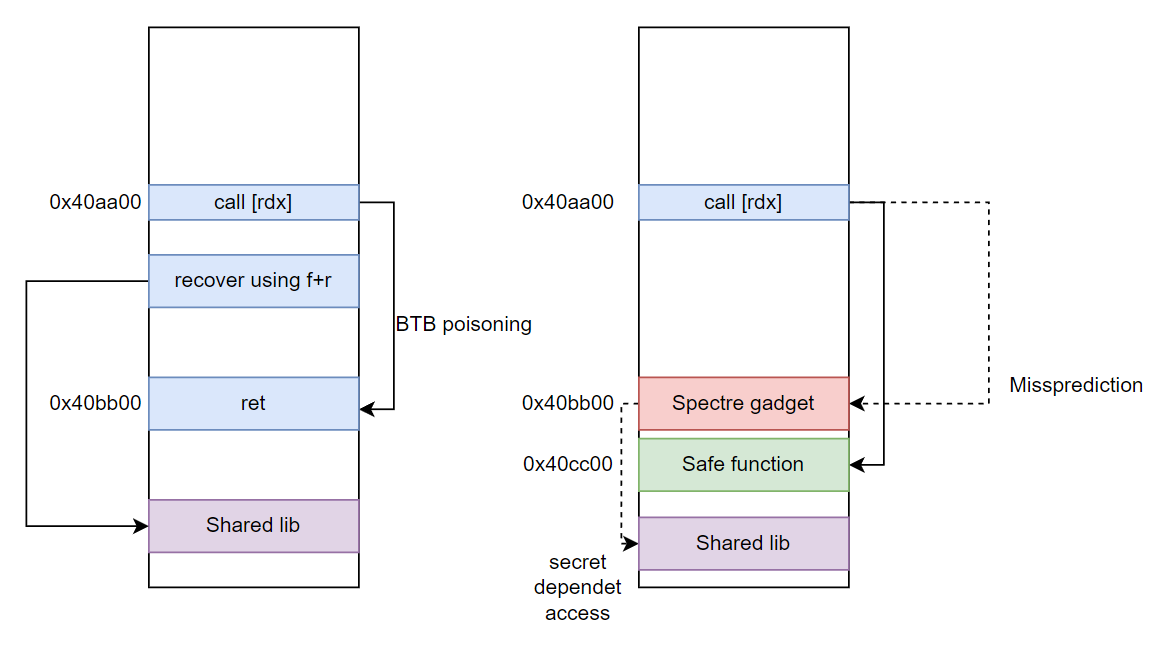 es0j/execaslr-ekoparty
Proof-of-concept exploit that bypasses ASLR on Intel CPUs by abusing branch target buffer and speculative execution to leak randomized addresses via…
 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents