SmuggleMyPayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

PoC demonstrating quadratic DoS in Elixir html_sanitize_ex via crafted HTML; includes timing benchmarks, remote exploitation curl, and verification…

XSS2Shell (CVE-2026-64638) WordPress pre-auth XSS to RCE PoC mirror — WordSec, MIT; for authorized security testing

A simple PoC on the Remote Code Execution (RCE) Vulnerability of CraftCMS designated as CVE-2025-32432 written in Go

A delicious, but malicious SSL-VPN server 🌮

image scaling attacks for multi-modal prompt injection

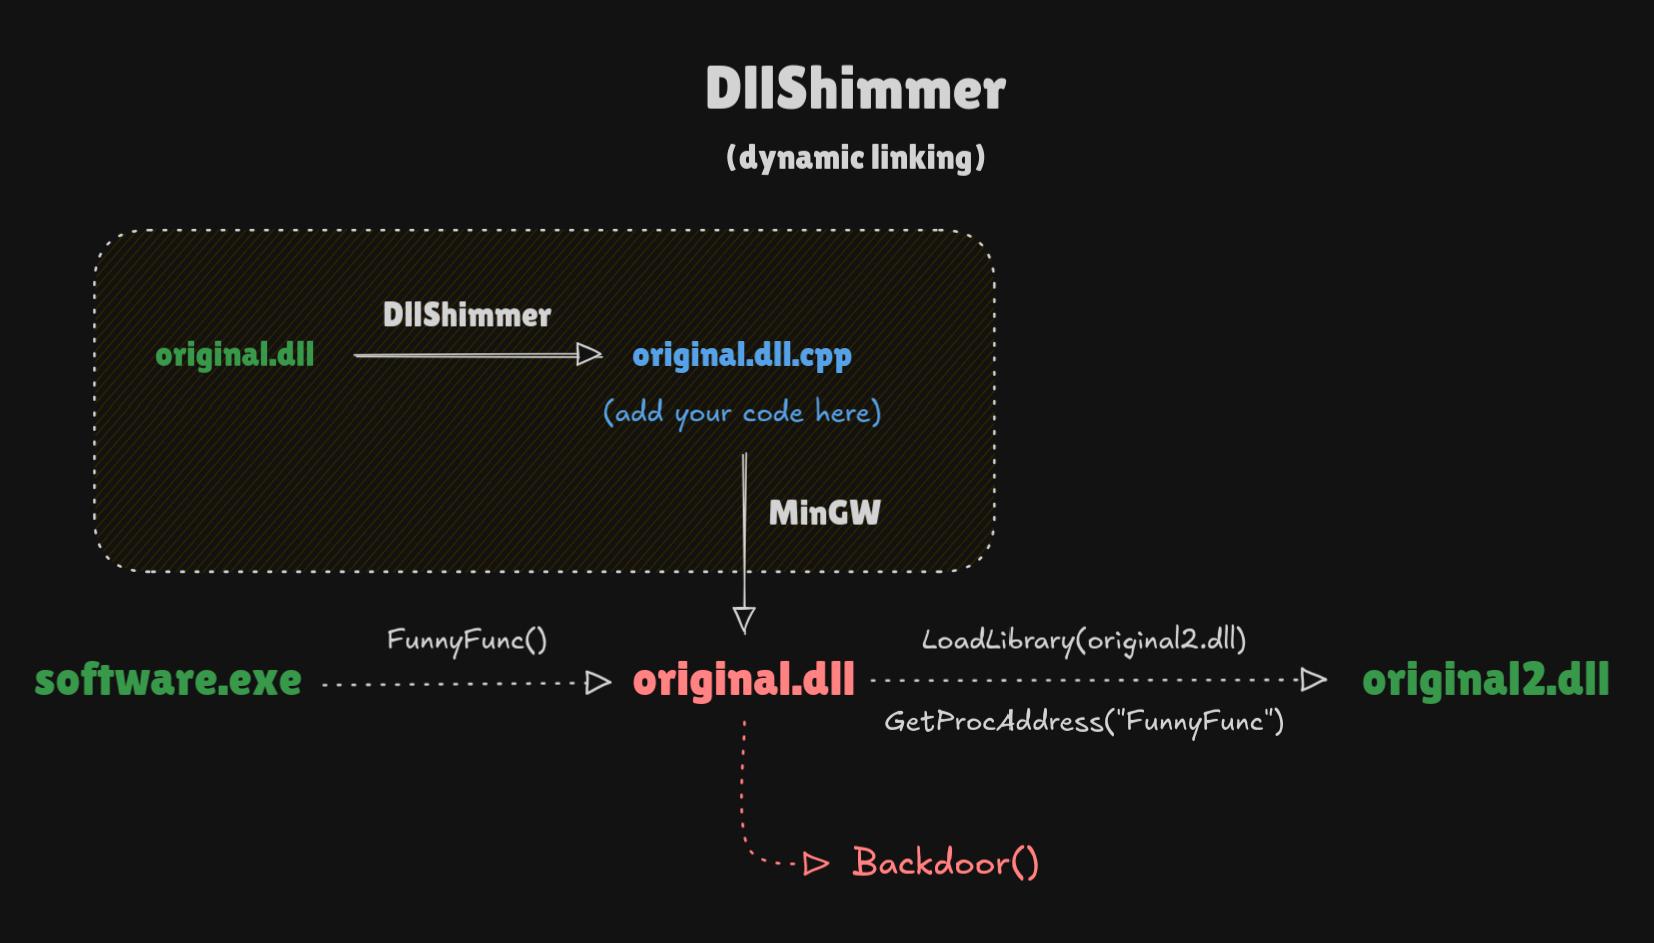
Weaponize DLL hijacking easily. Backdoor any function in any DLL.

Modern PIC implant for Windows (64 & 32 bit)

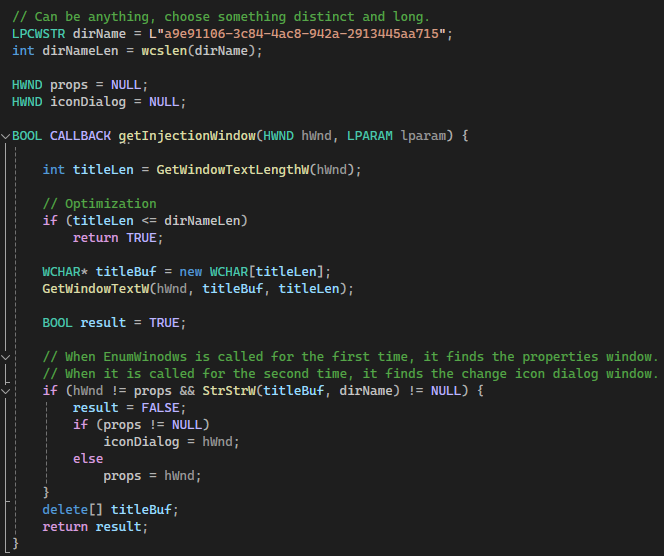
Inject DLLs into the explorer process using icons

Threadless Process Injection using remote function hooking.

A PoC demonstrating code execution via DLL Side-Loading in WinSxS binaries.

A new simple and powerfull packer for malware

A payload delivery system which embeds payloads in an executable's icon file!

macOS Initial Access Payload Generator

Jormungandr is a kernel implementation of a COFF loader, allowing kernel developers to load and execute their COFFs in the kernel.

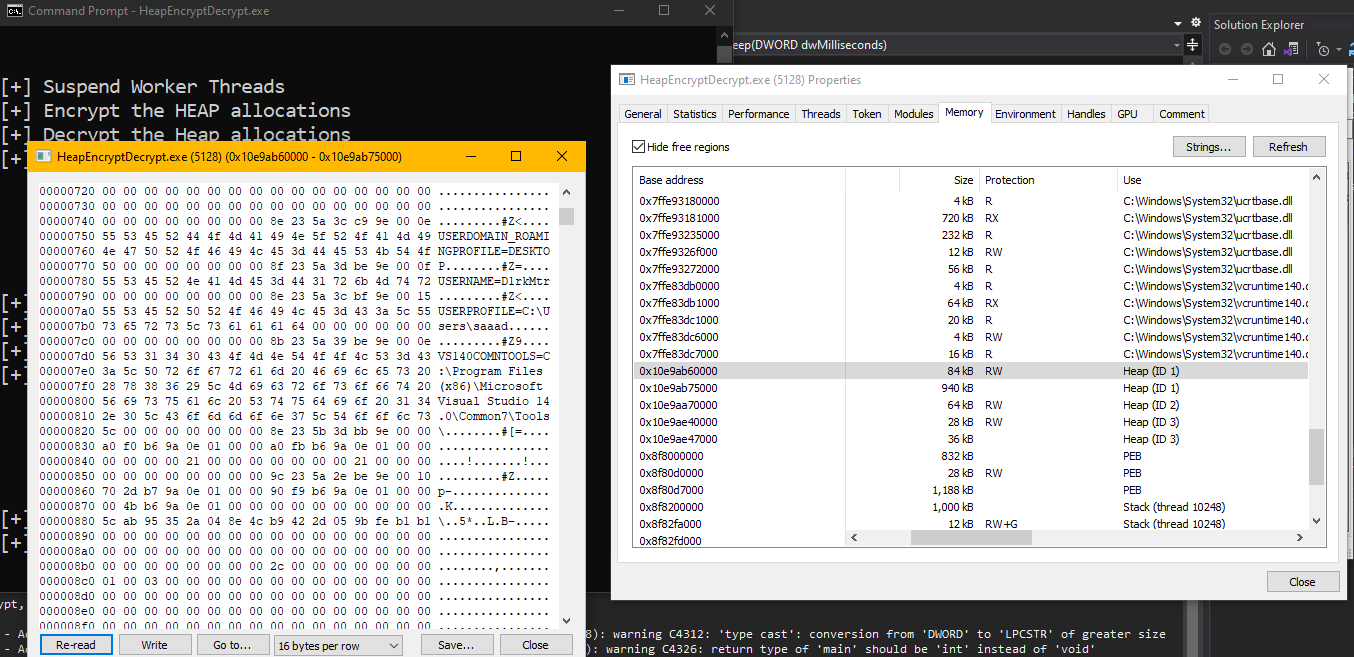
Encypting the Heap while sleeping by hooking and modifying Sleep with our own sleep that encrypts the heap

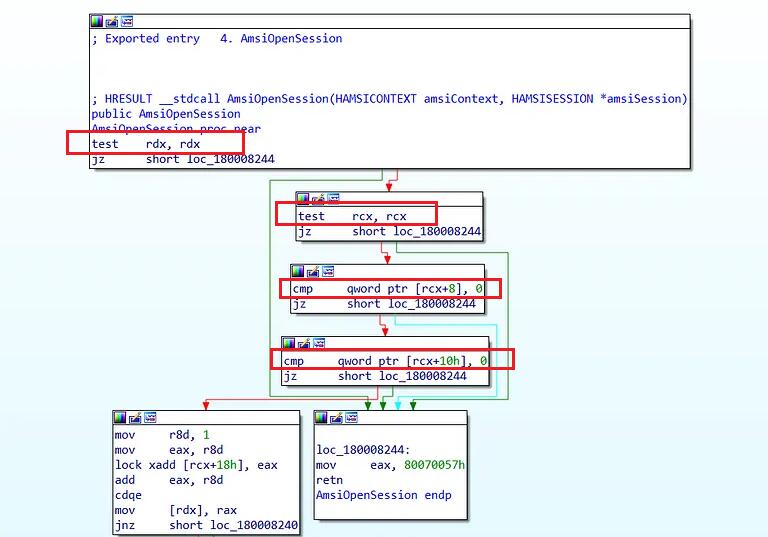
Amsi Bypass payload that works on Windwos 11

PE obfuscator with Evasion in mind