printnightmare-detection-lab

Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…

Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…

A delicious, but malicious SSL-VPN server 🌮

Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.

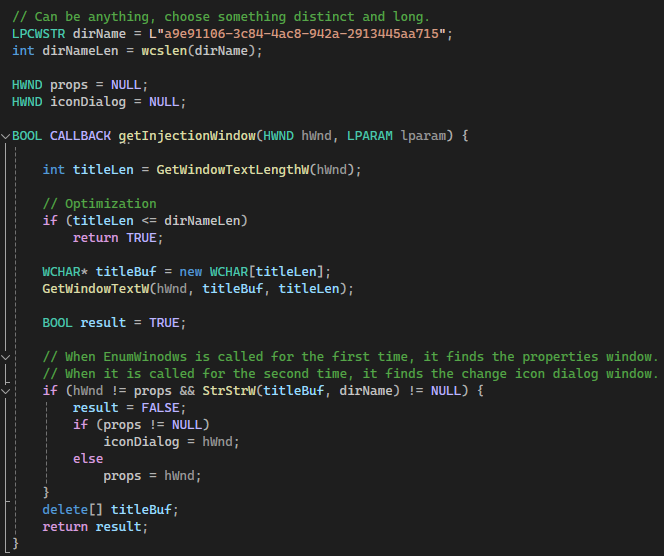
Inject DLLs into the explorer process using icons

PoC for Windows privilege escalation and code injection using OfficeClickToRun RPC and undocumented shim manipulation to inject DLLs into SYSTEM…

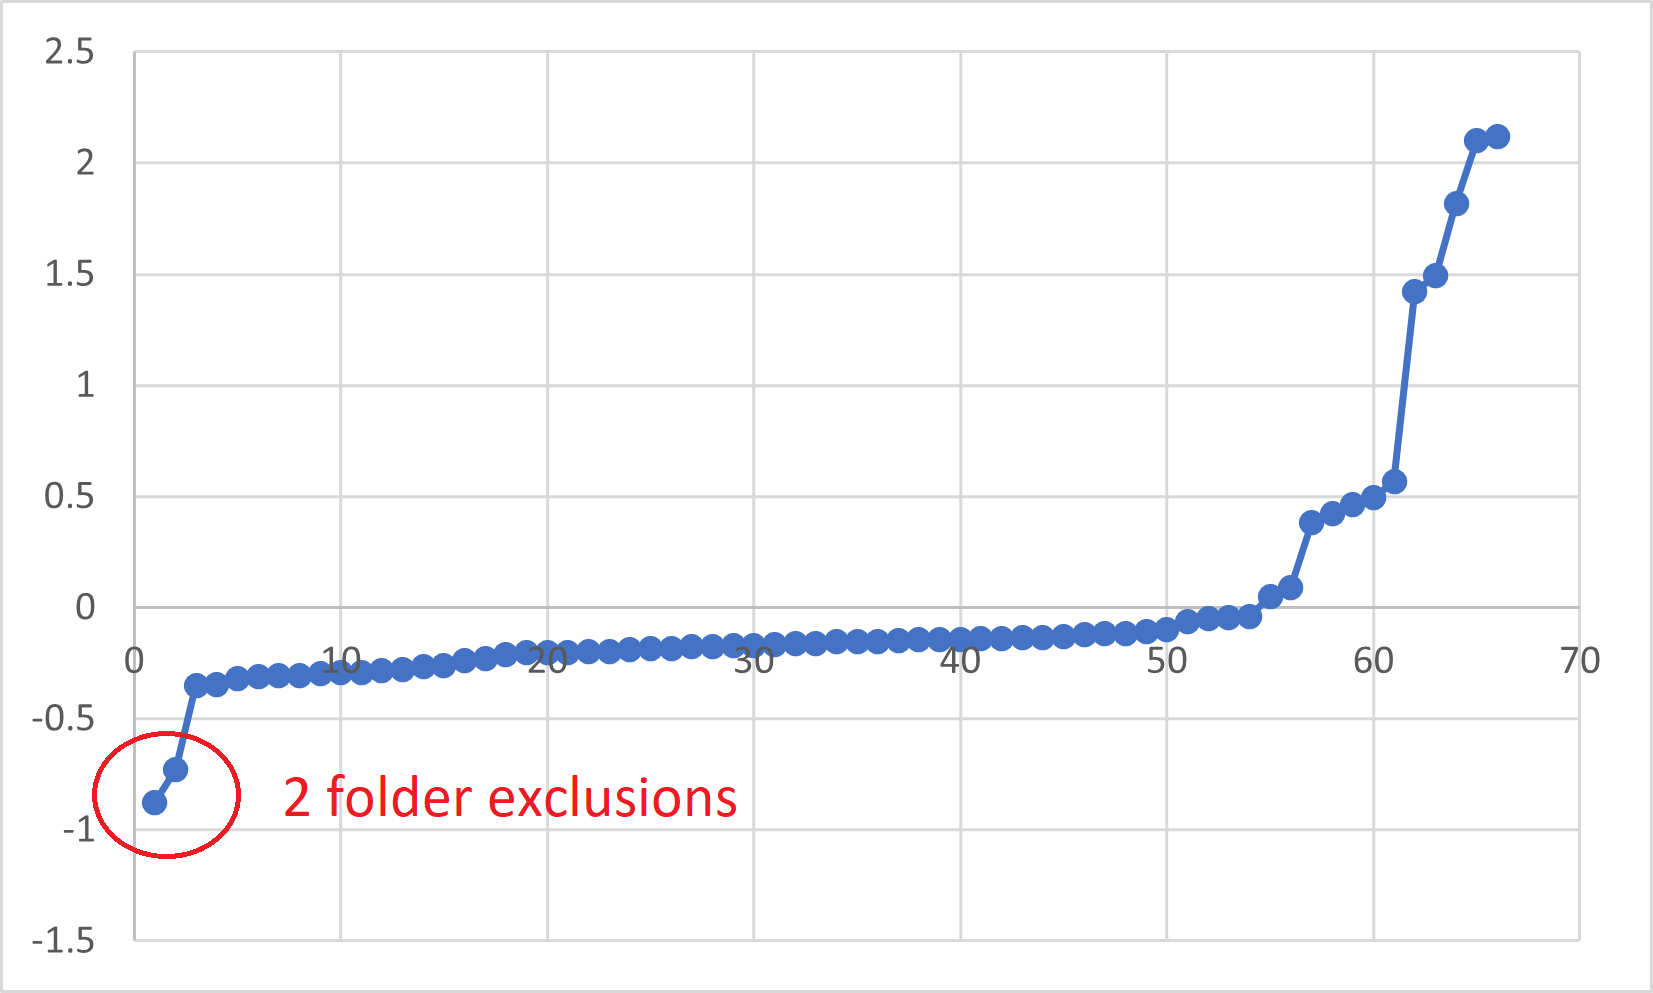
A tool to find folders excluded from AV real-time scanning using a time oracle

Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver

PrintNotifyPotato

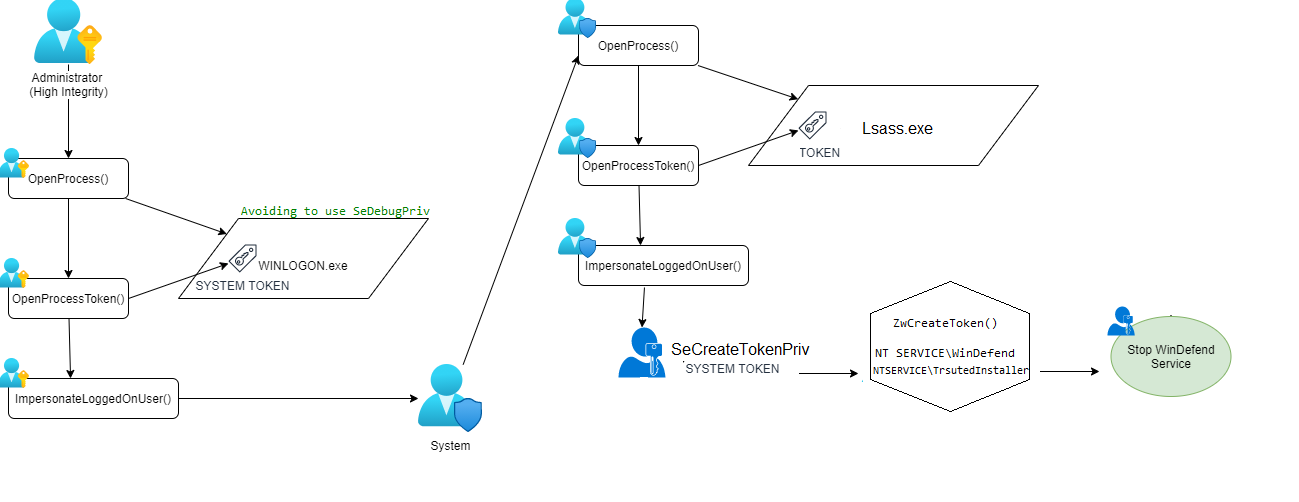
Stop Windows Defender programmatically

Resolves Windows APIs at runtime using vectored exception handlers and hashed lookups to hide imports and slow reverse engineering of offensive…

Windows privilege-escalation exploit abusing SeImpersonate via DiagTrack RPC, using Secondary Logon to get an INTERACTIVE token and gain SYSTEM.

A Python library for Secure and Explainable Machine Learning Documentation available @ https://secml.gitlab.io Follow us on Twitter @…