POC-CopyEscape-CVE-2026-17106

PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…
adversarial-attackcontainer-escapecontainer-security+5
PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…

PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp

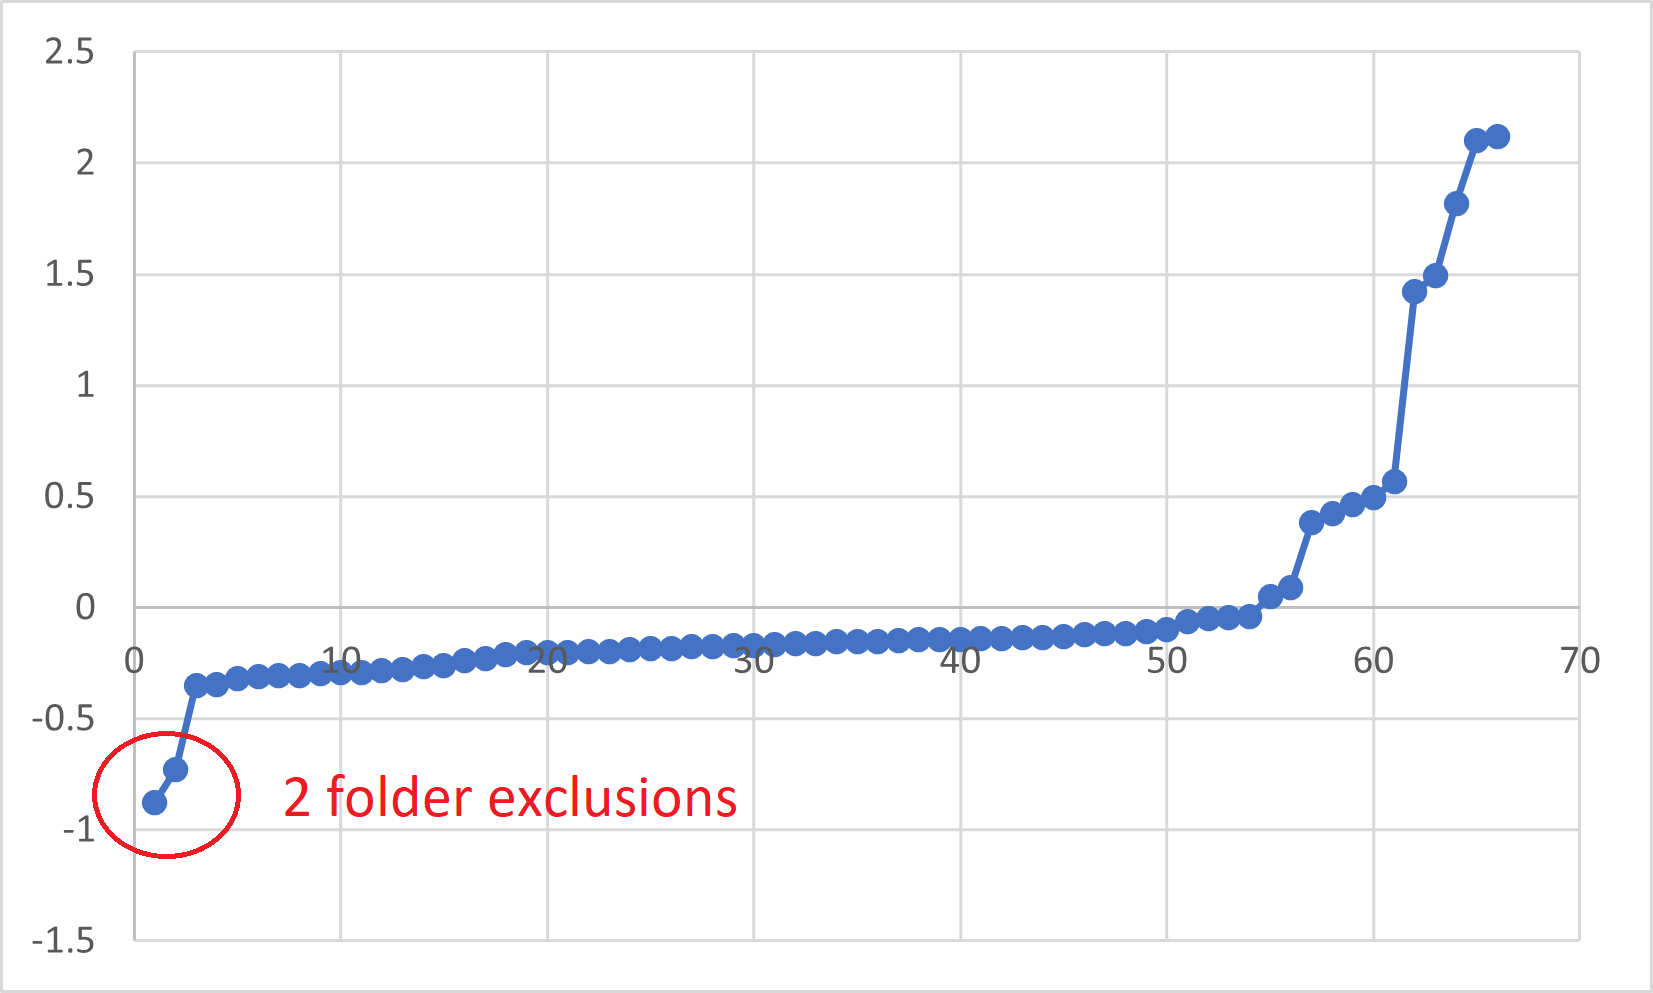
A tool to find folders excluded from AV real-time scanning using a time oracle

Python PoC for CVE-2026-22007: NTP monlist amplification over IPv6, including a simulated vulnerable server and spoofed UDP reflection attack.

Test your prompts, agents, and RAGs. Red teaming/pentesting/vulnerability scanning for AI. Compare performance of GPT, Claude, Gemini, DeepSeek, and…

Red Team K8S Adversary Emulation Based on kubectl