SmuggleMyPayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

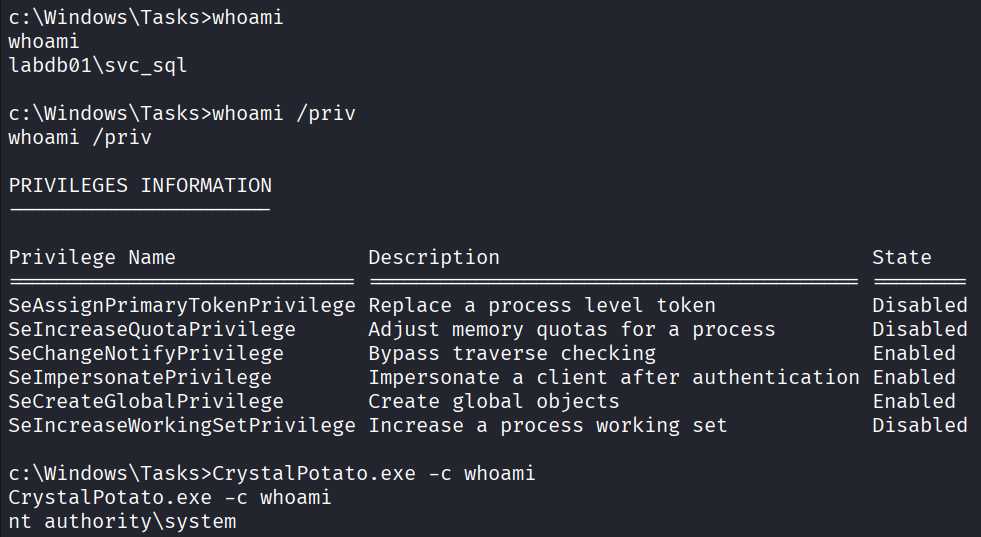
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…

Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.

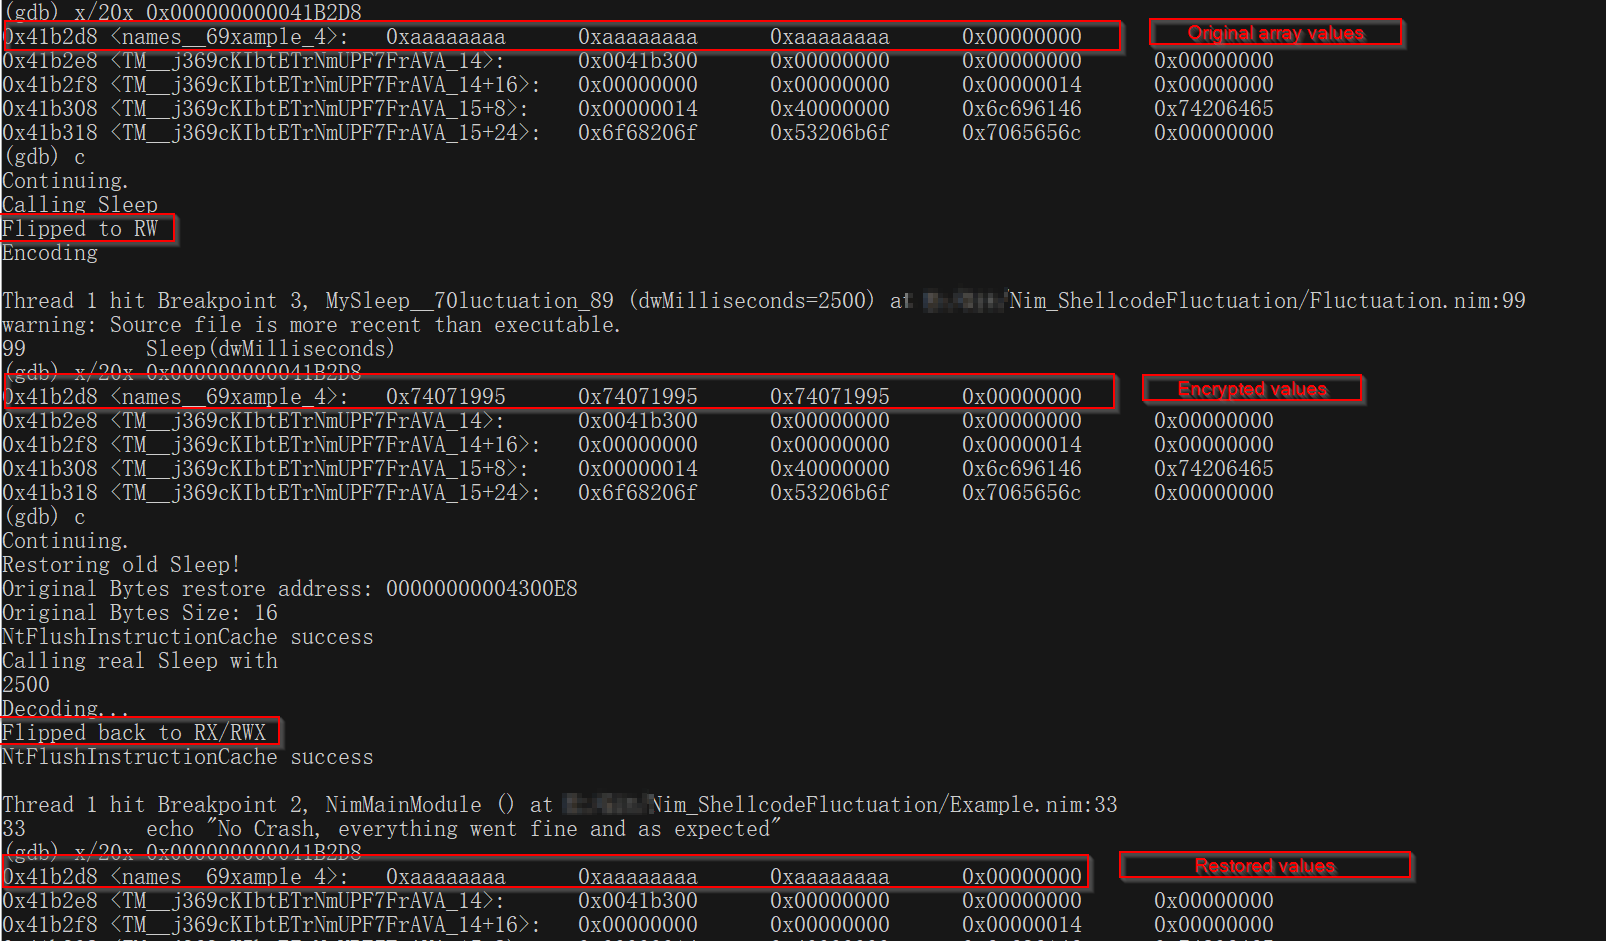
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents

A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…

Threadless Process Injection using remote function hooking.

macOS Initial Access Payload Generator

A new simple and powerfull packer for malware

Modern PIC implant for Windows (64 & 32 bit)

ShellcodeFluctuation PoC ported to Nim

A payload delivery system which embeds payloads in an executable's icon file!

PoC-Malware-TTPs

Dynamically invoke arbitrary unmanaged code from managed code without PInvoke.

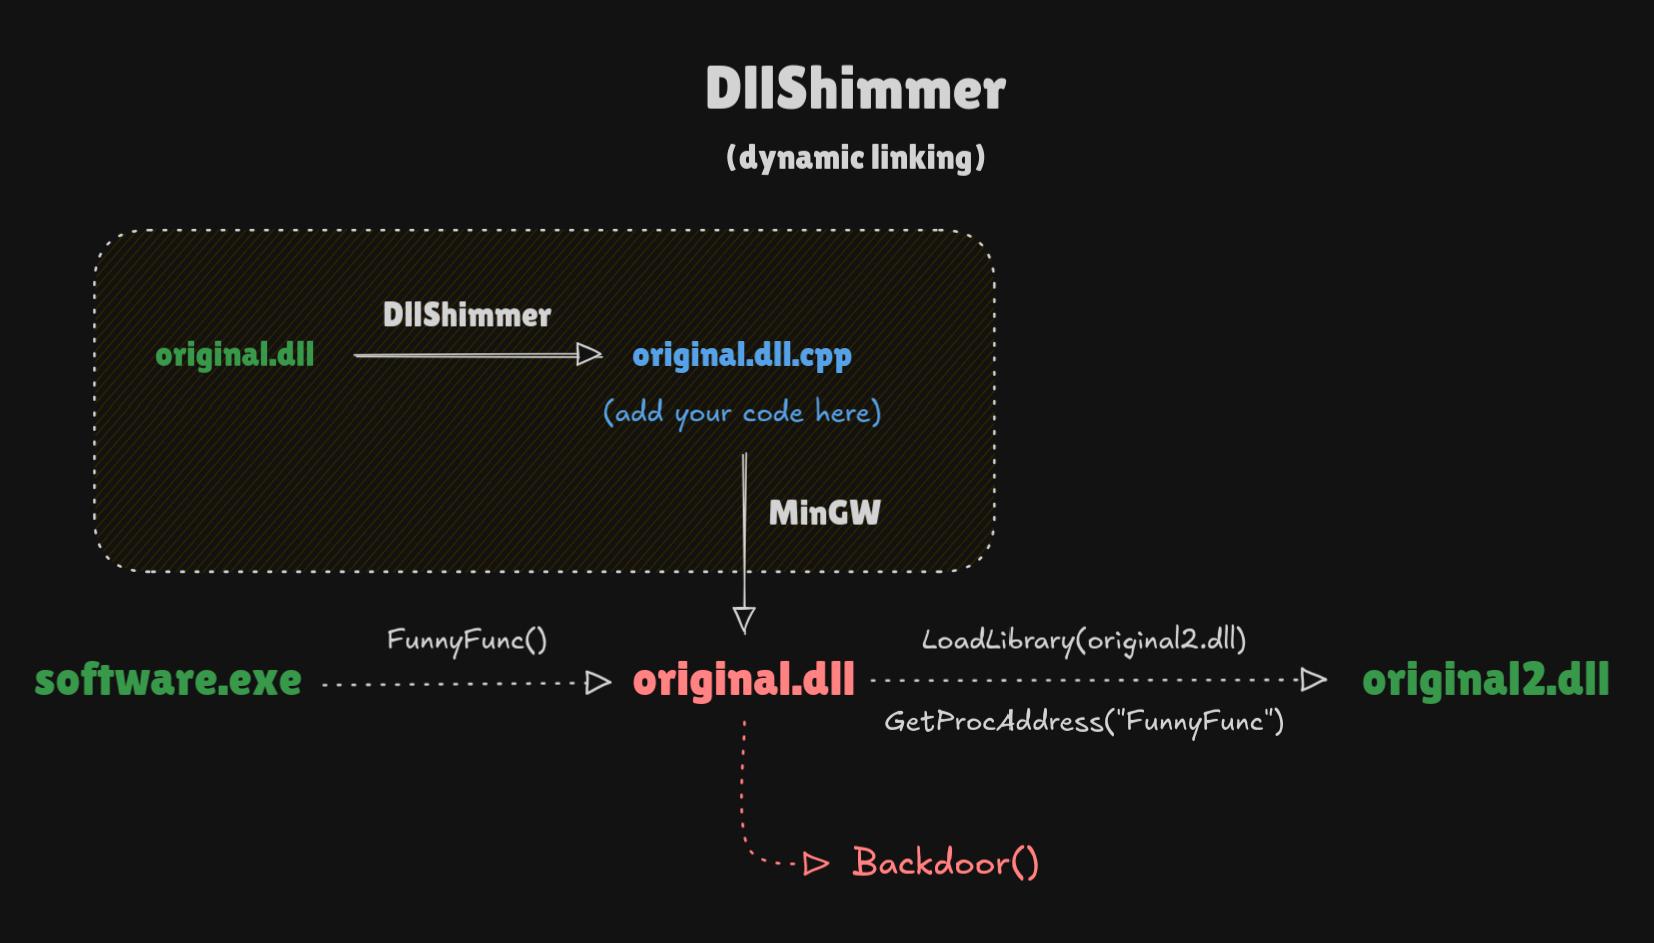
Weaponize DLL hijacking easily. Backdoor any function in any DLL.

A delicious, but malicious SSL-VPN server 🌮

A PoC demonstrating code execution via DLL Side-Loading in WinSxS binaries.

Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC

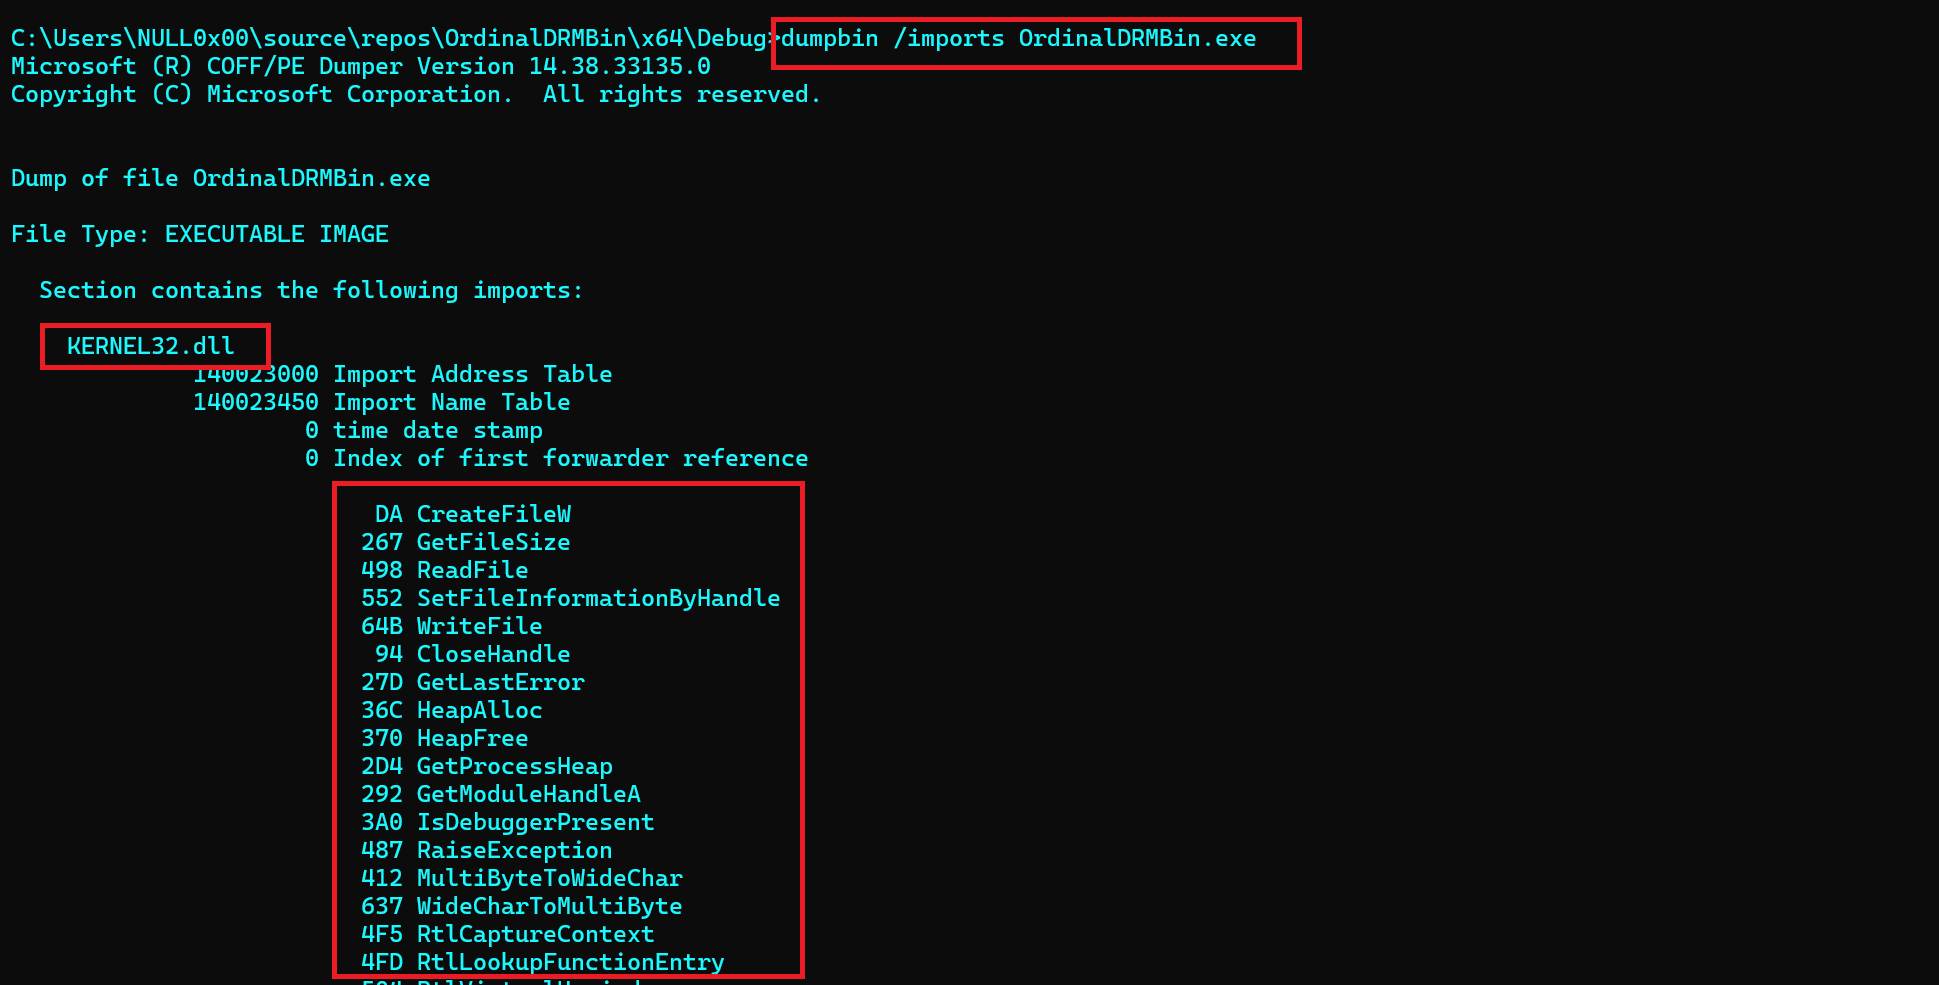
Create Anti-Copy DRM Malware