

RTA
 endgameinc/rta
Scripted framework for simulating over 50 MITRE ATT&CK techniques to test blue team detection capabilities. Includes Python scripts and a compiled…
adversarial-attackeducationlabs-practice+2
endgameinc/rtaScripted framework for simulating over 50 MITRE ATT&CK techniques to test blue team detection capabilities. Includes Python scripts and a compiled…
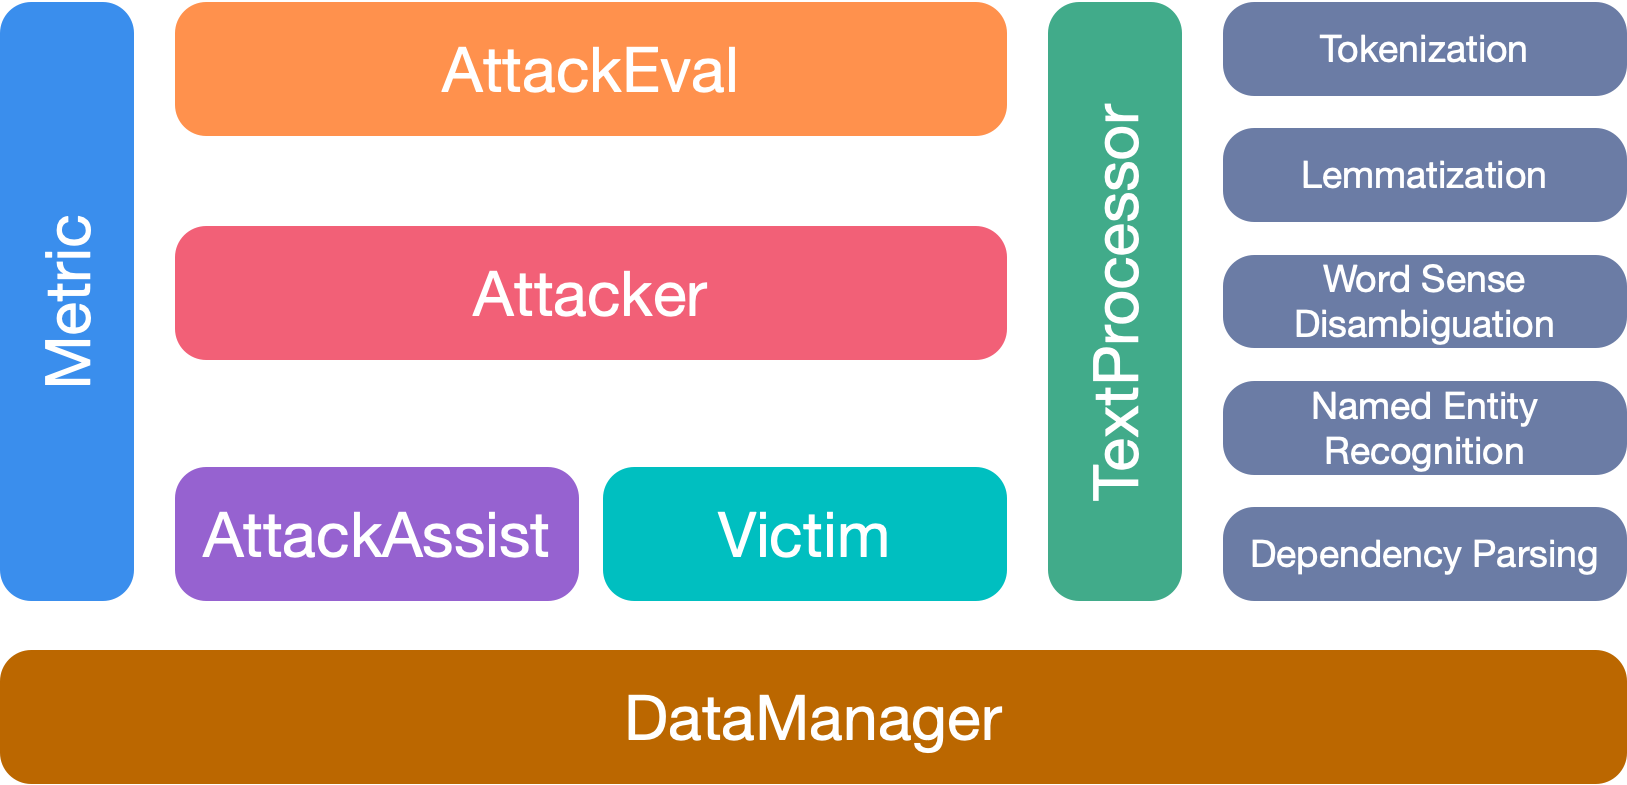 thunlp/openattack
An Open-Source Package for Textual Adversarial Attack.
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 soufianetahiri/teamsntlmleak
Leak NTLM via Website tab in teams via MS Office
 twosevenonet/wsass
This is the tool to dump the LSASS process on modern Windows 11
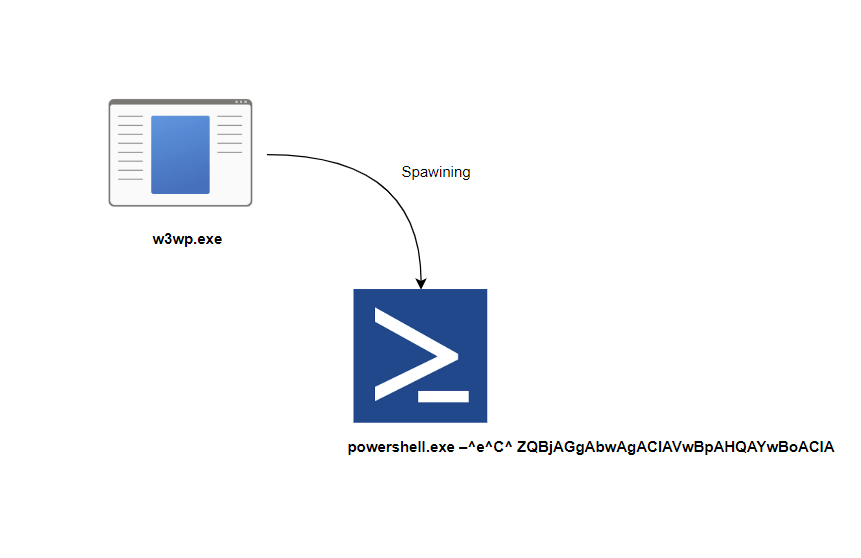 alwashali/detection-validation
Detection rule validation
 rasta-mouse/process-inject-kit
Port of Cobalt Strike's Process Inject Kit