BEAR-C2
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
adversarial-attackcommand-and-controldata-exfiltration+8
711
s3n4t0r-0x0/bear-c2The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 guillaumemeyer/watermarks-remover
A privacy-first app that strips AI watermarks from content you own.
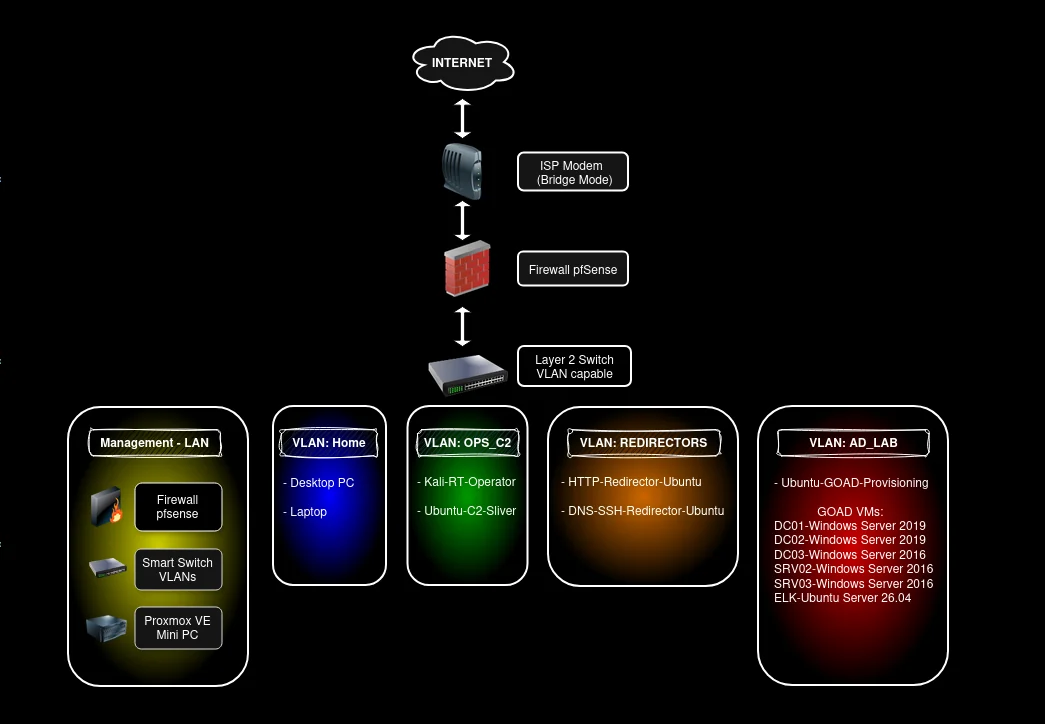 pho5nix/red-team-goad-lab-proxmox
Build guide for Red Teaming home lab. GOAD lab setup in Proxmox and pfSense, Operator/C2 and Redirectors.
 kaill-jlq/mmskillrisk
Benchmark and evaluation harness testing whether LLM agents resist malicious instructions hidden in multimodal skill images, with 108 cases across…
 davidcarliez/trustmebro
Bypass llm guardrails by confusing it with fabricated tool output.
 secdev02/easytokens
Kali365 - EvilTokens Replica
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 darkcodersc/sharpftpc2
A Streamlined FTP-Driven Command and Control Conduit for Interconnecting Remote Systems.
 datadog/stratus-red-team
:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud
 atsukisato/pgm-attack
Research code for poisoning attacks on the PGM-index, demonstrating how to craft adversarial data to degrade learned index performance.
 microsoft/ai-red-teaming-playground-labs
AI Red Teaming playground labs to run AI Red Teaming trainings including infrastructure.
 masasron/copyescape-cve-2026-17106
PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp
 686f6c61/poc-copyescape-cve-2026-17106
PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…
 george0papasotiriou/cve-2026-5556-kubernetes-admission-controller-bypass-via-case-sensitivity
Exploit PoC and vulnerable admission webhook for CVE-2026-5556, demonstrating Kubernetes admission controller bypass via case-sensitive pod name…
 borealisai/stepjack
Benchmarking framework for evaluating computer-use AI agents against multi-step indirect prompt injection, with automatic adversarial goal…
 owasp/ai-vulnerabilities-playground
Hands-on AI security lab platform with 50+ scenarios across prompt injection, agentic system exploitation, model manipulation, and MCP trust boundary…