
 rajus-agent/orbit-tracer

Orbit Tracer Security Agent for intelligent security remediation. Traces vulnerability blast radius using Orbit's knowledge graph, scores risk, identifies code owners, and orchestrates secure code generation—reducing analysis from 4+ hours to minutes. Automates vulnerability analysis, risk assessment, and secure code generation with human-in-the-loop approval. Works with any project structure, 7+ languages.
Automate security vulnerability analysis, risk assessment, and remediation across your entire codebase using AI and Orbit's knowledge graph


Security teams face a critical challenge: Finding vulnerabilities is fast. Fixing them takes forever.
Manual vulnerability remediation workflow:
1. SAST scan finds vulnerability         (~5 minutes)
2. Security engineer analyzes impact     (~2 hours)
3. Developer creates fix                 (~1 hour)
4. Code review and approval              (~30 minutes)
5. Merge and deploy                      (~30 minutes)

Total: 4+ hours per vulnerability
With hundreds of findings across multiple codebases, teams drown in manual work while security risks compound.
Orbit Tracer transforms security remediation from hours to 45 seconds.
Orbit Tracer automated workflow:
Finding → Blast Radius Analysis → Risk Scoring → MR Creation

45 seconds. End of story.
Using GitLab's Orbit knowledge graph and Claude agent, Orbit Tracer:
Result: 99.8% time savings. 100% human oversight.
| Approach | Manual | SAST Only | Orbit Tracer |
|---|---|---|---|
| Find vulnerabilities | Hours | Minutes | Minutes |
| Understand impact | Hours | No | Seconds (Orbit) |
| Generate fix | Hours | No | Seconds (Claude) |
| Create MR | Manual | No | Automatic |
| Human approval | Manual | N/A | ✅ Required |
| Total time | 4+ hours | 30+ minutes | 45 seconds |
Orbit Tracer includes two complementary security agents:
Fully automated security remediation workflow
.agents/flows/orbit-tracer/v1.ymlInteractive security analysis agent for security teams
Try the interactive agent: Ask about a security finding to see blast radius, affected services, and risk scoring!
STEP 1: Get Finding
        Extract vulnerability from GitLab SAST scan
               ↓
STEP 2: Query Orbit Knowledge Graph
        3-hop dependency tracing → Blast radius analysis
               ↓
STEP 3: Analyze Risk with Claude Agent
        Risk scoring (1-10) + Business impact assessment
               ↓
STEP 4: Check Approval Threshold (Human-In-The-Loop)
        Critical findings require human approval
               ↓
STEP 5: Draft Secure Code
        Claude generates remediation in detected language
               ↓
STEP 6: Create Merge Request
        GitLab MR with secure code, description, labels
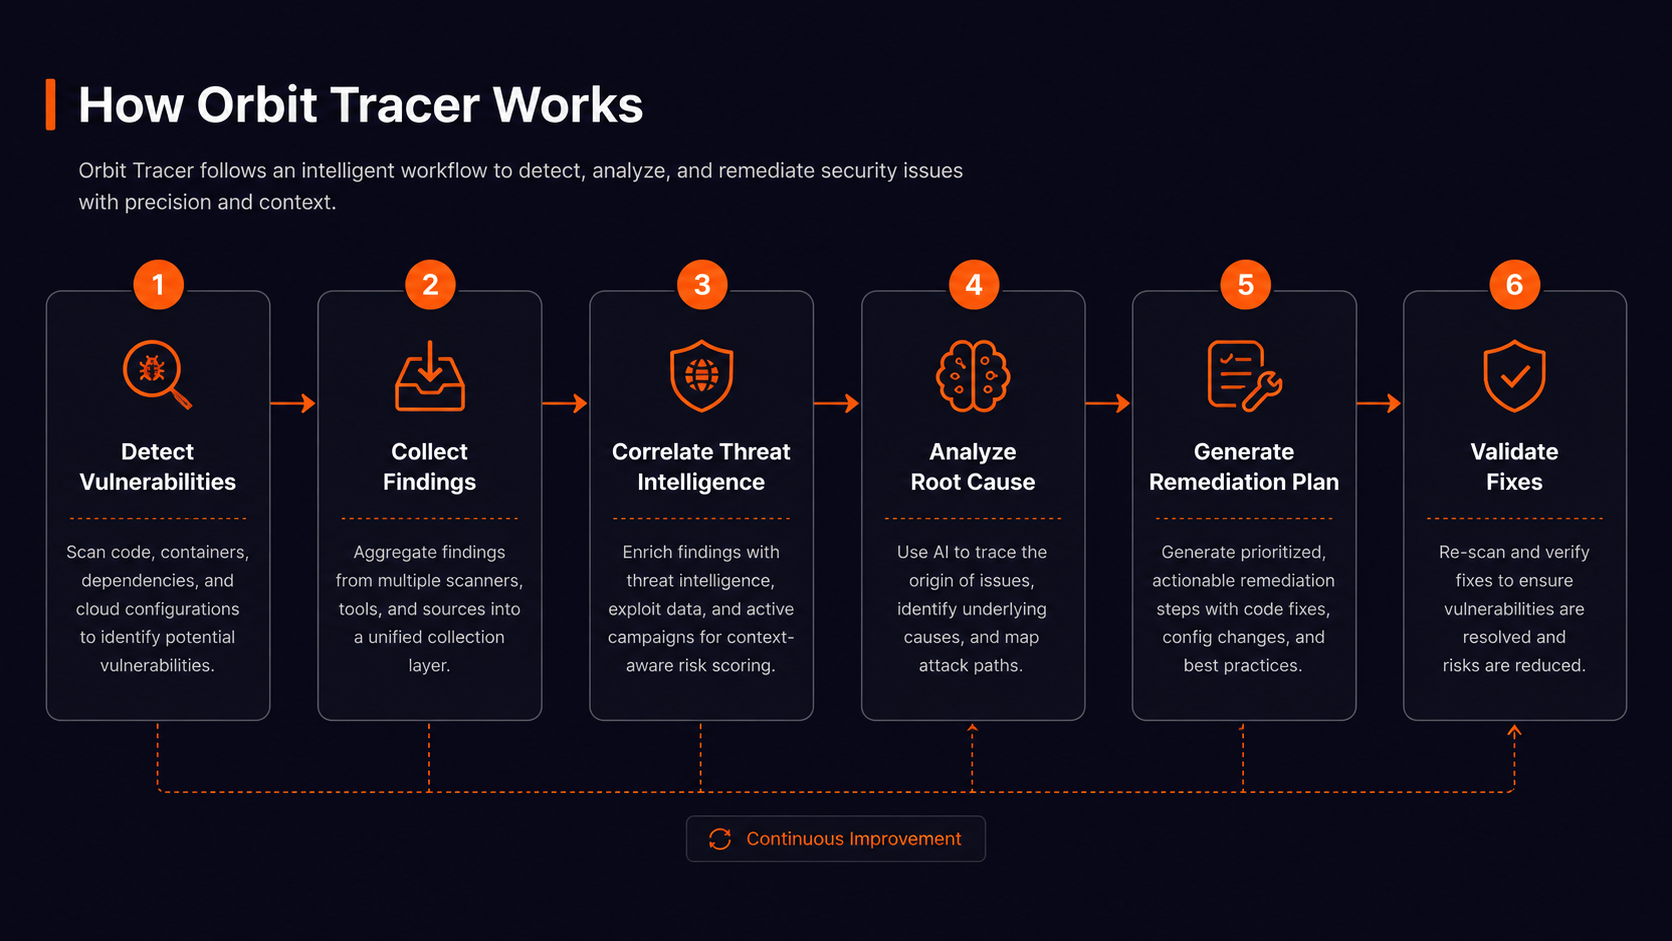
Orbit Tracer detects and remediates all major vulnerability types:
| # | Vulnerability | Risk | Detection | Status |
|---|---|---|---|---|
| TC-01 | SQL Injection | 🔴 9/10 | Database queries | ✅ |
| TC-02 | Command Injection | 🔴 10/10 | OS commands | ✅ |
| TC-03 | Hardcoded Secrets | 🟡 8/10 | Credential patterns | ✅ |
| TC-04 | Insecure Deserialization | 🔴 9/10 | Serialization calls | ✅ |
| TC-05 | Path Traversal | 🟡 7/10 | File operations | ✅ |
| TC-06 | Weak Cryptography | 🟡 6/10 | Hash algorithms | ✅ |
| TC-07 | XXE Attack | 🔴 8/10 | XML parsing | ✅ |
| TC-08 | Unsafe File Operations | 🔴 8/10 | File extraction | ✅ |
| TC-09 | IDOR | 🟡 7/10 | Access checks | ✅ |
| TC-10 | Insecure Logging | 🟢 5/10 | Log statements | ✅ |
All test cases include vulnerable + secure code versions for learning and testing.
Question: "Which services are affected by the SQL Injection
in database/user_service.py?"

Response:
✅ Affected services: Auth module, Payment processor, Admin dashboard
✅ Blast radius: 12 files across 3 services
✅ Risk score: 9/10 (CRITICAL)
✅ Teams notified: @database-team, @security-team
Question: "What's the business impact if we don't fix
the Command Injection?"

Response:
✅ Risk: Remote Code Execution on entire system
✅ Compliance: GDPR violation (4% revenue fine)
✅ Timeline: CRITICAL (fix in 4 hours)
✅ Proposed fix: Use subprocess.run() with arg list
Question: "Create a merge request to fix the XXE vulnerability"

Response:
✅ MR Created: security/fix-xxe-attack-#12345
✅ Secure Code: defusedxml implementation
✅ Status: ⏳ Awaiting human approval
✅ Link: https://gitlab.com/.../merge_requests/xyz
✅ Python        ✅ Go             ✅ Rust
✅ JavaScript    ✅ Java           ✅ Ruby
✅ TypeScript    ✅ C#/.NET        ✅ PHP
(Extensible to all languages)
✅ GDPR (EU)              ✅ PCI-DSS (Payment Cards)
✅ HIPAA (Healthcare)     ✅ SOC 2 (Coming)
Orbit Tracer enforces organization-wide security standards through SKILL.md:
