zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection RCE Full Chain).

🛡️ AI Security Tool Module
n8n Full Chain (CVE-2026-21858 + CVE-2025-68613) — "Ni8mare"
Official Security Audit Module for AI Security Tool Ecosystem





🌐 Web Demo • 📚 Project Website • 💬 Community Chat
Website Navigation: Home • Updates • Downloads • Modules
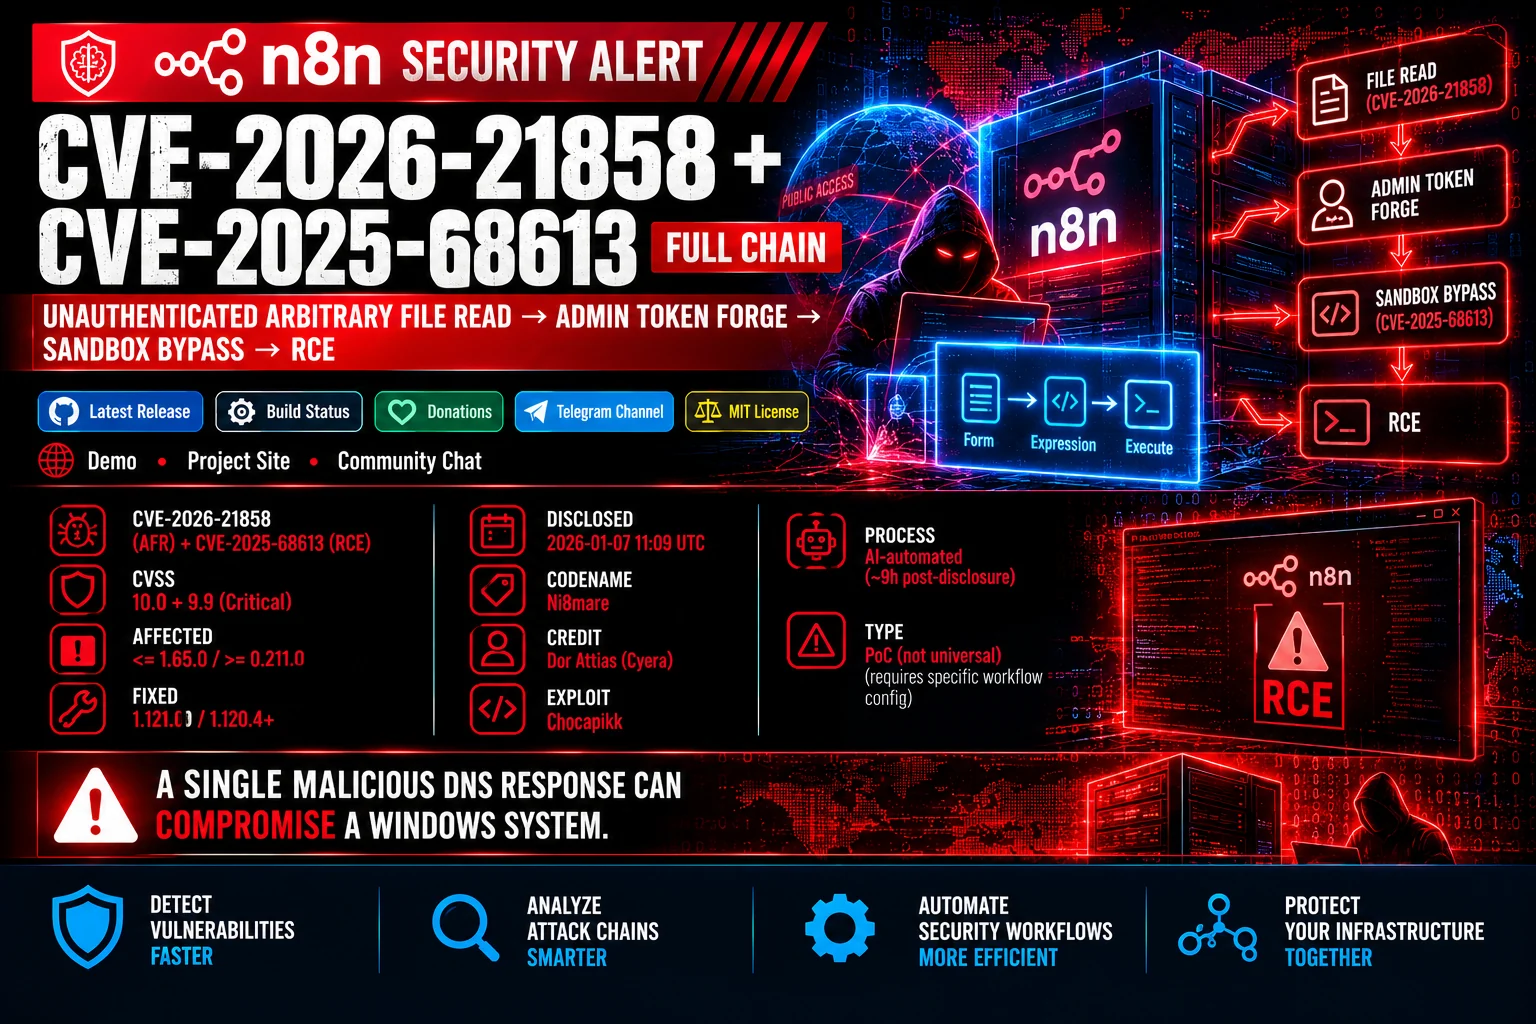
This module provides diagnostic tools and a complete exploitation chain for n8n workflow automation instances, dubbed Ni8mare.
The attack chain combines an unauthenticated Arbitrary File Read (CVE-2026-21858) caused by Content-Type confusion with an authenticated Expression Injection Sandbox Bypass (CVE-2025-68613). By sending a manipulated Content-Type: application/json request to an exposed file upload form, an attacker controls the filepath argument to read internal system files (/proc/self/environ, configuration, and SQLite DB). The retrieved encryptionKey and password hash allow offline forgery of an administrator JWT cookie. Once authenticated, expression injection via this.process.mainModule.require escapes the JavaScript sandbox to execute arbitrary system commands.
"From file read to full system takeover in three steps."
While the file read requires an active form workflow with binary output, expression injection works reliably on default n8n installations without requiring special nodes or explicit system permissions enabled.
| Specification | Assigned Value | Notes |
|---|---|---|
| CVE Identifiers | CVE-2026-21858 + CVE-2025-68613 |
Full Chain: Unauthenticated File Read to RCE |
| Severity Rating | Critical (CVSS v3.1: 10.0 + 9.9) | Unauthenticated RCE chain |
| Vulnerability Types | CWE-200 / CWE-94 |
Content-Type Confusion / Code Injection |
| Affected Component | n8n Workflow Automation Engine | Versions <= 1.65.0 (AFR) / >= 0.211.0 (RCE) |
| Patched Versions | 1.121.0 (AFR) / 1.120.4+ (RCE) | Official vendor patches released |
| Privileges Required | None | Unauthenticated initial access via public form |
graph TD
    A[Unauthenticated Attacker] -->|1. Content-Type Confusion| B[Vulnerable Form Endpoint]
    B -->|2. Arbitrary File Read| C[Extract /proc/self/environ & database.sqlite]
    C -->|3. Derive Secret & Hash| D[Forge Admin JWT Cookie]
    D -->|4. Authenticate as Admin| E[n8n Workflow Engine]
    E -->|5. Expression Injection Payload| F[Sandbox Escape via mainModule.require]
    F -->|6. Execute Command| G[Full Remote Code Execution]
={{ (function() {
  var require = this.process.mainModule.require;
  var execSync = require("child_process").execSync;
  return execSync("id").toString();
})() }}1.121.0 or higher.N8N_ENFORCE_SETTINGS_FILE_PERMISSIONS=true and restrict process capabilities in Docker containers.⚠️ IMPORTANT: This module is built specifically for safe execution and diagnostics within the AI Security Tool ecosystem. Always use verified modules sourced from official repositories.
To execute the monitoring and diagnostic scripts, ensure the AI Security Tool core engine is installed: