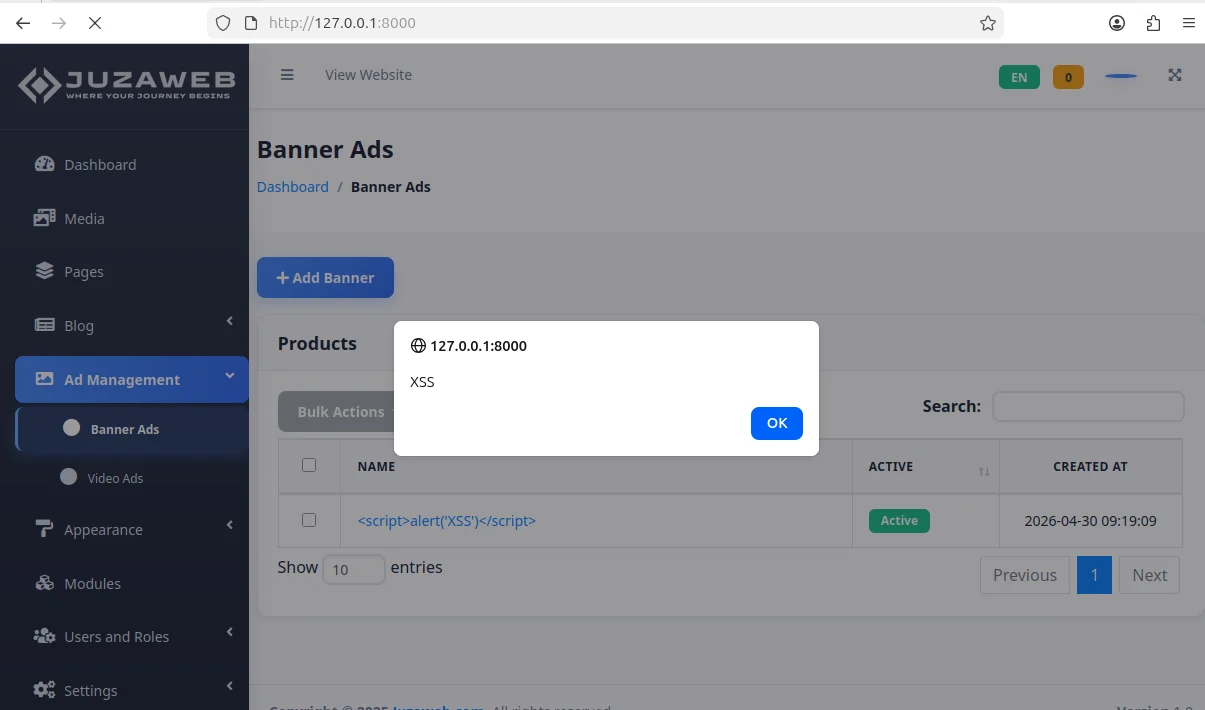
 yuhuamiao/cve-2026-36358
Proof-of-concept demonstrating a stored XSS vulnerability in Juzaweb CMS v5.0.0 via the banner ads HTML field, leading to arbitrary script execution in the admin panel.

First, set up the platform normally and register an account. Here, the administrator account I registered is [email protected] / 123456.
After setting up the platform, you can see the website homepage.
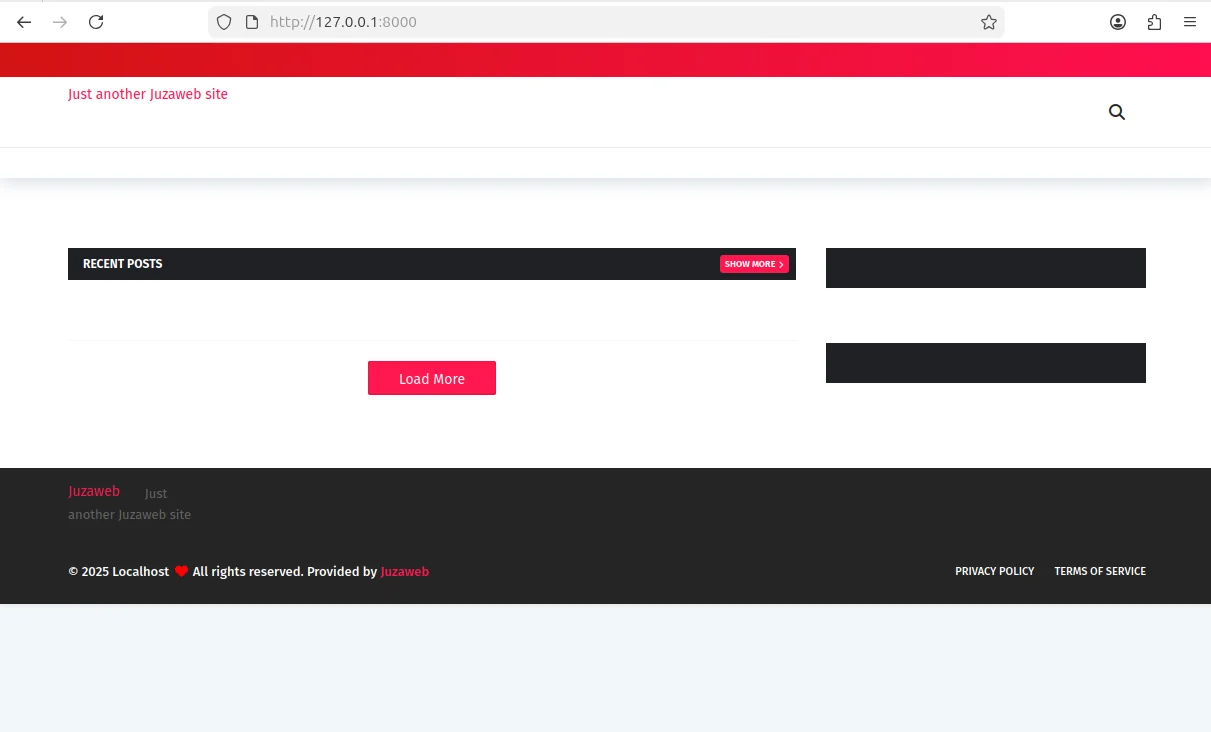
Access /admin and log in.
After logging in, you will enter the admin backend dashboard.
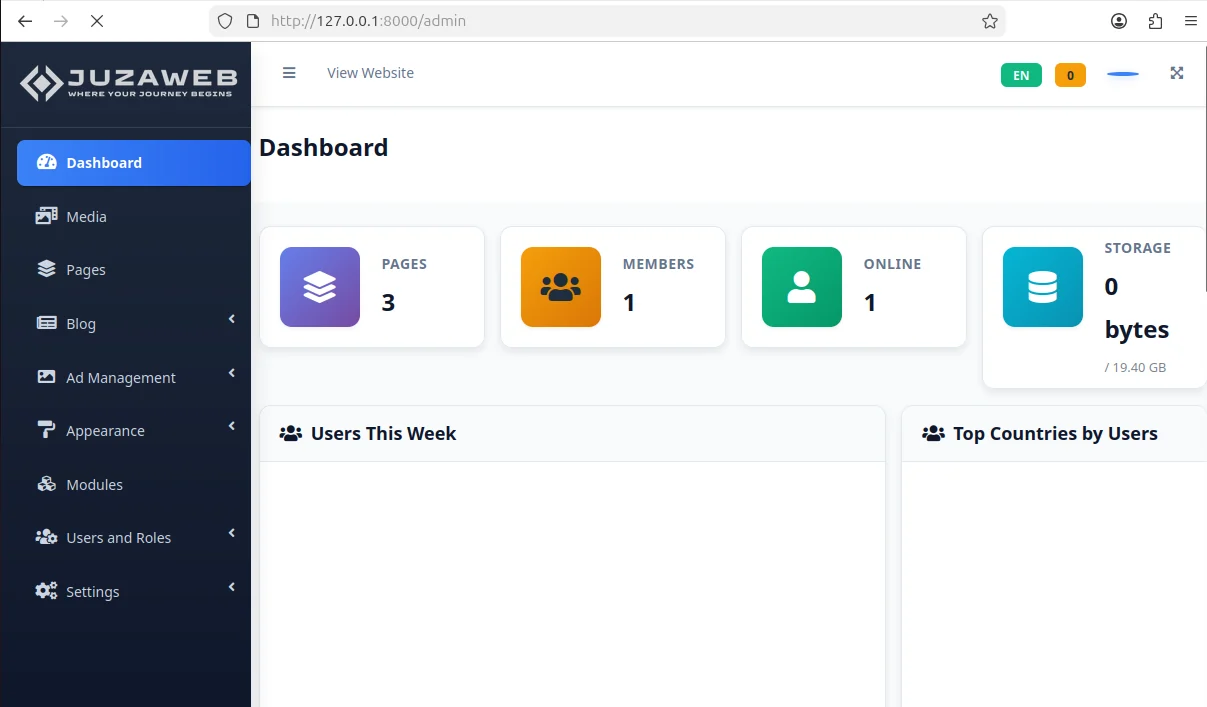
Navigate to the /admin/banner-ads route and click "Add Banner" to go to the ad creation page.
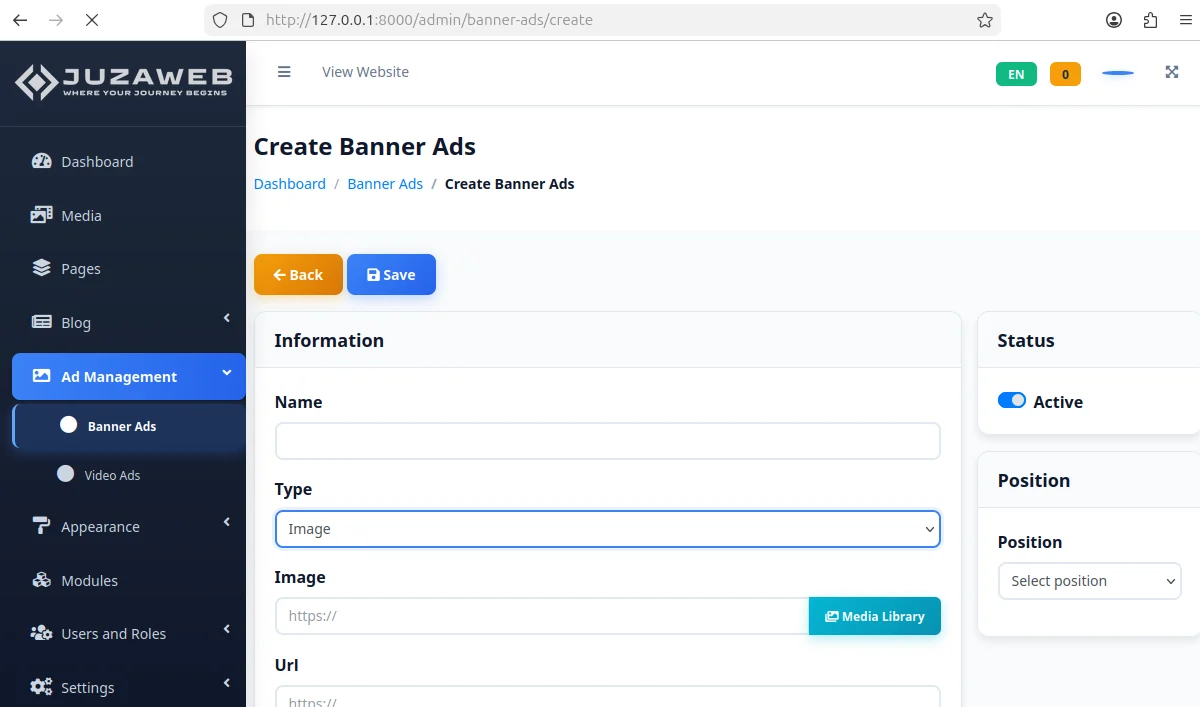
Change the Type to "HTML" and insert the malicious XSS code into the Body field.
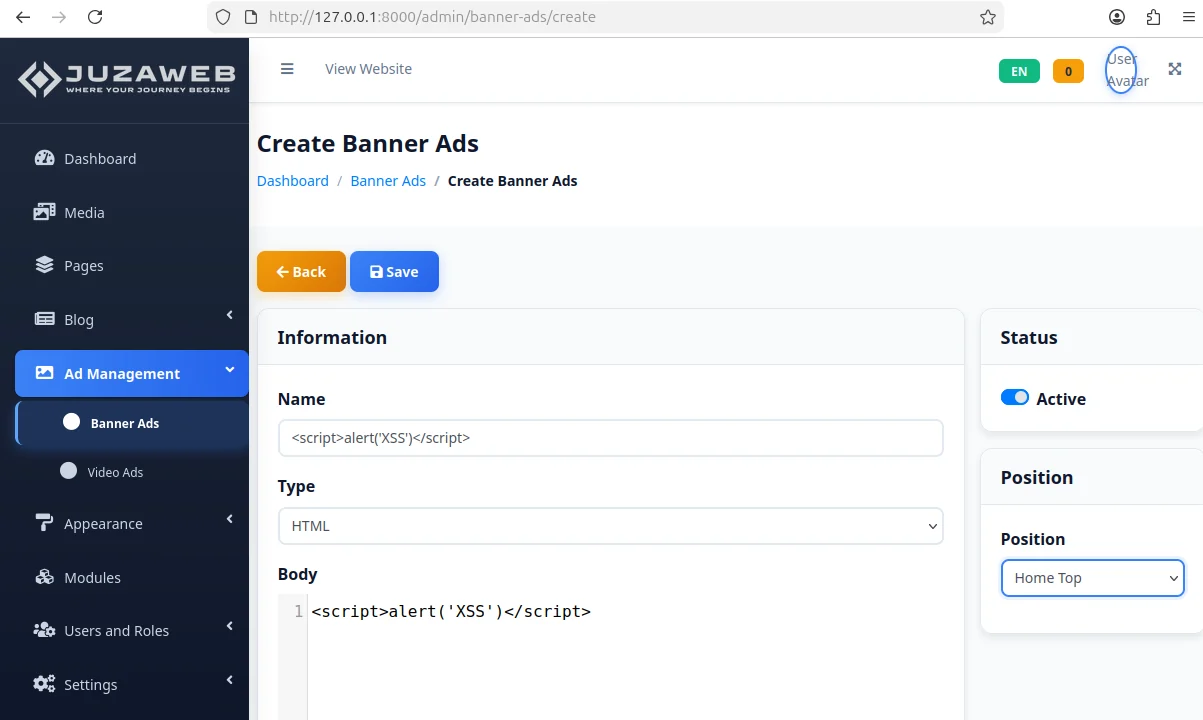
If you encounter an error like this:
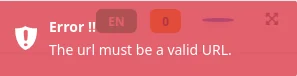
Go back to the "Image" Type and enter any URL in the URL field.
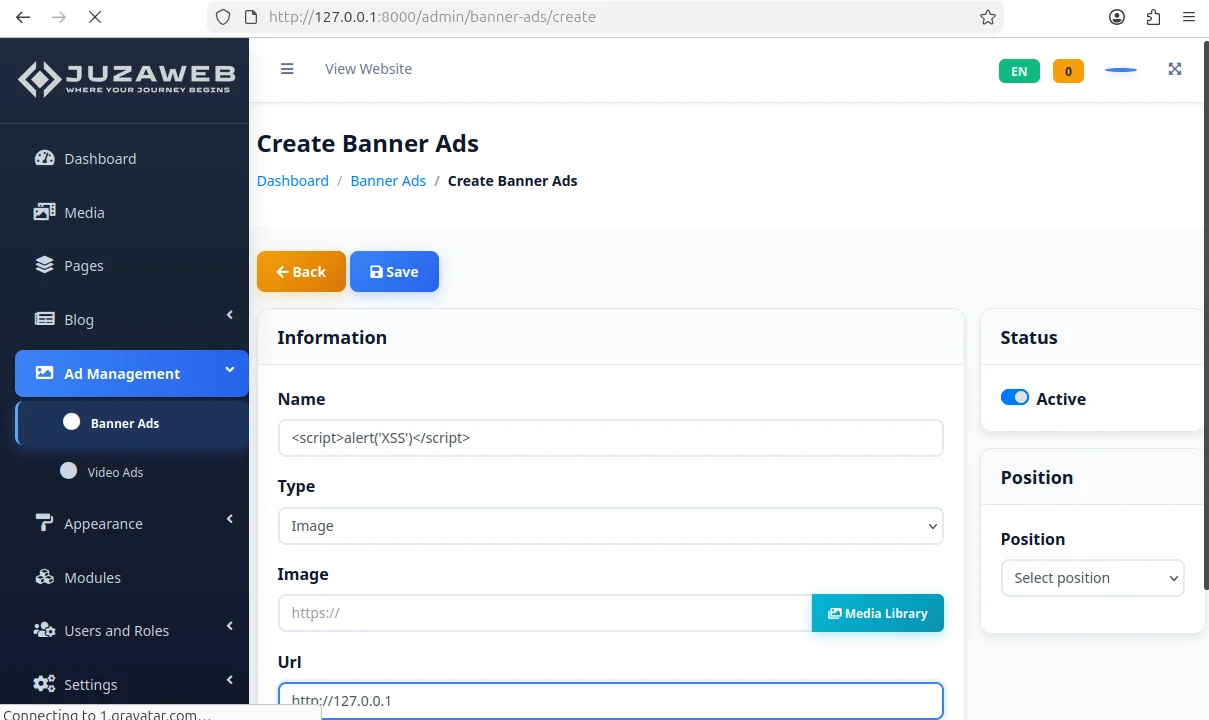
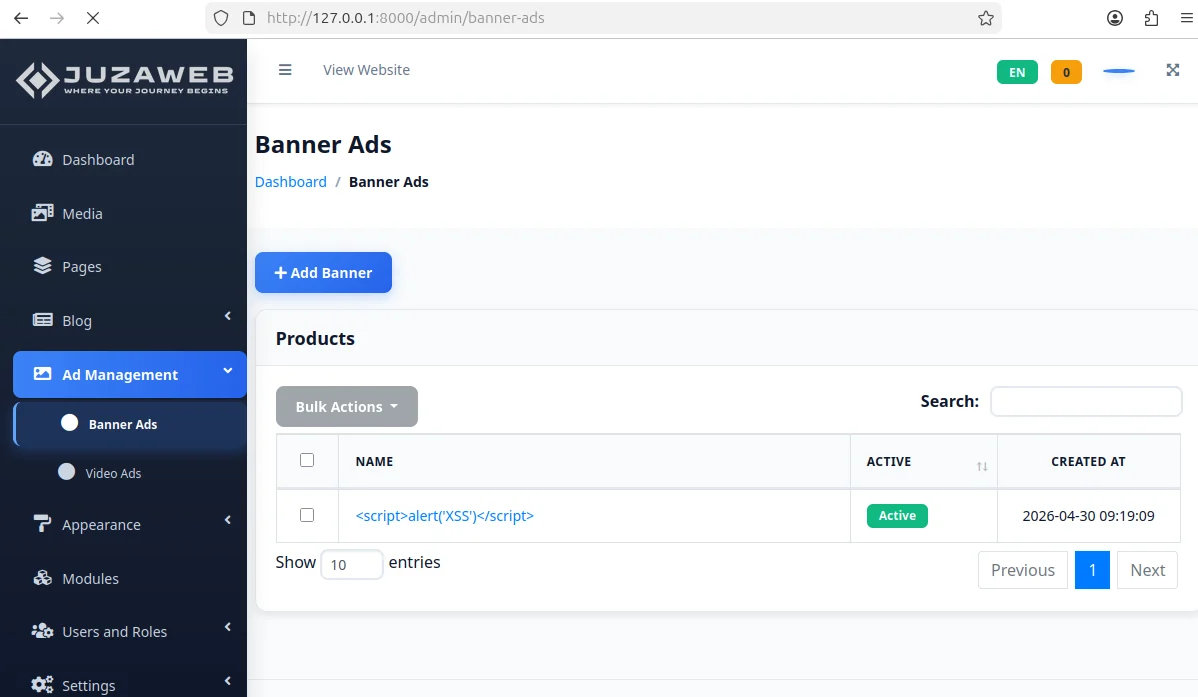
After successfully adding the ad, you can see it is active/running.
Now, return to the homepage. The alert box will pop up, demonstrating the XSS vulnerability.