 xssfile/cve-2017-8464-exp
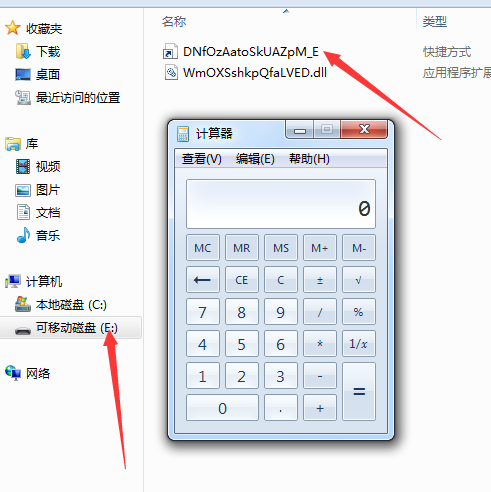
Exploit for CVE-2017-8464 LNK remote code execution vulnerability. Generates malicious .lnk files for USB-based payload delivery, supporting x86 and x64 architectures.

Support x86 and x64
Just for test
Lnk file from: https://github.com/rapid7/metasploit-framework/pull/8767
Thanks to ykoster
Small change,replace the dll file,fix the bug of crashing explorer.exe.(ykoster has fixed this bug)
POC:
x86:

x64:
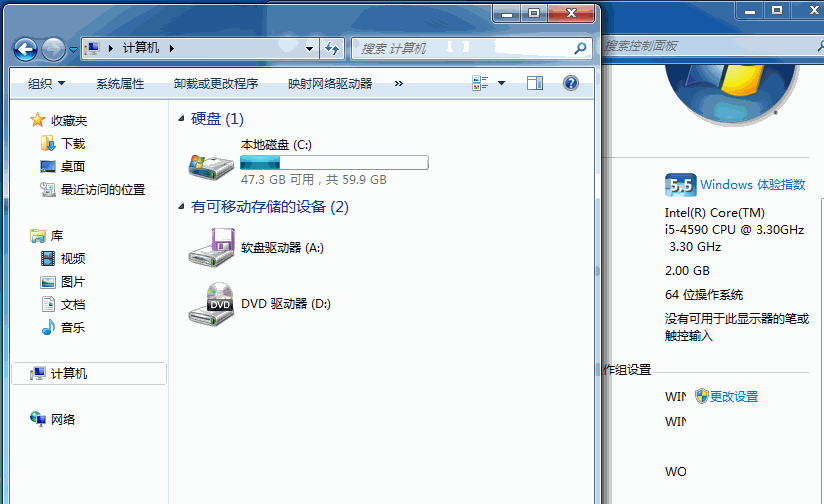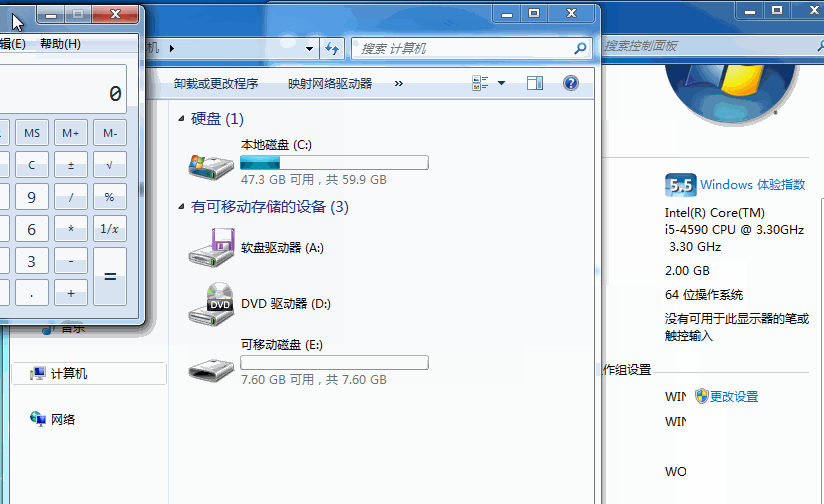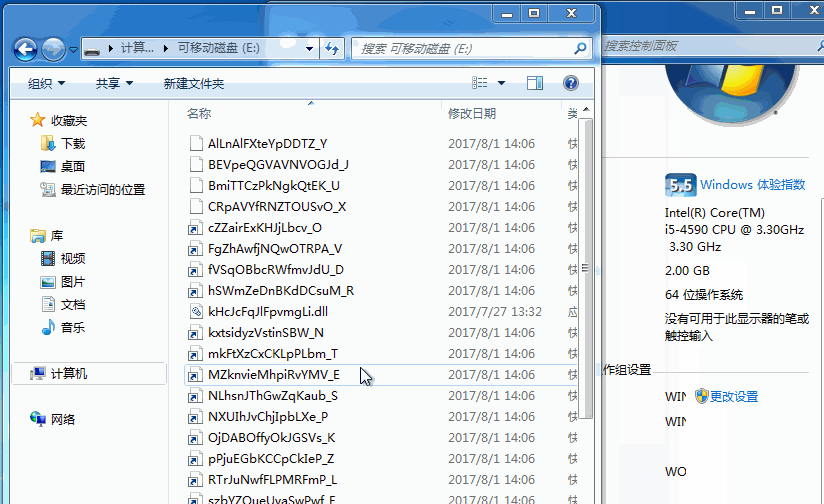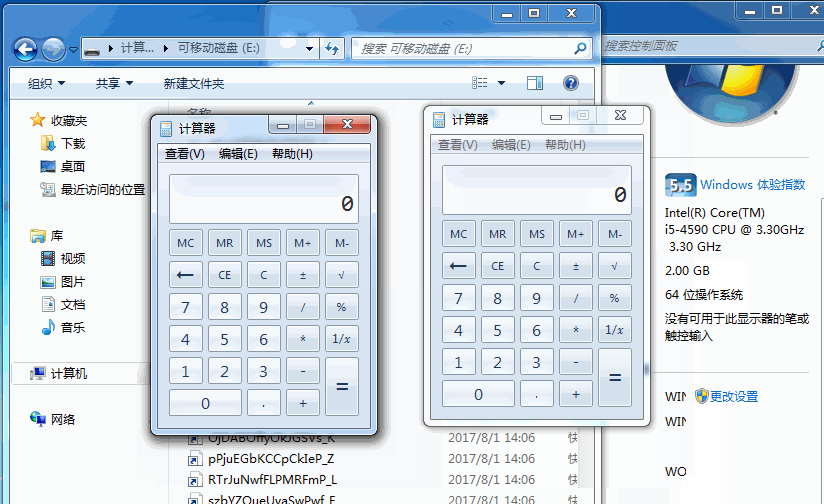
If you can determine the USB drive,one LNK file is enough,like this:

More details:
