 umpolungfish/byvalver
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities

THE SHELLCODE BAD-BYTE BANISHER


Overview • Quick Start • Interactive TUI • Targeted Bad-Byte Elimination • Bad-Byte Profiles • Features • Architecture • System Requirements • Dependencies • Building • Installation • Usage • Obfuscation Strategies • Denullification Strategies • ML Training • Agent Menagerie • Development • Troubleshooting • License
byvalver is a CLI tool built in C for automatically eliminating (or "banishing") bad-bytes from x86/x64/ARM/ARM64 shellcode while maintaining complete functional equivalence
NEW in v4.0: Cross-Architecture Support
| Architecture | Maturity | Strategies | Notes |
|---|---|---|---|
| x86 (32-bit Intel/AMD) | Stable v4.2 | 150+ | Production-tested, full coverage |
| x64 (64-bit Intel/AMD) | Stable v4.2 | 150+ | Default architecture, production-tested |
| ARM (32-bit) | Experimental v0.1 | 7 core | Limited testing, core instructions only |
| ARM64 (AArch64) | Experimental v0.1 | Basic | Framework ready, minimal strategies |
--arch flagv4.0.1 Bug Fixes:
can_handle logic for pass-through strategiesNEW in v4.2: Enhanced x64 Support
is_64bit_register(), is_extended_register(), build_rex_prefix()The tool uses the Capstone disassembly framework to analyze instructions and applies over 175+ ranked transformation strategies to replace bad-byte-containing code with equivalent alternatives
The generic bad-byte banishment framework provides 2x usage modes:
--bad-bytes option allows specification of arbitrary bytes to banish (e.g., --bad-bytes "00,0a,0d" for newline-safe shellcode)--profile option uses pre-configured bad-byte sets for common exploit scenarios (e.g., --profile http-newline, --profile sql-injection, --profile alphanumeric-only)Supports Windows, Linux, and macOS
CORE TECH:
C implementation for efficiency and low-level controlCapstone for precise disassemblyNASM for generating decoder stubs[!NOTE] Null-byte elimination (
--bad-bytes "00"or default): WELL-TESTED / Generic bad-byte elimination (--bad-bytes "00,0a,0d"etc.): NEWLY IMPLEMENTED
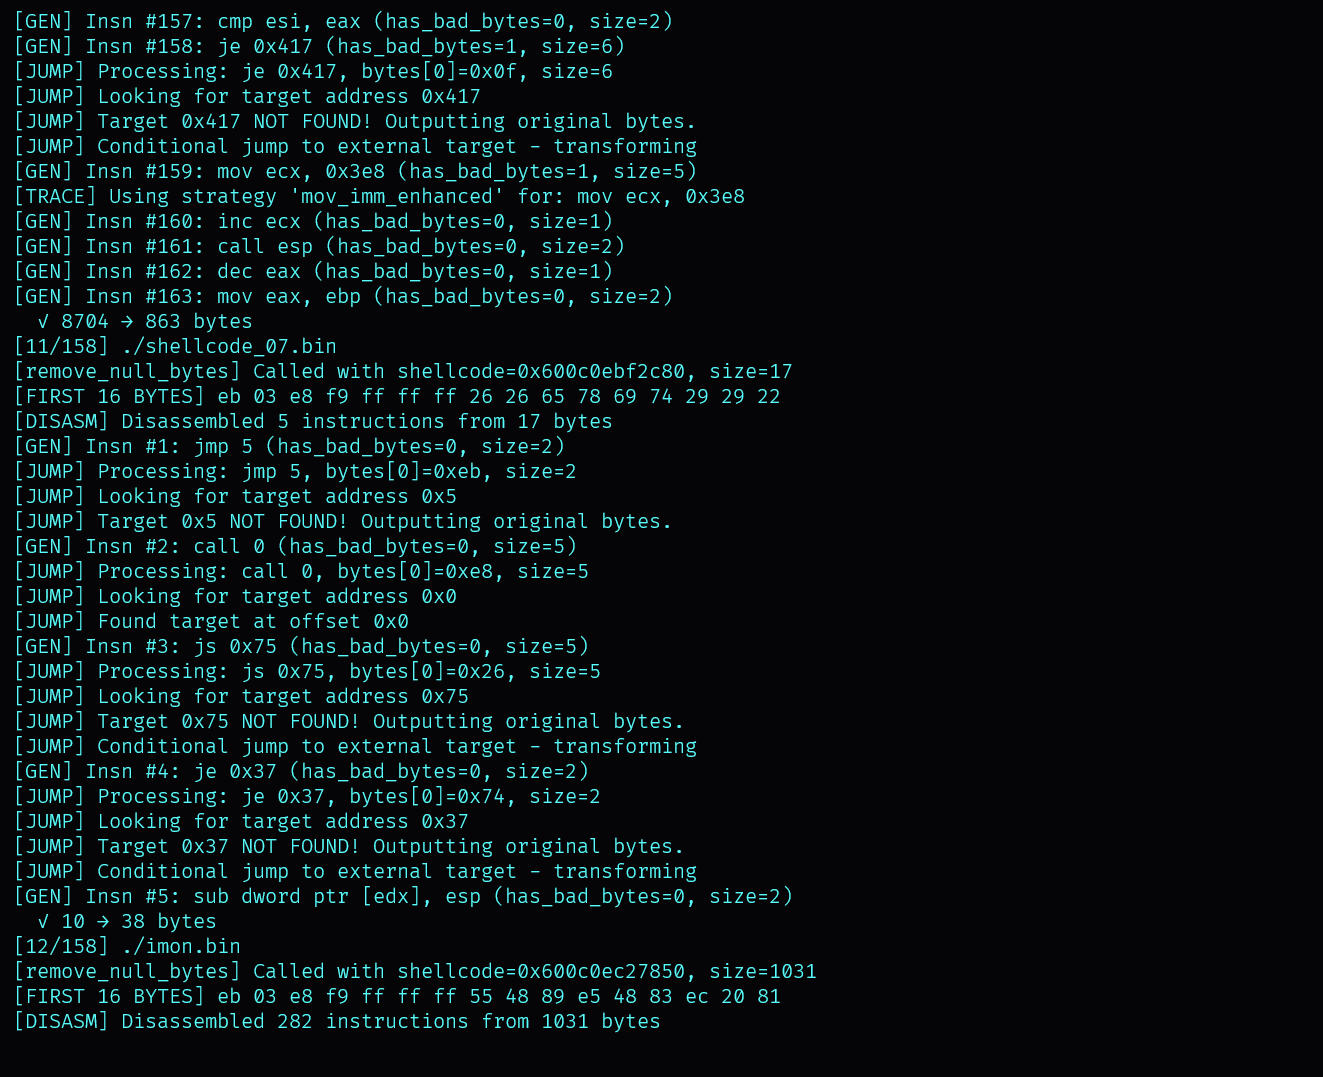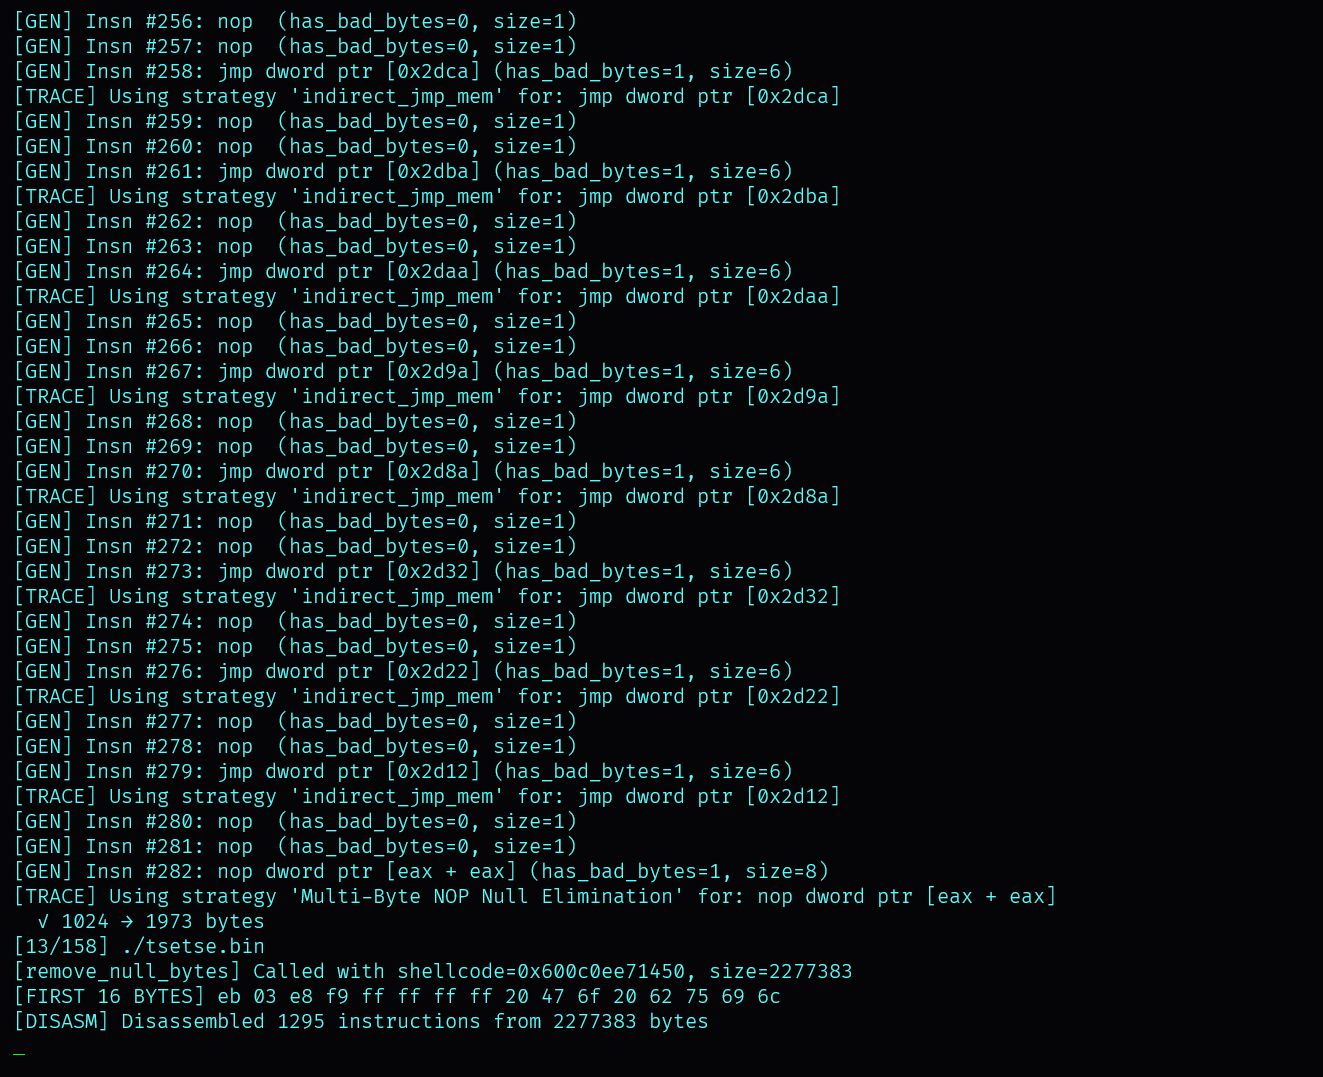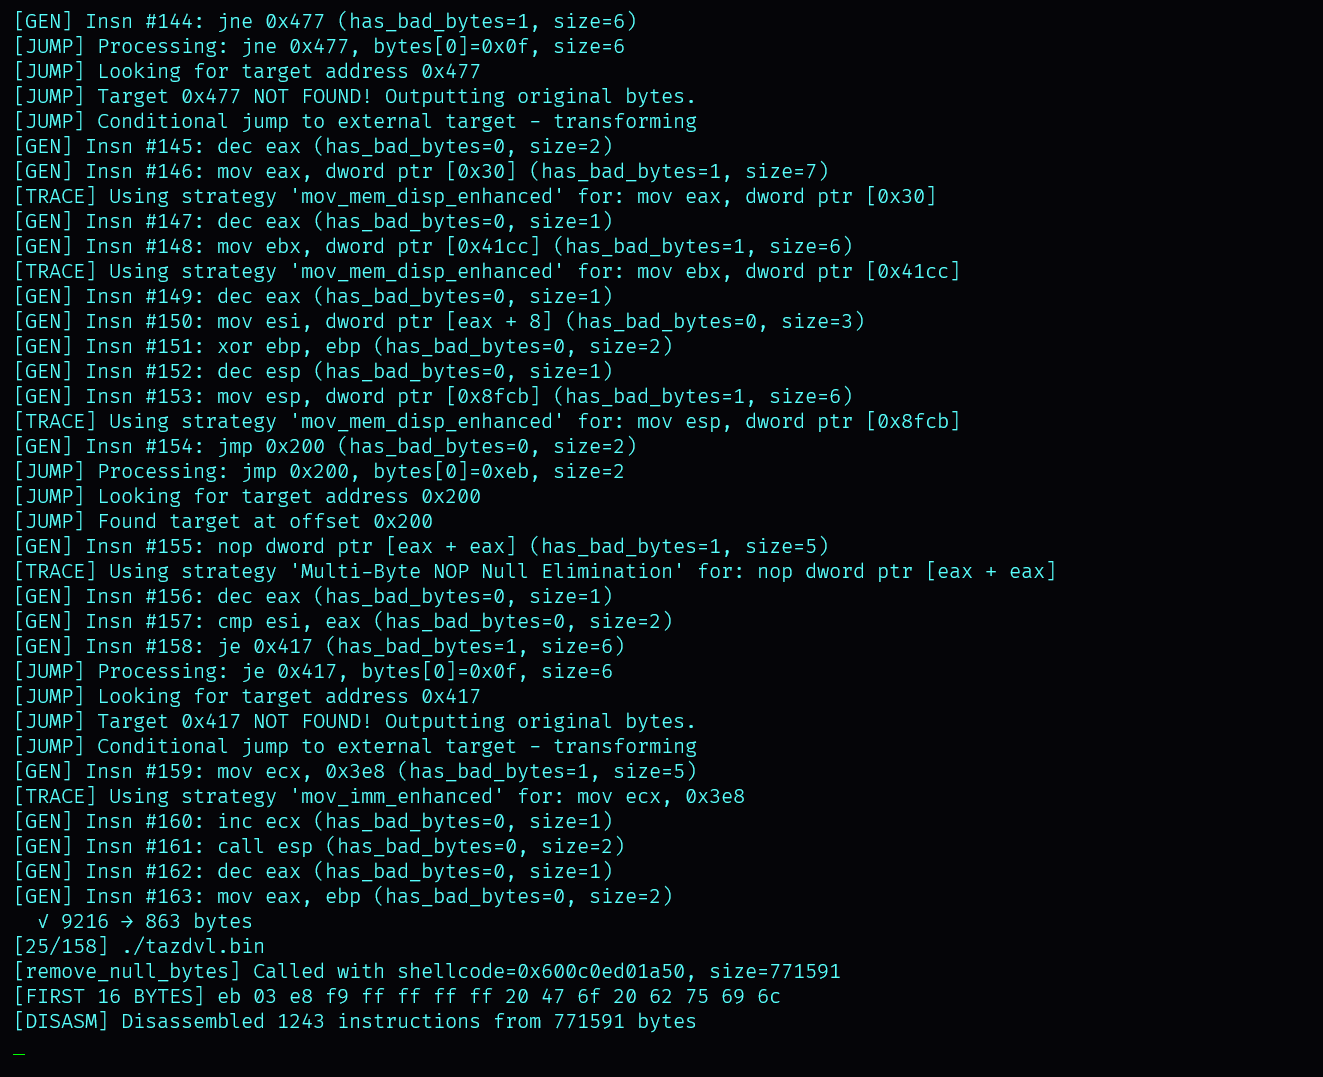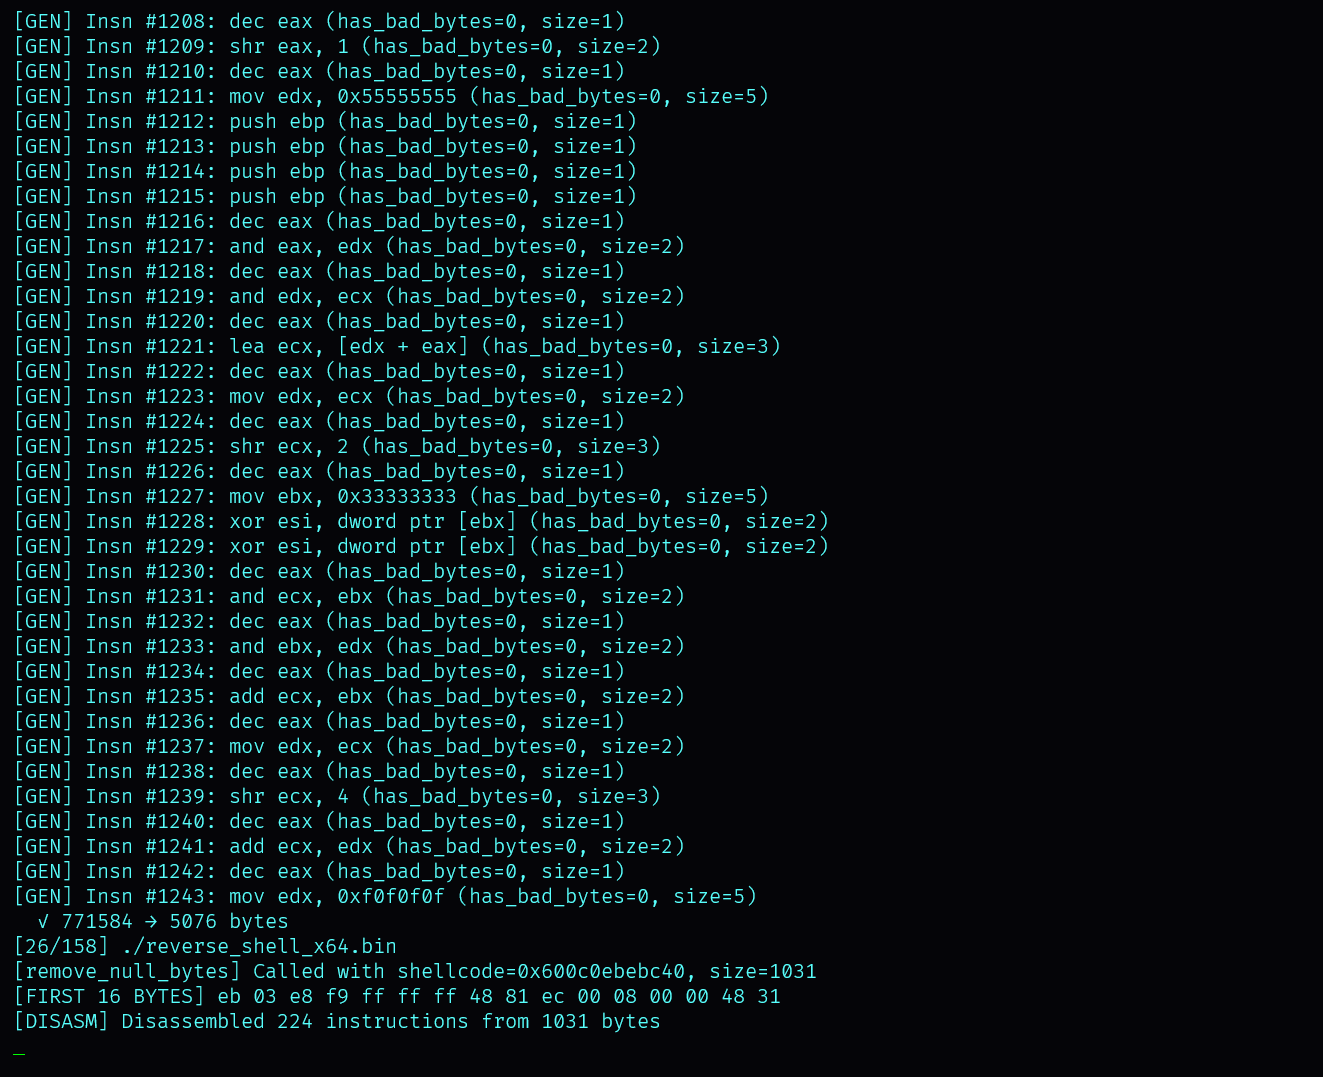
Get started with byvalver in minutes:
OPTION 1: FROM GITHUB (RECOMMENDED)
curl -sSL https://raw.githubusercontent.com/umpolungfish/byvalver/main/install.sh | bash
OPTION 2: BUILD FROM SOURCE
git clone https://github.com/umpolungfish/byvalver.git
cd byvalver
make
sudo make install
sudo make install-man  # Install man page
banish NULL BYTES (DEFAULT):
byvalver input.bin output.bin
USING BAD-BYTE PROFILES:
# HTTP contexts (removes null, newline, carriage return)
byvalver --profile http-newline input.bin output.bin

# SQL injection contexts
byvalver --profile sql-injection input.bin output.bin

# Alphanumeric-only shellcode (most restrictive)
byvalver --profile alphanumeric-only input.bin output.bin
MANUAL BAD-BYTE SPECIFICATION:
# banish null bytes and newlines
byvalver --bad-bytes "00,0a,0d" input.bin output.bin
ADVANCED FEATURES:
# Add obfuscation layer before denullification
byvalver --biphasic input.bin output.bin

# Enable ML-powered strategy selection
byvalver --ml input.bin output.bin
