
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
cve-2026-3437 — Exploit for CVE-2026-3437 enabling arbitrary physical memory read/write through the vulnerable Portwell portwell.sys driver via MmMapIoSpace, for local privilege escalation and BYOVD. | Kitploit
Tools/GitHubGitHub/tihomirocrew/cve-2026-3437
Privilege EscalationVulnerability AnalysisExploitationReverse EngineeringBinary ExploitationRepository Deleted
GitHubtihomirocrew/cve-2026-3437

cve-2026-3437

Exploit for CVE-2026-3437 enabling arbitrary physical memory read/write through the vulnerable Portwell portwell.sys driver via MmMapIoSpace, for local privilege escalation and BYOVD.

The upstream repository was not found during the latest Kitploit update check. This listing remains available for reference, but it has been removed from search results.
23 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

cve-2026-3437

Arbitrary physical memory read/write in portwell.sys (Portwell Engineering Toolkits v4.8.2) via MmMapIoSpace. Enables LPE/SYSTEM escalation and BYOVD by interacting with the driver's IOCTL interface.

analysis

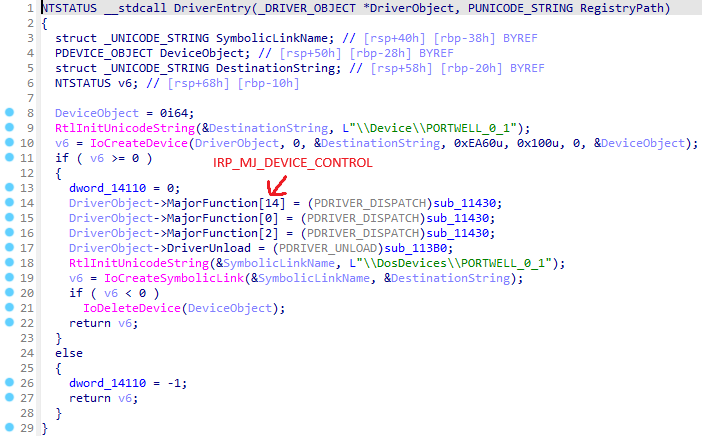
The driver registers a dispatch routine for IRP_MJ_DEVICE_CONTROL to handle DeviceIoControl calls from usermode.
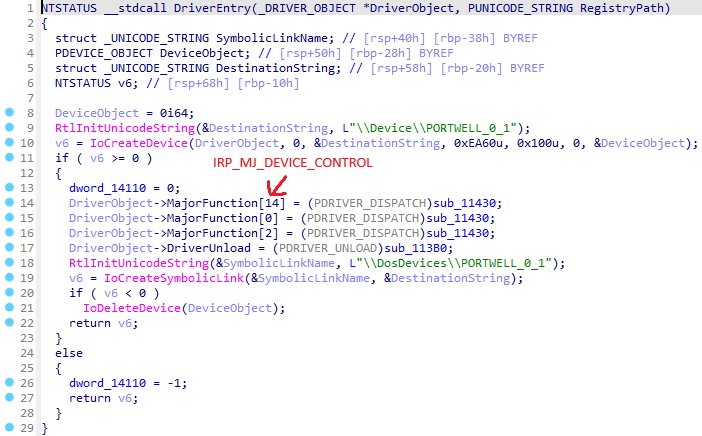
driver entry

Inside the dispatch routine we can find a call to sub_11F80.
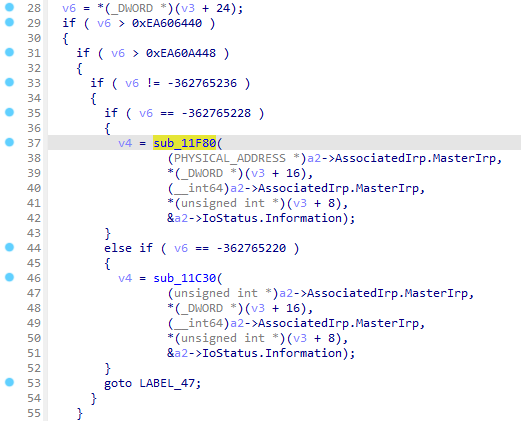
write physical call

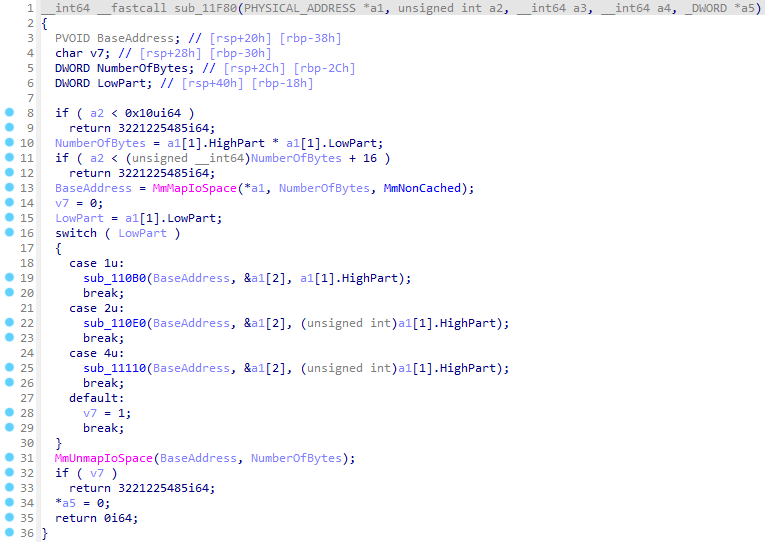
Looking inside this function reveals the following:

  1. Arbitrary physical memory write via MmMapIoSpace
  2. No validation of user-supplied arguments
  3. A usermode caller can pass an arbitrary physical address and data

write physical

Going back to the dispatch routine, we can also find a call to sub_11E40.
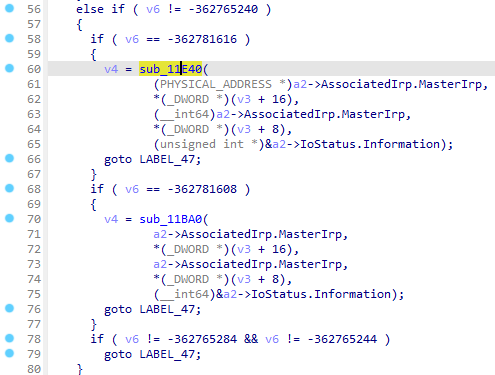
read physical call

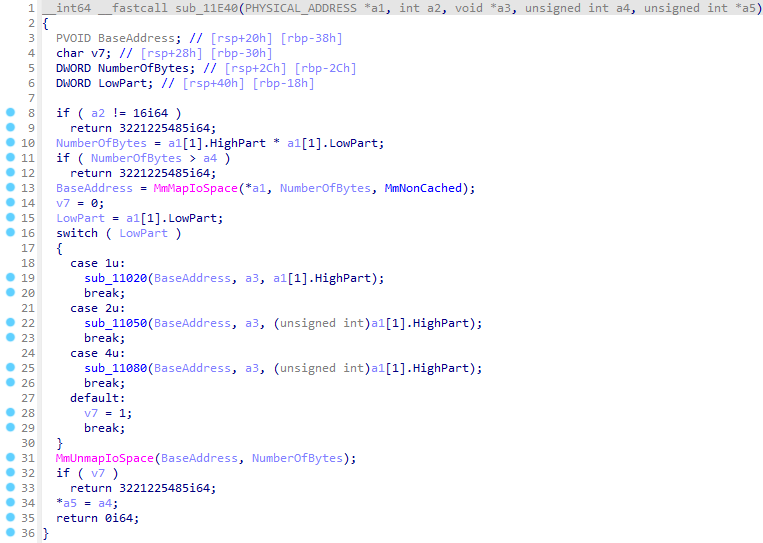
Looking inside this function reveals the following:

  1. Arbitrary physical memory read via MmMapIoSpace
  2. No validation of user-supplied arguments

read physical

usage

sc create portwell binPath=C:\windows\temp\portwell.sys type=kernel
sc start portwell

.\cve-2026-3437.exe

references

  • 🔍 SentinelOne Analysis
  • 🛡️ LOLDrivers
  • 📋 NVD Record
  • 🐙 GitHub Advisory